Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-27876 — CVE-2026-27876 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-27876
Vulnerability AnalysisCode AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHub0xblackash/cve-2026-27876

CVE-2026-27876

CVE-2026-27876

View Repository
3397 months agoNot yet reviewed
Share

🚨 CVE-2026-27876 - Grafana Critical RCE via SQL Expressions

Grafana Zero-Day Vulnerability

Grafana Severity CVSS

A chained vulnerability allowing arbitrary file writes through SQL Expressions, leading to full Remote Code Execution (RCE) on the host.


📋 Overview

CVE ID: CVE-2026-27876
Severity: Critical (CVSS v3.1: 9.1)
Published: March 27, 2026
CWE: CWE-94 (Improper Control of Generation of Code / Code Injection)

Grafana's SQL Expressions feature (introduced/reimplemented in v11.6.0 with MySQL-like syntax) allows users to transform query data using familiar SQL. However, this capability inadvertently permitted arbitrary file writes to the filesystem. When chained with specific components (including a Grafana Enterprise plugin), this leads to remote arbitrary code execution (RCE).

Attackers with sufficient permissions can overwrite critical files (e.g., Sqlyze driver or AWS data source configs), potentially gaining an SSH connection to the Grafana host.

Note: The underlying feature exists in Grafana OSS, but the full exploit chain often involves Enterprise plugin components. All users are strongly advised to update to prevent future attack vectors.
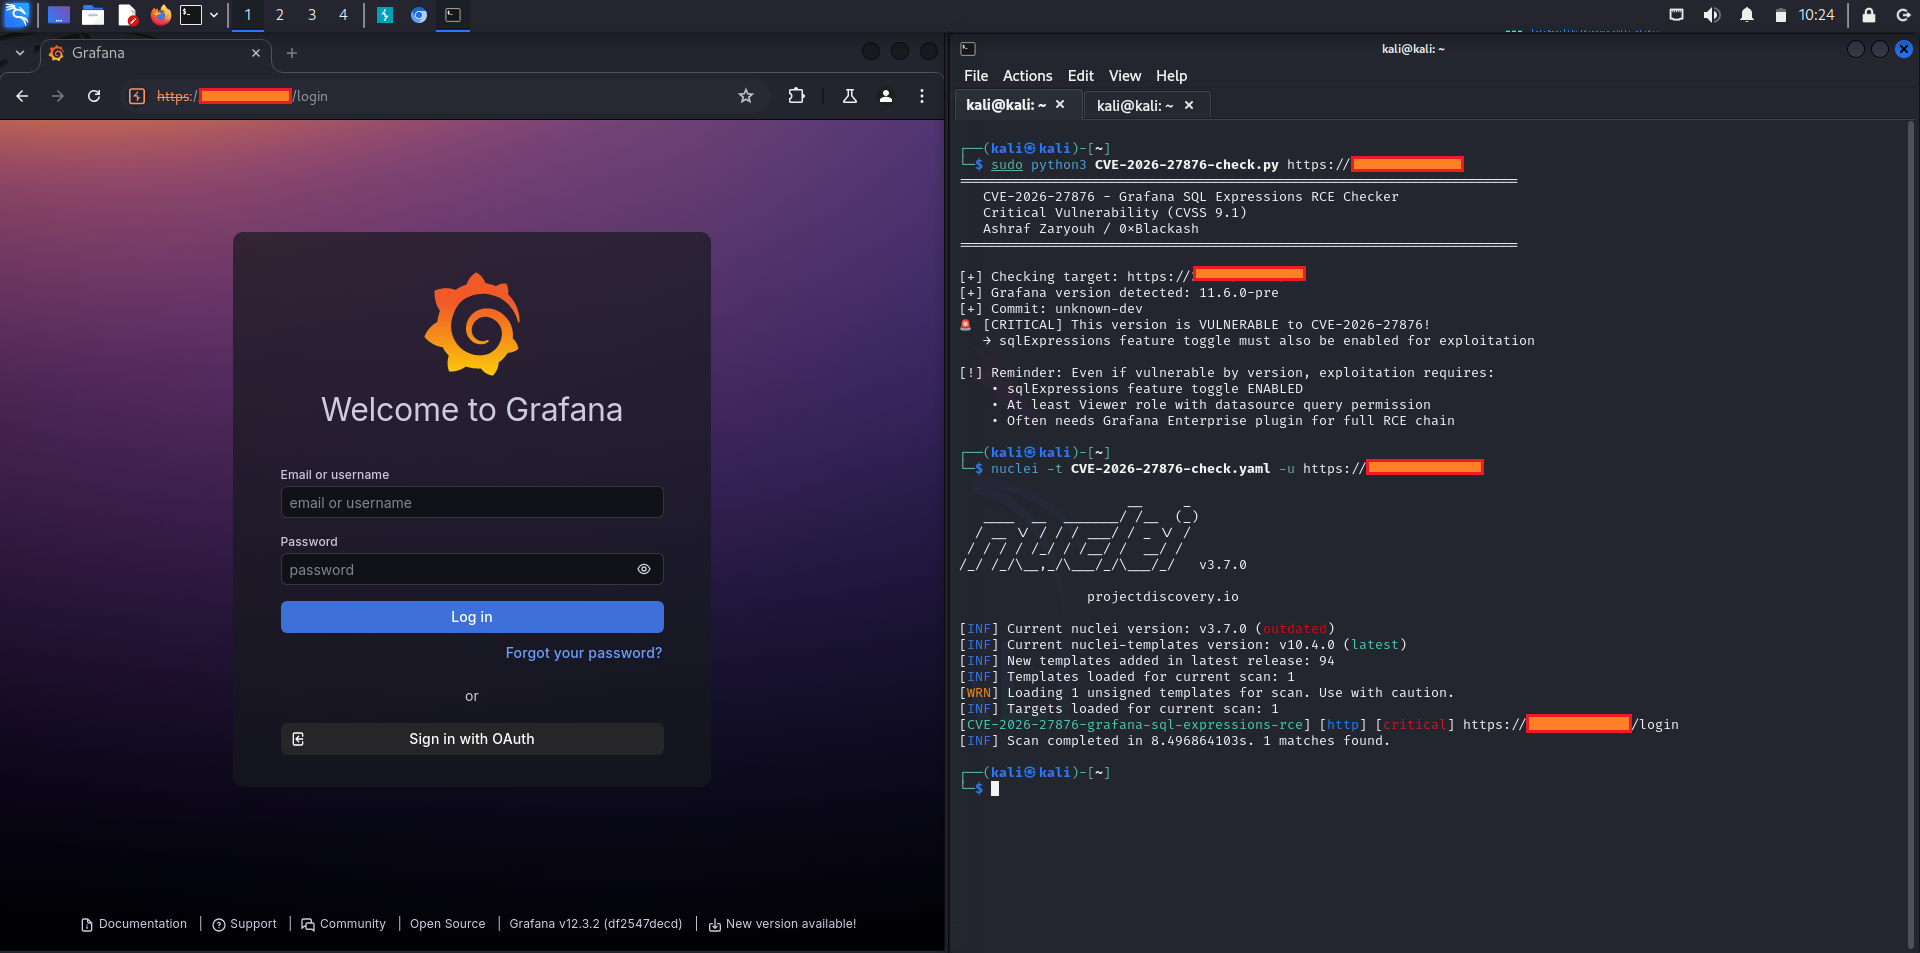

⚡ Impact

  • Remote Code Execution on the Grafana server/host
  • Full system compromise possible (data theft, persistence, lateral movement)
  • Confirmed chain can lead to SSH access
  • Affects monitoring/visualization environments with high business impact
cve-2026-27876 1

Prerequisites for Exploitation:

  • The sqlExpressions feature toggle must be enabled
  • Attacker needs access to execute data source queries (Viewer role or higher)

Attack Vector: Network (AV:N)
Attack Complexity: Low (AC:L)
Privileges Required: High (PR:H)
User Interaction: None (UI:N)
Scope: Changed (S:C)
Confidentiality/Integrity/Availability: High (C:H/I:H/A:H)


📌 Affected Versions

  • Grafana v11.6.0 and later (up to the patched releases)
  • Specifically impacts instances with sqlExpressions enabled

Enterprise plugin involvement noted in several reports for the full chain.


✅ Fixed Versions

Upgrade immediately to one of the following patched releases:

BranchFixed Version
Latest12.4.2
12.312.3.6
12.212.2.8
12.112.1.10
11.611.6.14

Download links available on the official Grafana site.


🛡️ Mitigation & Workarounds

Primary Recommendation

Upgrade to a fixed version as soon as possible.

Temporary Workarounds (if upgrade is delayed)

  1. Disable the sqlExpressions feature toggle (most effective single step)
  2. If using Sqlyze: Update to v1.5.0+ or disable it
  3. Disable all AWS data sources (if present)

⚠️ Workarounds may impact functionality and do not fully eliminate risk in all scenarios.

Additional Best Practices

  • Audit and restrict user permissions for data source query execution
  • Review and minimize installed plugins
  • Monitor for unusual query activity or file modifications in Grafana directories
  • Apply network segmentation and strong authentication

🕒 Timeline

  • 2025-02-06: SQL Expressions feature reimplemented and released in v11.6.0
  • 2026-02-23: Internal incident declared; Grafana Cloud patched shortly after
  • 2026-03-09: Private release to embargoed customers
  • 2026-03-25/26: Public disclosure and security release
  • March 27, 2026: CVE published

Discovered by: Liad Eliyahu (Head of Research at Miggo Security) via Grafana Labs' bug bounty program. Responsible disclosure acknowledged.


🔗 References

  • Official Grafana Security Release Blog: https://grafana.com/blog/grafana-security-release-critical-and-high-severity-security-fixes-for-cve-2026-27876-and-cve-2026-27880/
  • Red Hat CVE Page: https://access.redhat.com/security/cve/cve-2026-27876
  • NVD Detail: https://nvd.nist.gov/vuln/detail/CVE-2026-27876
  • Related: CVE-2026-27880 (unauthenticated DoS via OpenFeature)

📢 Stay Secure

Update your Grafana instances today. Monitor official channels for any follow-up advisories.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    424
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    276

Explore all tools

Browse our collection of tools

View all tools →