

Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/gpheheise/cve-2025-70600---urve-smart-office---stored-xss-in-ios-app
iOS SecurityVulnerability AnalysisWeb Application ExploitationMobile SecurityPapers & ResearchLearning & Education
GitHubgpheheise/cve-2025-70600---urve-smart-office---stored-xss-in-ios-app

CVE-2025-70600---Urve-Smart-Office---Stored-XSS-in-iOS-App

Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in the URVE Smart Office iOS app, with CVE details, impact analysis, and remediation guidance for mobile security assessments.

View Repository
2910 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    645
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    420
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    388
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    330
  • 6

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    328

Explore all tools

Browse our collection of tools

View all tools →
Share

URVE Smart Office iOS — Stored XSS via Tile HTML Field (PoC)

This repository documents a proof-of-concept (PoC) for a stored cross-site scripting (XSS) vulnerability affecting the iOS mobile application of URVE Smart Office.

Due to insufficiently implemented input validation, attacker-controlled JavaScript can be injected into the HTML field of a tile. The payload is stored and later executed when the affected content is delivered to mobile clients and rendered on iOS devices.

⚠️ LEGAL DISCLAIMER
Usage of this PoC for attacking targets without prior mutual consent is illegal.
It is the end user's responsibility to comply with all applicable local, state, and federal laws.
The author(s) and contributor(s) are not responsible for any misuse or damage caused.


CVE Details

  • CVE ID: CVE-2025-XXXX
  • Vulnerability Type: Stored Cross-Site Scripting (XSS)
  • Severity: High
  • CVSS Score (Estimated): 7.1 (High)
    • Vector: CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N
  • Affected Product: URVE Smart Office – iOS App
  • Affected Version: 1.1.22
  • Vendor: https://smartoffice.expert/
  • Discovered by: Georg Ph. E. Heise / Lufthansa Industry Solutions
  • Year: 2025

Technical Description

During a security assessment, arbitrary JavaScript code could be injected into the HTML field of a tile within the URVE Smart Office management interface.

The application fails to properly validate and sanitize user-supplied input before storing and distributing the tile content to mobile clients. As a result:

  • The malicious payload is stored server-side
  • The tile can be set online by a privileged user
  • The content is subsequently pushed to iOS devices
  • The injected JavaScript is executed when the tile is rendered

This behavior was confirmed using benign JavaScript alert payloads.

The identified injection points are not exhaustive.
Not all available input fields were tested, and additional affected vectors may exist.


Proof of Concept (PoC)

The following image demonstrates the exploitation flow:
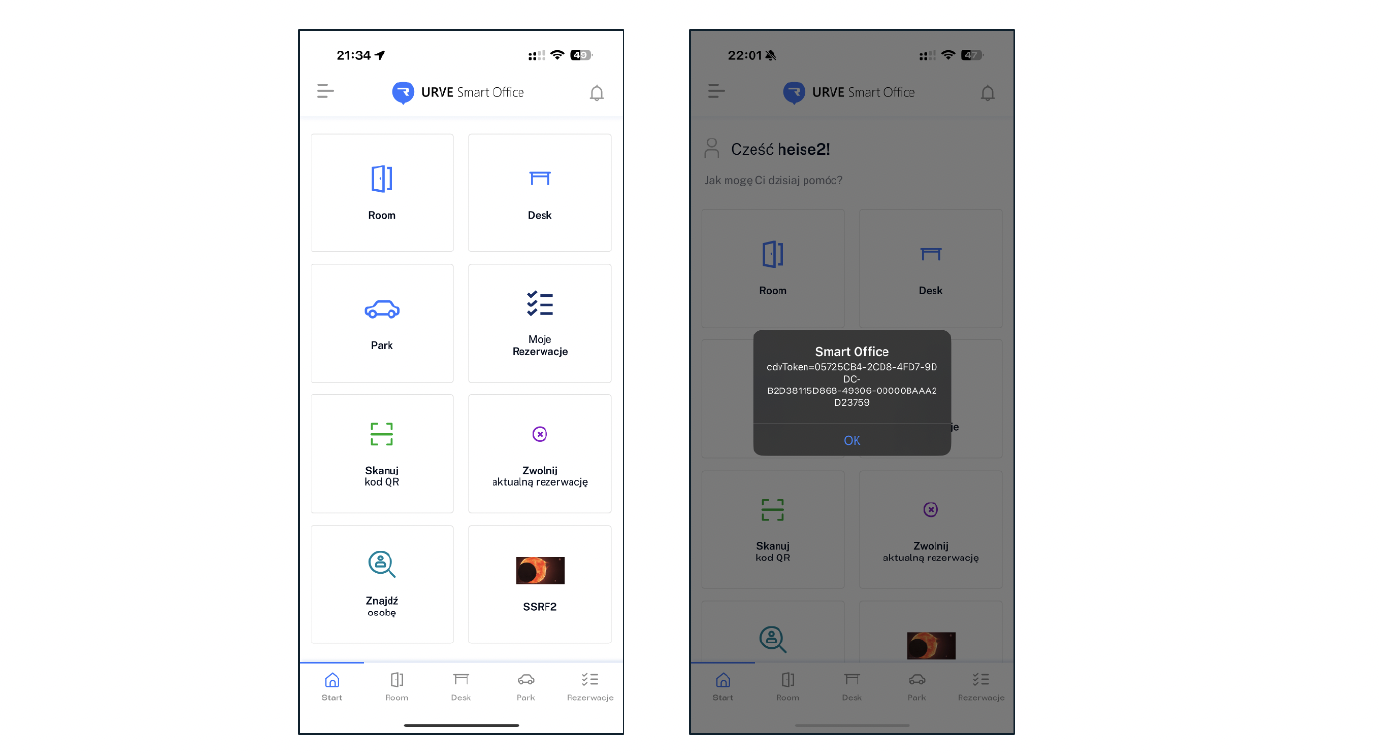
  • A manager-level user creates a tile containing malicious HTML/JavaScript
  • The tile is set to online and distributed to mobile clients
  • When the tile is rendered on an iOS device, the injected JavaScript executes

Stored XSS execution on iOS client

Note:
This repository intentionally omits full operational exploitation steps and payload details to prevent misuse. The PoC is provided solely for documentation and remediation purposes.


Impact

Successful exploitation may allow an attacker to:

  • Execute arbitrary JavaScript within the mobile app’s web context
  • Abuse trust relationships between backend and mobile clients
  • Target all users receiving the affected tile
  • Perform social engineering or phishing attacks via trusted UI elements

Timeline

DateEvent
2025-XX-XXVulnerability discovered
2025-XXVendor notified
NAVendor acknowledged
NAPatch released
2026-01-15Public disclosure

Usage

This repository does not contain exploit code.

The PoC is provided for:

  • Vulnerability validation
  • Mobile application security assessment
  • Defensive testing and remediation support
  • Security awareness and documentation

Legal & Ethical Notice

DO NOT use this information to test systems without explicit authorization.
Unauthorized security testing is illegal and may result in civil or criminal penalties.


References

  • https://cwe.mitre.org/data/definitions/79.html
  • https://owasp.org/www-community/attacks/xss/
  • https://owasp.org/www-project-mobile-top-10/
  • https://cve.mitre.org/
  • https://www.cvedetails.com/

© 2026 Georg Ph. E. Heise / Lufthansa Industry Solutions

Download Tool



