Blackash-CVE-2025-53770

Technical analysis and detection guidance for CVE-2025-53770, a critical unauthenticated RCE vulnerability in Microsoft SharePoint Server exploited…

Technical analysis and detection guidance for CVE-2025-53770, a critical unauthenticated RCE vulnerability in Microsoft SharePoint Server exploited…

Exploit code for CVE-2021-26855, a Microsoft Exchange Server vulnerability, enabling unauthorized access and remote code execution.

Proof of Concept for CVE-2021-34473, CVE-2021-34523, and CVE-2021-31207

PoC about CVE-2019-0708 (RDP; Windows 7, Windows Server 2003, Windows Server 2008)

Proof-of-concept exploit for CVE-2024-38063, a Windows TCP/IP remote code execution vulnerability triggered by sending two crafted IPv6 packets with…

WAC RCE - CVE-2026-26119 Windows Admin Center authenticated RCE via WinREST/PowerShell invokeCommand.

POC Of CVE-2022-26937

Proof-of-concept exploit for CVE-2022-26503, a local privilege escalation vulnerability in Veeam Agent for Windows via .NET deserialization, enabling…

Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…

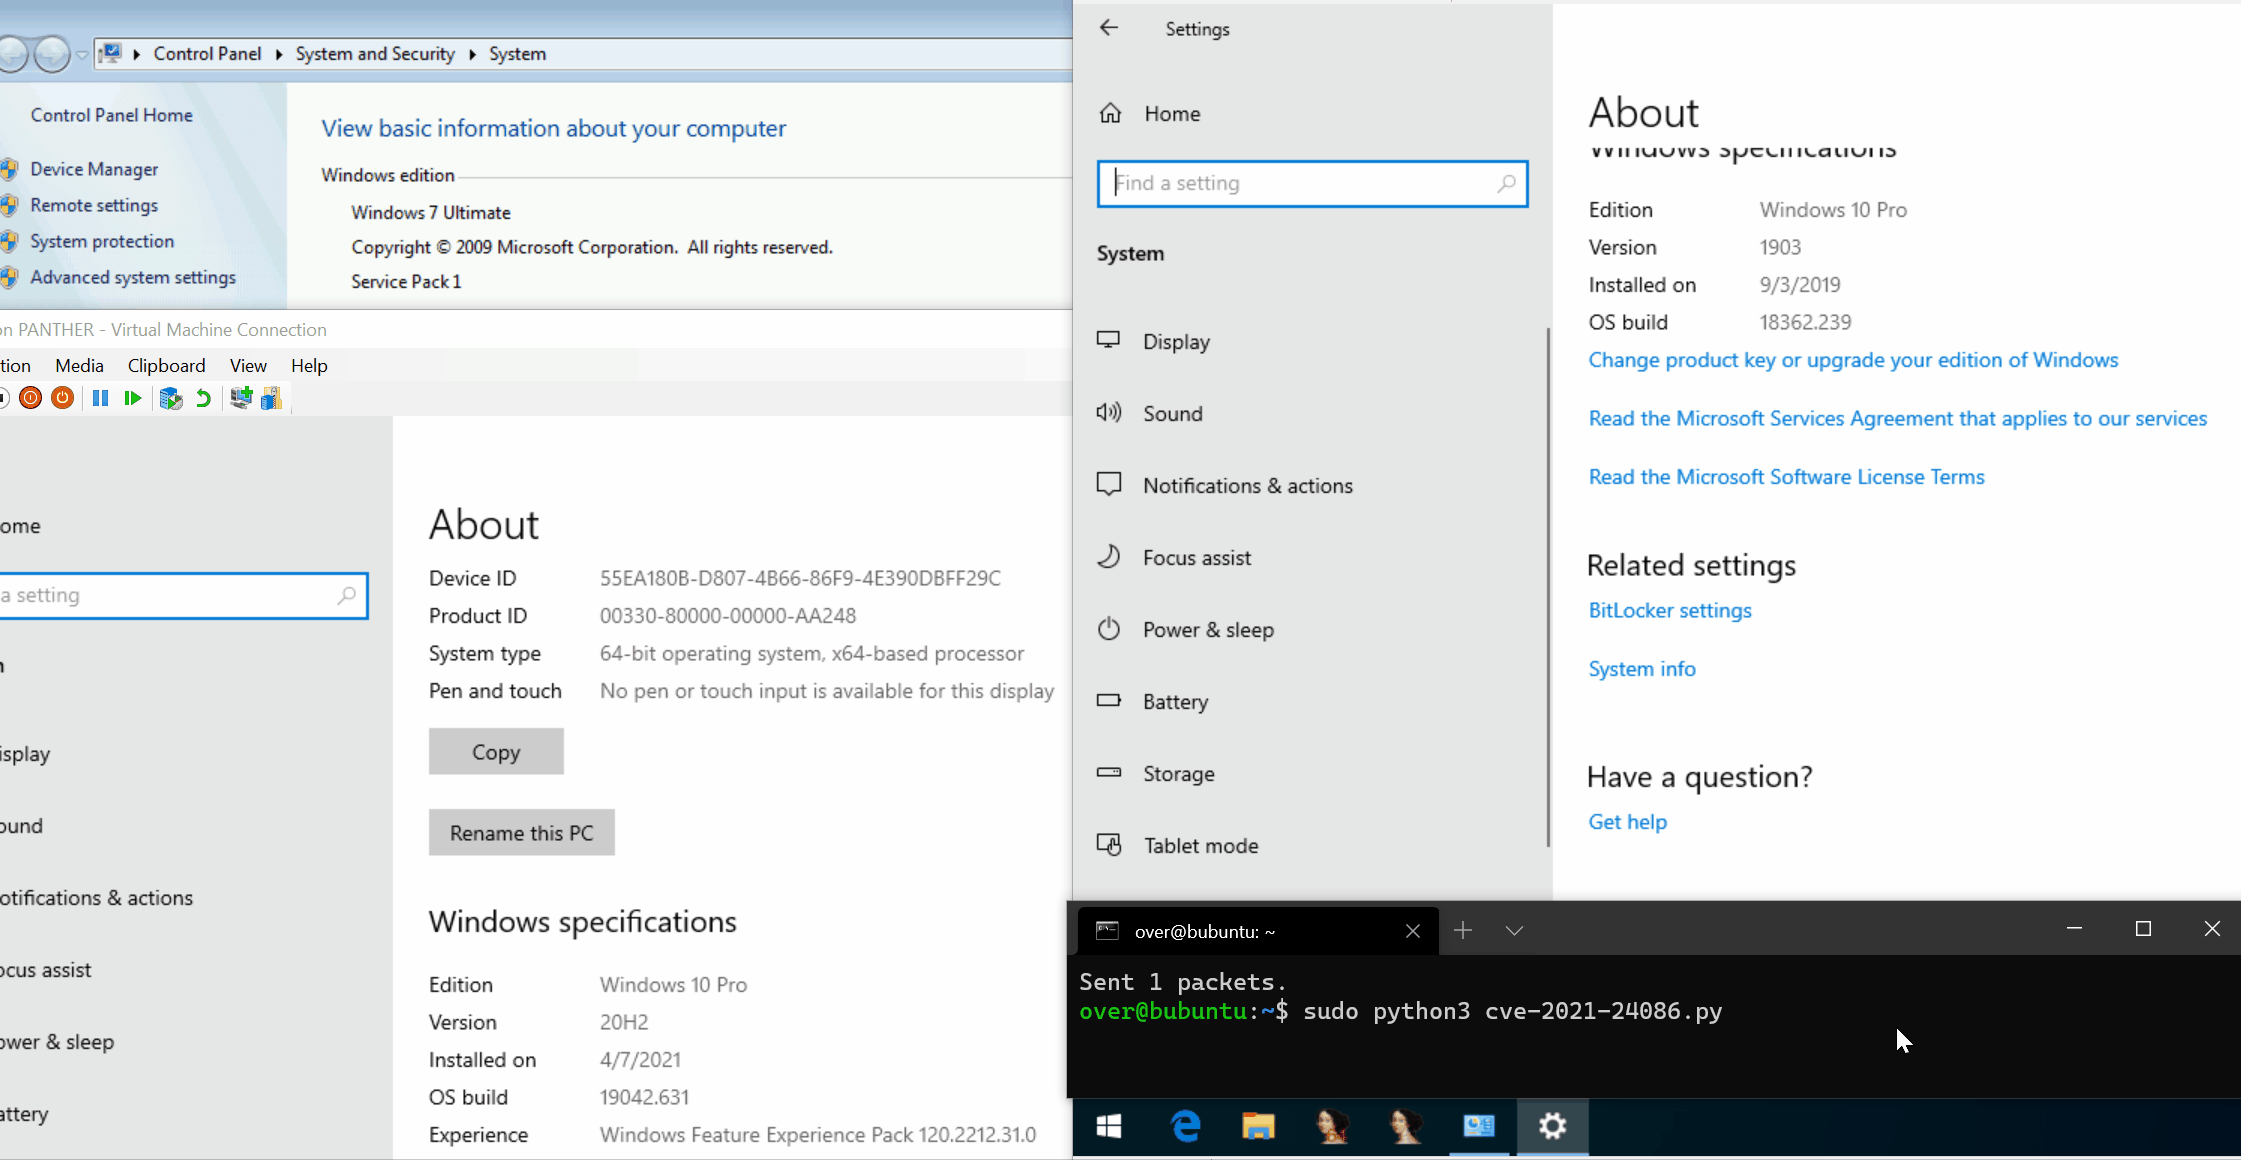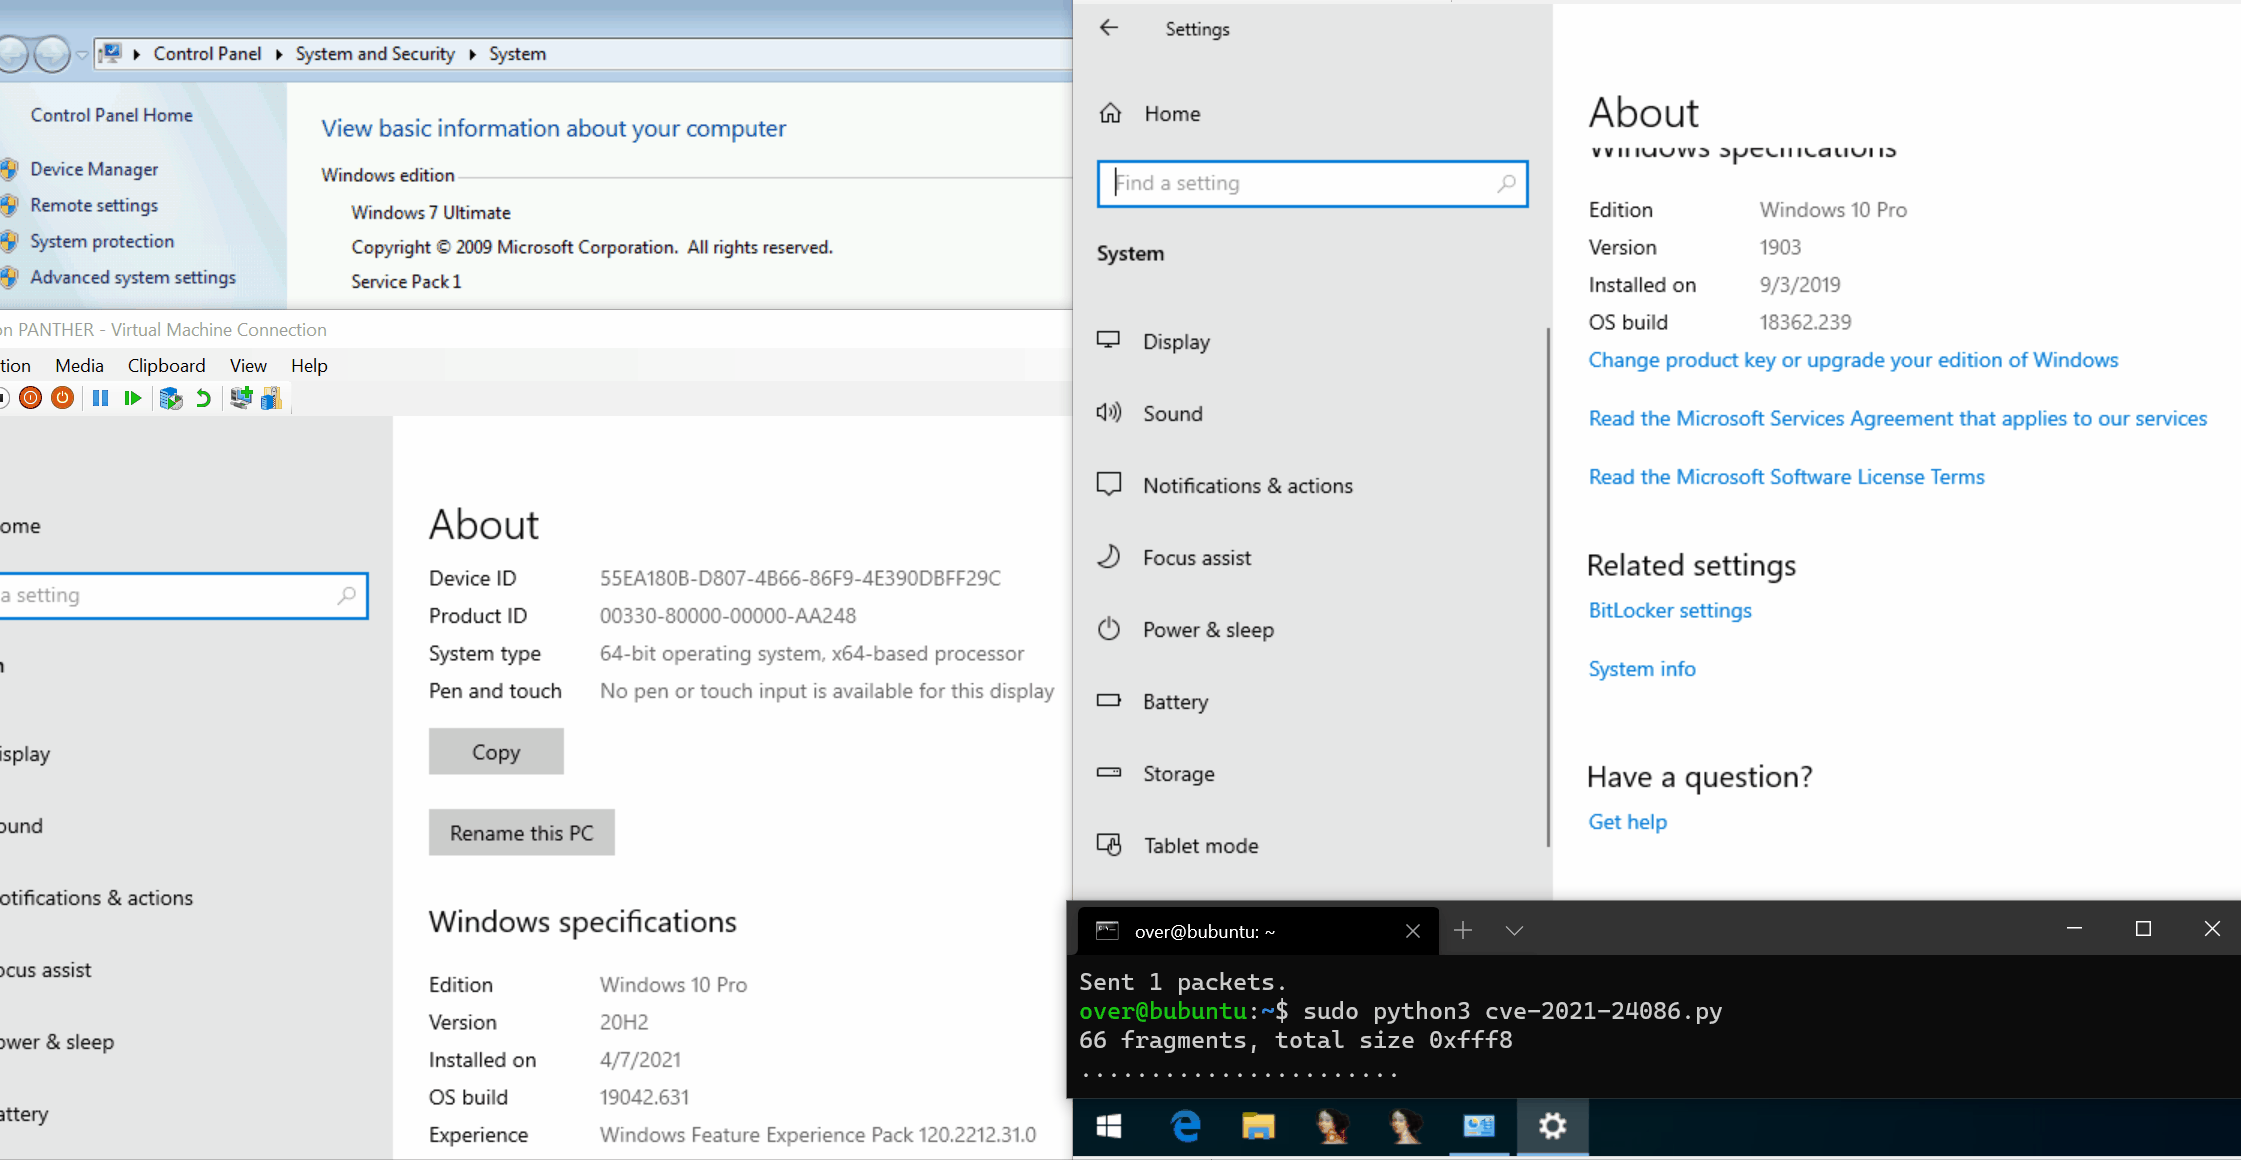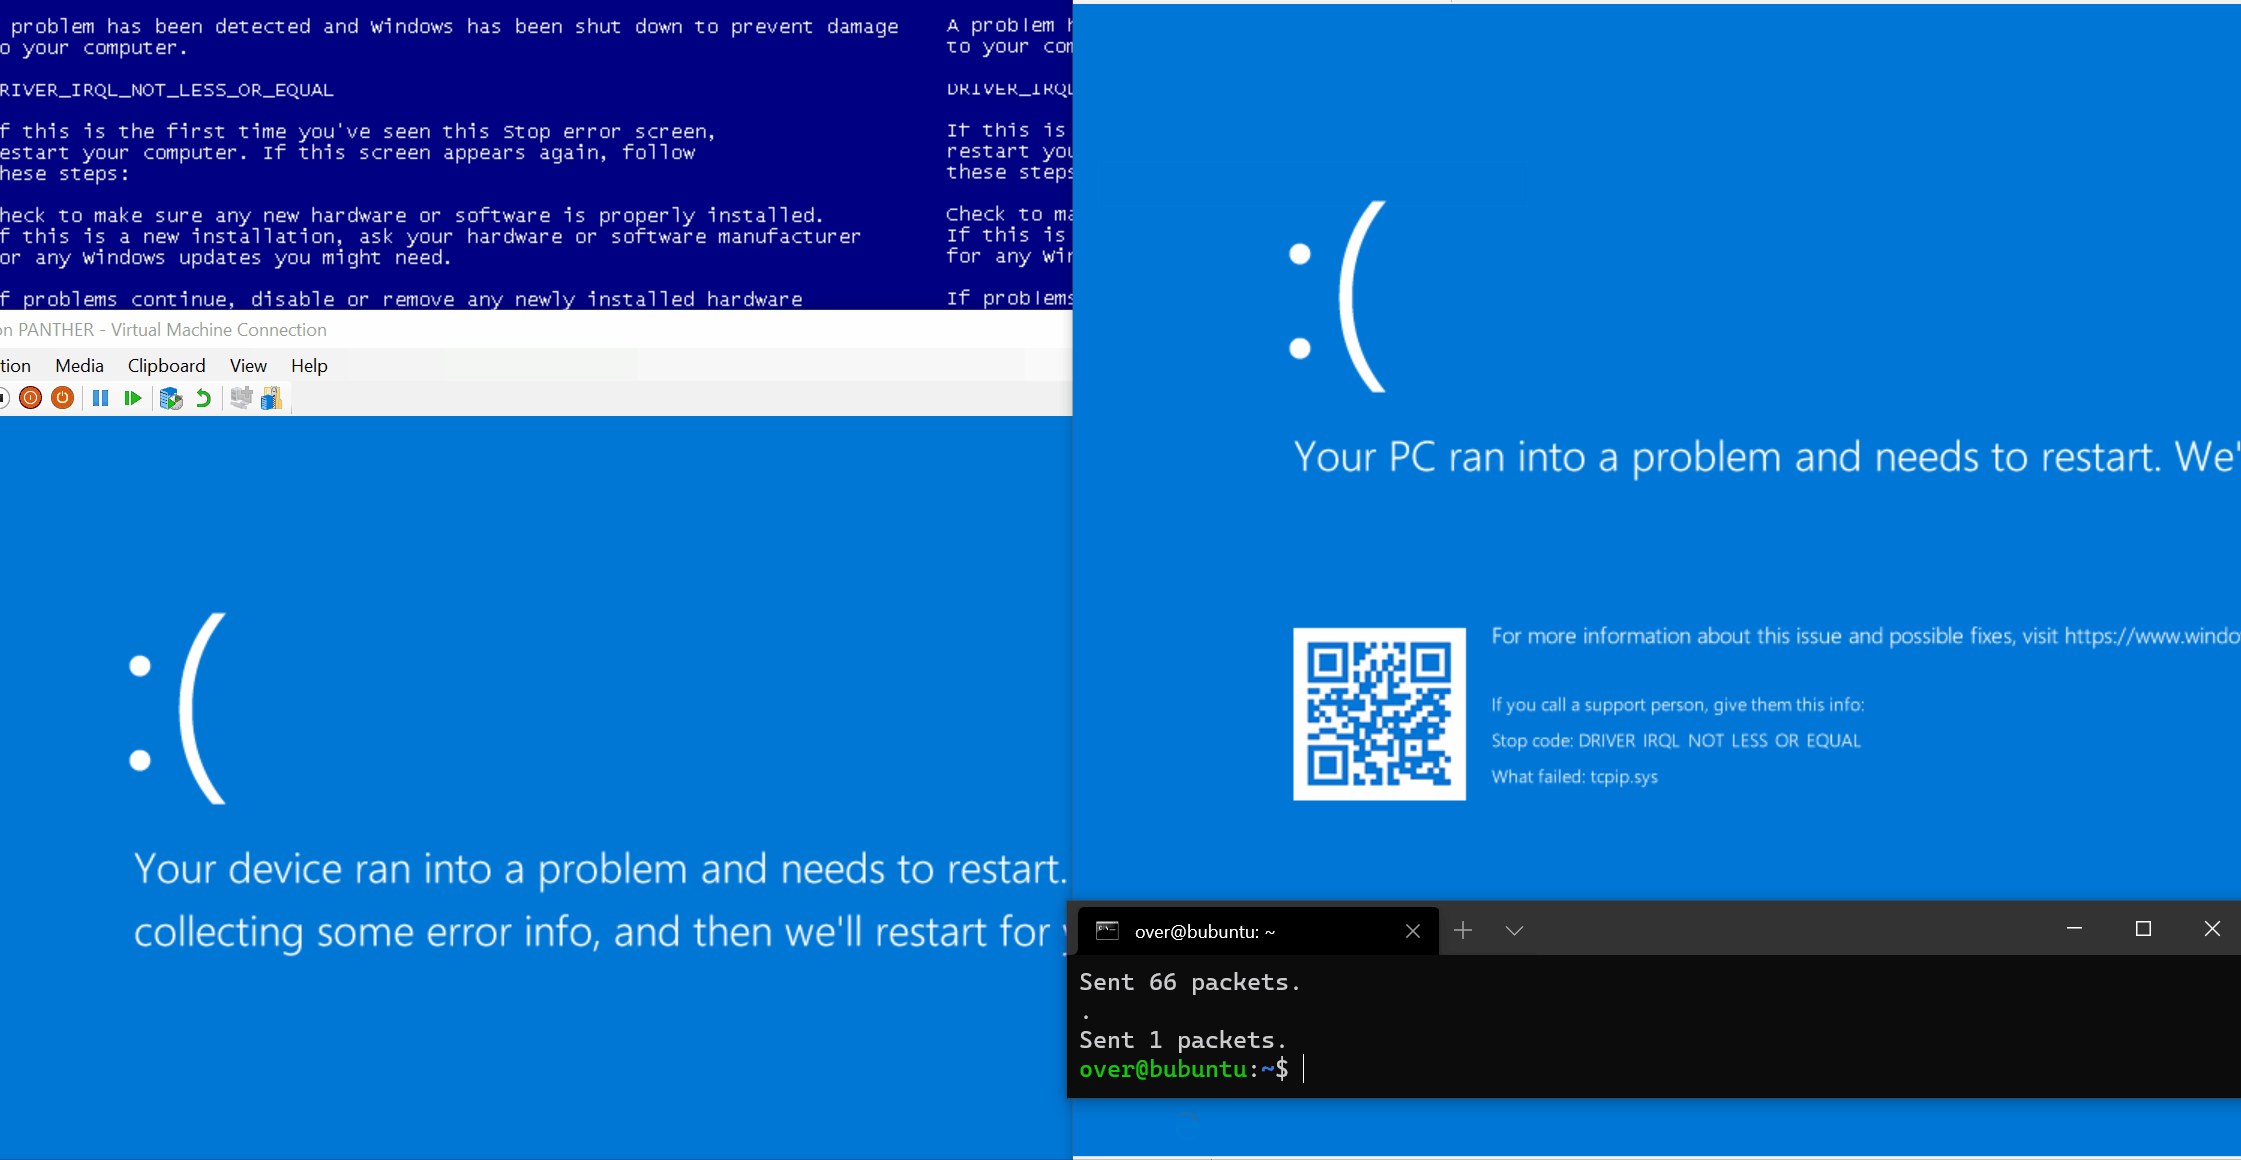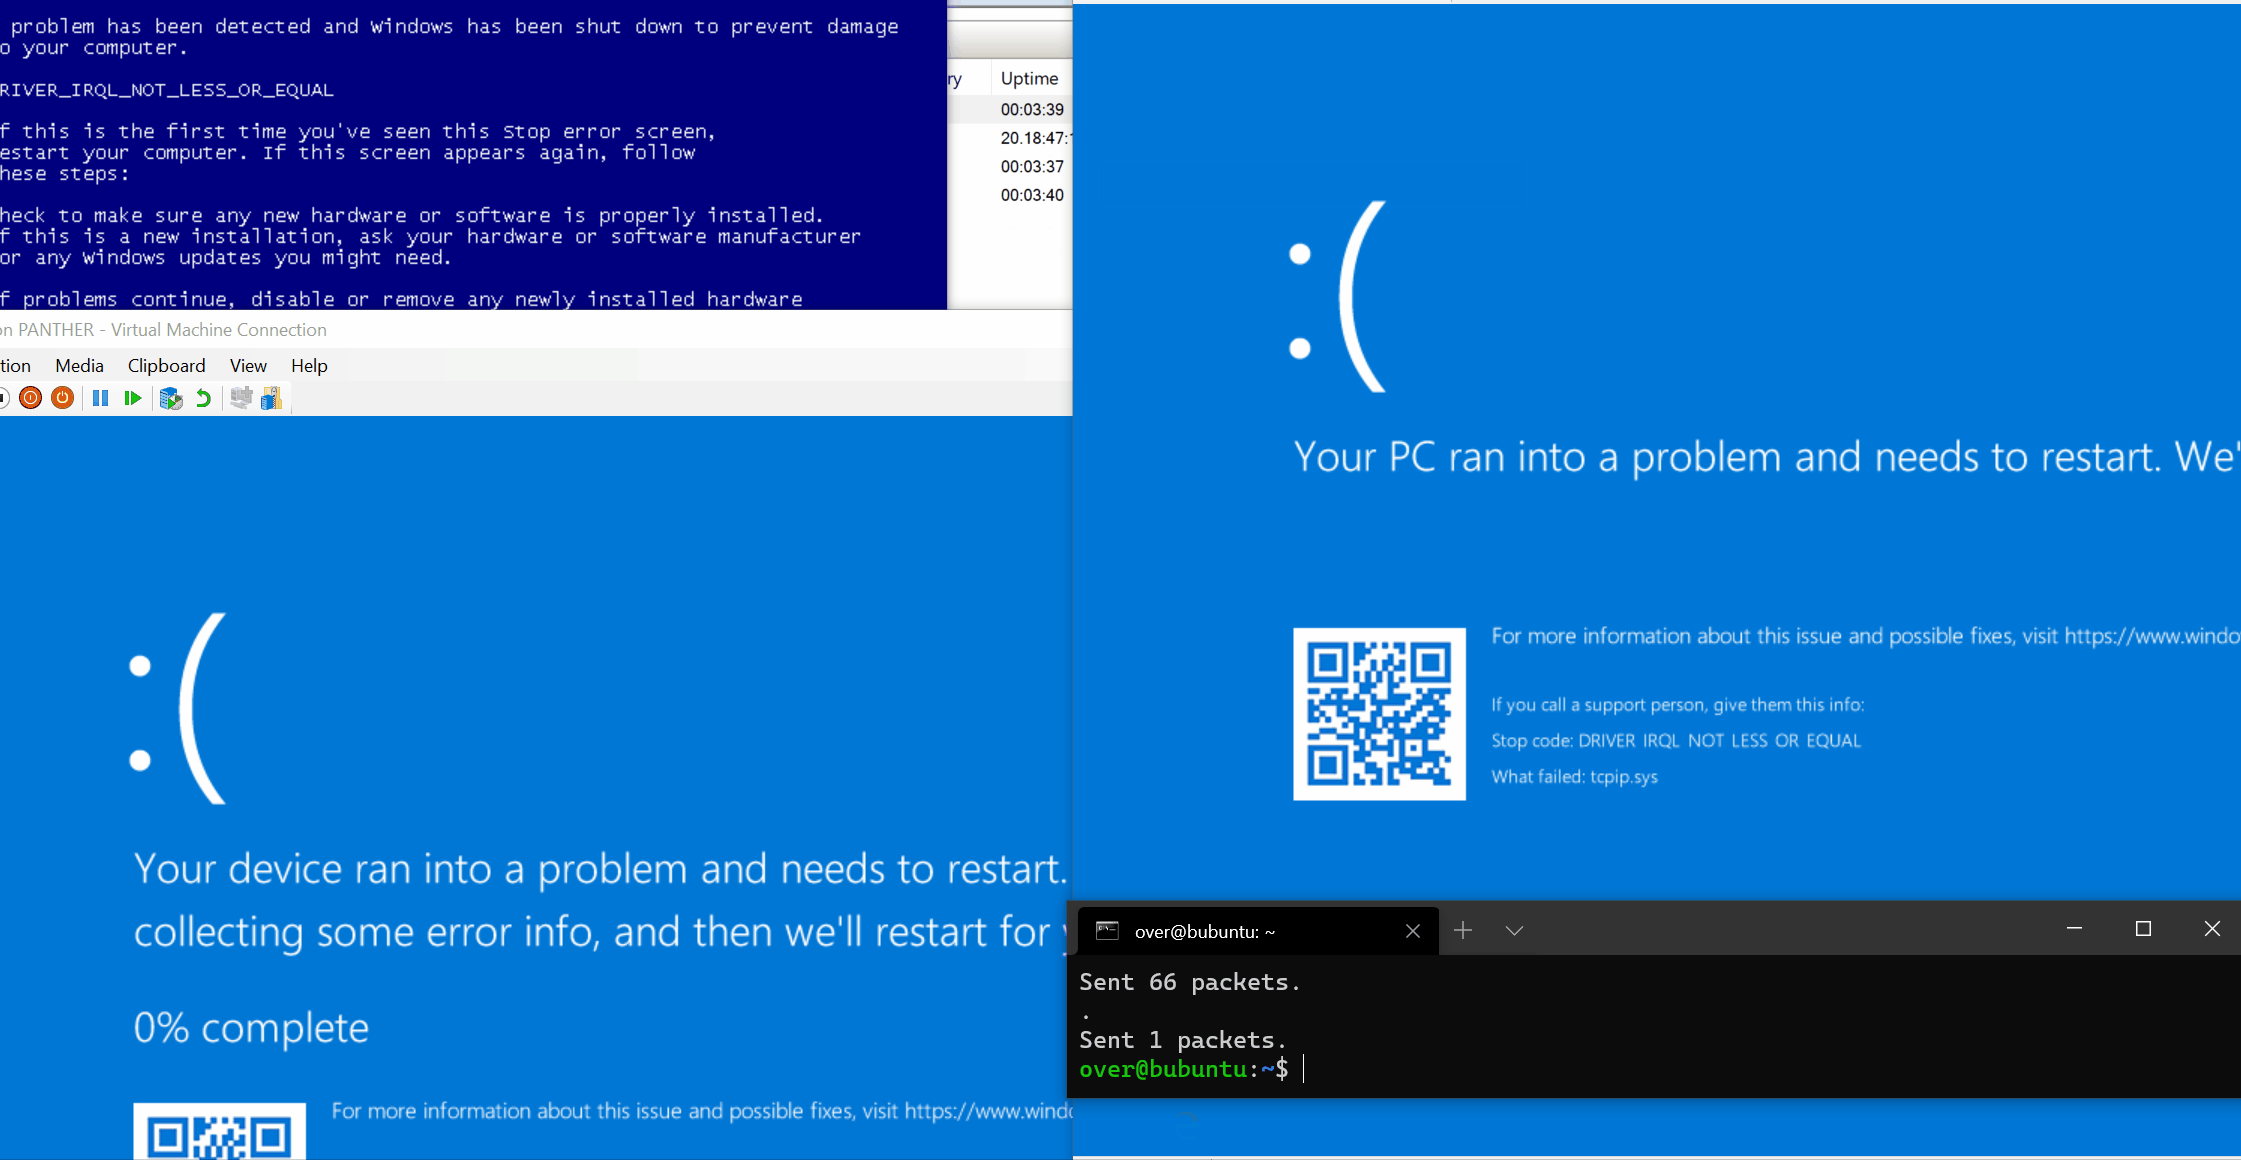
Proof-of-concept exploit for CVE-2021-24086, a NULL dereference in tcpip.sys causing remote denial of service via malicious UDP packets over IPv6.

This script test the CVE-2021-26855 vulnerability on Exchange Server.

Proof of concept for CVE-2021-24086, a NULL dereference in tcpip.sys triggered remotely.

PoC for CVE-2021-28476 a guest-to-host "Hyper-V Remote Code Execution Vulnerability" in vmswitch.sys.

Portfolio lab documenting MSMQ vulnerability (CVE-2023-21554) with detection rules, network capture evidence, mitigation planning, and patch…

Proof-of-concept demonstrating command injection in Windows Notepad via crafted Markdown links, enabling remote code execution. Includes attack…

Python library for auditing Microsoft Active Directory via LDAP, supporting NTLM, Kerberos, SSPI authentication, channel binding, encryption, and…

CVE-2024-38200 & CVE-2024-43609 - Microsoft Office NTLMv2 Disclosure Vulnerability

KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…