
pentest-a2p2v-core
 pentest-a2p2v/pentest-a2p2v-core
Core A2P2V functionality (command line based)
exploit-frameworkspenetration-testingvulnerability-analysis
pentest-a2p2v/pentest-a2p2v-coreCore A2P2V functionality (command line based)
 owasp/odtm
OWASP Ontology-driven Threat Modelling framework
 karmahostage/gethspoit
Finding Ethereum nodes which are vulnerable to RPC-attacks
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 jeffaf/cve-2026-32746
CVE-2026-32746 - GNU InetUtils telnetd LINEMODE SLC Buffer Overflow PoC (pre-auth RCE, CVSS 9.8)
 corelight/ripple20
A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.
 xmzyshypnc/cve-2021-30551
my exp for chrome V8 CVE-2021-30551
 breaktoprotect/cve-2017-16778-intercom-dtmf-injection
A coordinated disclosure and security advisory on Fermax Intercom DTML Injection vulneraiblity. Special thanks to Fermax International for prompt…
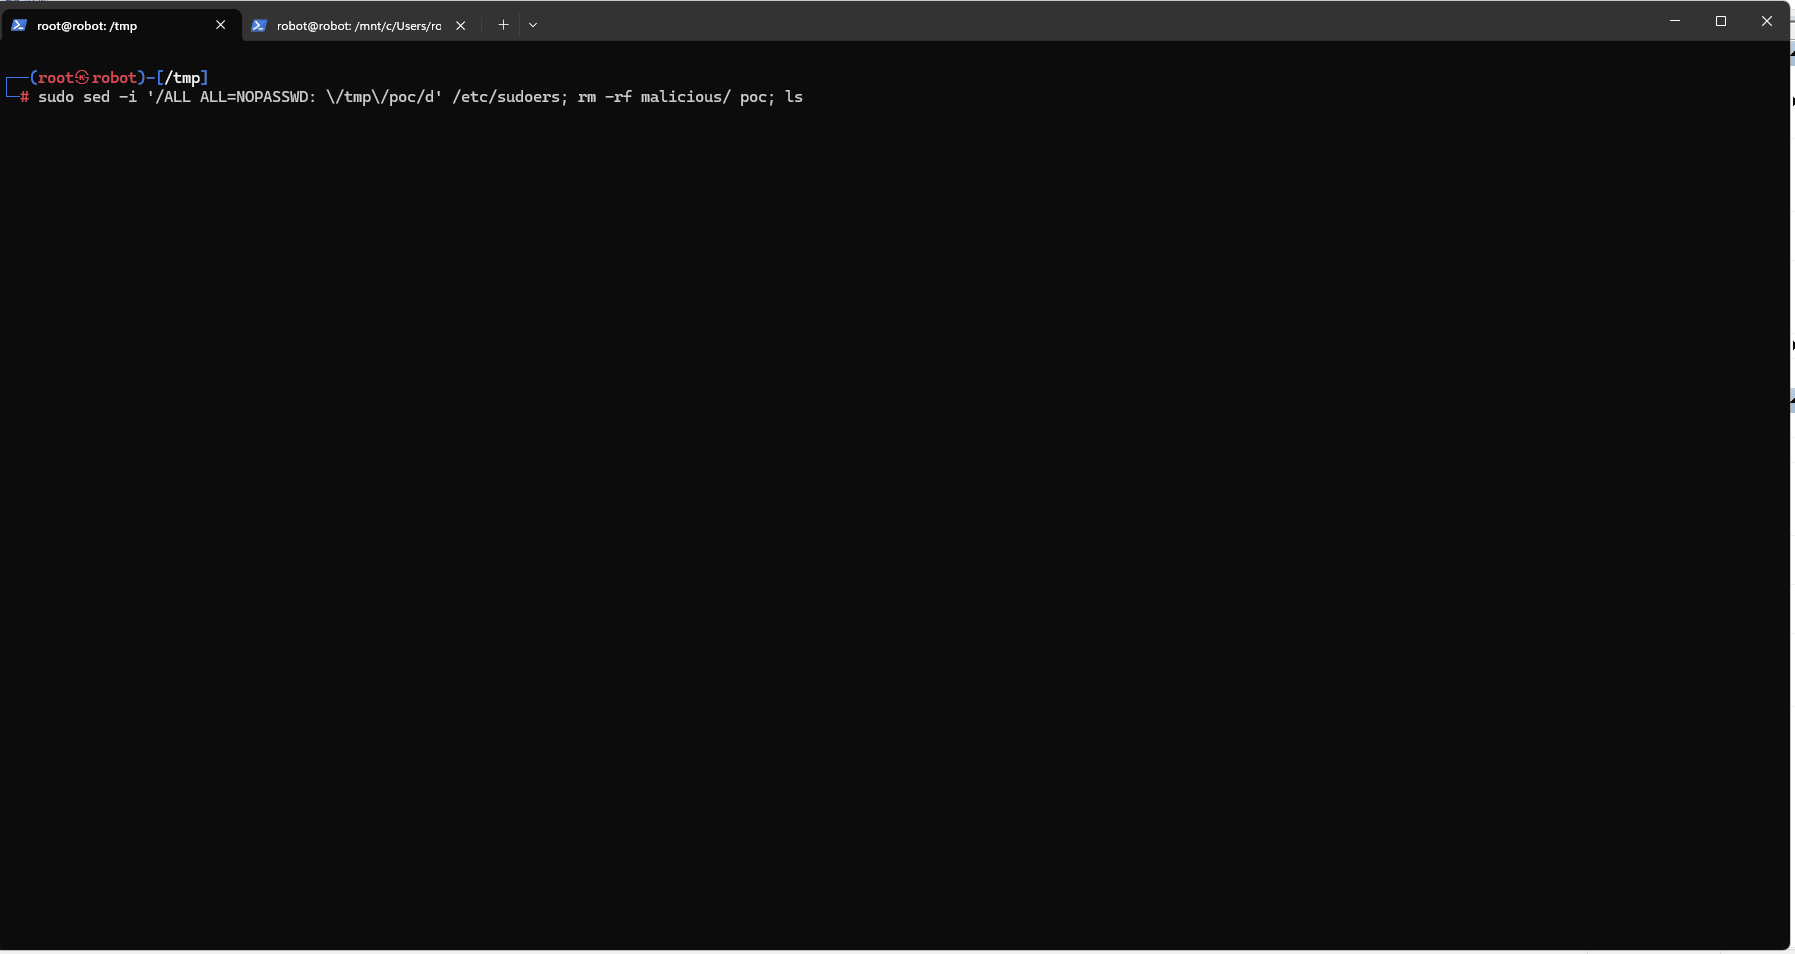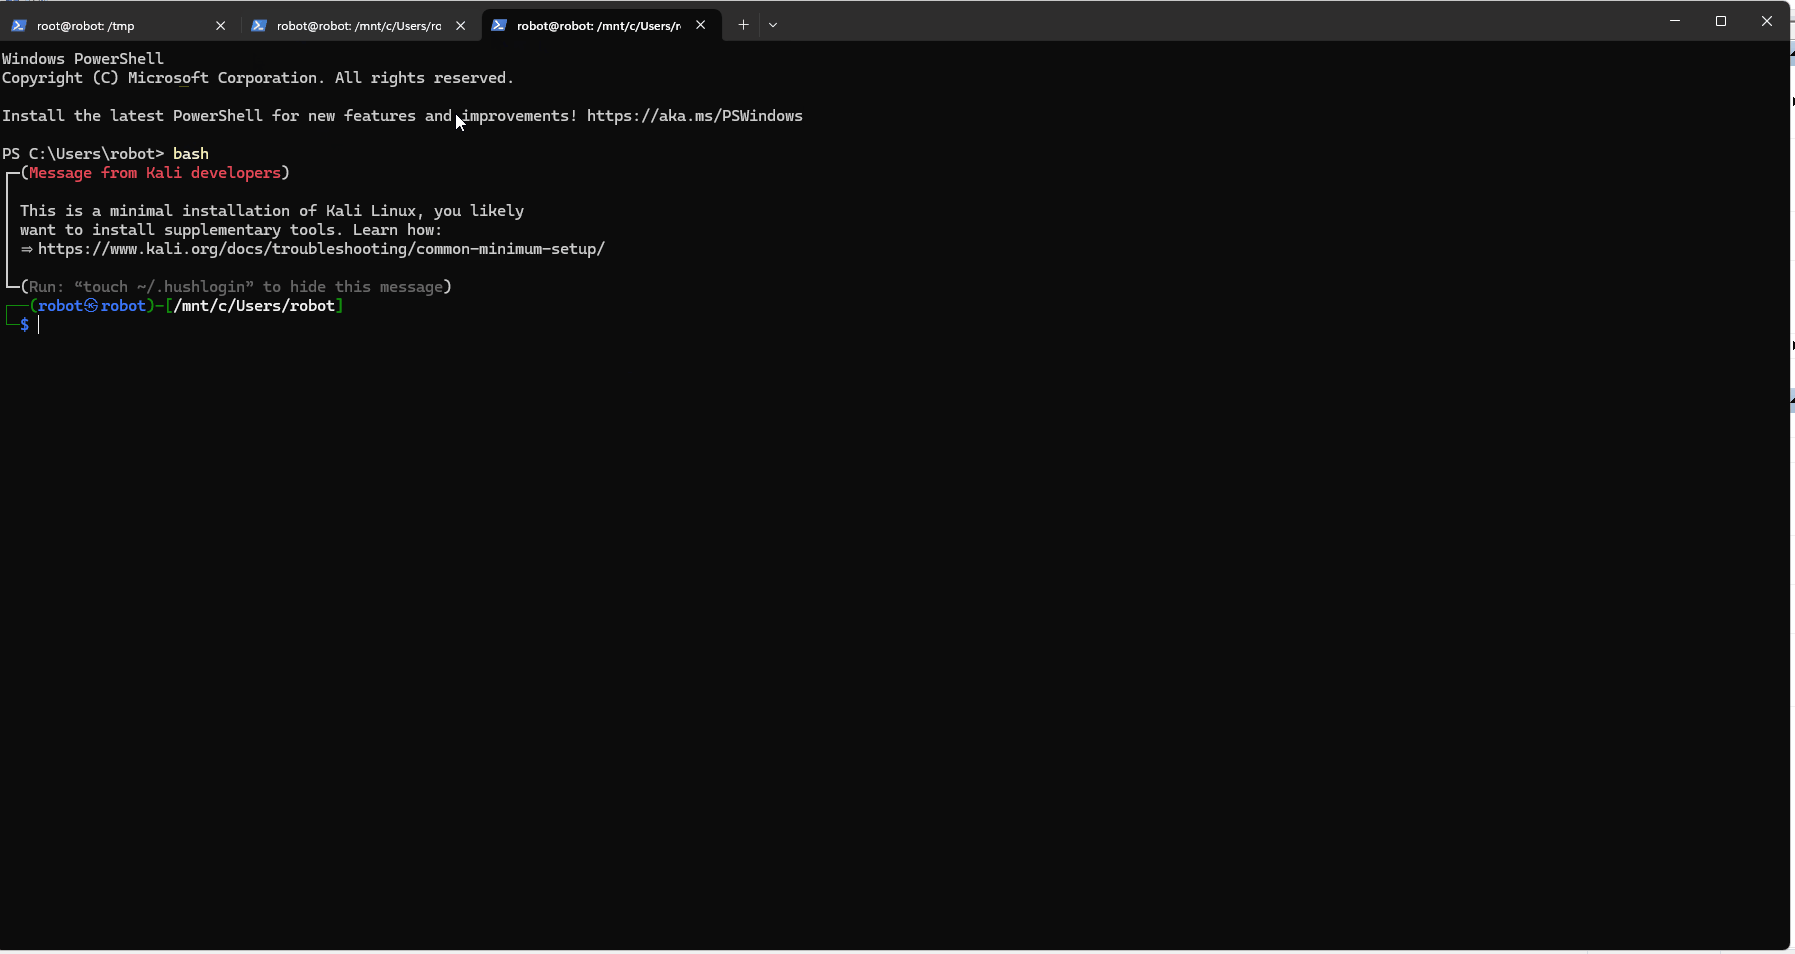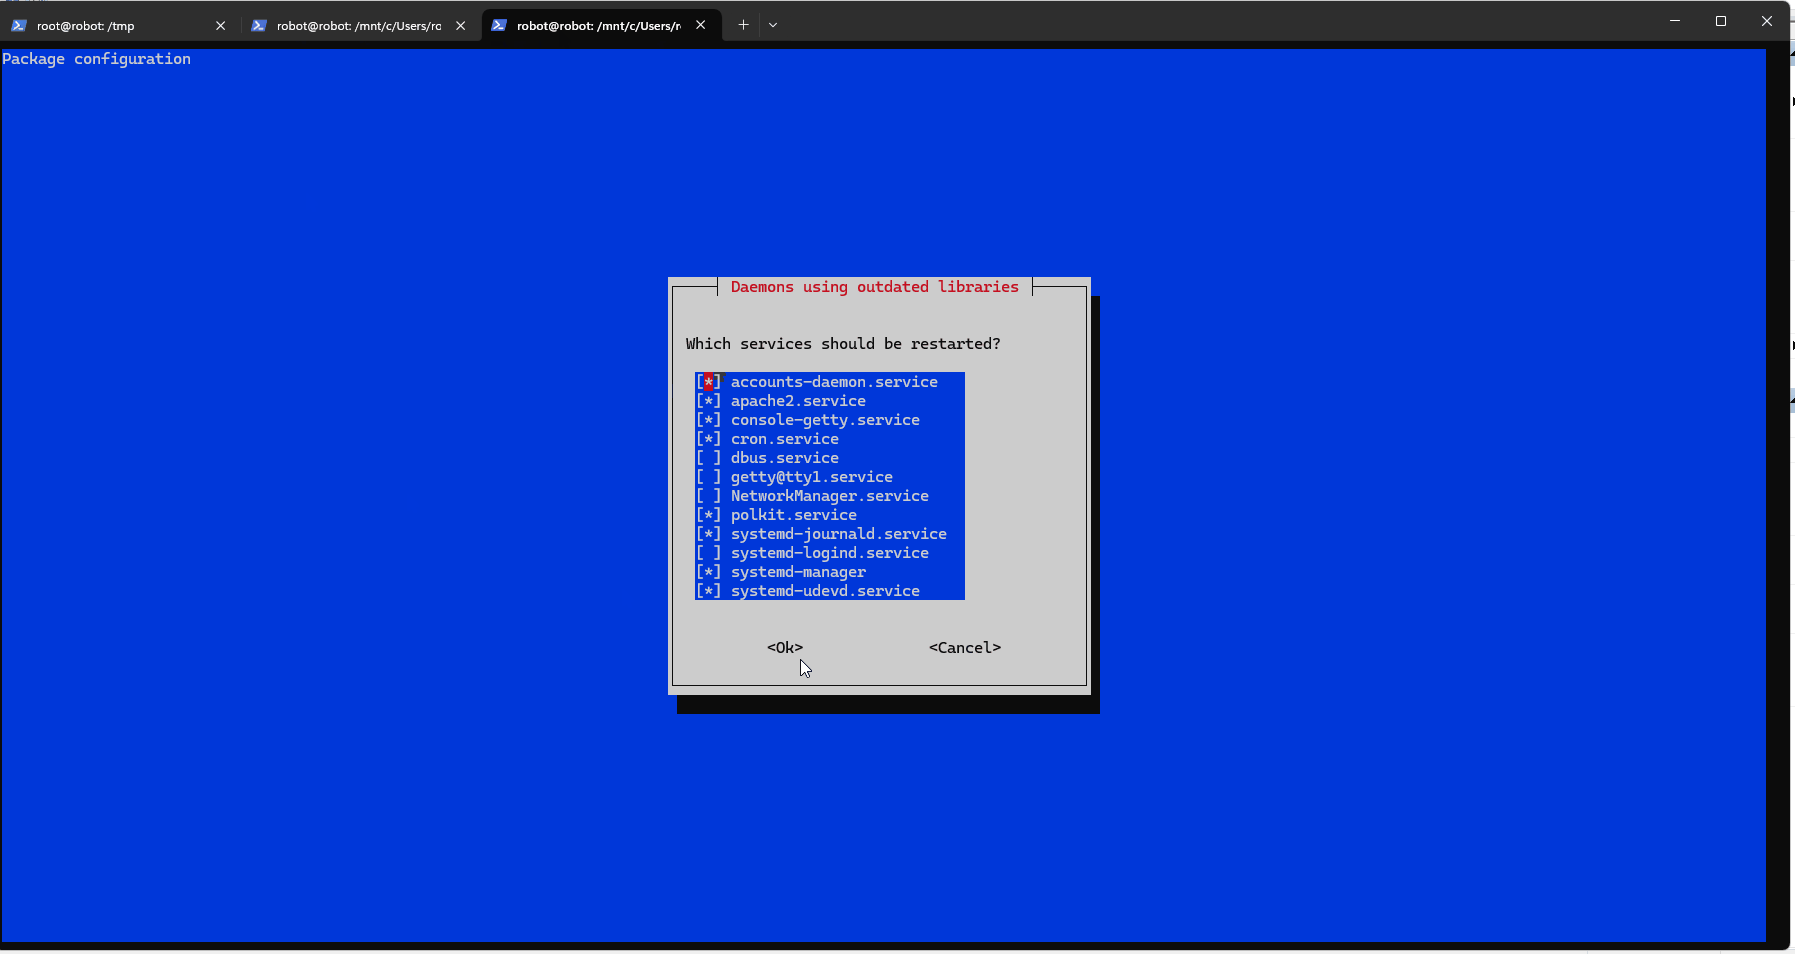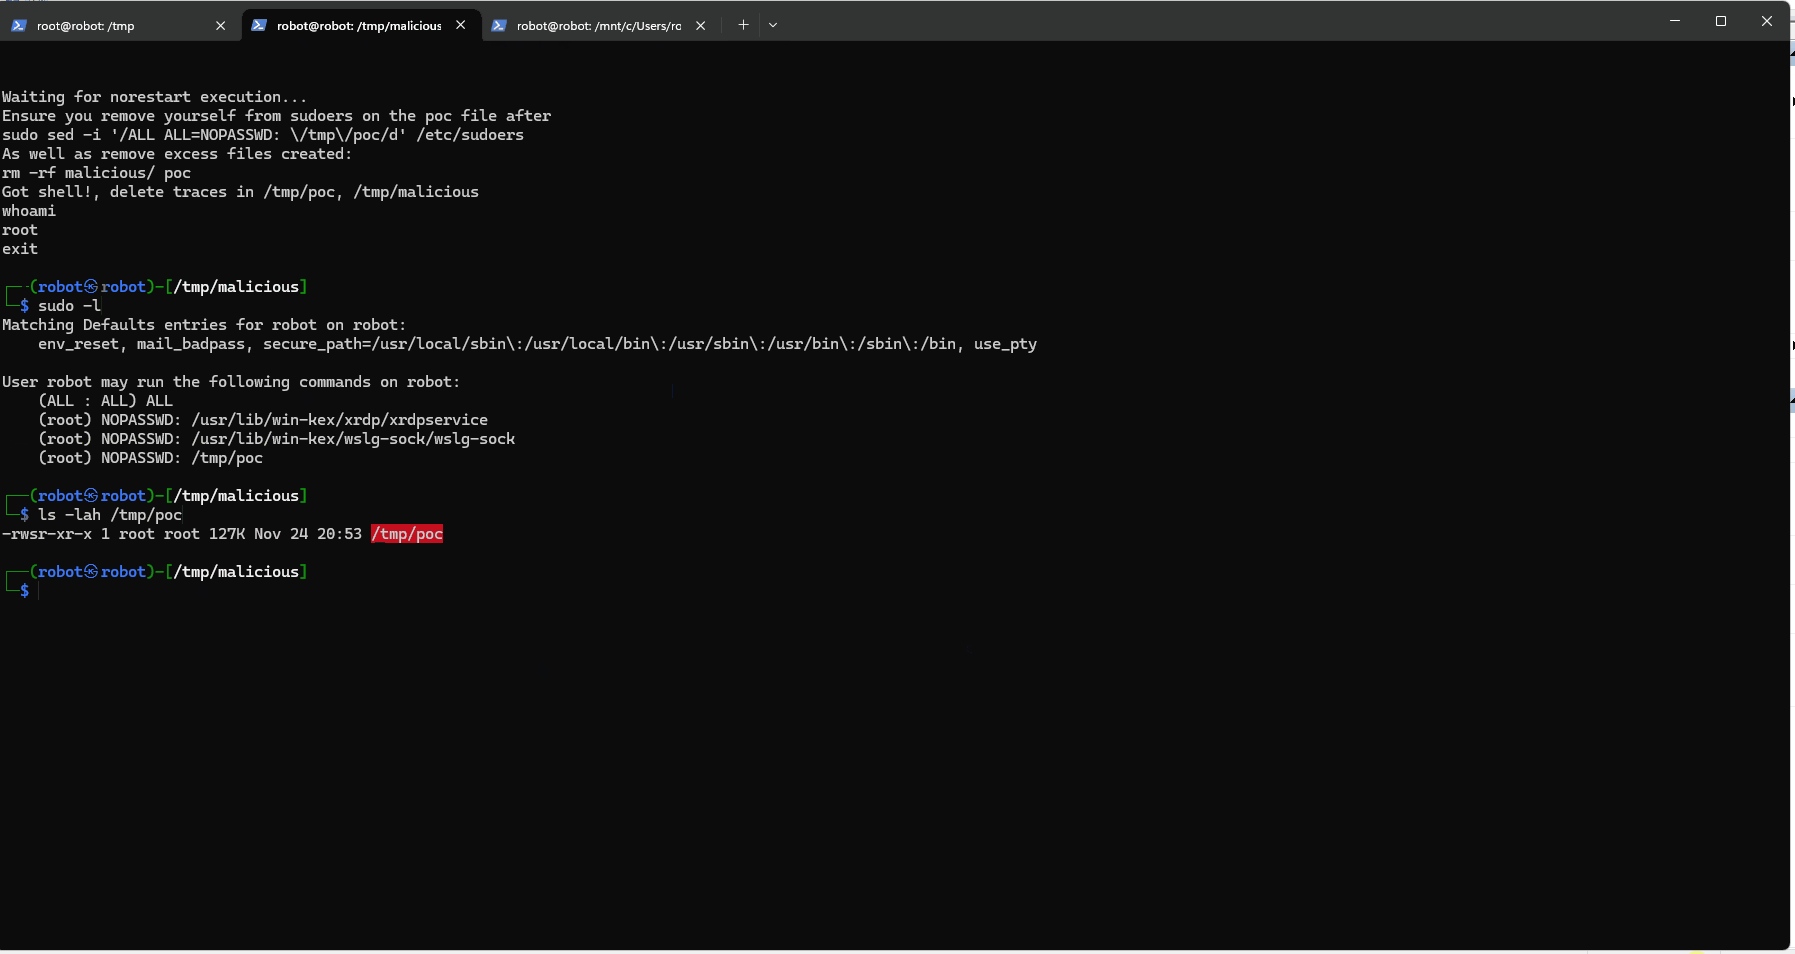 pentestfunctions/cve-2024-48990-poc-testing
Testing POC for use cases
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
 cfielding-r7/poc-cve-2023-2868
Ruby-based proof-of-concept exploit for CVE-2023-2868 command injection in Barracuda ESG, delivering a reverse shell for targeted penetration testing.
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 philfry/cve-2026-31431-ftrace
Kernel module using ftrace to block AF_ALG/AEAD requests, mitigating CVE-2026-31431 without requiring LSM BPF. Provides logging and easy compilation…
 duality084/cve-2023-33381-mitrastar-gpt-2741gnac
Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…
 andripwn/django_cve201919844
PoC for CVE-2019-19844 ( https://www.djangoproject.com/weblog/2019/dec/18/security-releases/ )
 muyuanlove/cve-2025-6018-cve-2025-6019-privilege-escalation-exploit
CVE-2025-6018 + CVE-2025-6019 Privilege Escalation Exploit
 bluefrostsecurity/cve-2021-28476
Proof-of-concept exploit for CVE-2021-28476, a Microsoft Hyper-V vmswitch vulnerability allowing attacker-controlled pointer dereference and…
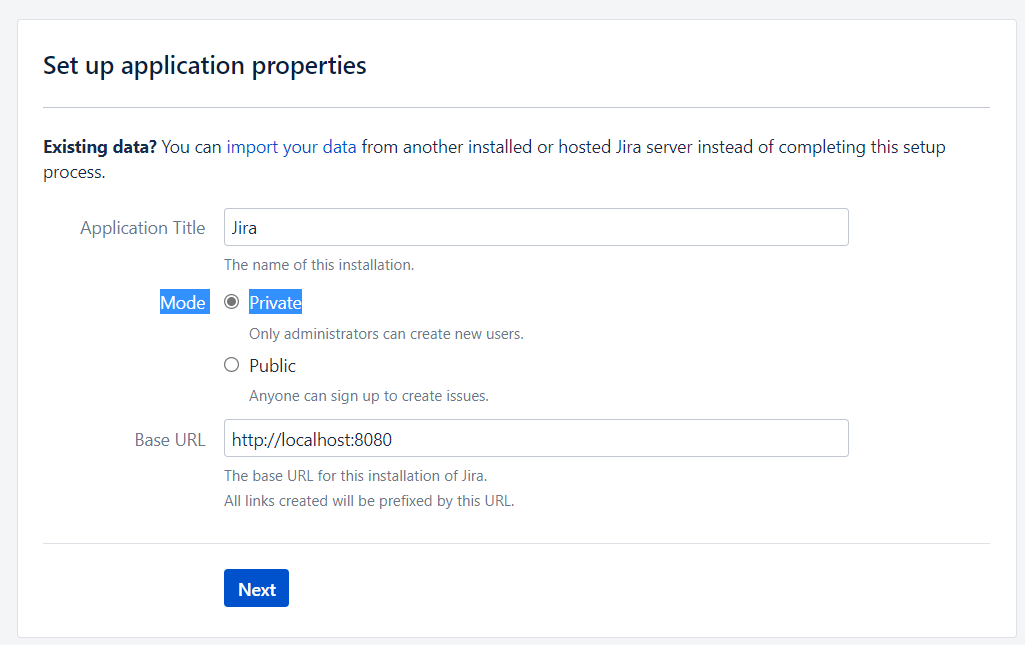 petrusviet/cve-2019-11581
Atlassian Jira unauthen template injection