

lynis
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
configuration-auditingdatabase-securitydefensive-tools+5
16.1k
cisofy/lynisAgentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
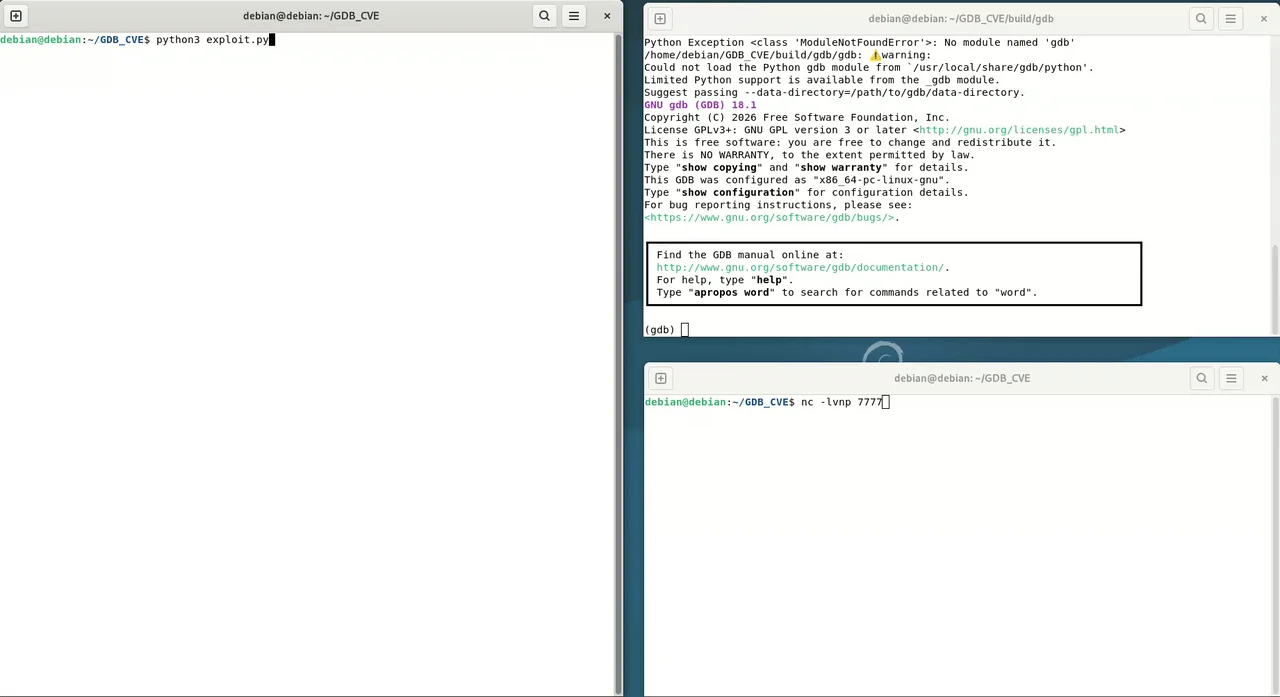 deebumg/cve-2026-121994-poc
Weaponized proof-of-concept for CVE-2026-121994: a fake GDB remote debug stub that sends a malicious p-packet to trigger memory corruption and a…
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 wvllxe/cve-2026-100520-laranode-path-traversal
Path Traversal -> RCE in Laranode < 1.2.1 (CWE-22). PoC + advisory writeup.
 pentestershell/cve-2026-116779
Python PoC for CVE-2026-116779: unauthenticated OS command execution in FreeSWITCH via the SIP MESSAGE api chat handler, with arbitrary API command…
 eqstlab/cve-2026-111497
Proof-of-concept exploit for CVE-2026-111497 (Node2Shell) that triggers remote code execution via a crafted upload and delivers a reverse shell, with…
 e4zyy/project-cve-2026-75604
Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…
 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
 mushr00w/cve-2026-116512
Python exploit for CVE-2026-116512, an unauthenticated RCE in weDevs Project Manager <= 4.1.1, with single or bulk target scanning, threading, and…
 decker757/cs440-langgraph-nosql-demo
Local classroom demo of NoSQL operator injection in LangGraph's MongoDBSaver (GHSA-98xf-r82g-9mhx / CVE-2026-48121). Fictional data only.
 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 carterlasalle/cve-2026-122051
Python PoC driver for CVE-2026-122051, a pre-auth command injection in the Edimax BR-6208AC /goform/mp handler, with firmware emulation recipe, bulk…
 ahmadf77/cve-2026-23744
Python exploit script for CVE-2026-23744 that delivers a reverse shell to a specified target URL, requiring a netcat listener for command-and-control.
 godylockz/cve-2024-42327
POC for CVE-2024-42327: Zabbix Privilege Escalation -> RCE
 godylockz/cve-2021-44967
Proof-of-concept exploit for CVE-2021-44967 enabling remote code execution in LimeSurvey 5.2.4 via malicious plugin upload, with reverse shell…
 r3vpwnx/cve-2025-55182
Standalone exploit for CVE-2025-55182 achieving unauthenticated RCE in Next.js App Router via React Server Components Flight deserialization, with…
 shouvikkkk/oauth-sink-check
Trace untrusted OAuth endpoint URLs from source to shell sink — the CVE-2026-119025 attack class, checked in your code, lockfile and MCP configs.
 eqstlab/cve-2026-109619
Proof-of-concept exploit for PHP session.upload_progress pre-auth RCE (PHP2Shell), with heap/ASLR leak, per-build offset profiles, and an all-in-one…