pocindex
 0xmarcio/pocindex
Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
curated-resourcesexploitationexploit-frameworks+5
1.5k
0xmarcio/pocindexSearch public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
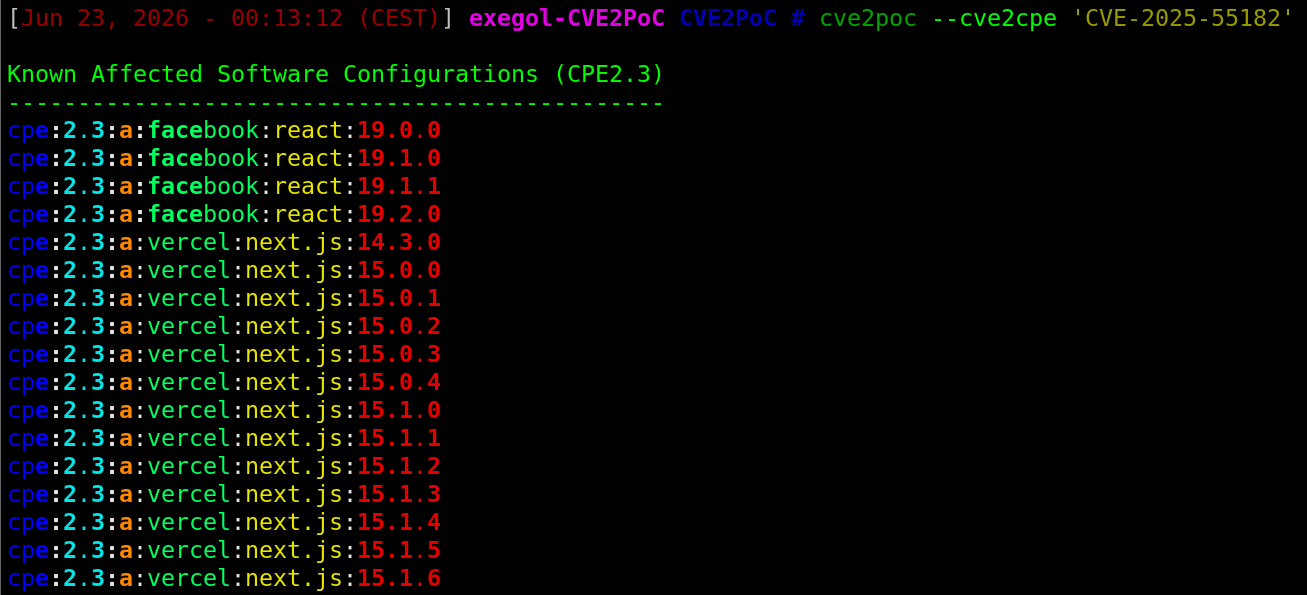 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 projectdiscovery/awesome-search-queries
Community curated list of search queries for various products across multiple search engines.
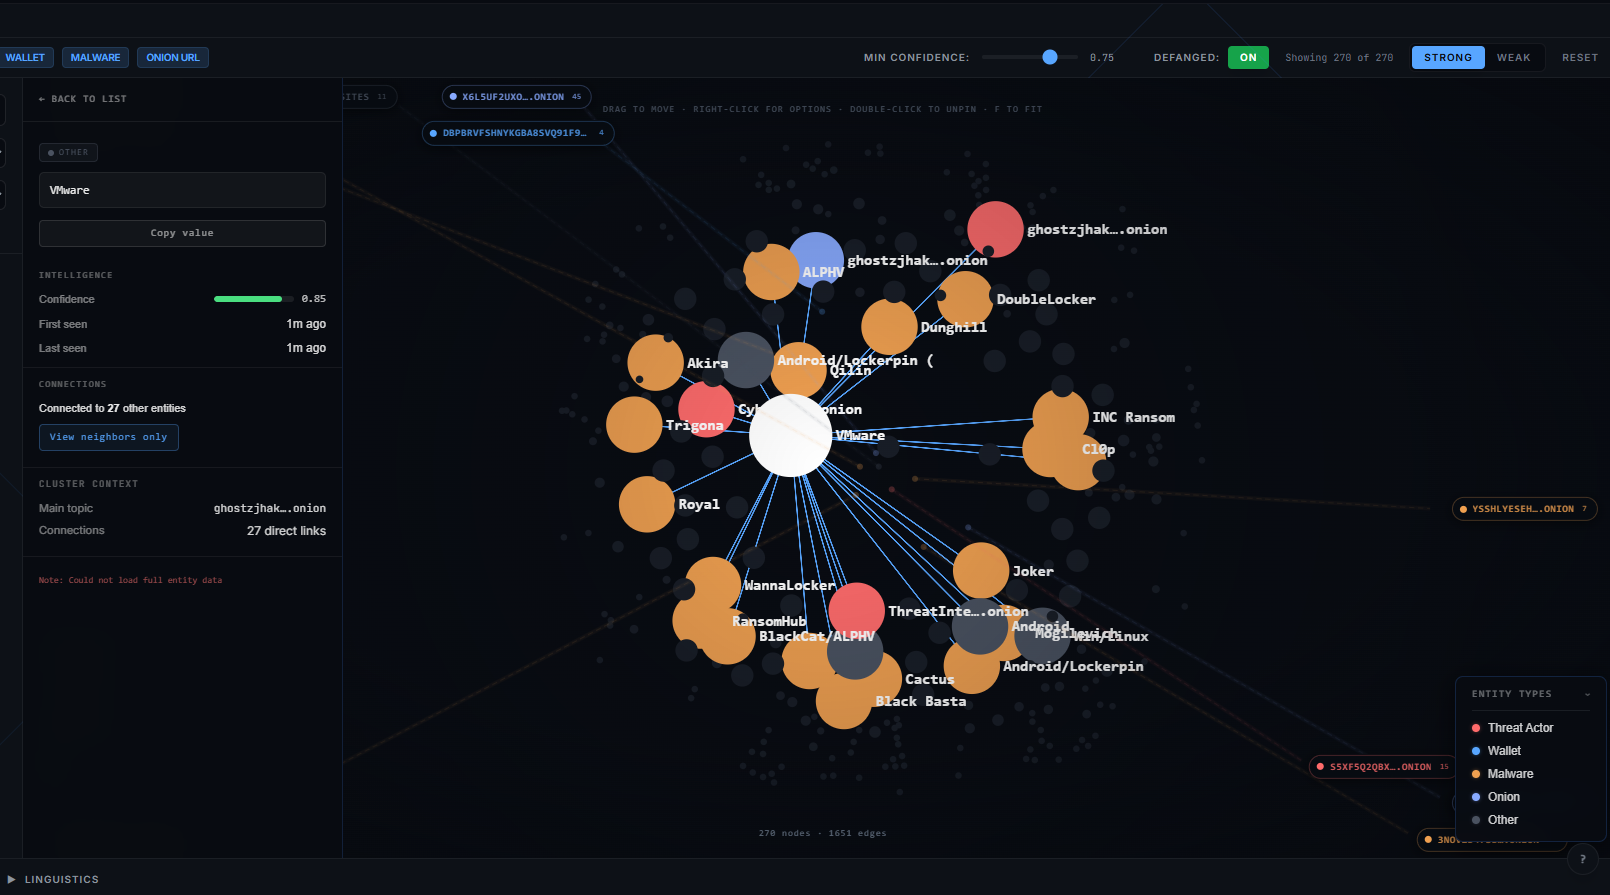 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 edoardottt/awesome-hacker-search-engines
A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty
 haitam-lazaar/libextractor-privesc
Proof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…
 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
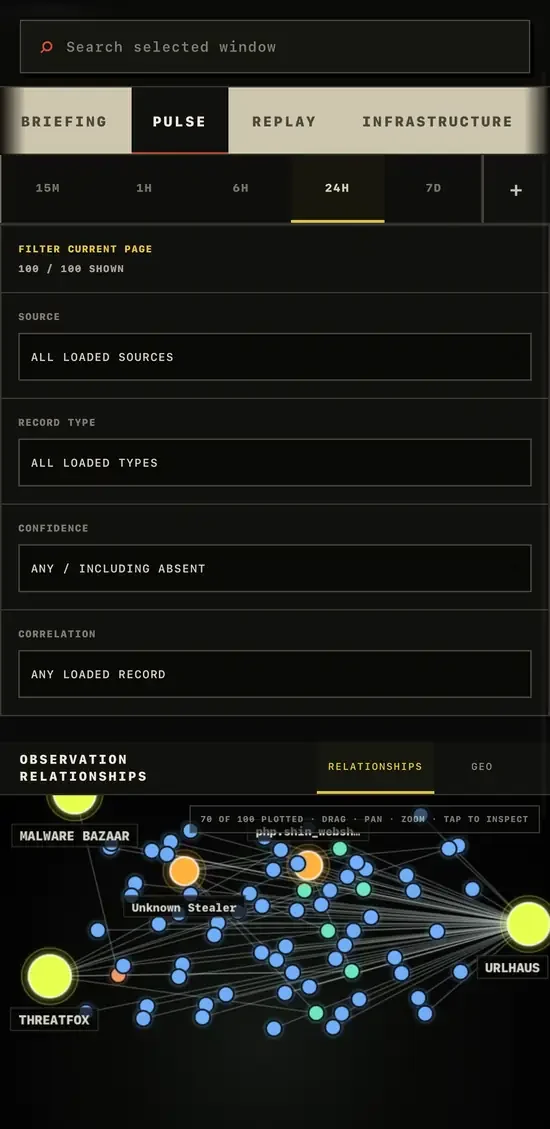
 gnomeman/badbanana-threat-observatory
Threat intel observatory aggregating CISA KEV, ThreatFox, URLhaus, and MalwareBazaar feeds with search, change tracking, and STIX/CSV/JSONL export.
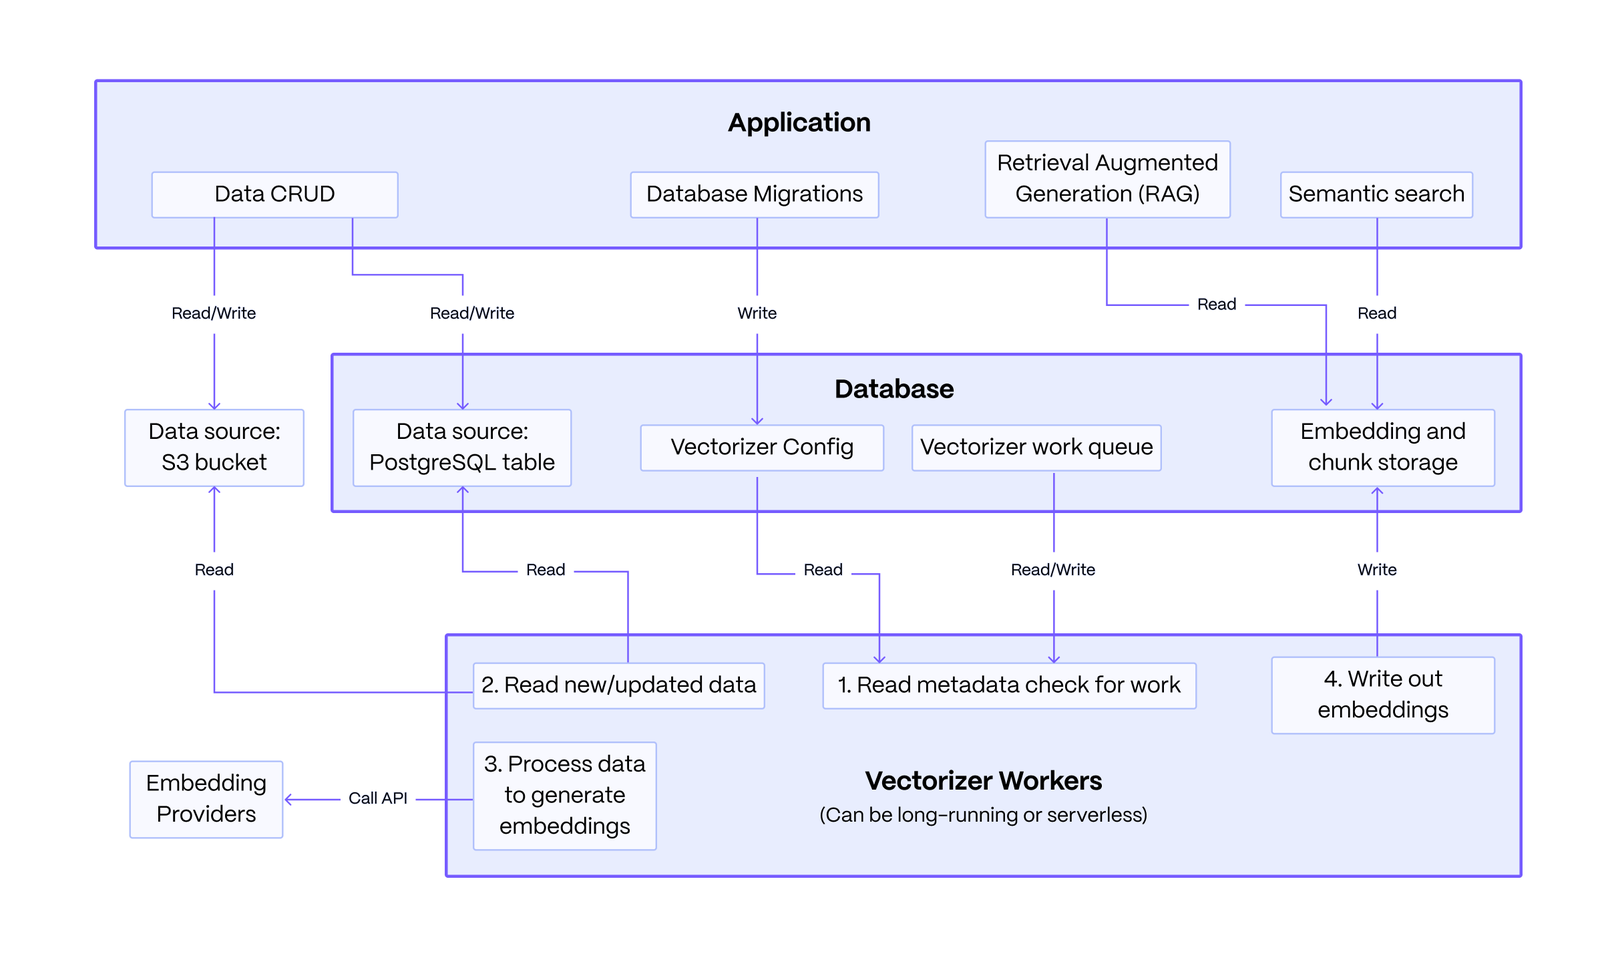 pvharmo2/gha-lab-e8902eccd3
Security research lab: reproduction of CVE-2025-52467 (pgai pull_request_target workflow code execution / GITHUB_TOKEN exfiltration) — snapshot of…
 george0papasotiriou/cve-2026-5050-blind-ldap-injection-via-unescaped-filter
Reproduces CVE-2026-5050 with a simulated Flask LDAP server and exploit script, demonstrating blind LDAP injection via unescaped filters to bypass…
 anthropics/cryptography-research-demo
Reproducible cryptanalysis artifacts for single-key recovery attacks on reduced-round AES, including black-box key recovery, DDT-Gray search, S-box…
 0xmrma/cve-2026-33146
A public share looked clean in the page tree, but the search endpoint told a different story. In Docmost, restricted child pages hidden from public…
 inertfluid/sk-cve-2026-26030-lab
Ethical, network-isolated Docker lab reproducing CVE-2026-26030 — Semantic Kernel in-memory vector store filter eval() RCE (patched in 1.39.4)
 ex-cal1bur/cve-2026-42568
An LDAP injection vulnerability exists in org.yamcs.security.LdapAuthModule. The username parameter is inserted directly into LDAP search filters…
 mrtdlgc/goodoldsearch-oss
Local static query builder for precise search across web engines, Shodan, crt.sh, and Wayback Machine. Supports Google dorks, filetype filters, date…