

ModSecurity
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
anti-botapi-securitydefensive-tools+7
9.8k
owasp-modsecurity/modsecurityModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
 atiilla/cve-2026-42897
CVE-2026-42897 - Exchange Health Checker blind spot: outbound IIS URL Rewrite rules silently ignored, making EOMT mitigations invisible in diagnostic…
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 killian0713/assignement_3-cve-2017-7269
Educational exploit reproduction of CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, with setup guide, vulnerability analysis, and Metasploit…
 0xbruno/wsusploit.net
C# proof-of-concept for CVE-2025-59287 targeting WSUS, demonstrating exploitation and providing defensive detection guidance for IIS logs and Windows…
 nika0x38/cve-2017-7269
A Rust implementation of the POC for CVE-2017-7269, targeting the WebDAV service in Microsoft Internet Information Services (IIS) 6.0.
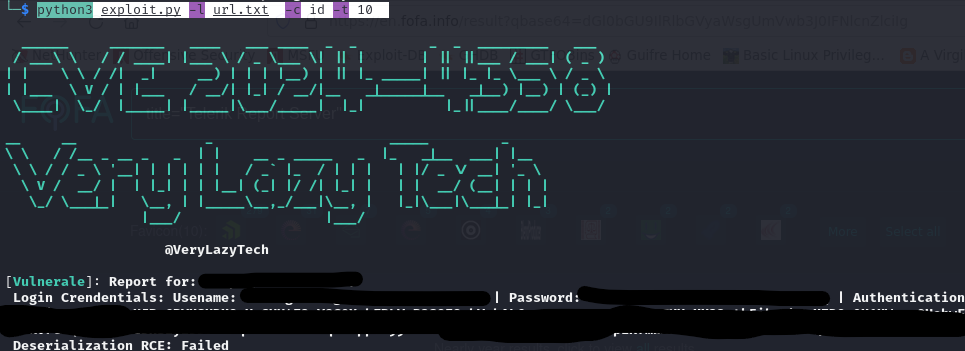 verylazytech/cve-2024-4358
Authentication Bypass Vulnerability — CVE-2024–4358 — Telerik Report Server 2024
 corelight/cve-2021-31166
Detection rules (Suricata + Zeek) for CVE-2021-31166 HTTP Protocol Stack vulnerability, providing network-level alerts on exploit attempts against…
 vanishedpeople/cve-2017-7269
Python proof-of-concept for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution on Windows Server 2003 R2.
 p0dalirius/cve-2022-21907-http.sys
Proof of concept of CVE-2022-21907 Double Free in http.sys driver, triggering a kernel crash on IIS servers
 asepsaepdin/cve-2022-21907
Proof-of-concept exploit for CVE-2022-21907, a remote code execution vulnerability in the HTTP protocol stack (IIS). Includes a Python script and…
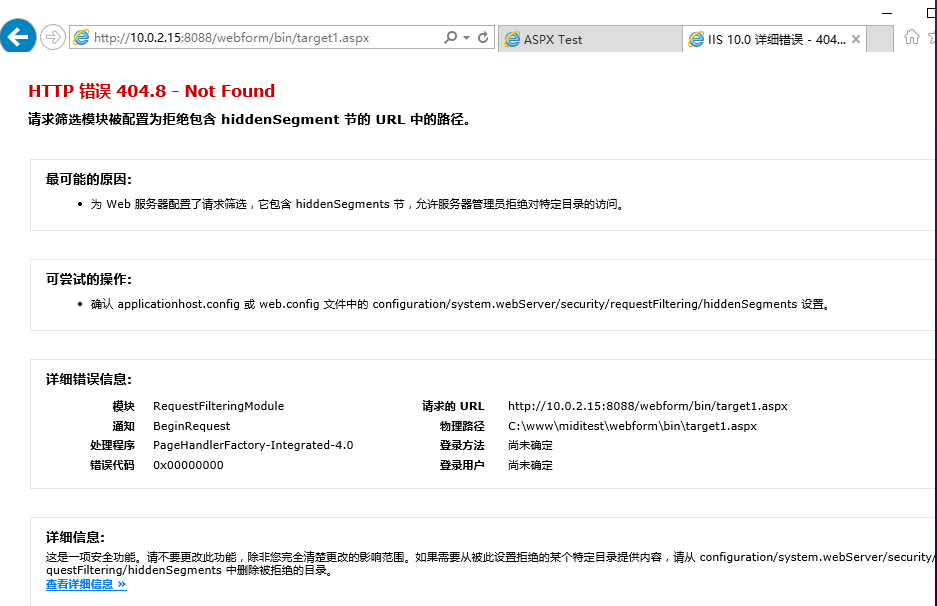 midisec/cve-2023-36899
CVE-2023-36899漏洞的复现环境和工具,针对ASP.NET框架中的无cookie会话身份验证绕过。
 netjbs/cve-2017-0055-poc
This it's a PoC of Departament of justice VDP. By rootkit
 denchief1/cve-2017-7269
C# implementation of CVE-2017-7269 exploit for Microsoft IIS WebDAV remote code execution. Designed for penetration testing and vulnerability…
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
 mauricelambert/cve-2022-21907
CVE-2022-21907: detection, protection, exploitation and demonstration. Exploitation: Powershell, Python, Ruby, NMAP and Metasploit. Detection and…
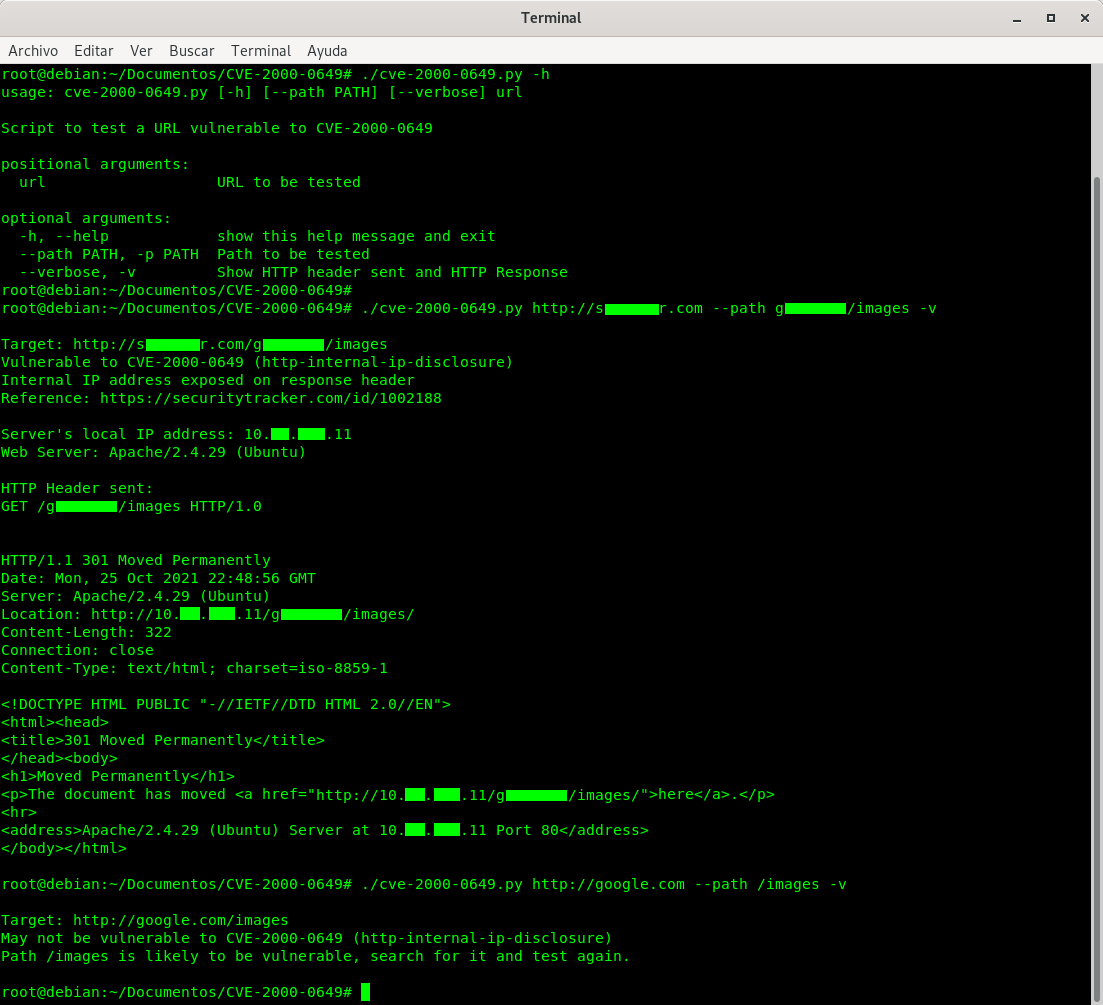 stevenvegar/cve-2000-0649
Script fo testing CVE-2000-0649 for Apache and MS IIS servers