
CVE-2026-65343-e7eb2ed
 hidayat-tanjung/cve-2026-65343-e7eb2ed
PoC for CVE-2026-65343, an AppleKeyStore kernel OOB read on iOS 26.6 that leaks kernel pointers to defeat KASLR from a sandboxed app via…
binary-exploitationexploitationios-security+6
hidayat-tanjung/cve-2026-65343-e7eb2edPoC for CVE-2026-65343, an AppleKeyStore kernel OOB read on iOS 26.6 that leaks kernel pointers to defeat KASLR from a sandboxed app via…
 bytev0rtex/cve-2026-65343
Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 crowthearchfiend/rtcore64-probe
A tiny cpp program to test reading memory using a vulnerable RTCore64.sys driver/device (CVE-2019-16098). It tries to read a "secret" from its own…
 oxfemale/cve-2026-2636_poc
Proof-of-concept for CVE-2026-2636, a Windows CLFS.sys vulnerability causing BSoD via ReadFile on CreateLogFile handle, enabling unprivileged denial…
 mbanyamer/cve-2026-25512-poc-group-office-authenticated-rce
Authenticated remote code execution exploit for Group-Office via TNEF attachment handler, targeting CVE-2026-25512 with OS command injection.
 abrewer251/cve-2025-62215_windows_kernel_pe
This PoC demonstrates a race condition in the Windows kernel leading to a double-free vulnerability, allowing local privilege escalation to SYSTEM.…
 nxploited/cve-2025-8625
Copypress Rest API 1.1 - 1.2 - Missing Configurable JWT Secret and File-Type Validation to Unauthenticated Remote Code Execution
 shoucheng3/jenkinsci__workflow-multibranch-plugin_cve-2022-25175_706-vd43c65dec013
Exploit for CVE-2022-25175 targeting Jenkins Pipeline: Multibranch plugin, enabling automated exploitation of a specific vulnerability in CI/CD…
 nxploited/cve-2025-6058
WPBookit <= 1.0.4 - Unauthenticated Arbitrary File Upload
 bytereaper77/cve-2025-2783
This project is a research-oriented and educational simulation designed to demonstrate the concept of a sandbox escape vulnerability within Google…
 rockrid3r/cve-2023-5178
Exploit for CVE-2023-5178
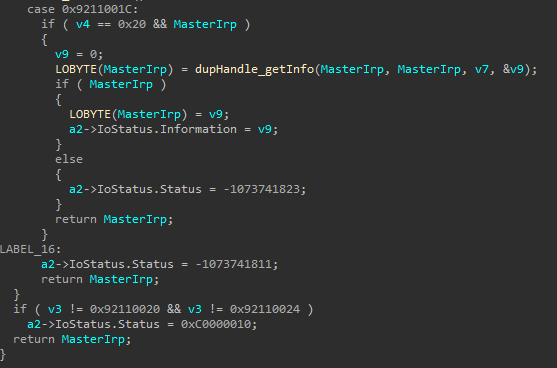 alfarom256/logmeinpochandledup
Exploit for a LogMeIn/GoTo Windows kernel driver race condition that duplicates SYSTEM handles, enabling thread-token impersonation and local…
 pctripsesp/cve-2023-6036
POC about Web3 – Crypto wallet Login & NFT token gating < 3.0.0 - Authentication Bypass Wordpress plugin
 hardsoftsecurity/cve-2020-11651-poc
Repository that contains a CVE-2020-11651 Exploit updated to work with the latest versions of python.
 owasp/docker-security
Getting a handle on container security
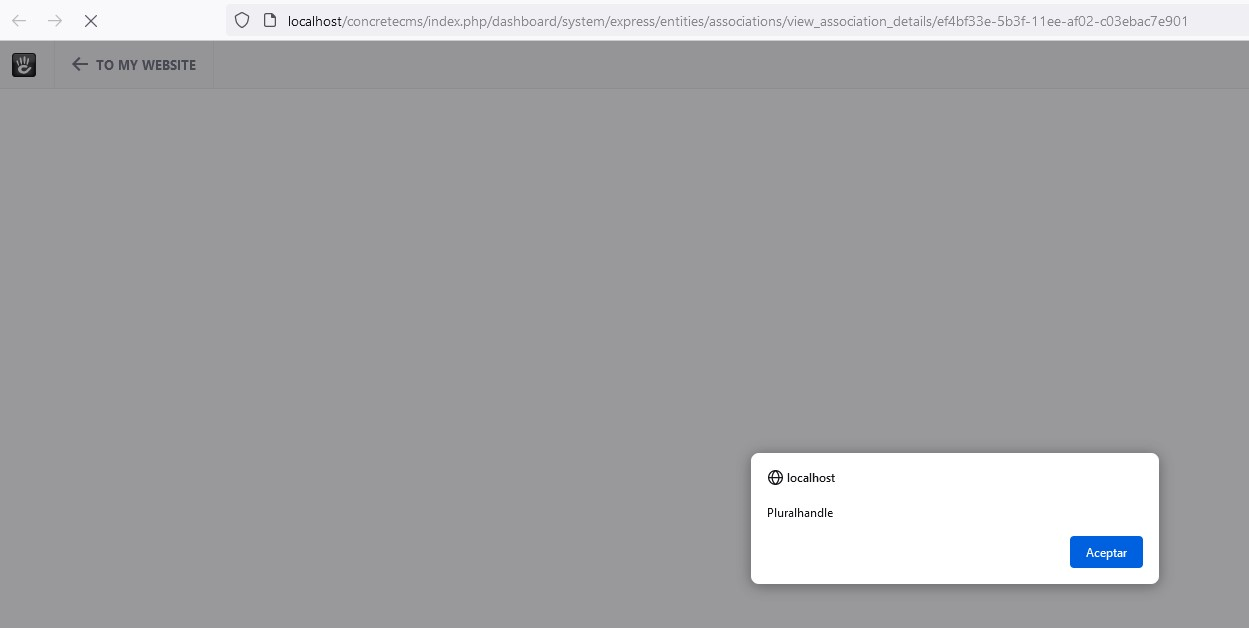 sromanhu/cve-2023-44765_concretecms-stored-xss---associations
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the Plural Handle…
 0xl0k1/cve-2012-1823
PHP CGI Argument Injection.