
TrueVerdict
 prox0959/trueverdict
Zero-dependency Windows PE provenance and false-positive reduction engine (Embedded Authenticode + OS Security Catalogs, Rich Header ROL32…
binary-analysisdefensive-toolsdigital-forensics+6
1
prox0959/trueverdictZero-dependency Windows PE provenance and false-positive reduction engine (Embedded Authenticode + OS Security Catalogs, Rich Header ROL32…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
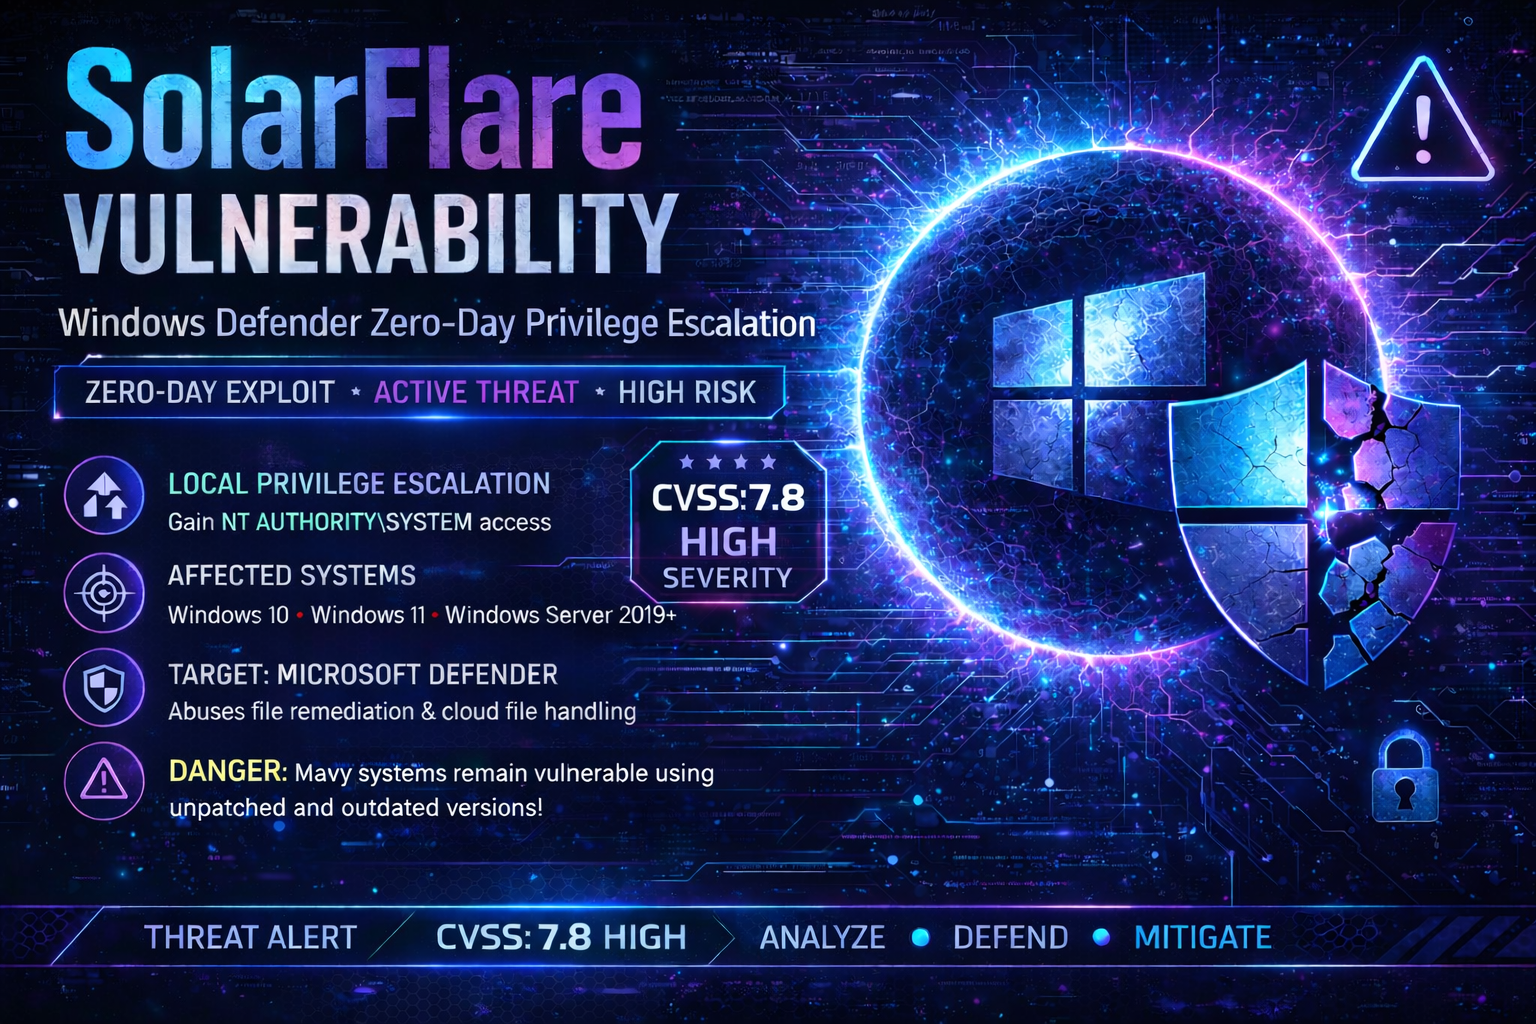 tc4dy/cve-2026-41091-poc-exploit
CVE-2026-41091 RedSun | Microsoft Defender LPE exploit. Low-privileged users gain NT AUTHORITY\SYSTEM 🔥 via Cloud Files API + NTFS junction…
 misterdengi/cve-2026-1801c
Static reverse-engineering analysis of movement input heuristics in Source 2 engine, identifying structural edge cases in input automation and jump…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
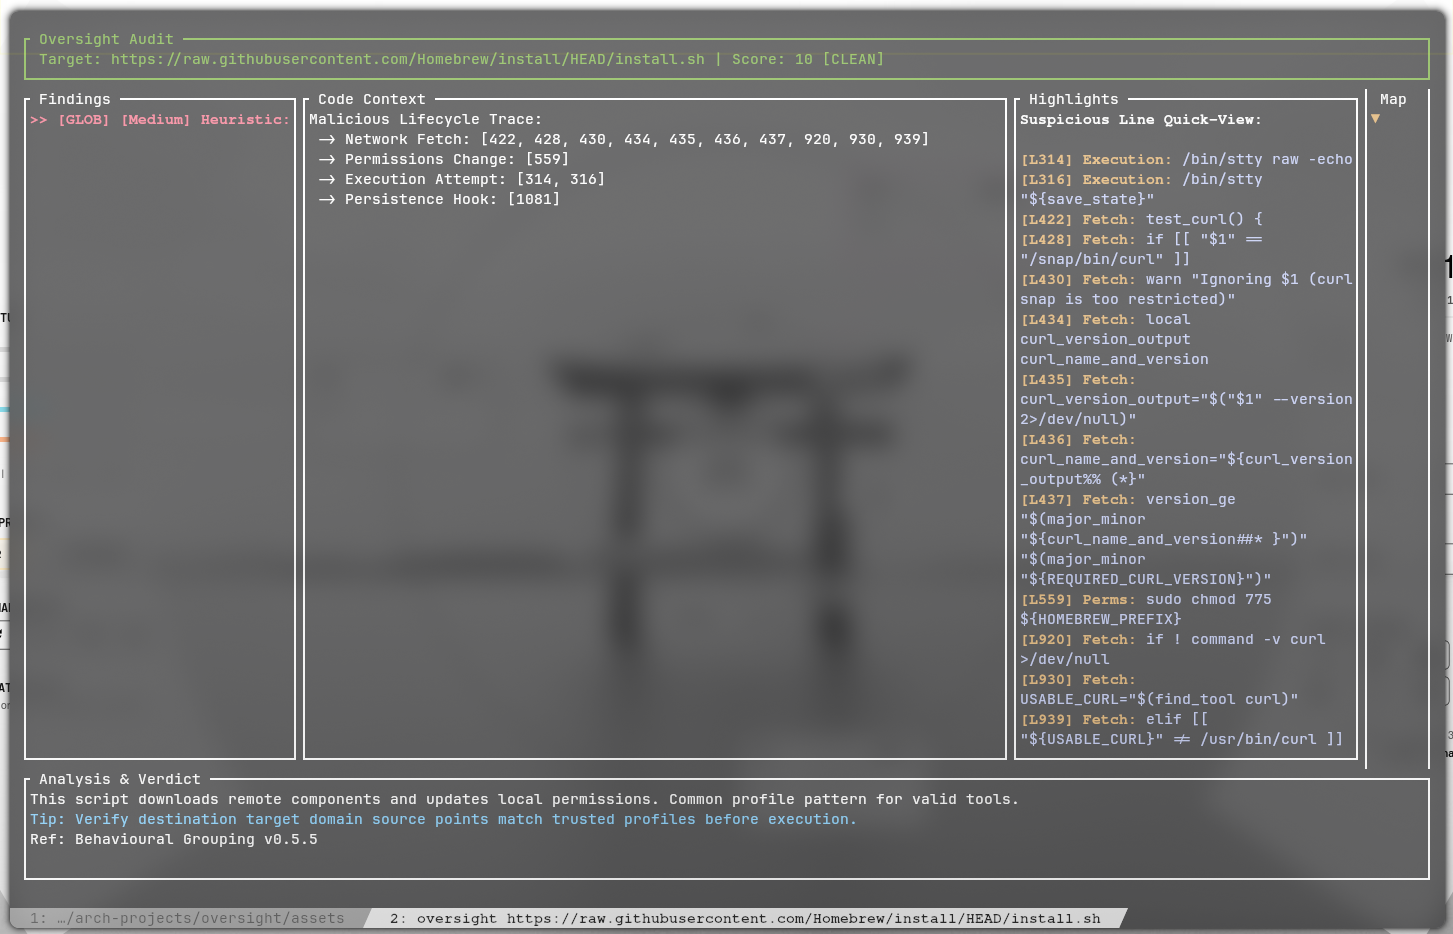 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 jaf0rk/cve-2026-14431
Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.

 at190510-cuong/cve-2026-38165-ssti-
CVE-2026-38165 (SSTI)
 martinastarone/cve-2026-2441
Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…