

php-cve-2026-115560-demo
 prnjlksingh/php-cve-2026-115560-demo
Local intentionally vulnerable PHP lab demonstrating CVE-2026-115560: session serialize_handler mismatch leading to unserialize() gadget RCE, with a…
educationexploitationlabs-practice+4
prnjlksingh/php-cve-2026-115560-demoLocal intentionally vulnerable PHP lab demonstrating CVE-2026-115560: session serialize_handler mismatch leading to unserialize() gadget RCE, with a…
 pentestershell/cve-2026-116779
Python PoC for CVE-2026-116779: unauthenticated OS command execution in FreeSWITCH via the SIP MESSAGE api chat handler, with arbitrary API command…
 cushz/cve-2026-118238
Proof-of-concept for unauthenticated root OS command injection in the Tenda W18E AP httpd diagnose module, with a self-verifying exploit script and…
 shouvikkkk/oauth-sink-check
Trace untrusted OAuth endpoint URLs from source to shell sink — the CVE-2026-119025 attack class, checked in your code, lockfile and MCP configs.
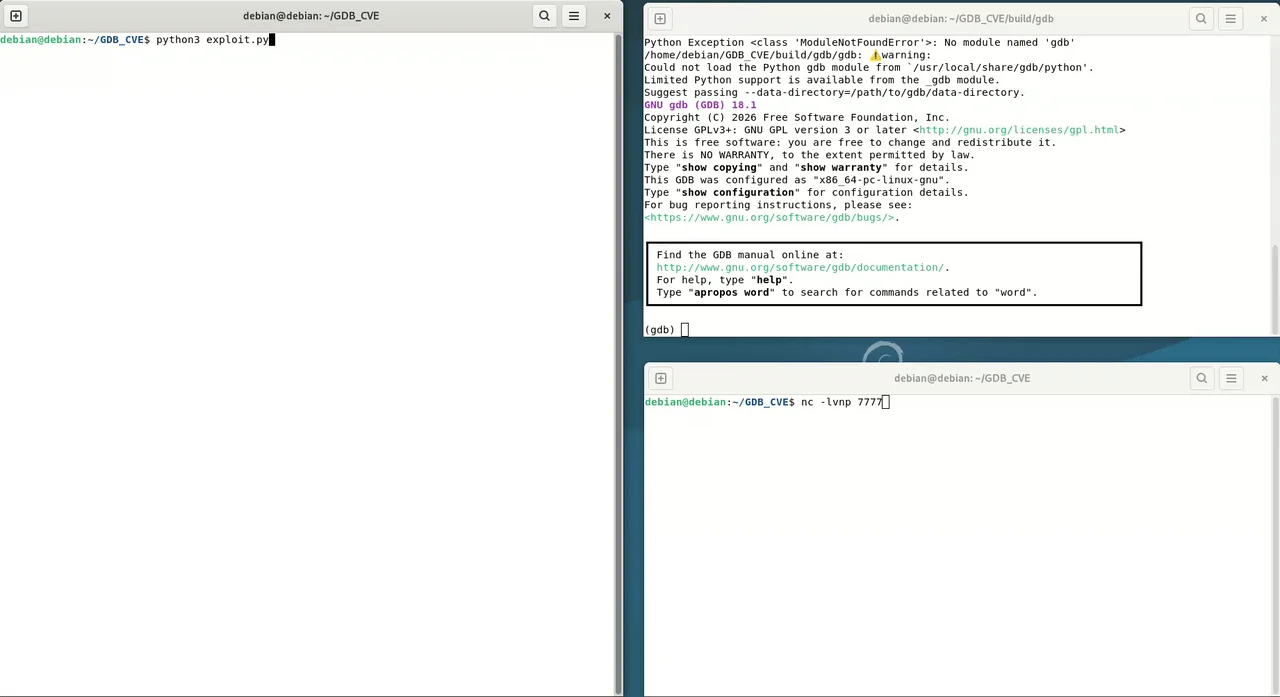 deebumg/cve-2026-121994-poc
Weaponized proof-of-concept for CVE-2026-121994: a fake GDB remote debug stub that sends a malicious p-packet to trigger memory corruption and a…
 mushr00w/cve-2026-116512
Python exploit for CVE-2026-116512, an unauthenticated RCE in weDevs Project Manager <= 4.1.1, with single or bulk target scanning, threading, and…
 carterlasalle/cve-2026-122051
Python PoC driver for CVE-2026-122051, a pre-auth command injection in the Edimax BR-6208AC /goform/mp handler, with firmware emulation recipe, bulk…
 aaaronp/seguridad---proyecto-de-investigaci-n
Lab reproduction of CVE-2026-27606 in rollup: path traversal via chunkName leading to arbitrary file write and reverse shell, with setup,…
 shisones/cve-2026-27626
Python proof-of-concept for CVE-2026-27626: discovers OliveTin password-typed arguments, breaks out of sh -c quoting to inject commands, and provides…
 1337or420/cve-2026-33017-langflow-rce
Proof-of-concept exploit for CVE-2026-33017, an unauthenticated RCE in Langflow before 1.9.0 via the build_public_tmp flow API, injecting Python code…
 0xgh057r3c0n/cve-2026-40281
Python proof-of-concept exploit for CVE-2026-40281, an unauthenticated argument injection RCE in Gotenberg <= 8.30.1, with interactive shell and…
 industri4l-h3ll-xpl0it3rs/cve-2026-39987-marimo-rce
Python proof-of-concept exploiting an unauthenticated WebSocket terminal endpoint in Marimo (< 0.23.0) to achieve pre-auth remote code execution and…
 theendofabbys/cve-2026-48908
Python PoC for CVE-2026-48908: unauthenticated ZIP upload in Joomla SP Page Builder (com_sppagebuilder) leading to remote code execution via a PHP…
 decker757/cs440-langgraph-nosql-demo
Local classroom demo of NoSQL operator injection in LangGraph's MongoDBSaver (GHSA-98xf-r82g-9mhx / CVE-2026-48121). Fictional data only.
 personne-lambda/cve-2026-5562-exploit
Python proof-of-concept script that sends a crafted PUT request to a Kafka UI testexecutions endpoint to validate CVE-2026-5562 exposure and trigger…
 vpxuser/cve-2026-59310
Python PoC for CVE-2026-59310: exploits vCenter rsyslog path traversal to write files and execute commands as root via cron, with check, exec, shell,…
 lulztigre/cve-2026-72867
Working, stdlib-only PoC. A low-privileged authenticated user stores a shell palistener
 eqstlab/cve-2026-111497
Proof-of-concept exploit for CVE-2026-111497 (Node2Shell) that triggers remote code execution via a crafted upload and delivers a reverse shell, with…