
fuzz
 xsscx/fuzz
Commodity Injection Signatures, Malicious Inputs, XSS, HTTP Header Injection, XXE, RCE, Javascript, XSLT
curated-resourcesexploitationfuzzing+6
xsscx/fuzzCommodity Injection Signatures, Malicious Inputs, XSS, HTTP Header Injection, XXE, RCE, Javascript, XSLT
 cujanovic/crlf-injection-payloads
Collection of CRLF injection payloads gathered from bug bounty reports, used as a reference for testing HTTP header and response splitting…
 cujanovic/open-redirect-payloads
Curated collection of open redirect payloads sourced from bug bounty reports, with a shell script to substitute a target whitelisted domain for…
 nishikawaakira/waf-dojo
Hands-on AWS WAF training game with tutorials, scored labs, and exams where players write Web ACL rules to block real attack shapes while avoiding…
 scyrix-llc/cve-2026-88773
Technical analysis of a NetScaler nsppe HTTP/1.1 chunk-size integer-wrap request smuggling flaw, with disassembly, wire-level PoC flows, and firmware…
 oscerd/cve-2026-101259
Runnable proof-of-concept reproducer for CVE-2026-101259, demonstrating error-message disclosure in Apache Camel camel-coap consumers on Spring Boot…
 oscerd/cve-2026-90885
Runnable proof-of-concept reproducer for CVE-2026-90885, an XXE (CWE-611) in Apache Camel camel-saxon XQuery, with Spring Boot and Quarkus builds and…
 oscerd/cve-2026-95628
Runnable proof-of-concept reproducer for CVE-2026-95628, an absolute-path validation gap in Apache Camel camel-docling, with Spring Boot and Quarkus…
 oscerd/cve-2026-95629
Runnable proof-of-concept reproducer for CVE-2026-95629, a path-traversal flaw in Apache Camel camel-docling where the output-path header reaches…
 oscerd/cve-2026-95664
Runnable Spring Boot and Quarkus reproducer for CVE-2026-95664, demonstrating Simple expression injection via the CamelAwsS3Key header in…
 gmh5225/plex2shell
CVE-2026-96652 CVE-2026-96654 CVE-2026-96655 CVE-2026-96656
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
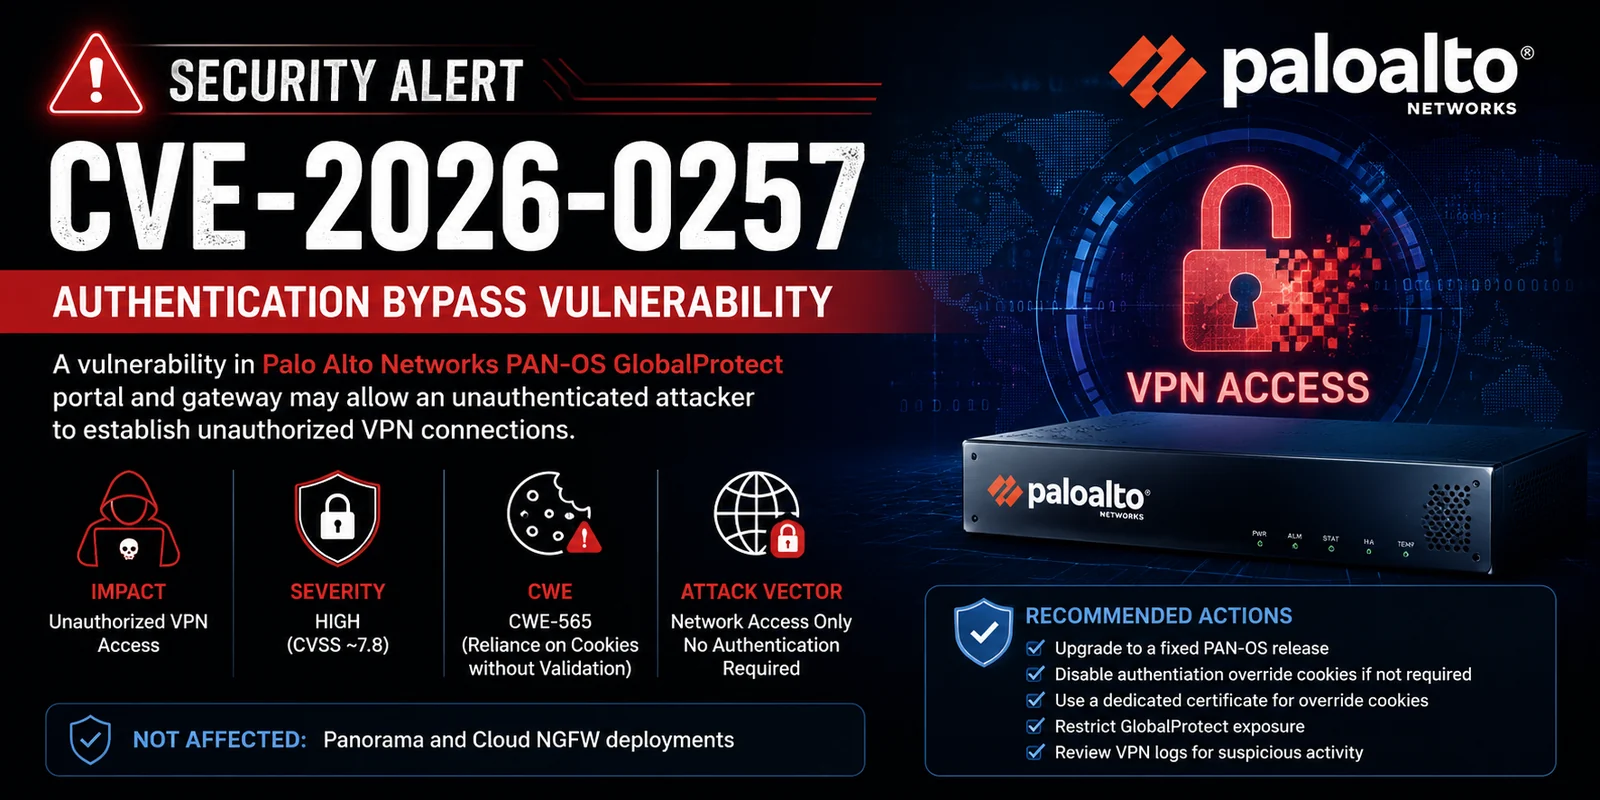 0xredash/cve-2026-0257
Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
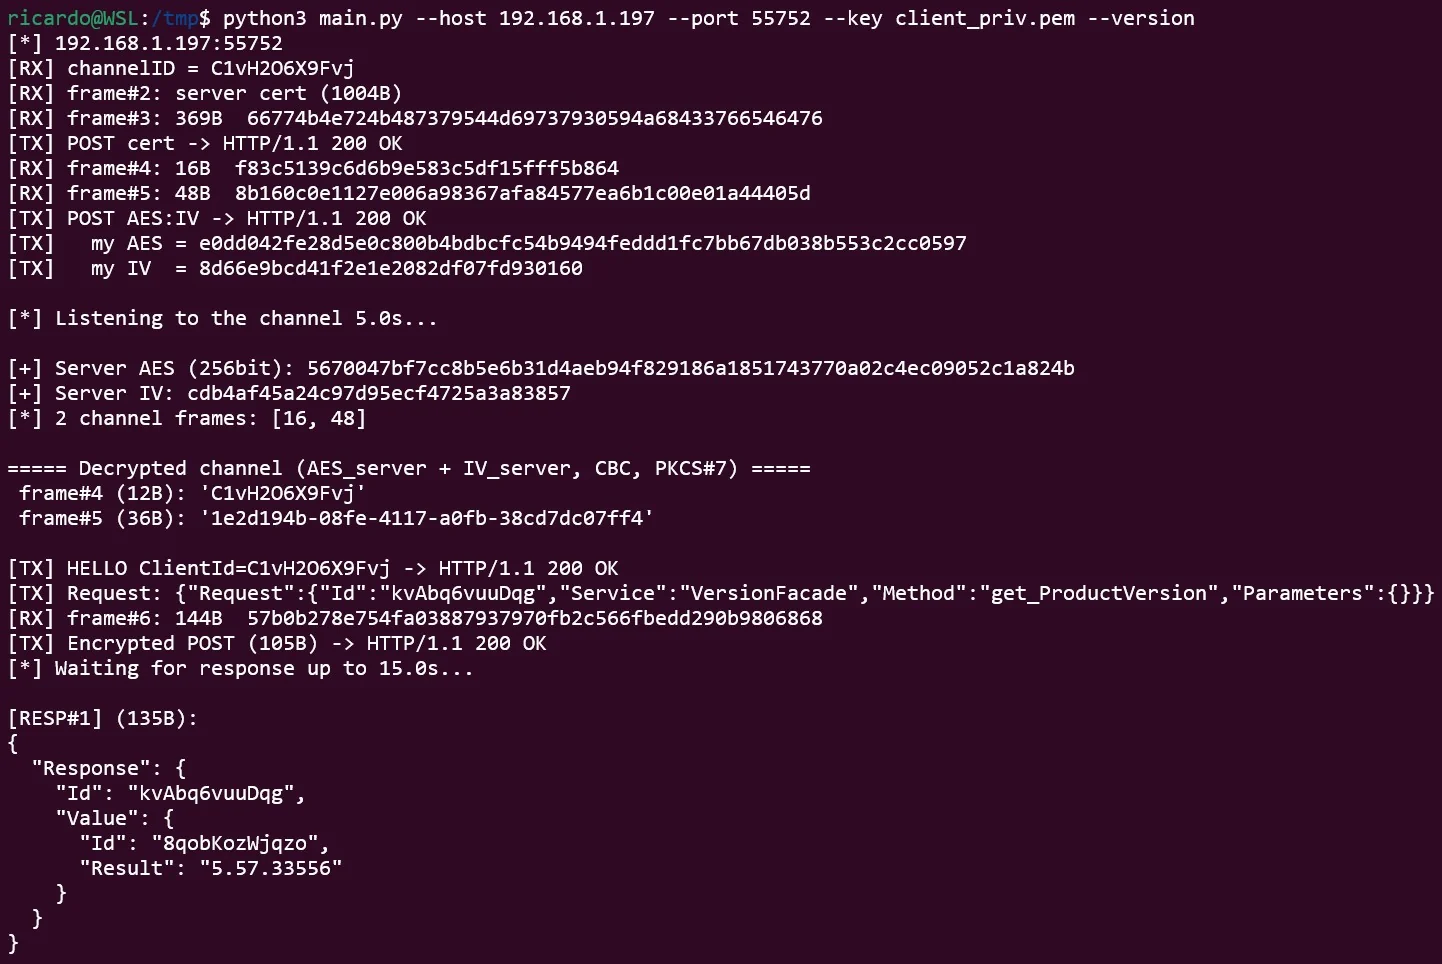 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
 az0x7/vulnerability-checklist
Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…
 caveeroo/cve-2026-111497-wordpress-poc
CVE-2026-111497 RCE PoC for one pinned Docker Official Image for WordPress
 inforcqb-self/cve-2026-0013-exploit
Proof-of-concept exploit code for CVE-2026-0013, demonstrating the vulnerability for research and validation purposes.
 iamlucif3r/cve-2026-109618-exploit
[PHP2Shell] Golang exploit for CVE-2026-109618 / CVE-2026-109619: Unauthenticated RCE in PHP 5.4–8.5.11 via OOM corruption + session.upload_progress…