initial-access-community

Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…

Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…

Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)

EDK2 BrotliCustomDecompressLib security findings — coordinated disclosure

Disclosure and PoC for a root file read/write flaw in the TP-Link Deco XE75 Pro V3 debug channel (tmpsvr opcodes 0xC456/0xF0), with CVSS analysis and…

Writeup of a 0-click remote code execution exploit chain developed for the Alpine iLX-F511 automotive head unit at Pwn2Own Automotive 2026.

Documents and reproduces a fail-open authentication flaw in SONiC gNMI where an empty UserAuth map allows unauthenticated gNMI Set and gNOI writes,…

Working POC of Mikrotik exploit from Vault 7 CIA Leaks

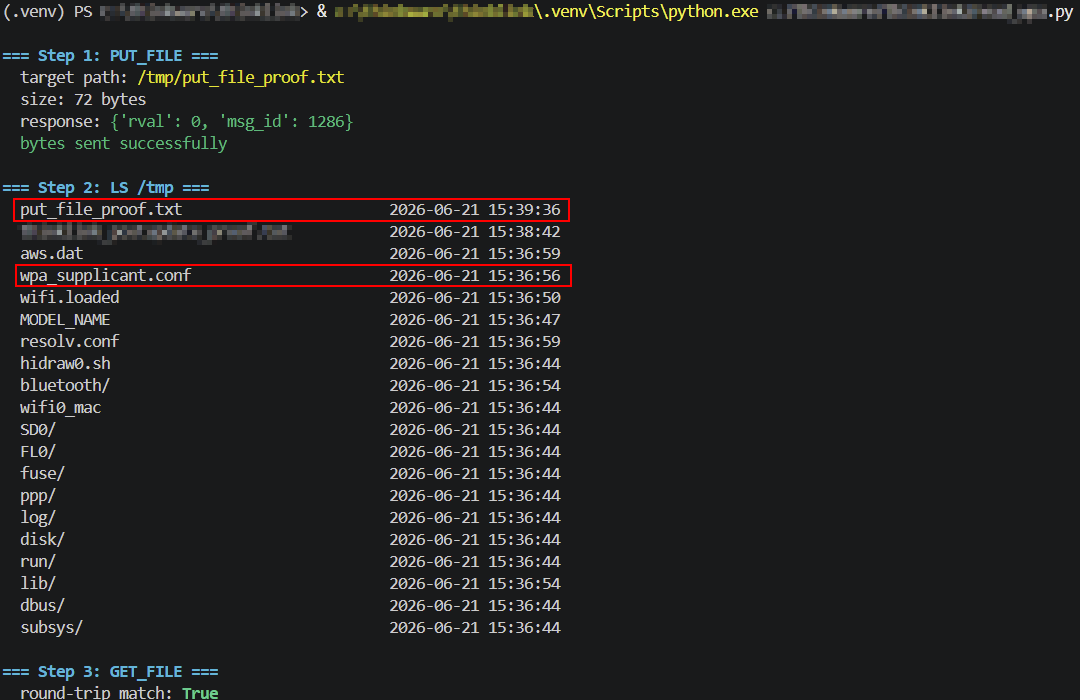
Three unauthenticated vulnerabilities in the Thinkware U3000 dashcam's local WiFi control protocol: arbitrary file write, arbitrary file read, and…

Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…

CVE-2026-100886 | Unauthenticated Remote Code Execution toolkit.

Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…

Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…

Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…

Python script that checks Netis routers for CVE-2026-36539, detecting vulnerable devices on a network.

Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…

Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…