
CVE-2021-31166
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
exploitationexploit-frameworkspayload-development+4
6
mauricelambert/cve-2021-31166CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 h3x0v3rl0rd/cve-2015-1635
Python exploit for CVE-2015-1635 (MS15-034) targeting HTTP.sys remote code execution vulnerability in IIS servers. Supports custom arguments for…
 h3x0v3rl0rd/cve-2017-7269
Exploit for CVE-2017-7269 targeting IIS 6.0 WebDAV remote code execution vulnerability. Enables buffer overflow exploitation on legacy Windows…
 atiilla/cve-2026-42897
CVE-2026-42897 - Exchange Health Checker blind spot: outbound IIS URL Rewrite rules silently ignored, making EOMT mitigations invisible in diagnostic…
 dcscoder/exchange_ioc_hunter
CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, CVE-2021-27065
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 corelight/cve-2021-31166
Detection rules (Suricata + Zeek) for CVE-2021-31166 HTTP Protocol Stack vulnerability, providing network-level alerts on exploit attempts against…
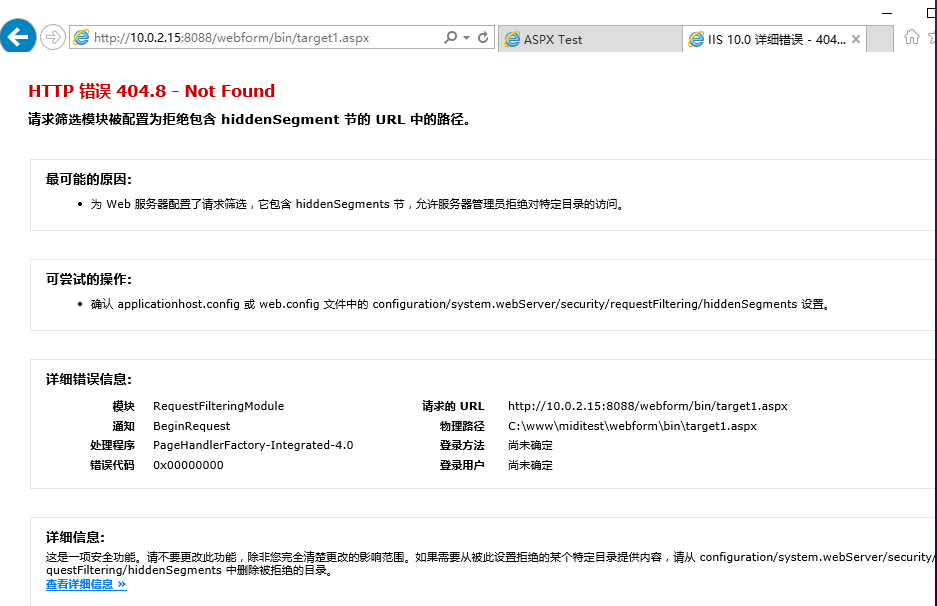 midisec/cve-2023-36899
CVE-2023-36899漏洞的复现环境和工具,针对ASP.NET框架中的无cookie会话身份验证绕过。
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
 mauricelambert/cve-2022-21907
CVE-2022-21907: detection, protection, exploitation and demonstration. Exploitation: Powershell, Python, Ruby, NMAP and Metasploit. Detection and…
 killian0713/assignement_3-cve-2017-7269
Educational exploit reproduction of CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, with setup guide, vulnerability analysis, and Metasploit…
 vanishedpeople/cve-2017-7269
Python proof-of-concept for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution on Windows Server 2003 R2.
 g0rx/iis6-exploit-2017-cve-2017-7269
Exploit for CVE-2017-7269 targeting Microsoft IIS 6.0 WebDAV remote code execution vulnerability. Enables authenticated buffer overflow attacks on…
 al1ex/cve-2017-7269
Exploit for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution. Designed for use with Metasploit in penetration…
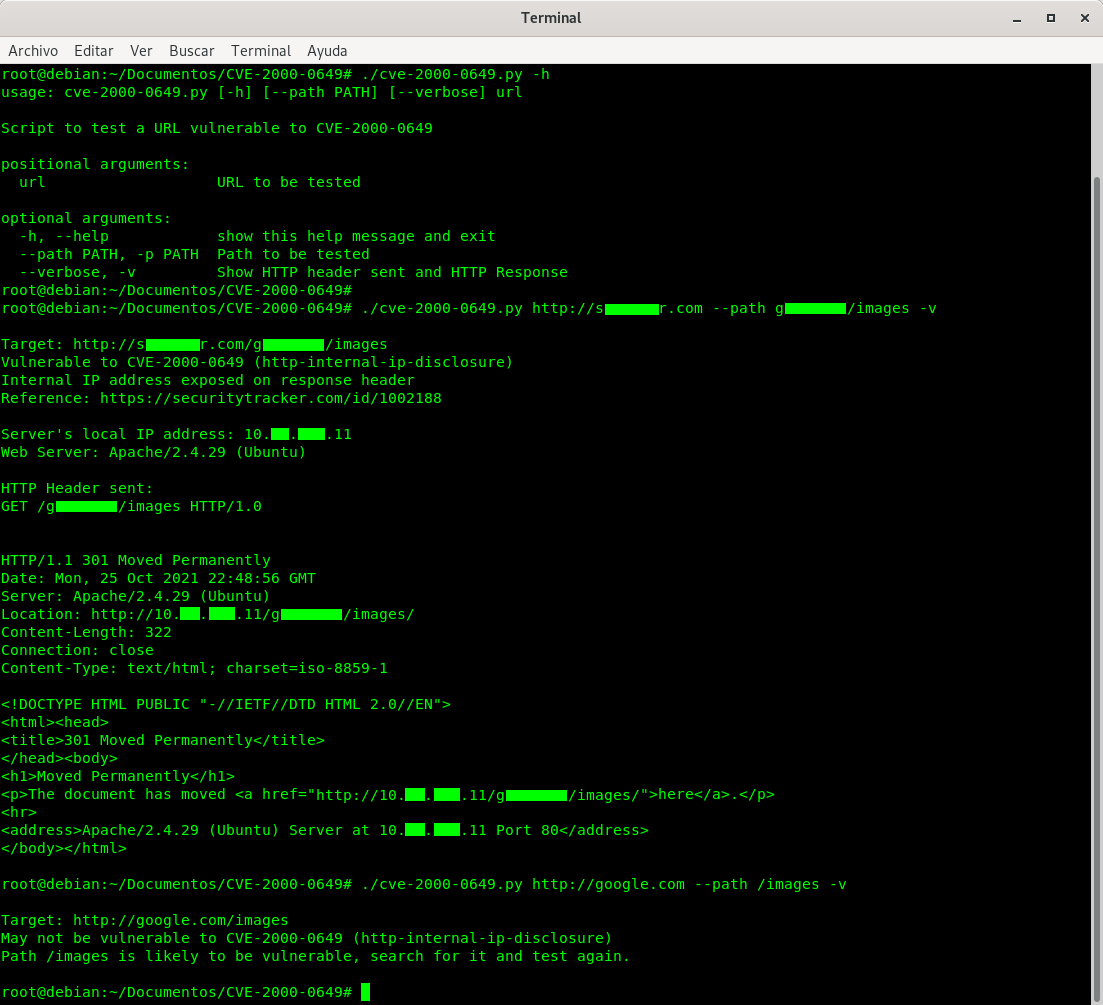 stevenvegar/cve-2000-0649
Script fo testing CVE-2000-0649 for Apache and MS IIS servers
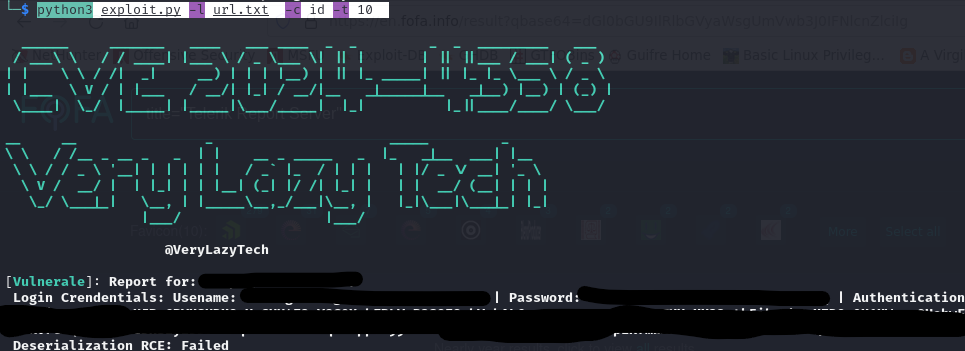 verylazytech/cve-2024-4358
Authentication Bypass Vulnerability — CVE-2024–4358 — Telerik Report Server 2024
 0xbruno/wsusploit.net
C# proof-of-concept for CVE-2025-59287 targeting WSUS, demonstrating exploitation and providing defensive detection guidance for IIS logs and Windows…