active-scan-plus-plus

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…

openrisk is a tool that generates a risk score based on the results of a Nuclei scan.

Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…

Tactical Identity Operator for Linux & Hybrid Active Directory

Isolated JavaScript sandbox for Node.js that runs untrusted code with restricted access to built-in modules and host resources via Proxy-based…

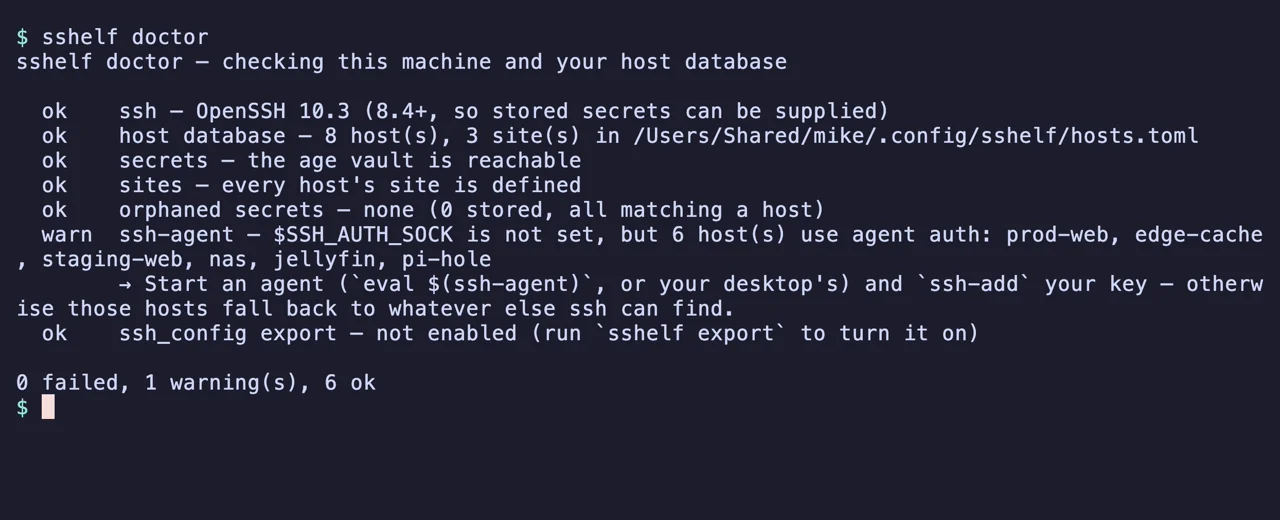
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…

Collection of cryptographic hash functions written in pure Rust

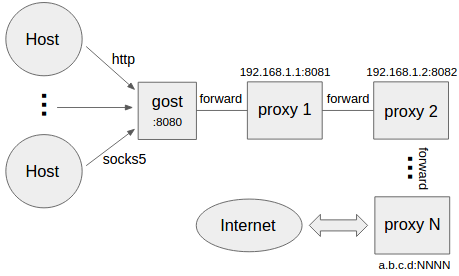
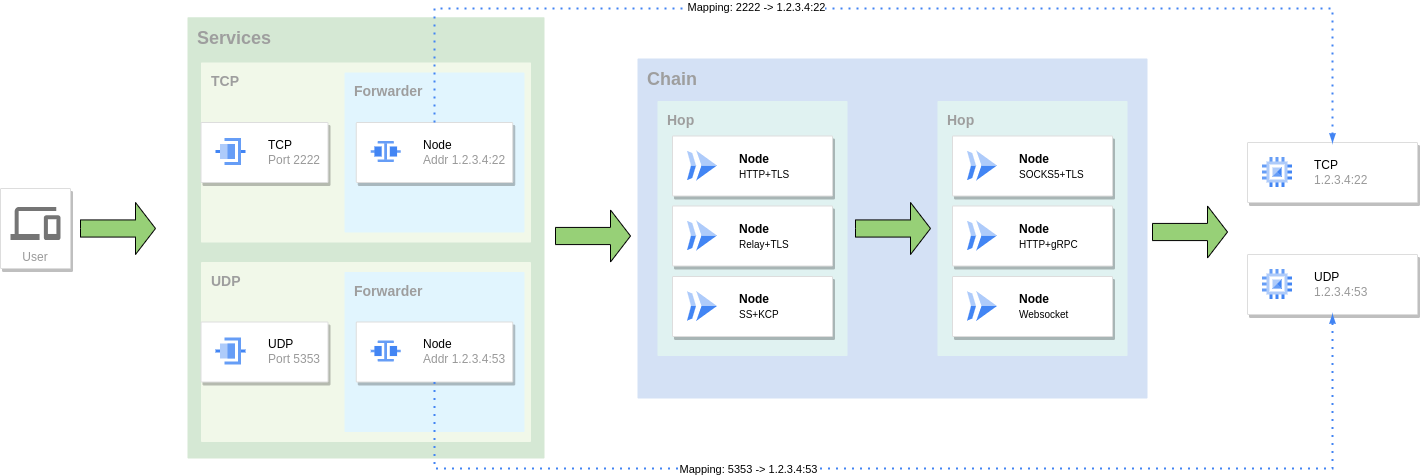
GO Simple Tunnel - a simple tunnel written in golang

GO Simple Tunnel - a simple tunnel written in golang

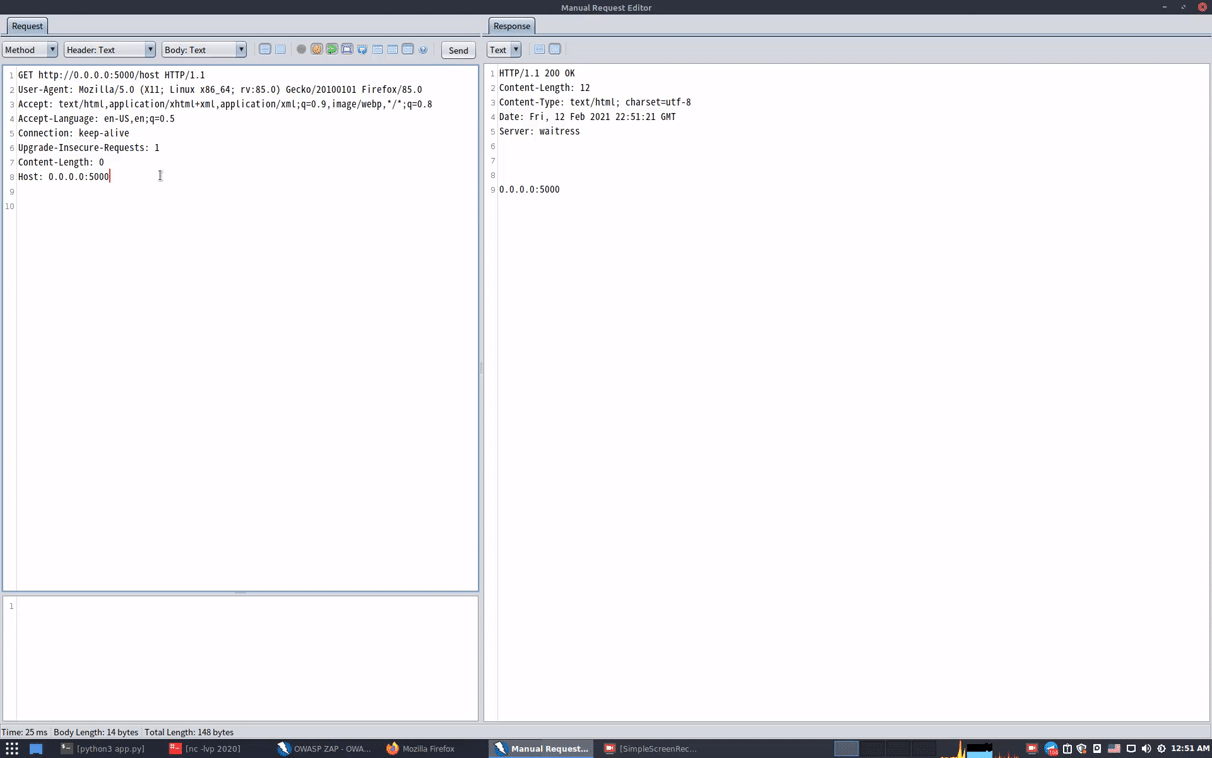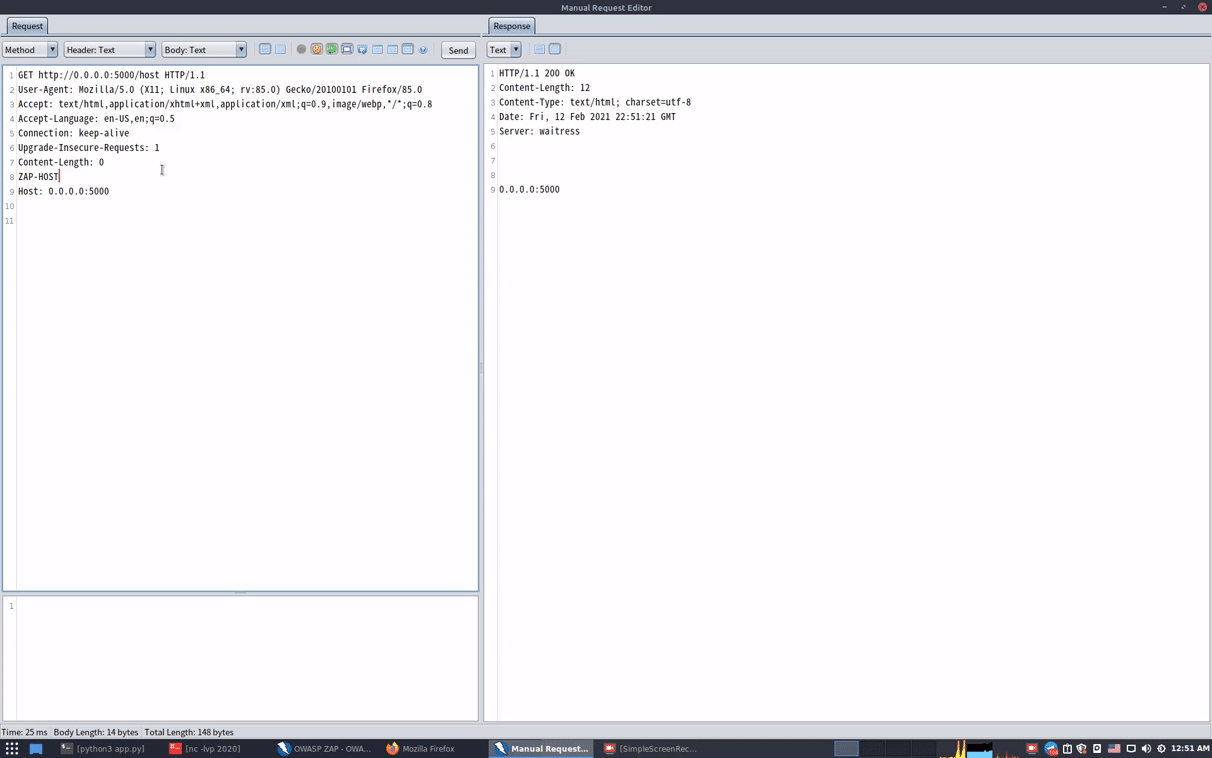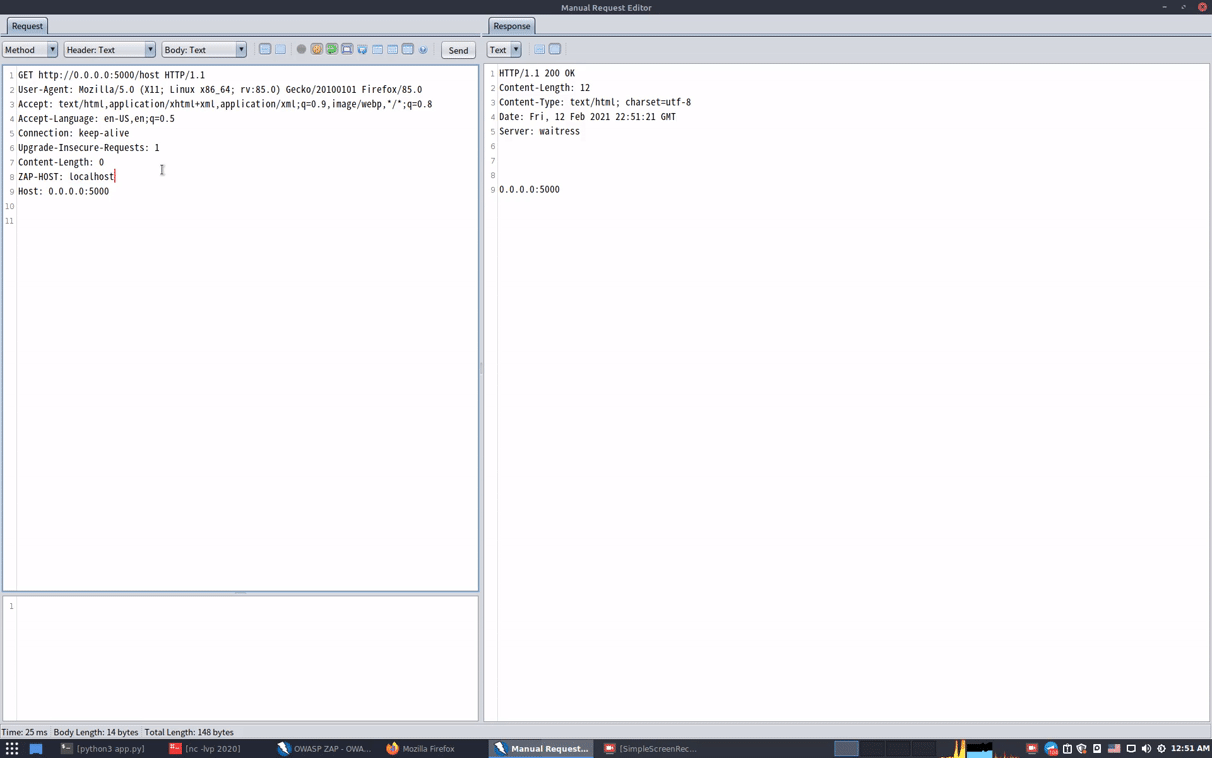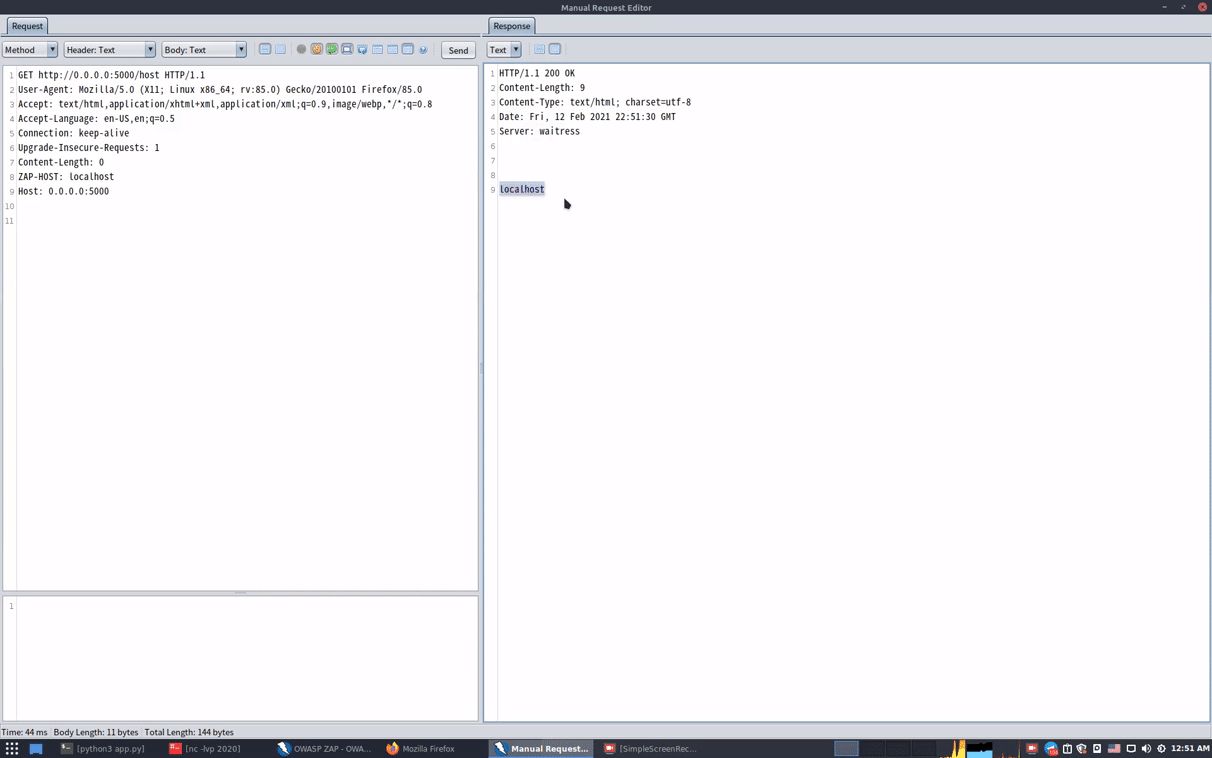
Fix host header error in zaproxy

An information gathering tool to collect git commit emails in version control host services

Accept URLs on stdin, replace all query string values with a user-supplied value

Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss

MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…