

Doozer
 coalfire-research/doozer
Password cracking utility
hash-analysispassword-crackingpenetration-testing+2
coalfire-research/doozerPassword cracking utility
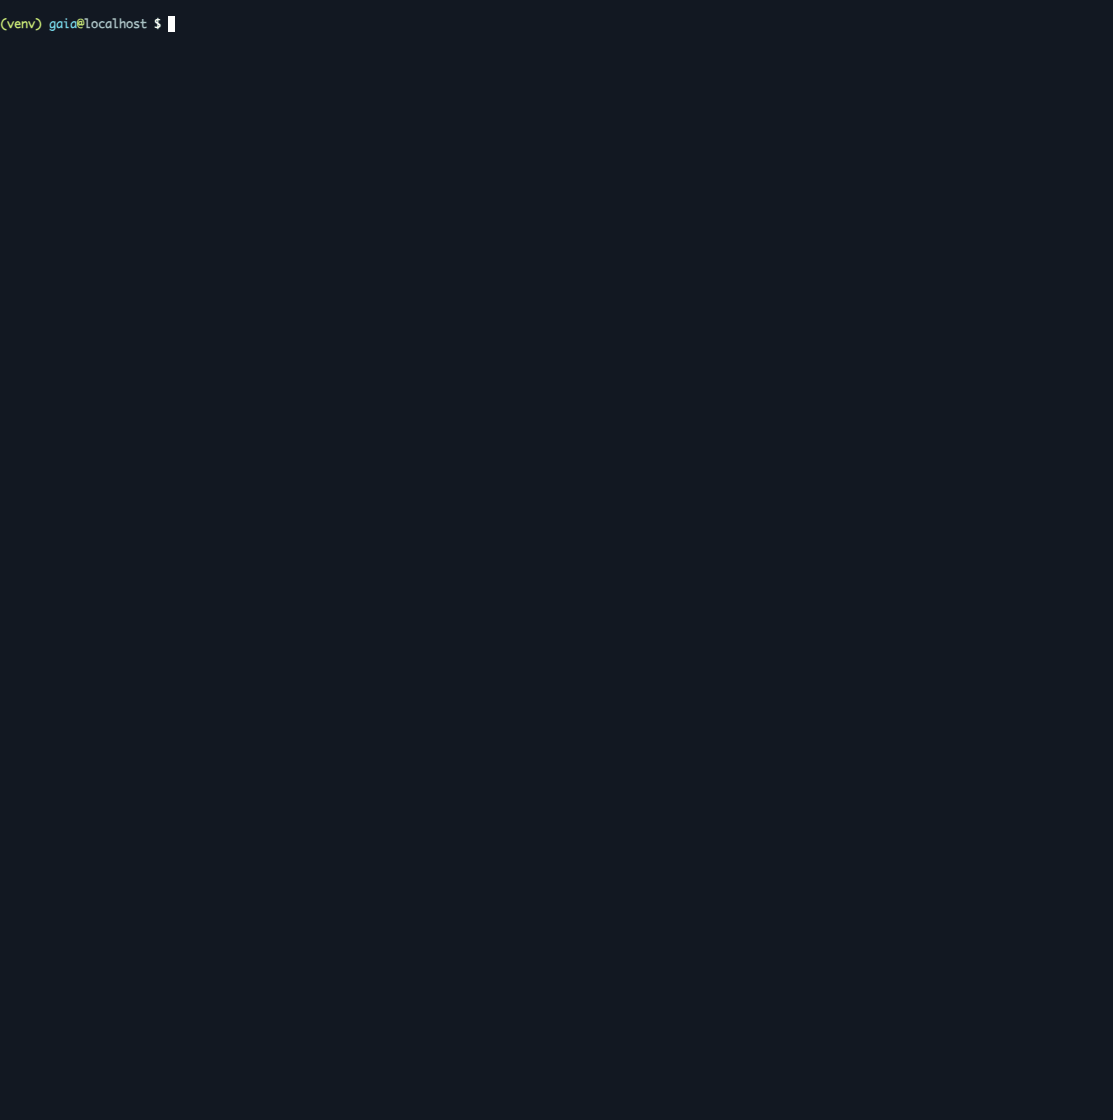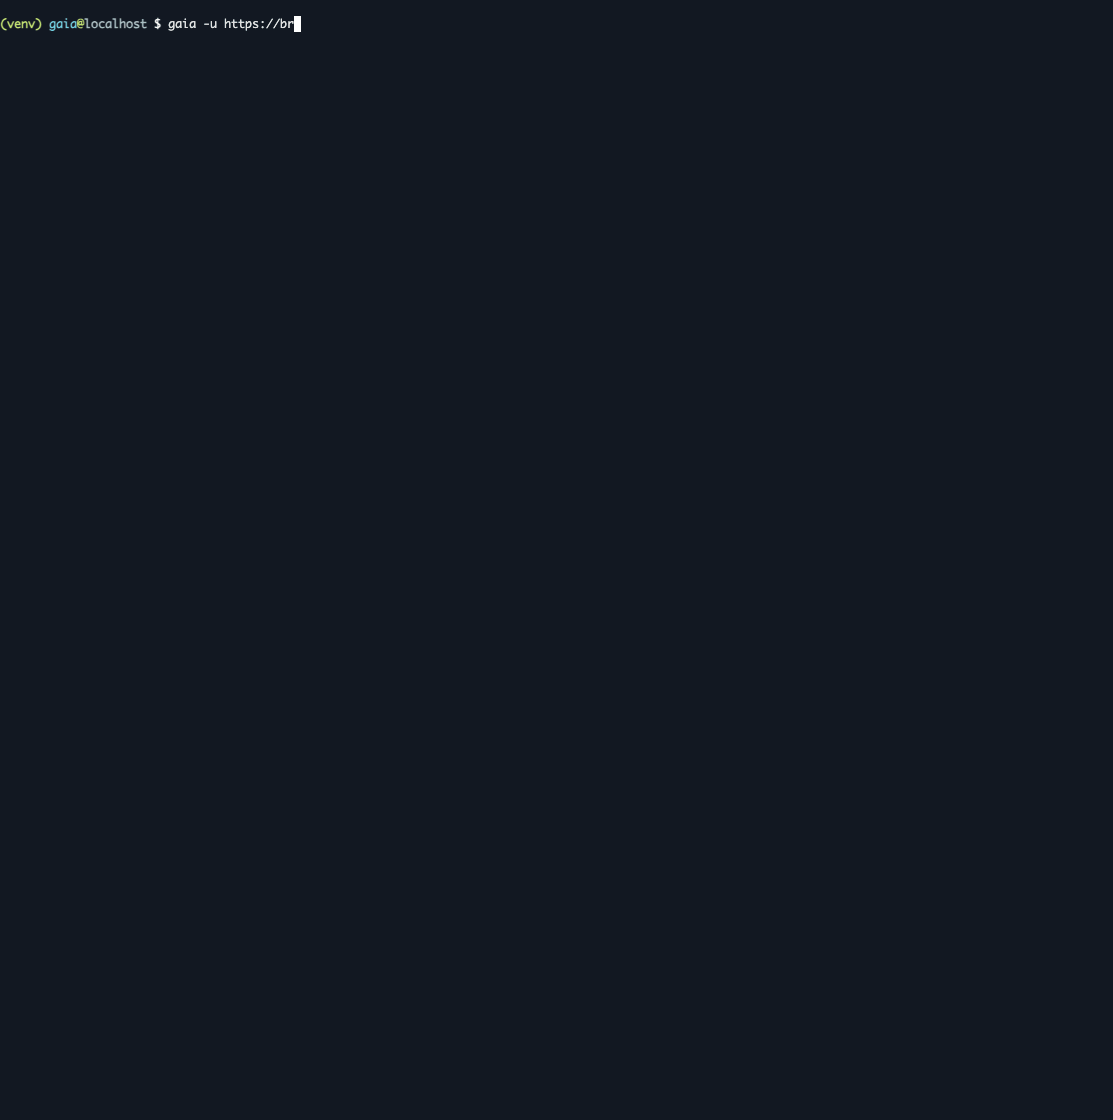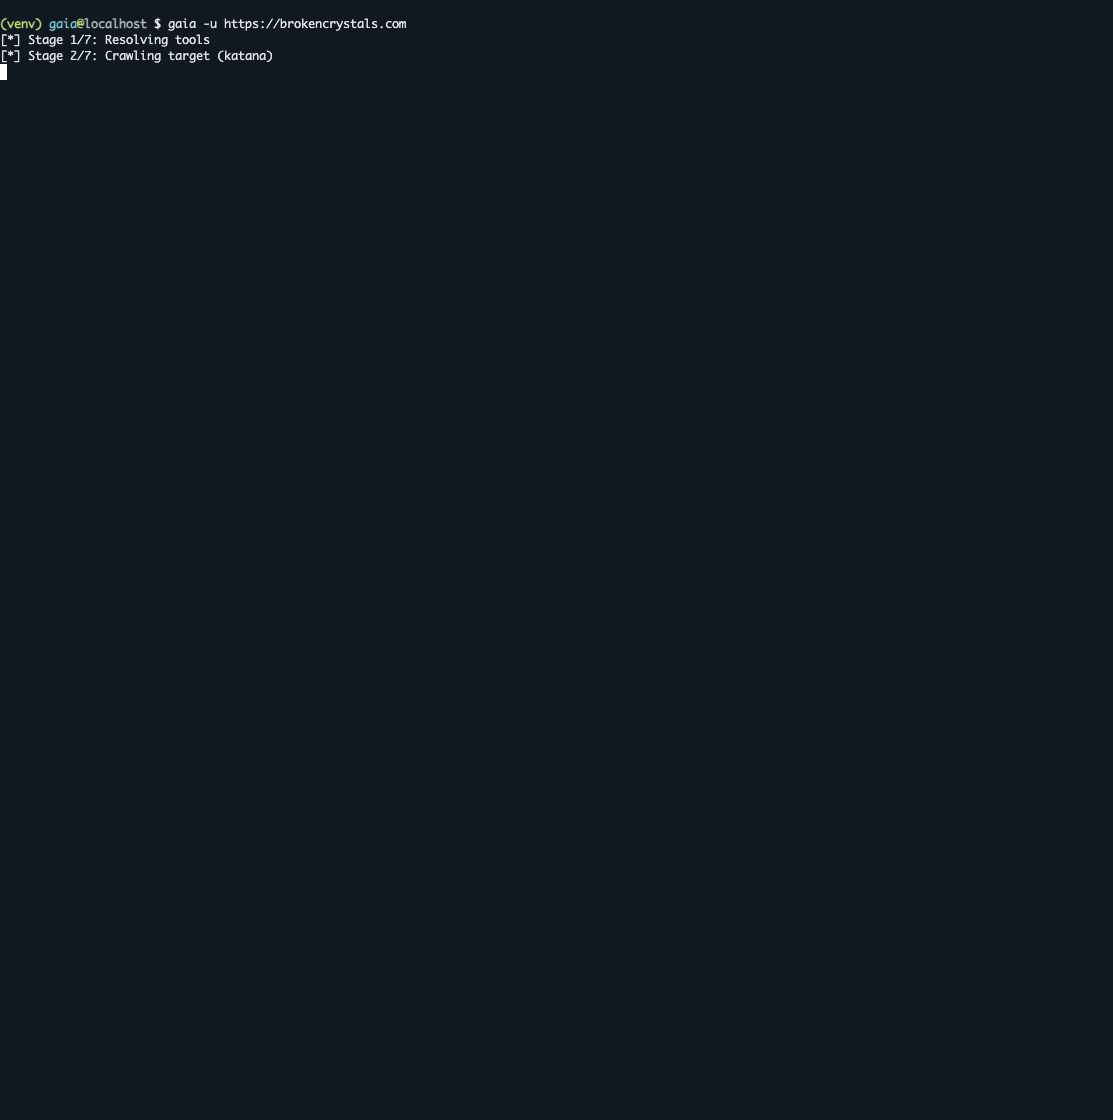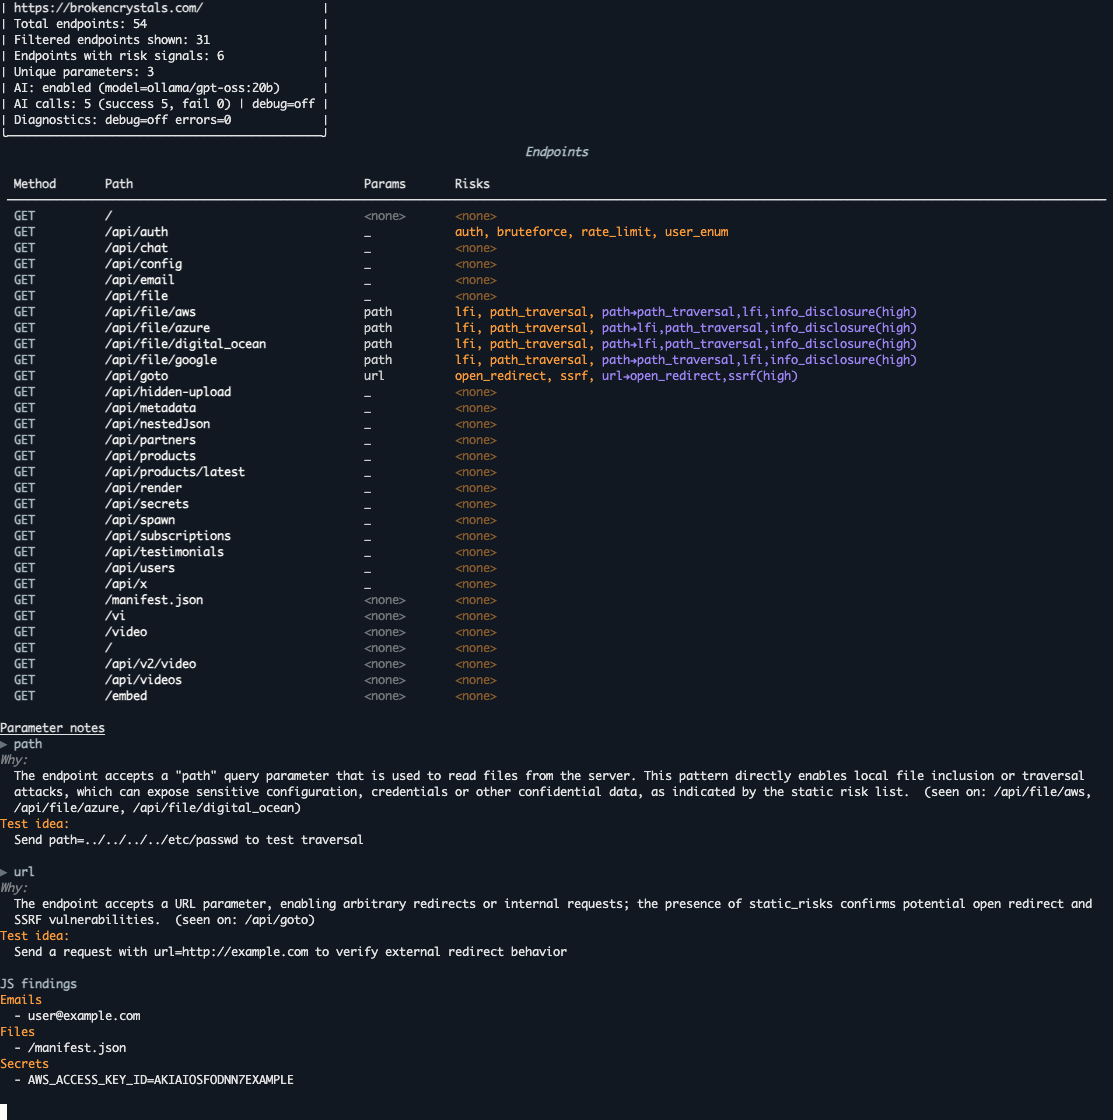 oksuzkayra/gaia
Attack surface discovery and AI-assisted triage for security researchers. Endpoint & parameter mapping with actionable testing hints.
 arxhr007/aliens_eye
AI powered OSINT engine to discover and map 840+ social media identities across the web
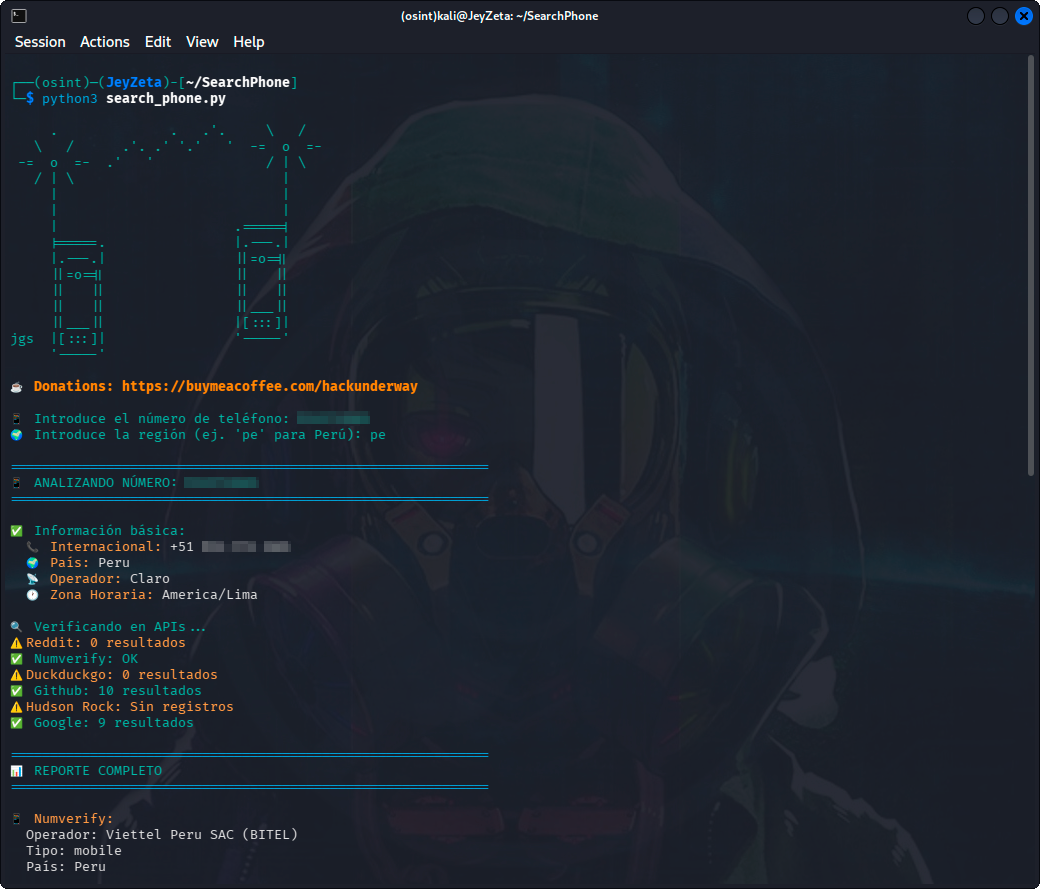 hackunderway/searchphone
Phone number OSINT toolkit with multi-API search (Google, GitHub, Numverify, Reddit, DuckDuckGo), Hudson Rock infostealer intelligence, and automatic…
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 projectdiscovery/wappalyzergo
A high performance go implementation of Wappalyzer Technology Detection Library
 rverton/webanalyze
Port of Wappalyzer (uncovers technologies used on websites) to automate mass scanning.
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
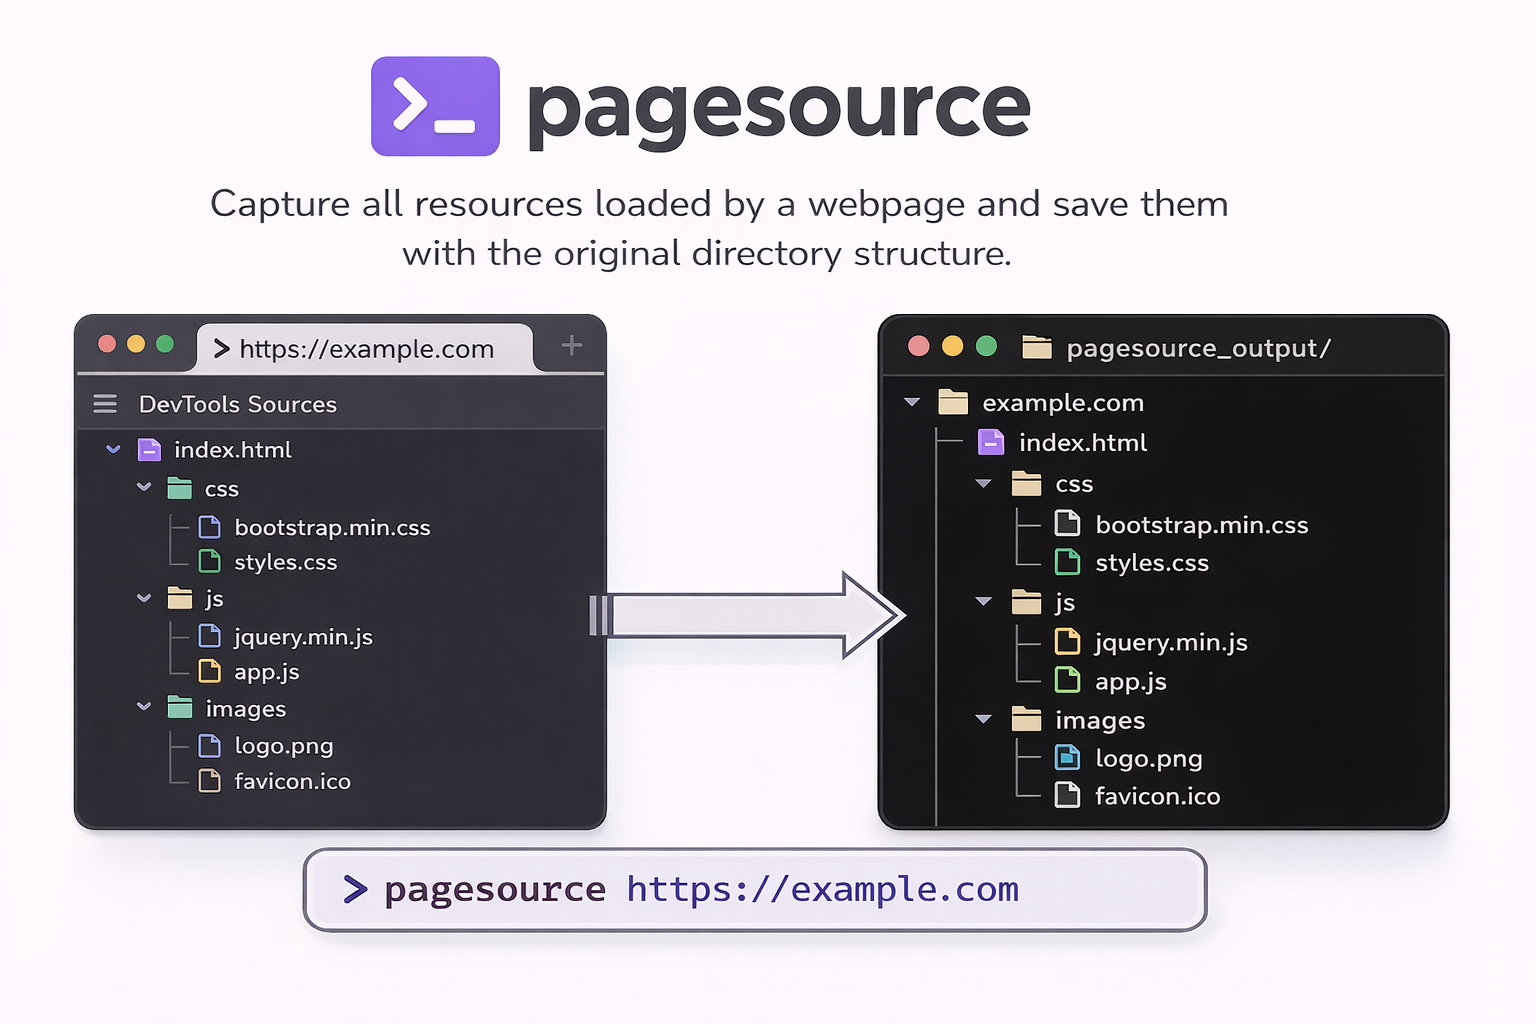 timf34/pagesource
CLI to download websites' actual JS/CSS/assets (not flattened HTML)
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
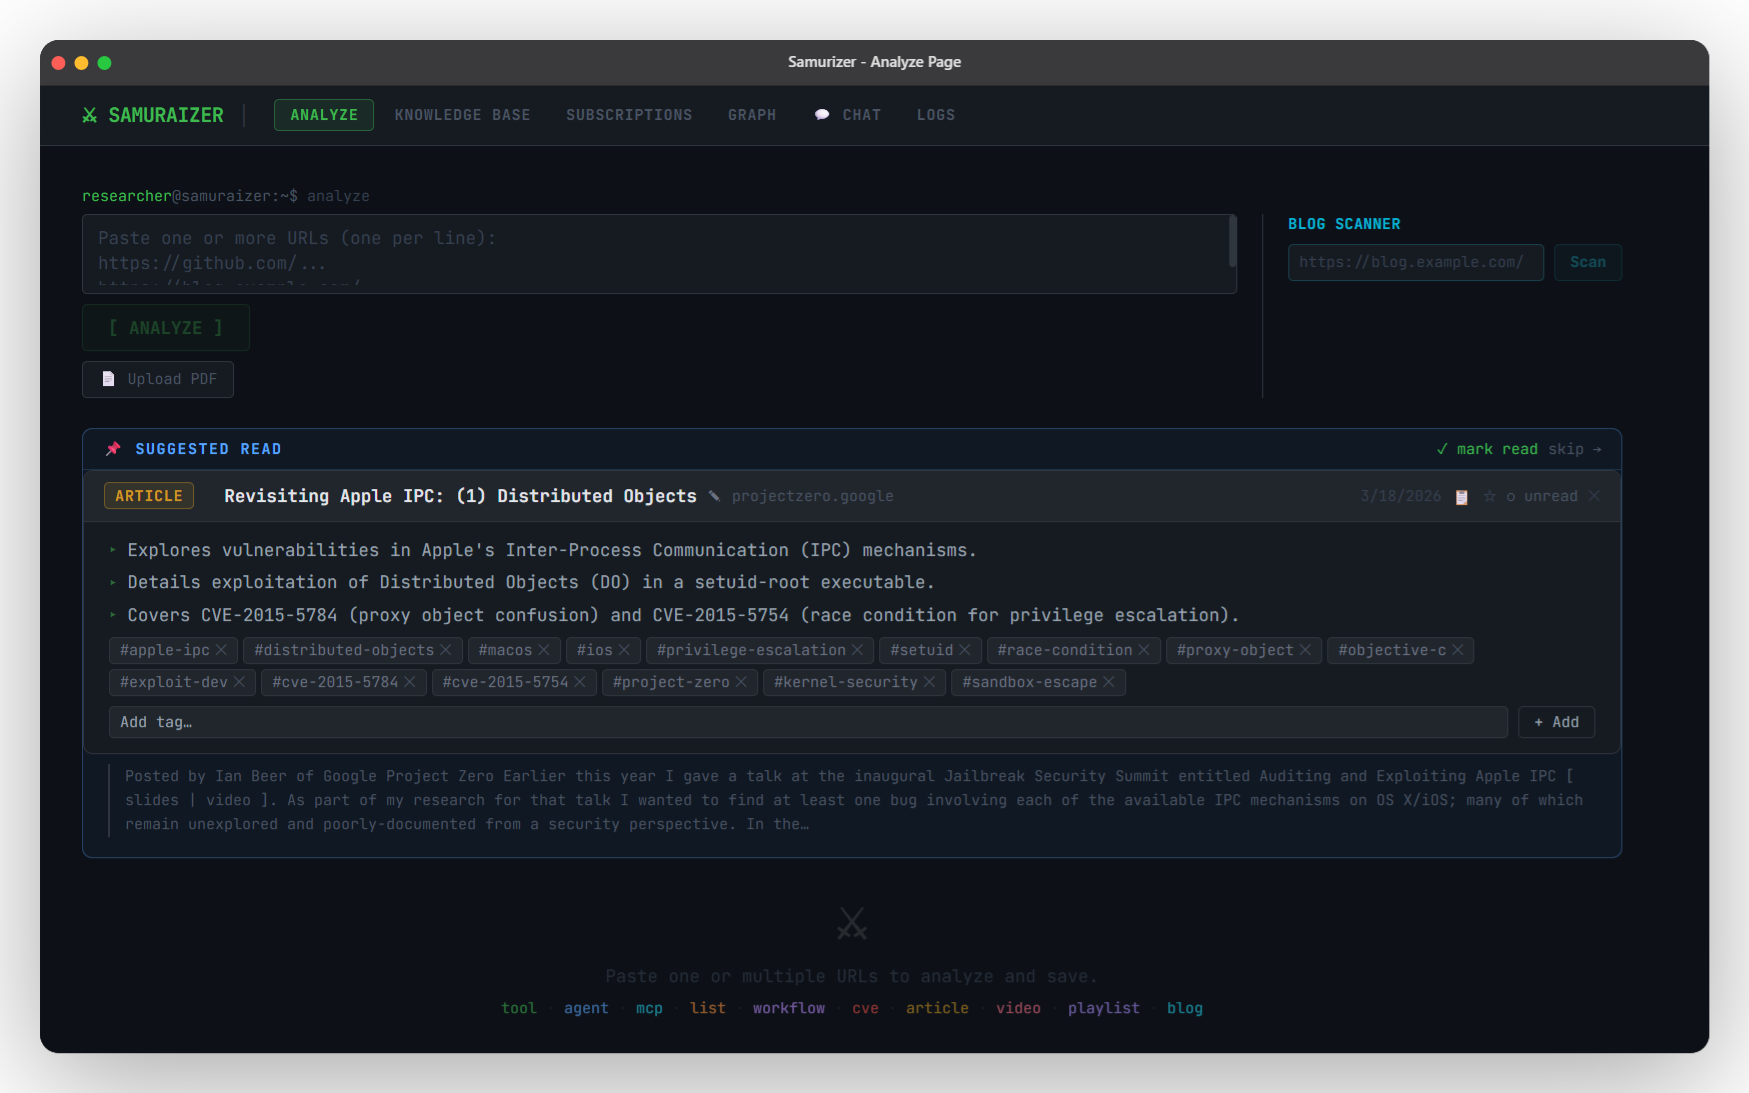 zomry1/samuraizer
NotebookLM on steroids — purpose-built for security researchers.
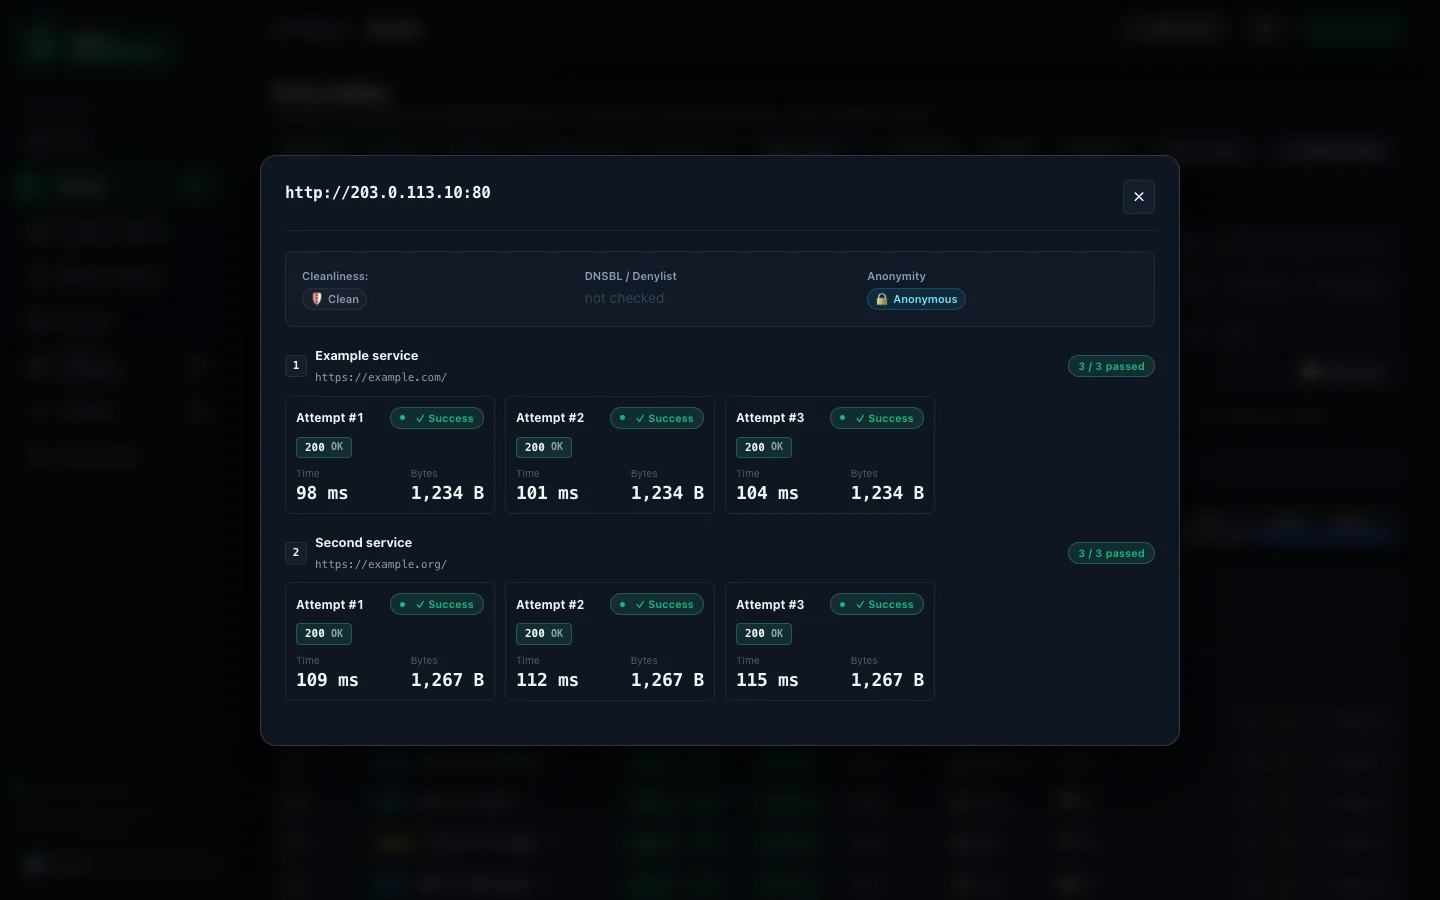 davidvoitenko/proxy-workbench
Collects, checks and ranks public HTTP/SOCKS proxies against your own targets, then serves them via ranked exports, pools, a rotating gateway and a…
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 didierstevens/didierstevenssuite
Collection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 mentebinaria/retoolkit
Pre-configured bundle of reverse engineering and malware analysis tools for x86/x64 Windows systems, with desktop integration and plugin-ready…