
tanuki
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory
ai-securityauthenticationdefensive-tools+6
mafifrizi/tanukiTactical Identity Operator for Linux & Hybrid Active Directory
 c3c/adexplorersnapshot
Parses AD Explorer snapshots into BloodHound-compatible JSON or NDJSON for Active Directory reconnaissance and attack path mapping.
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 matijamiki/ranwhat
Flight recorder and secret scanner for AI coding agents. Reads what Claude Code, Codex, Gemini CLI and 17 more ran, and flags risky actions and…
 ugzv/ublockdnsclient
Cross-platform system DNS client for uBlockDNS with device wide ad and tracker blocking and real time filter updates.
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
 macmod/sopa
A practical client for ADWS in Golang.
 zakipedio/bridgehead
Native C++ access to Active Directory over ADWS, no .NET, no WCF, no HTTP stack.
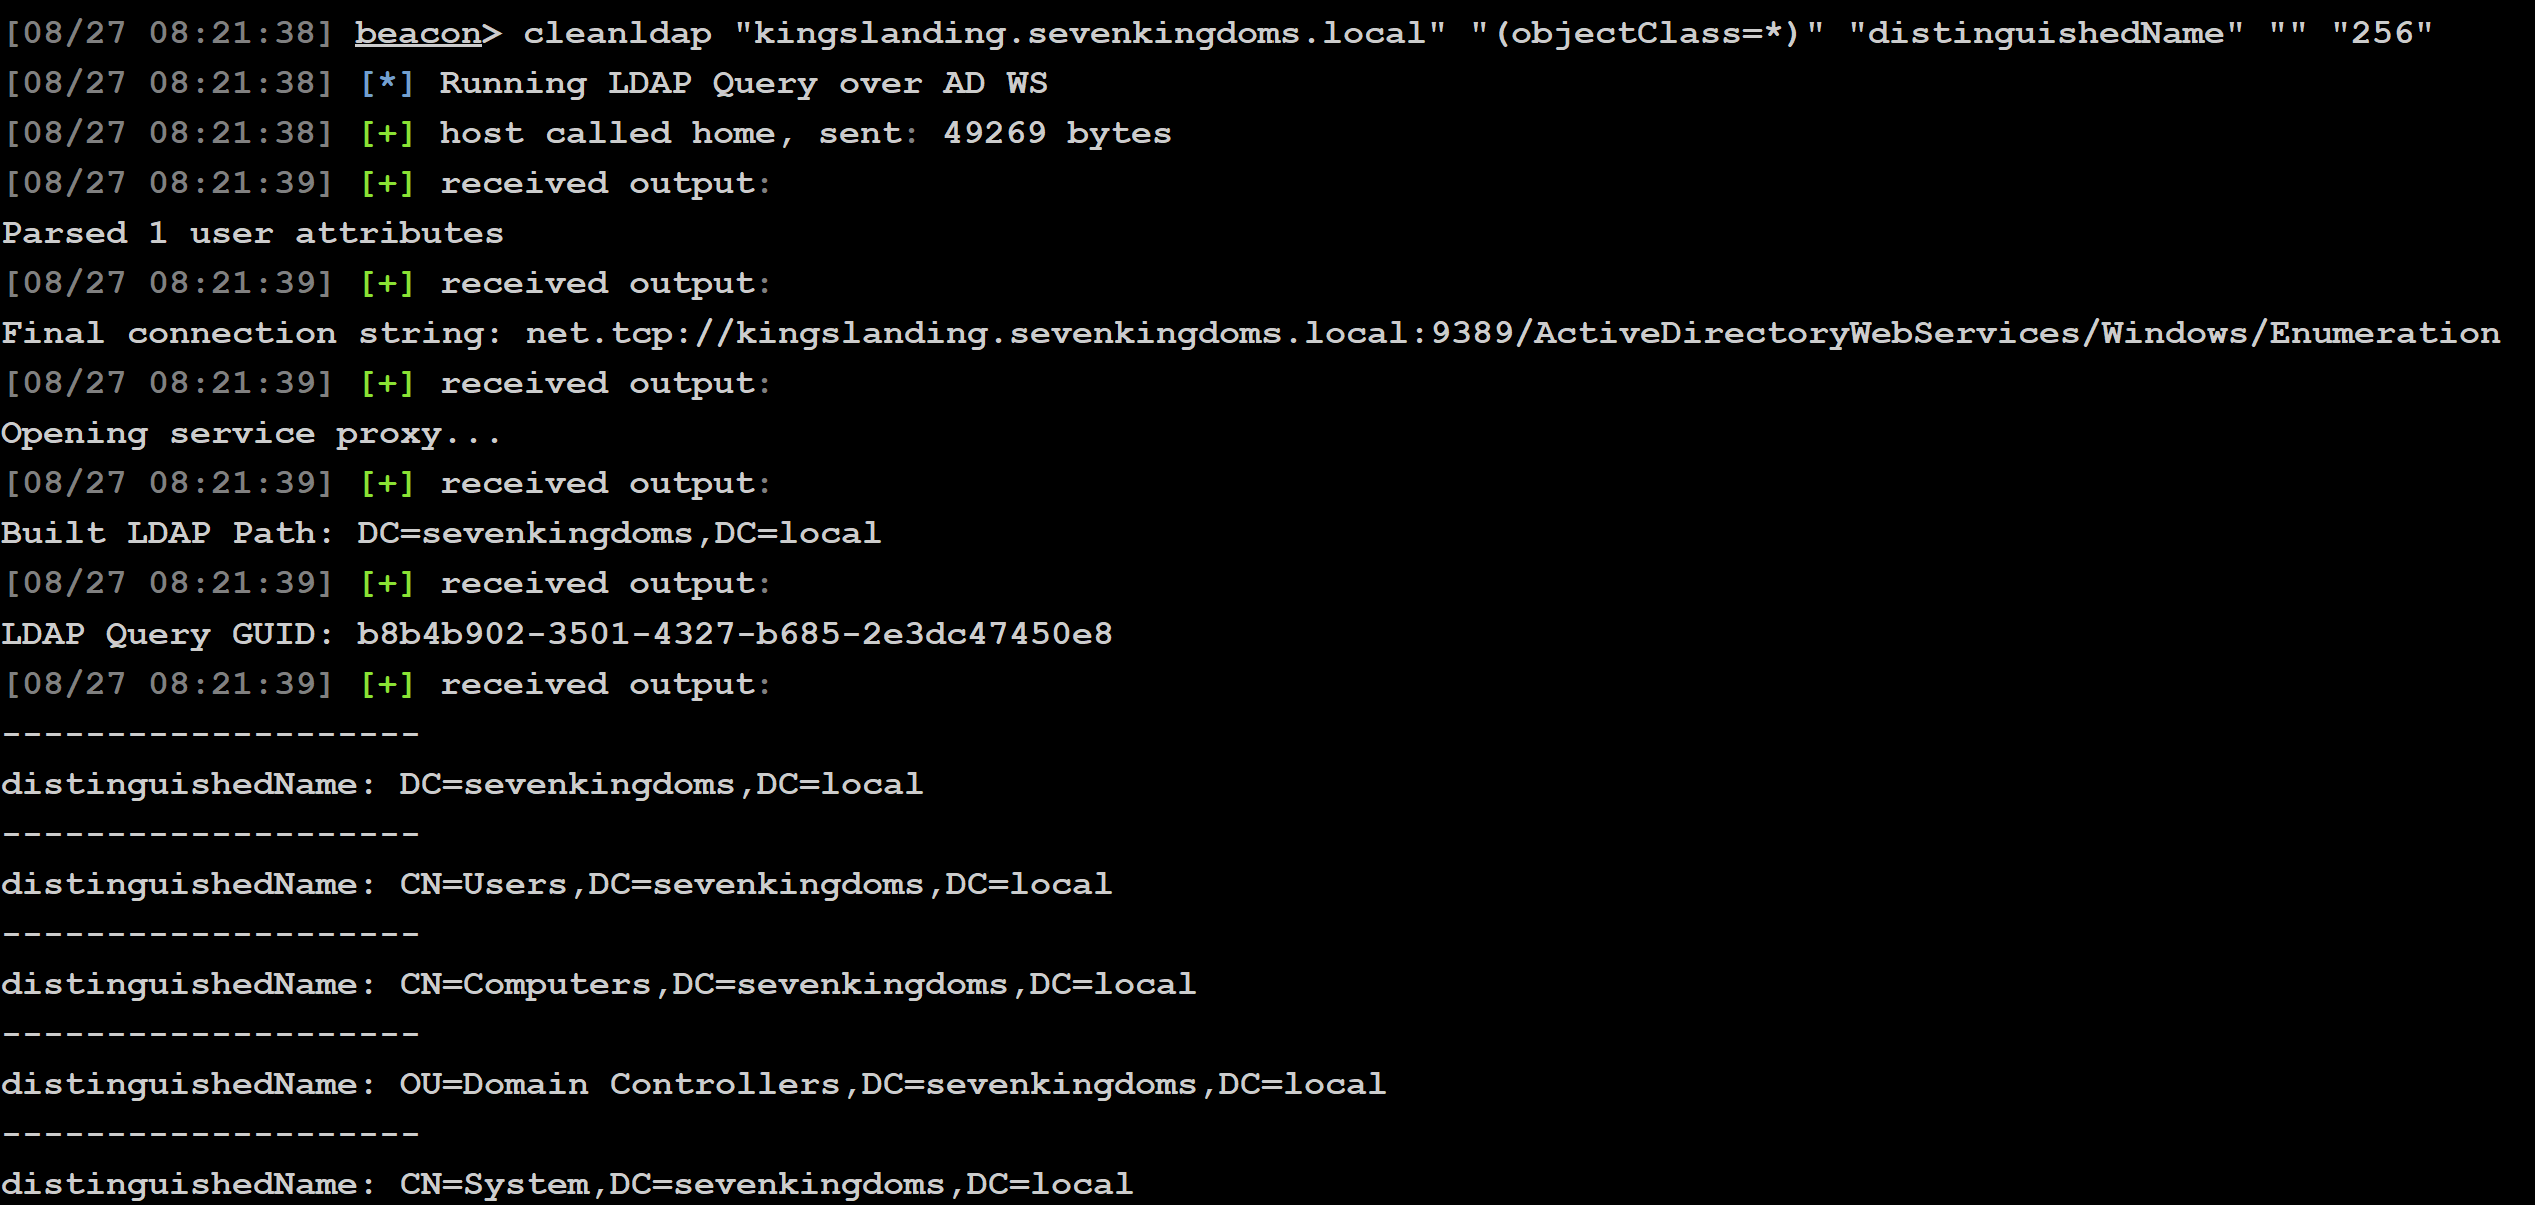 mandiant/cleanldap
Stealthy LDAP query BOF for Active Directory reconnaissance via AD WS, enabling attribute enumeration and data collection for red team operations.
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
 kgoins/ldsview
Offline LDAP directory dump search tool with LDIF parsing, entity filtering, UAC flag translation, and ldapsearch command generation for Active…
 idarlingteam/idarling
Collaborative Reverse Engineering plugin for IDA Pro & Hex-Rays
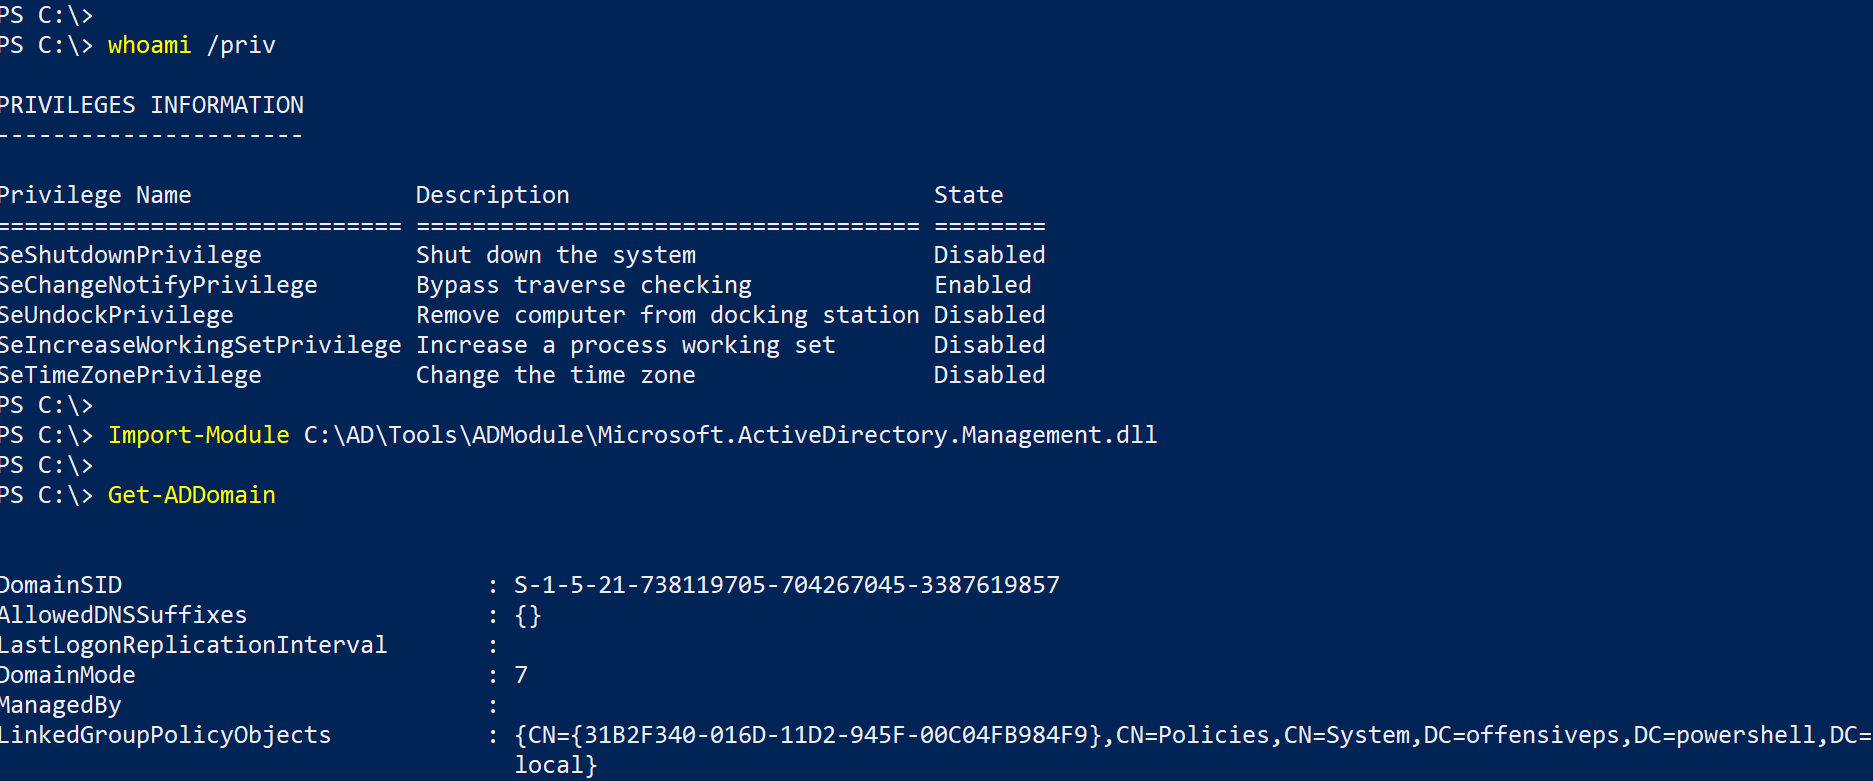 samratashok/admodule
Microsoft signed ActiveDirectory PowerShell module