
archlive
 p3ng0s/archlive
Physical access red team live ISO built on Arch Linux
password-crackingpenetration-testingpost-exploitation+2
p3ng0s/archlivePhysical access red team live ISO built on Arch Linux
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 vulncheck-oss/cli
VulnCheck's official command line tool
 qmonnet/rbpf
Rust virtual machine and JIT compiler for eBPF programs
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 gmh5225/keypatchx
KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 mrechofi/greedos_v2
A Multi-vector DoS tool for Cybersecurity Red Teamers' .
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 nmatt0/moria
IoT firmware identification and extraction
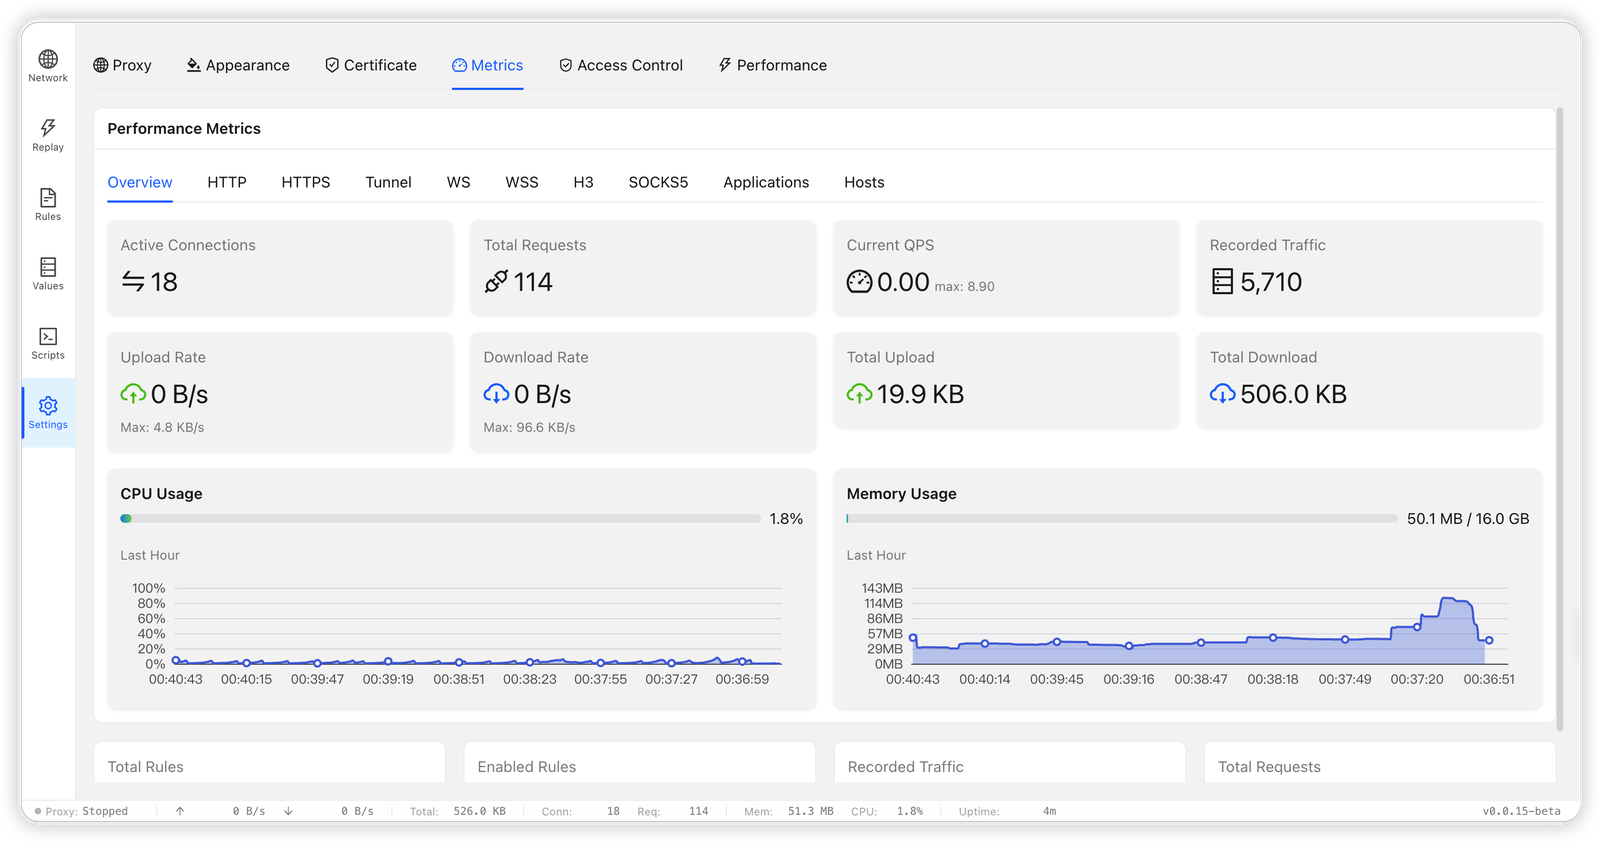 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench