
obfuscation_analysis
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
binary-analysiscode-analysismalware-analysis+3
258
mrphrazer/obfuscation_analysisBinary Ninja plugin to analyze and simplify obfuscated code
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
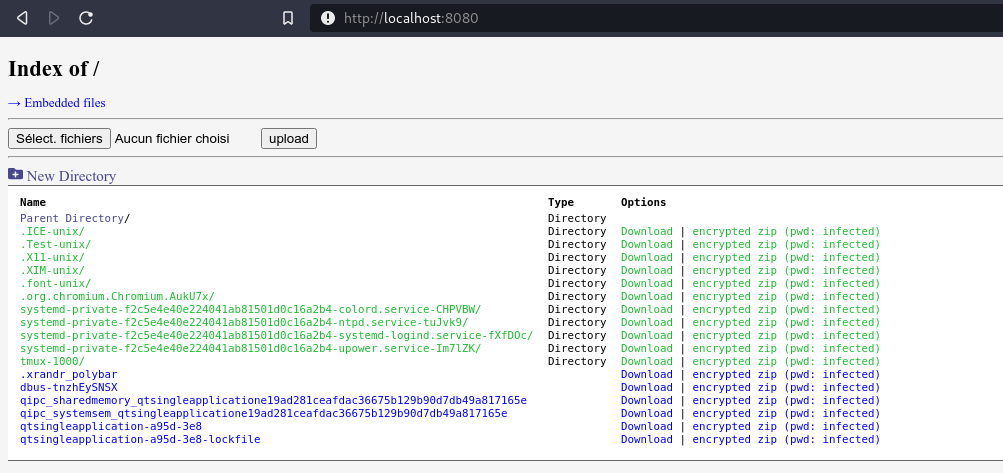 nodauf/swego
Swiss army knife Webserver in Golang. Keep simple like the python SimpleHTTPServer but with many features
 byt3bl33d3r/pymalleablec2
Python interpreter for Cobalt Strike Malleable C2 Profiles. Allows you to parse, build and modify them programmatically.
 kingsabri/sqlmap-tamper-api
SQLMap tamper api to accept tamper scripts from all languages
 mscholtes/ps2exe
Module to compile powershell scripts to executables
 gvcoder09/nodpi
Local proxy that bypasses Deep Packet Inspection by fragmenting TLS ClientHello packets, enabling access to blocked websites without requiring…
 thelicato/secbutler
The perfect butler for pentesters, bug-bounty hunters and security researchers
 aaaddress1/pr0cess
some gadgets about windows process and ready to use :)
 yanncam/exe2powershell
exe2powershell - exe2bat reborn for modern Windows
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 rasta-mouse/cswhispers
Source generator to add D/Invoke and indirect syscall methods to a C# project.
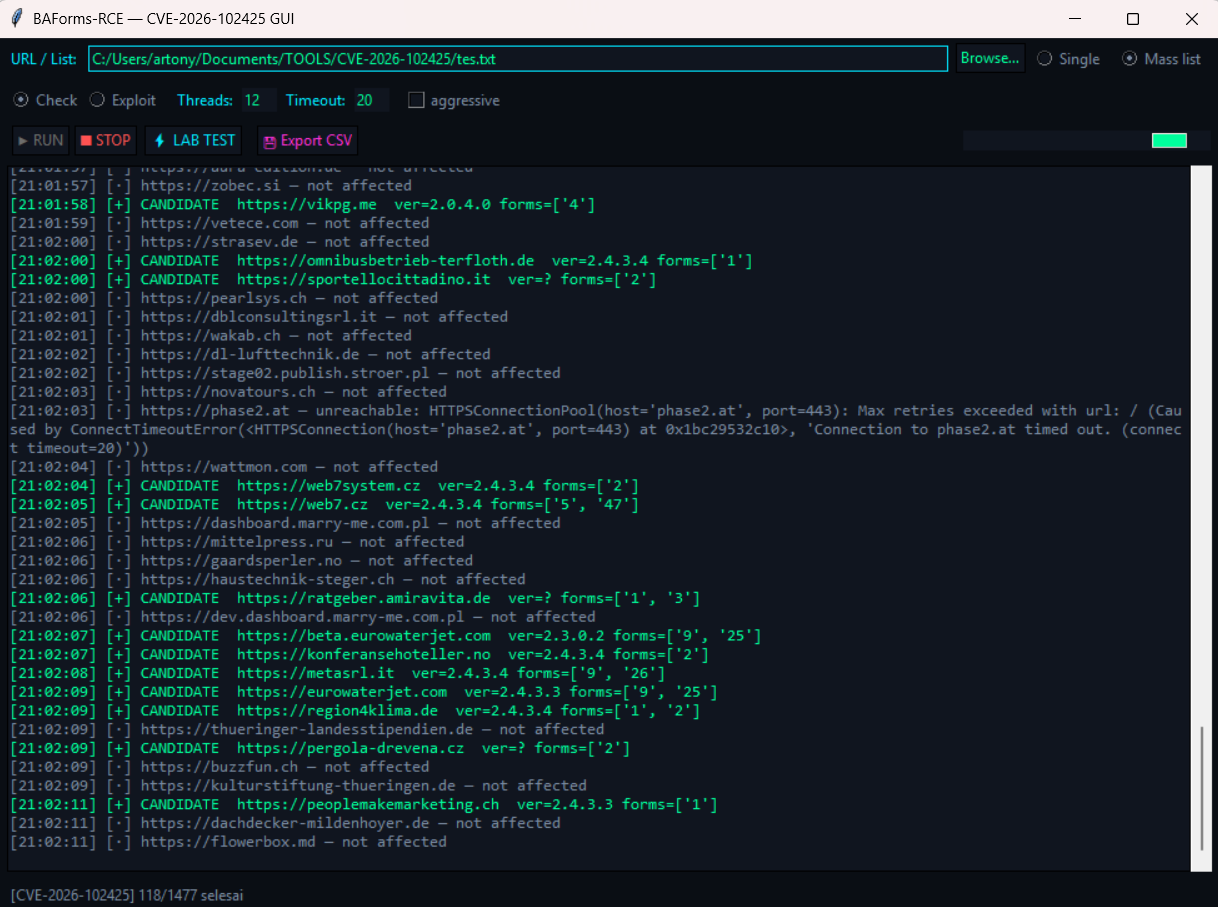 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 guibacellar/penel
[Powershell with Embedded .NET Library] Program that prepares a .NET DLL Library to run embedded in Powershell Script
 coactionbrittlemaidenhair51/coactionbrittlemaidenhair51.github.io
Explore and validate CVE-2026-42978 PoC with an integrated AI security tool, multi-protocol terminal, and autonomous agent suite for Windows Push…