
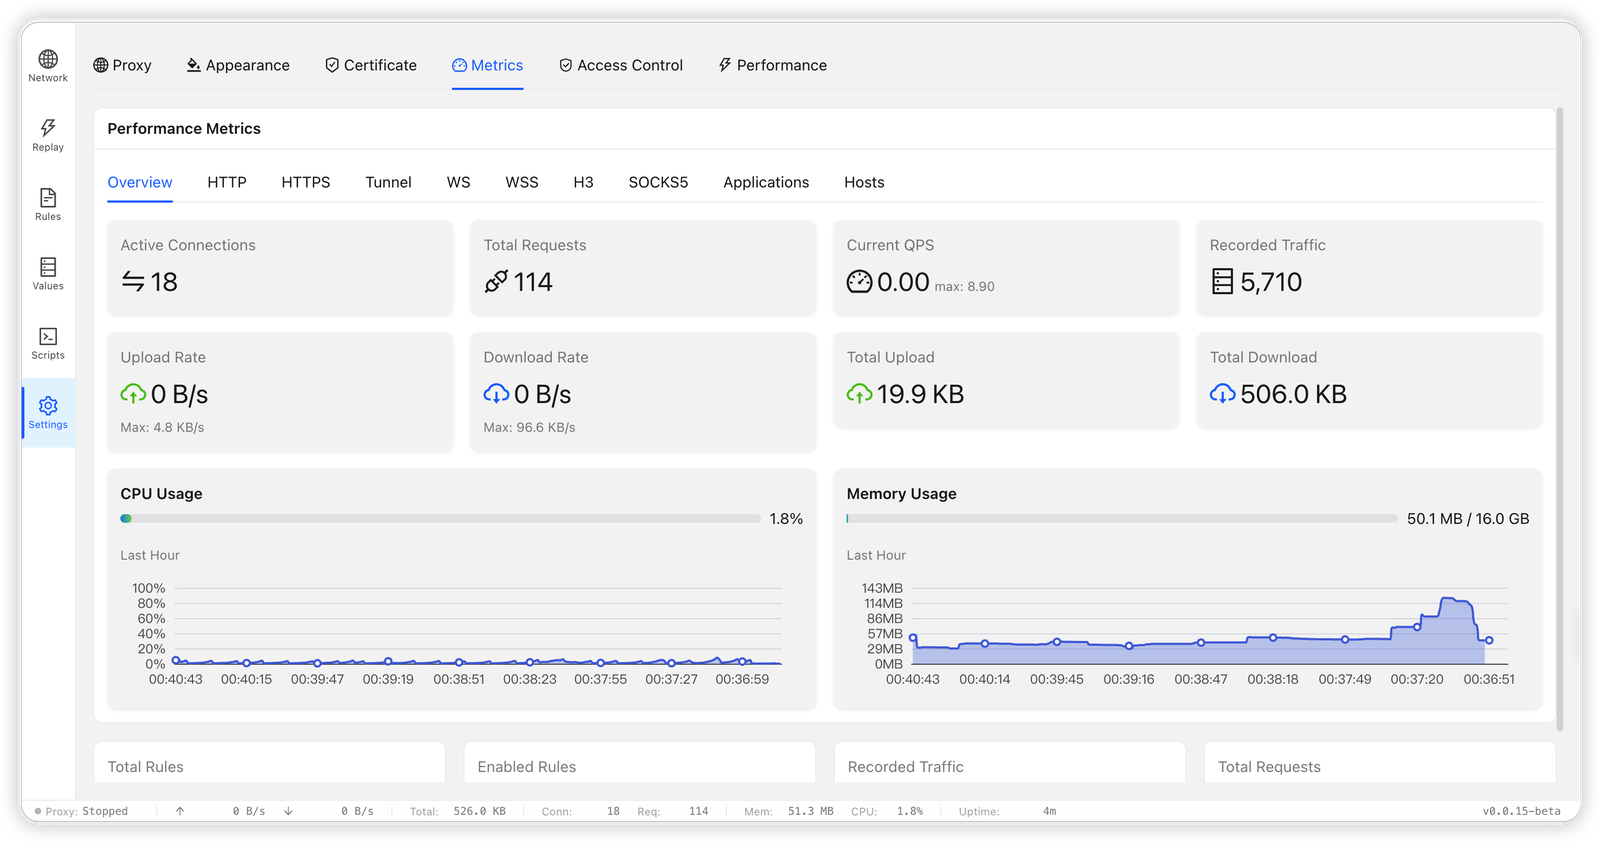
bifrost
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
api-security-testingnetwork-securitypacket-sniffing-analysis+6
161
bifrost-proxy/bifrostHigh-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
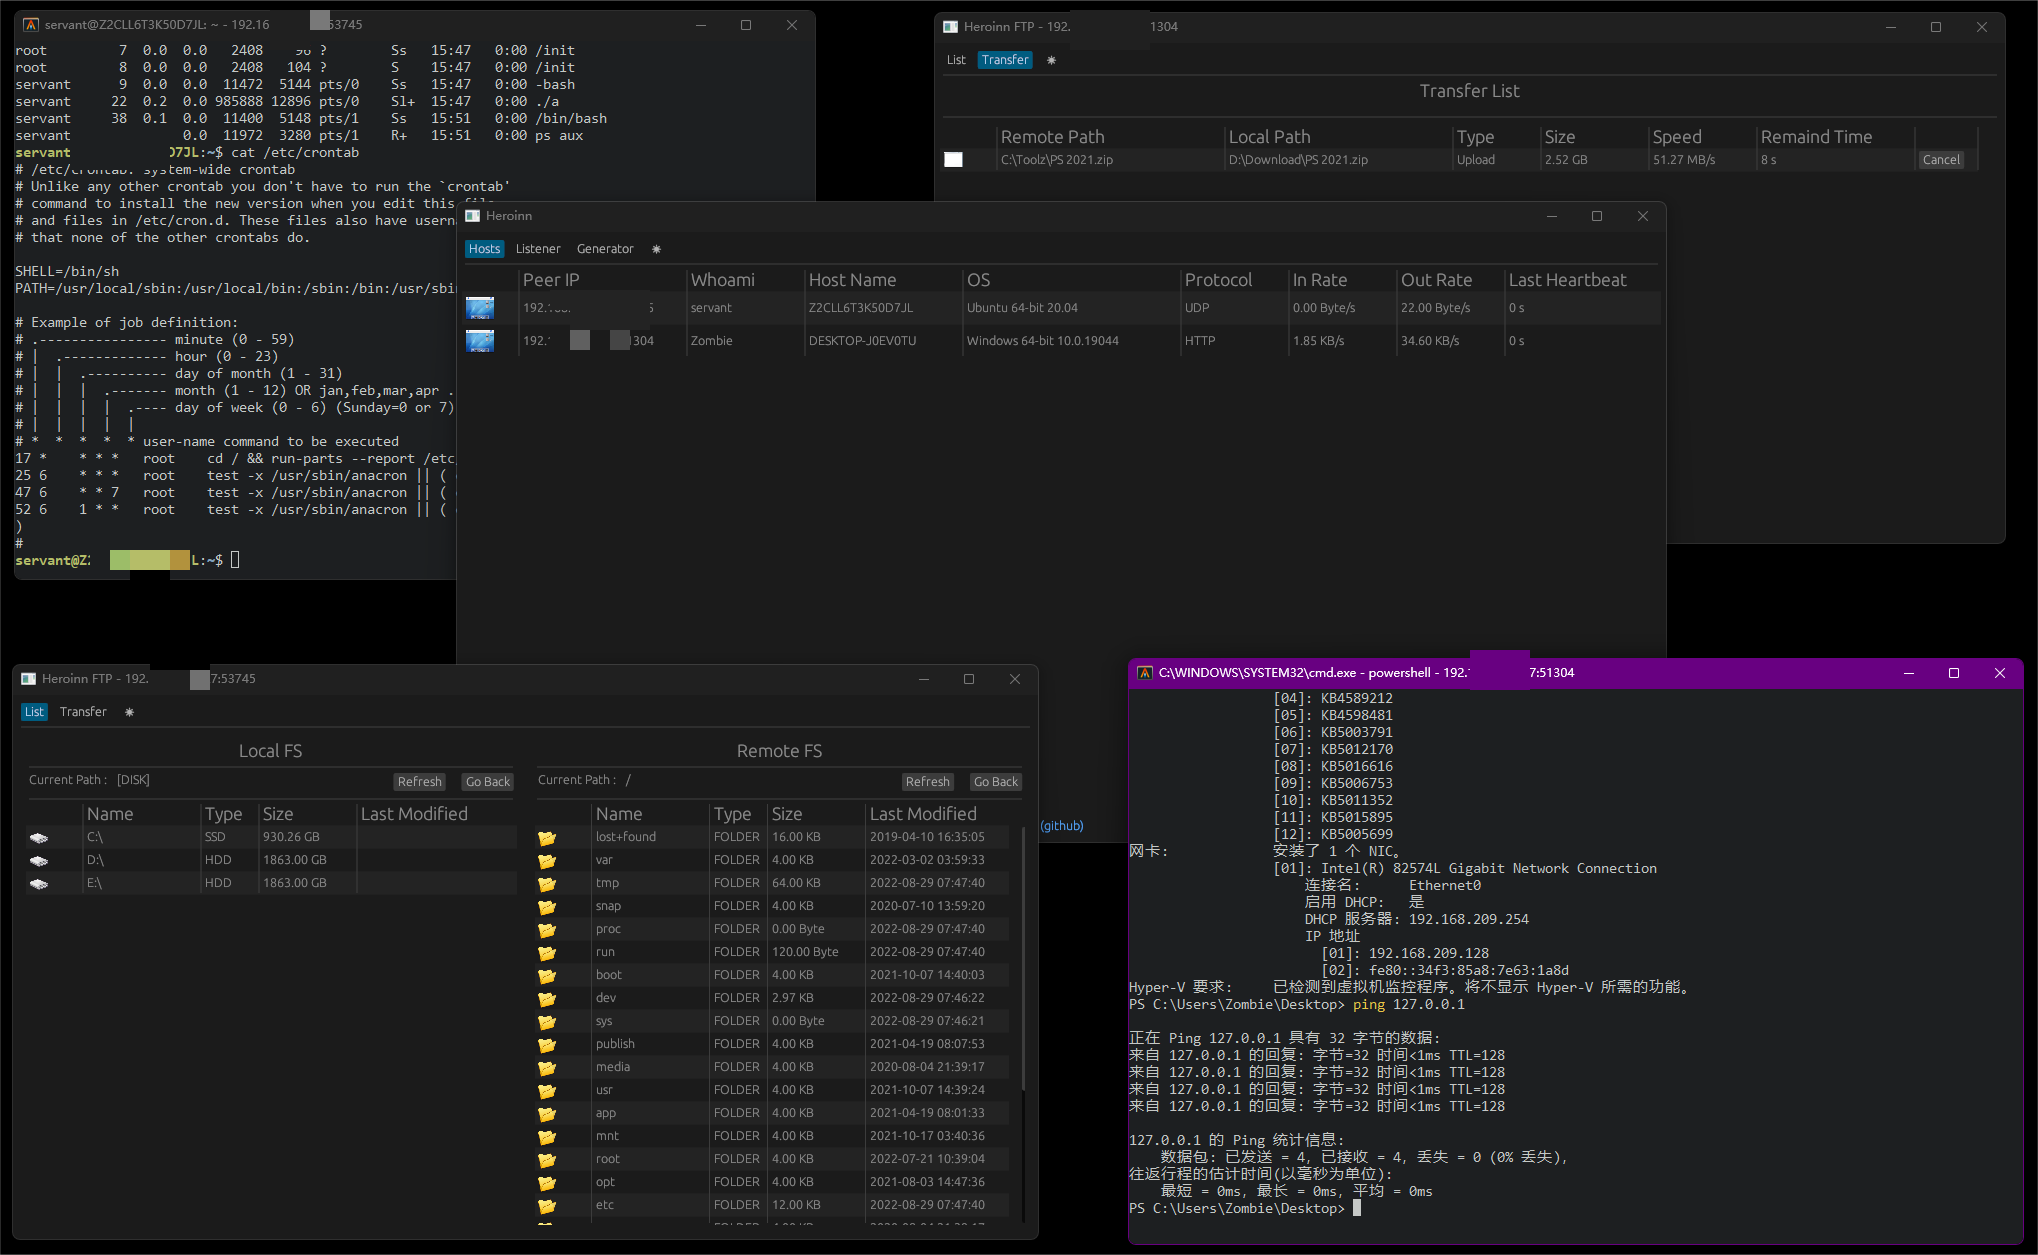 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 theporgs/exegol
Fully featured and community-driven hacking environment
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
 vulncheck-oss/cli
VulnCheck's official command line tool
 nmatt0/moria
IoT firmware identification and extraction
 garrytan/gstack
Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 mrechofi/greedos_v2
A Multi-vector DoS tool for Cybersecurity Red Teamers' .
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 rustdesk/rustdesk
An open-source remote desktop application designed for self-hosting, as an alternative to TeamViewer.
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator