Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
232 results
conti-ransomware-writeup preview

conti-ransomware-writeup

GitHubjustjeff211/conti-ransomware-writeup

Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…

digital-forensicseducationforensics+6
6 months ago
GhostTrace preview

GhostTrace

GitHubdevzinh/ghosttrace

Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…

digital-forensicsforensicsincident-response+3
2 months ago
BearFTP preview
Archived

BearFTP

GitHubkolya5544/bearftp

Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.

defensive-toolsincident-responseinformation-gathering+4
143 years ago
pywintrace preview

pywintrace

GitHubfireeye/pywintrace

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…

defensive-toolsdigital-forensicsincident-response+2
3033 years ago
LogonTracer preview

LogonTracer

GitHubjpcertcc/logontracer

Investigate malicious Windows logon by visualizing and analyzing Windows event log

ai-securitydigital-forensicsincident-response+2
3.3k2 months ago
fleet-cve-scanner preview

fleet-cve-scanner

GitHubboostedchaos/fleet-cve-scanner

An open-source, single-script CVE scanner for RMM-managed fleets. Pure PowerShell 7 — joins your RMM software inventory against NVD, CISA KEV, EPSS…

configuration-auditingincident-responselog-analysis+3
122 months ago
Get-AppLockerEventlog preview

Get-AppLockerEventlog

GitHubromaissaadjailia/get-applockereventlog

This is a repo for fetching Applocker event log by parsing the win-event log

forensicsincident-responselog-analysis+1
294 years ago
Zircolite preview

Zircolite

GitHubwagga40/zircolite

A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs

forensicsincident-responselog-analysis+1
8552 days ago
APT-Hunter preview

APT-Hunter

GitHubahmedkhlief/apt-hunter

APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…

forensicsincident-responselog-analysis+1
1.4k15 days ago
ALFA preview

ALFA

GitHubinvictus-ir/alfa

Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…

cloud-securitydigital-forensicsforensics+3
1861 month ago
amcache-evilhunter preview

amcache-evilhunter

GitHubcristianzsh/amcache-evilhunter

Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.

digital-forensicsforensicsincident-response+2
1147 days ago
IATelligence preview

IATelligence

GitHubfr0gger/iatelligence

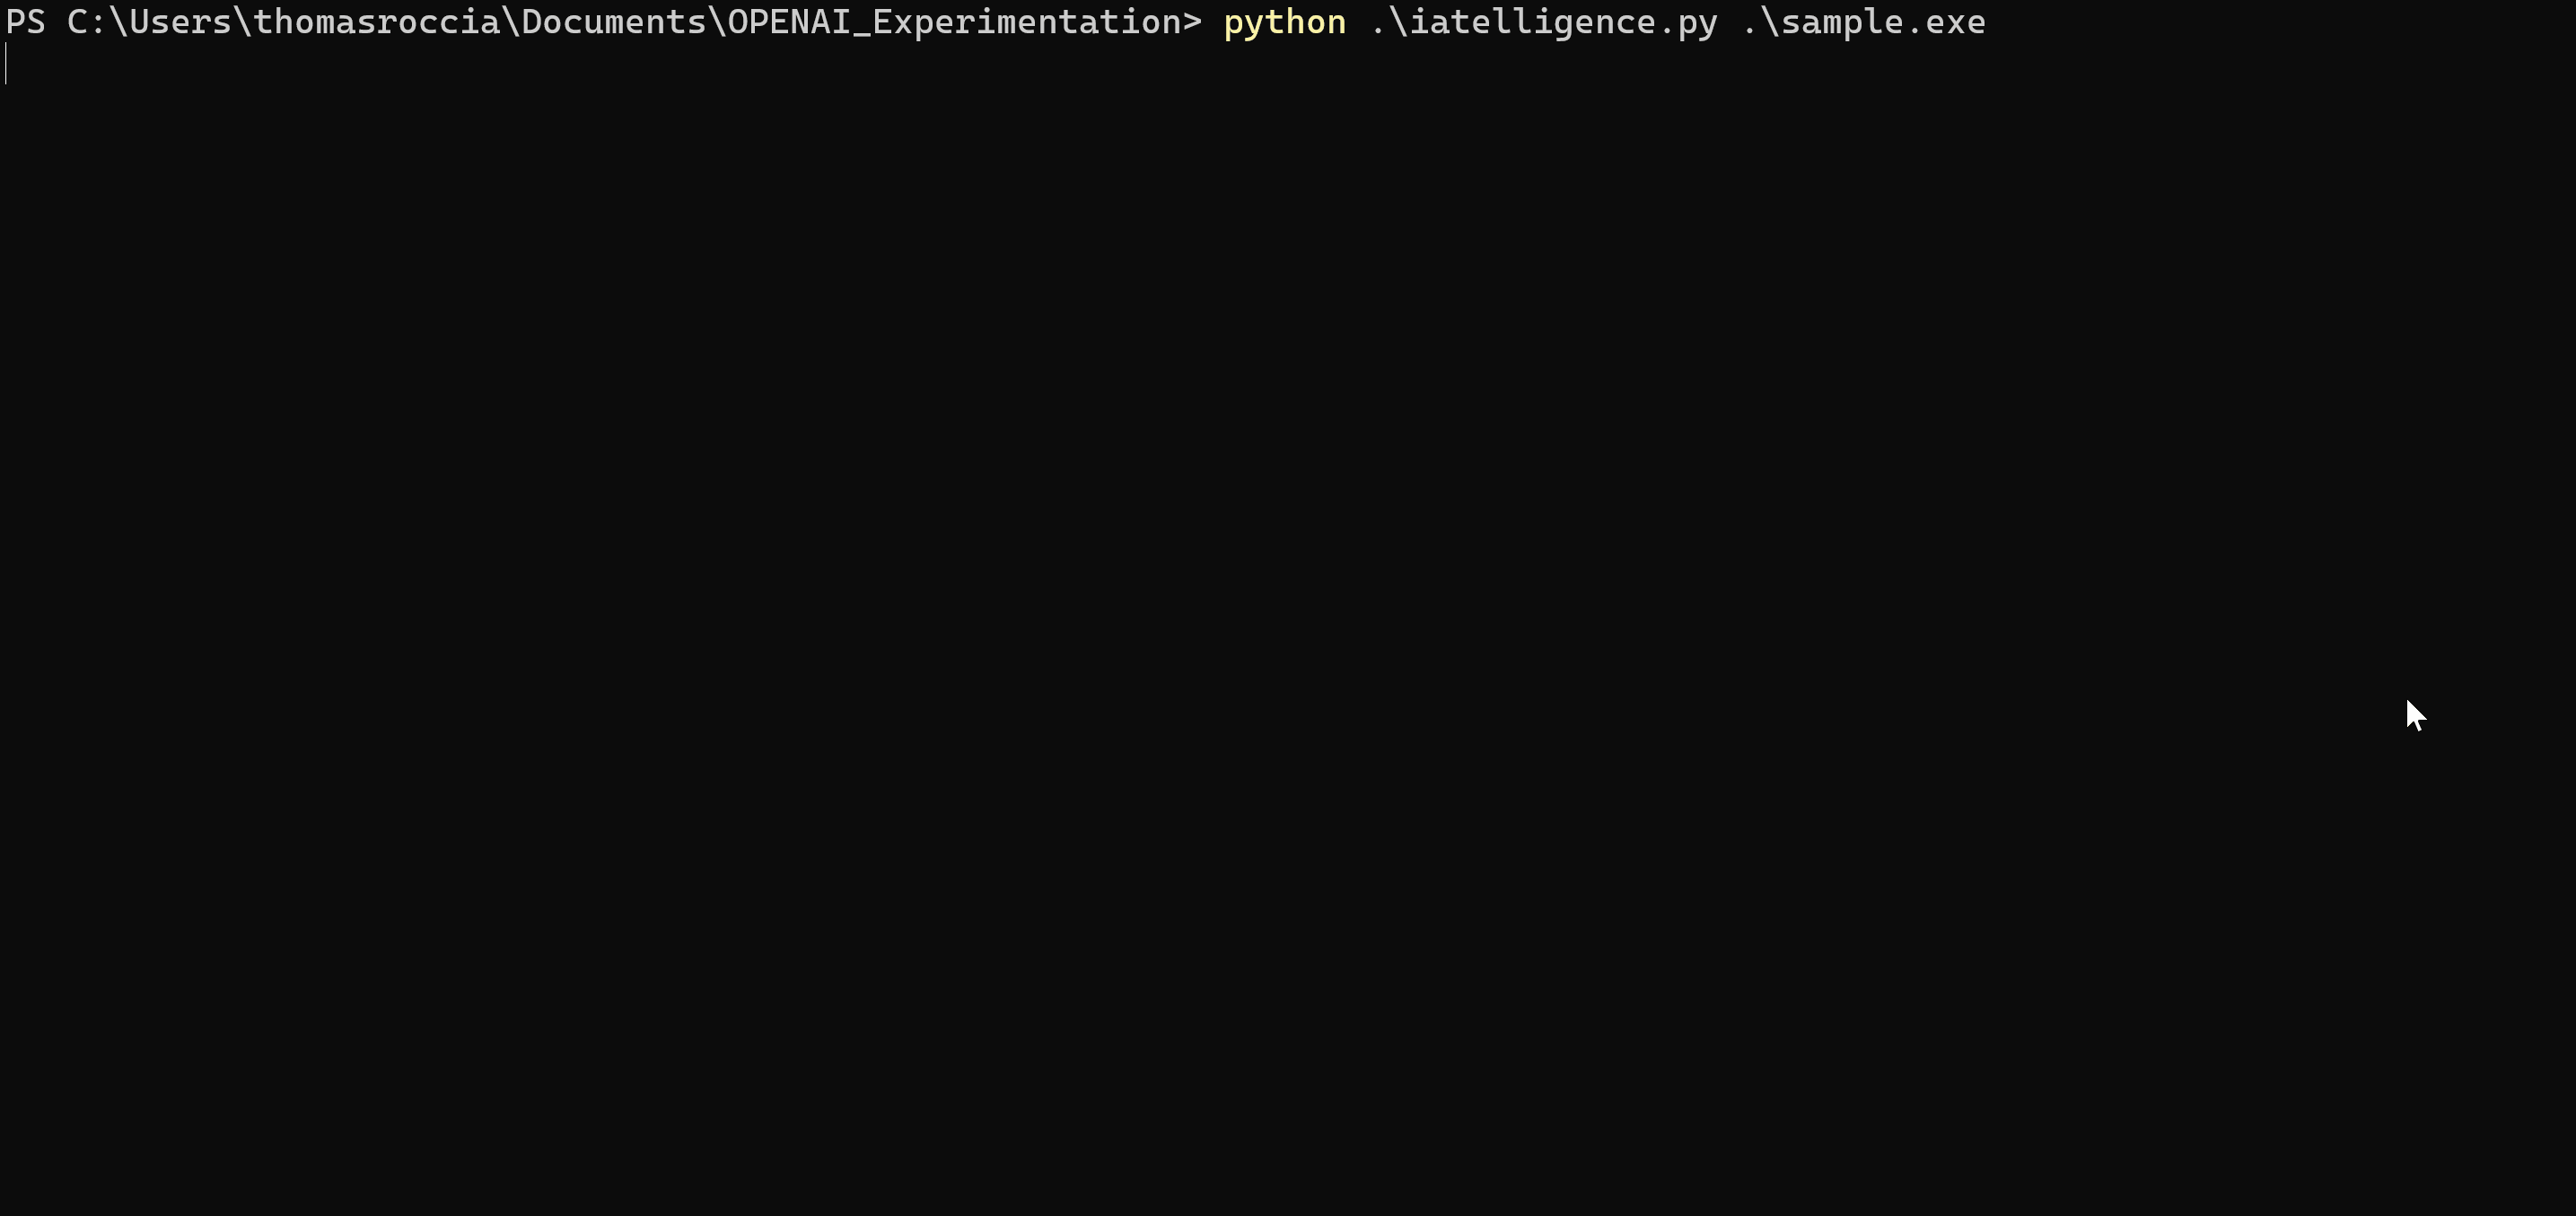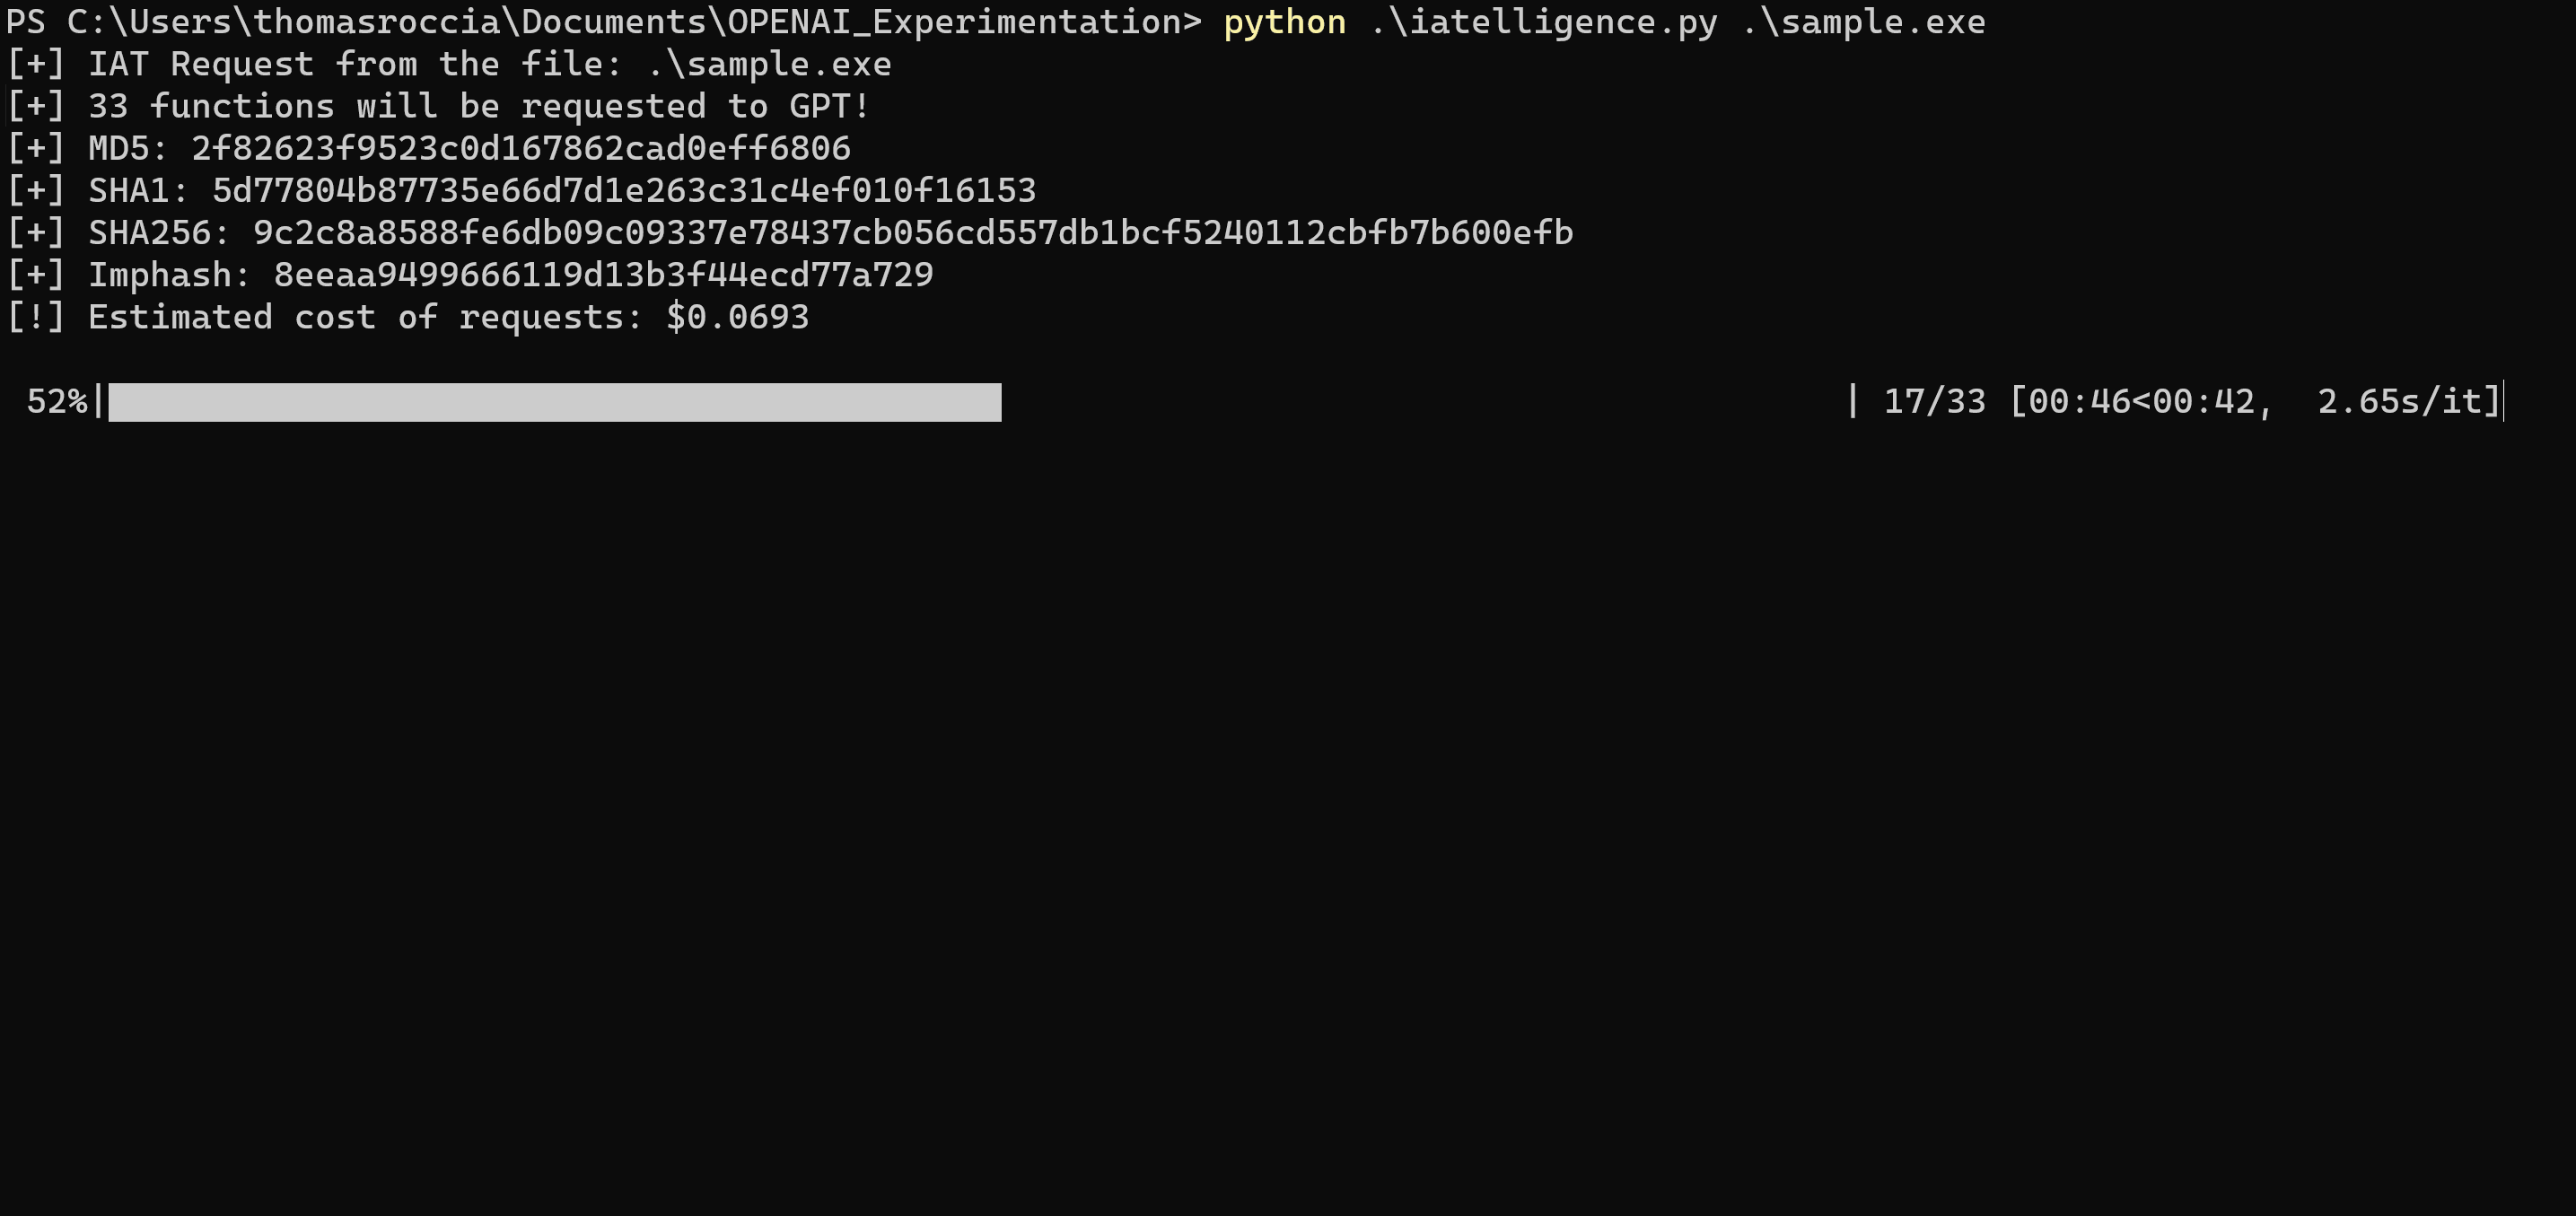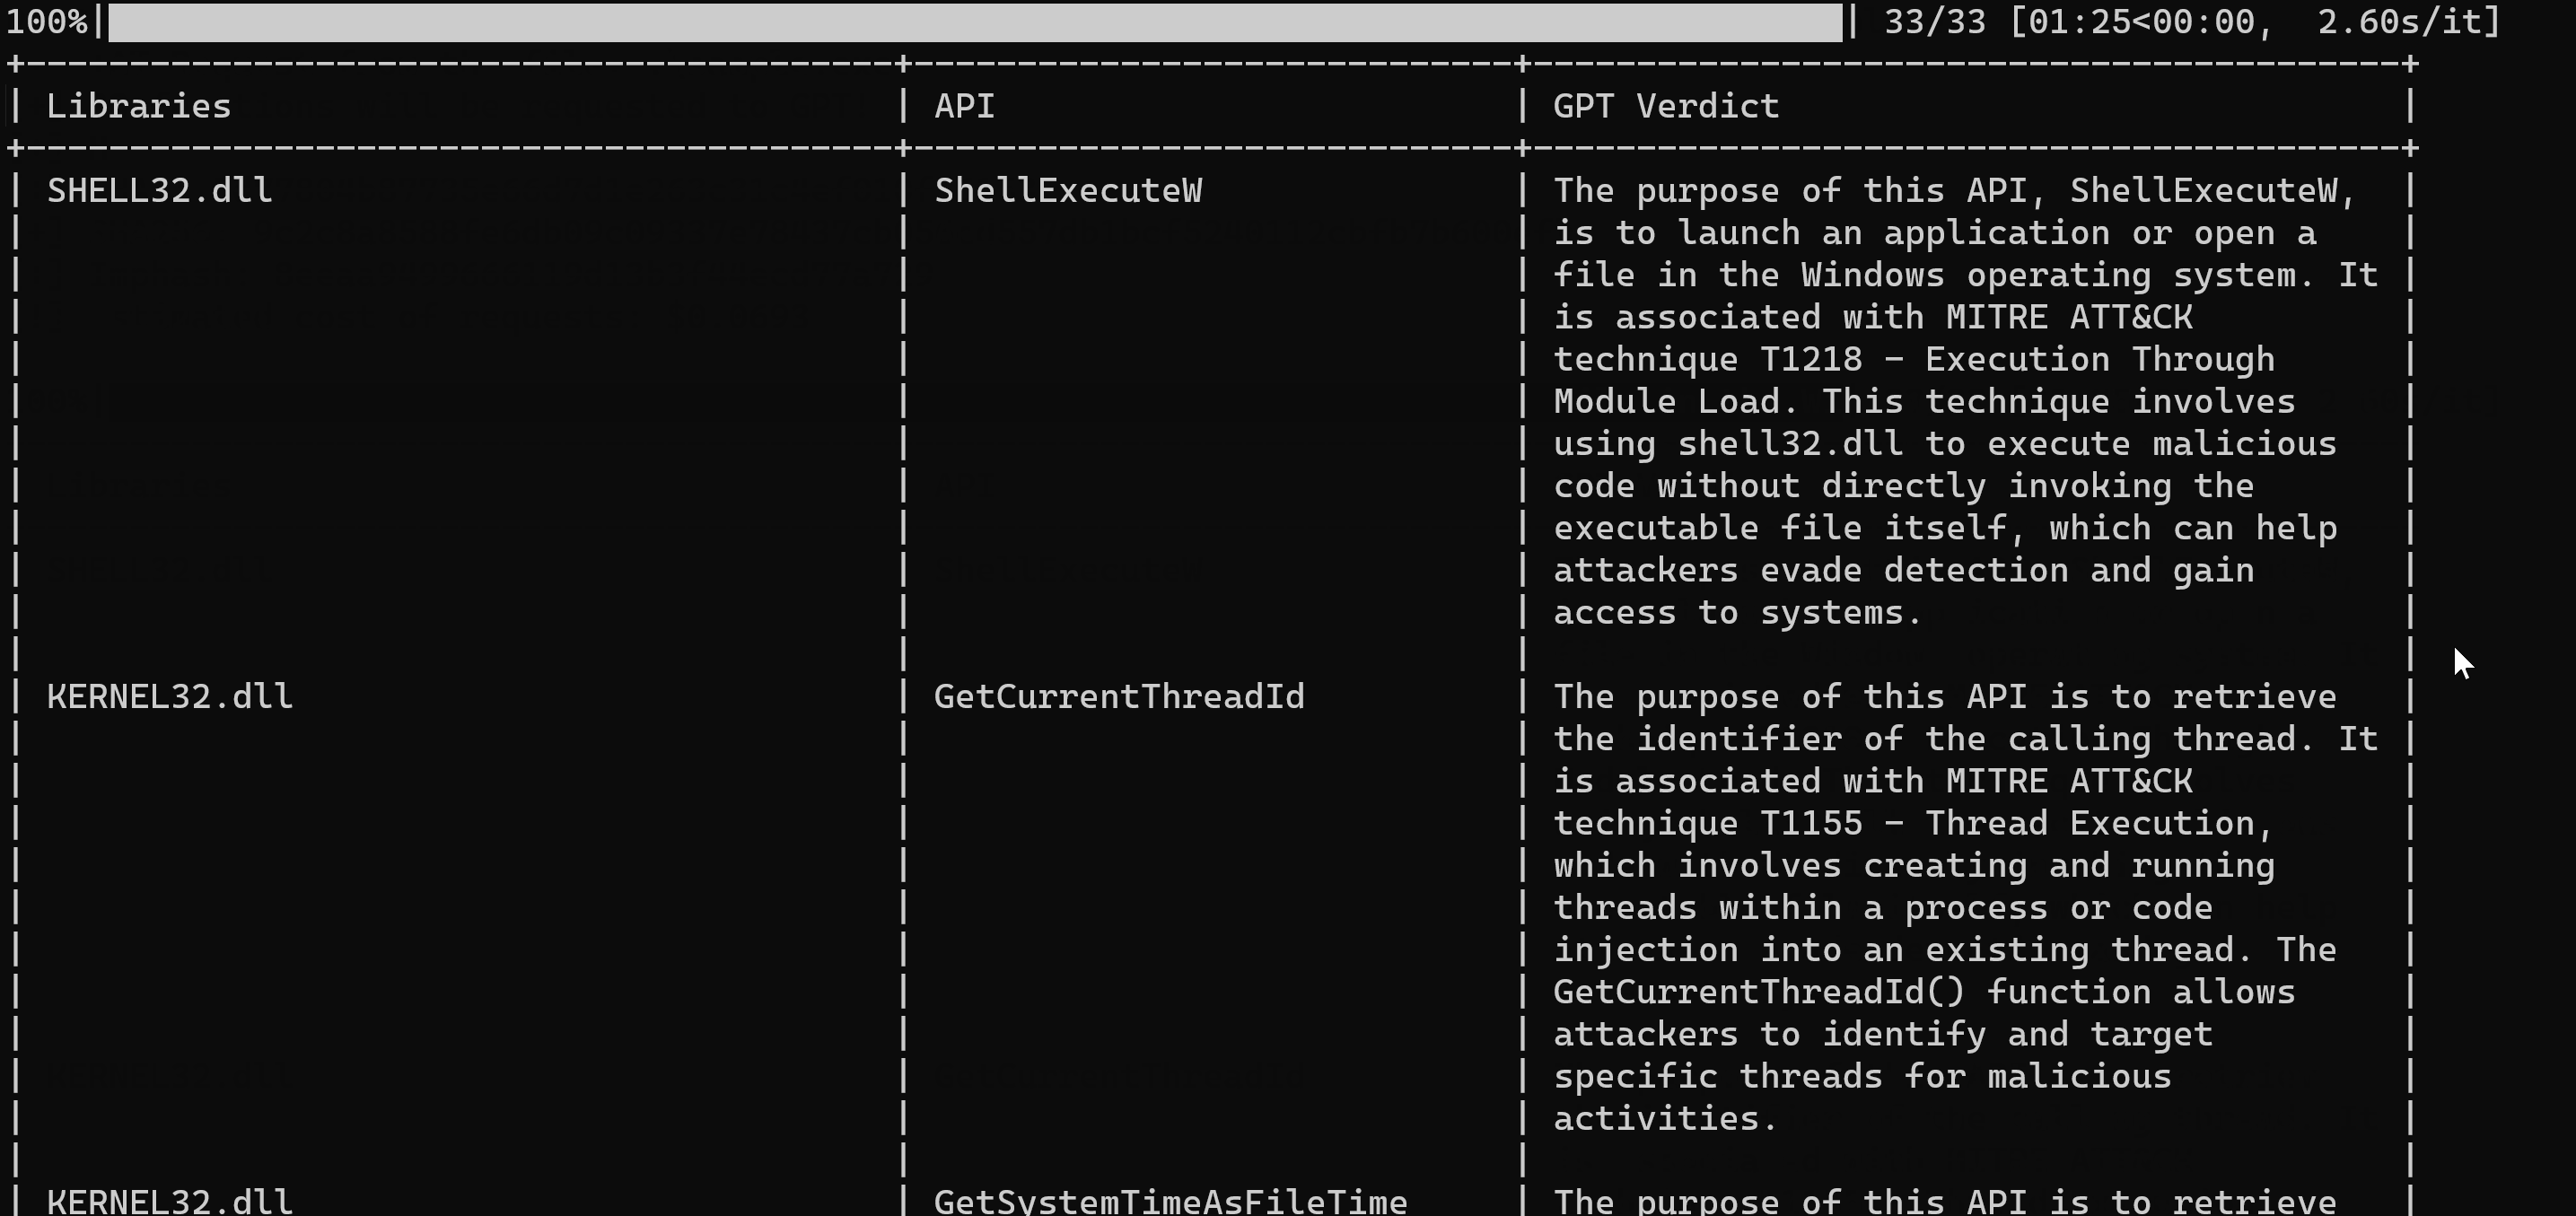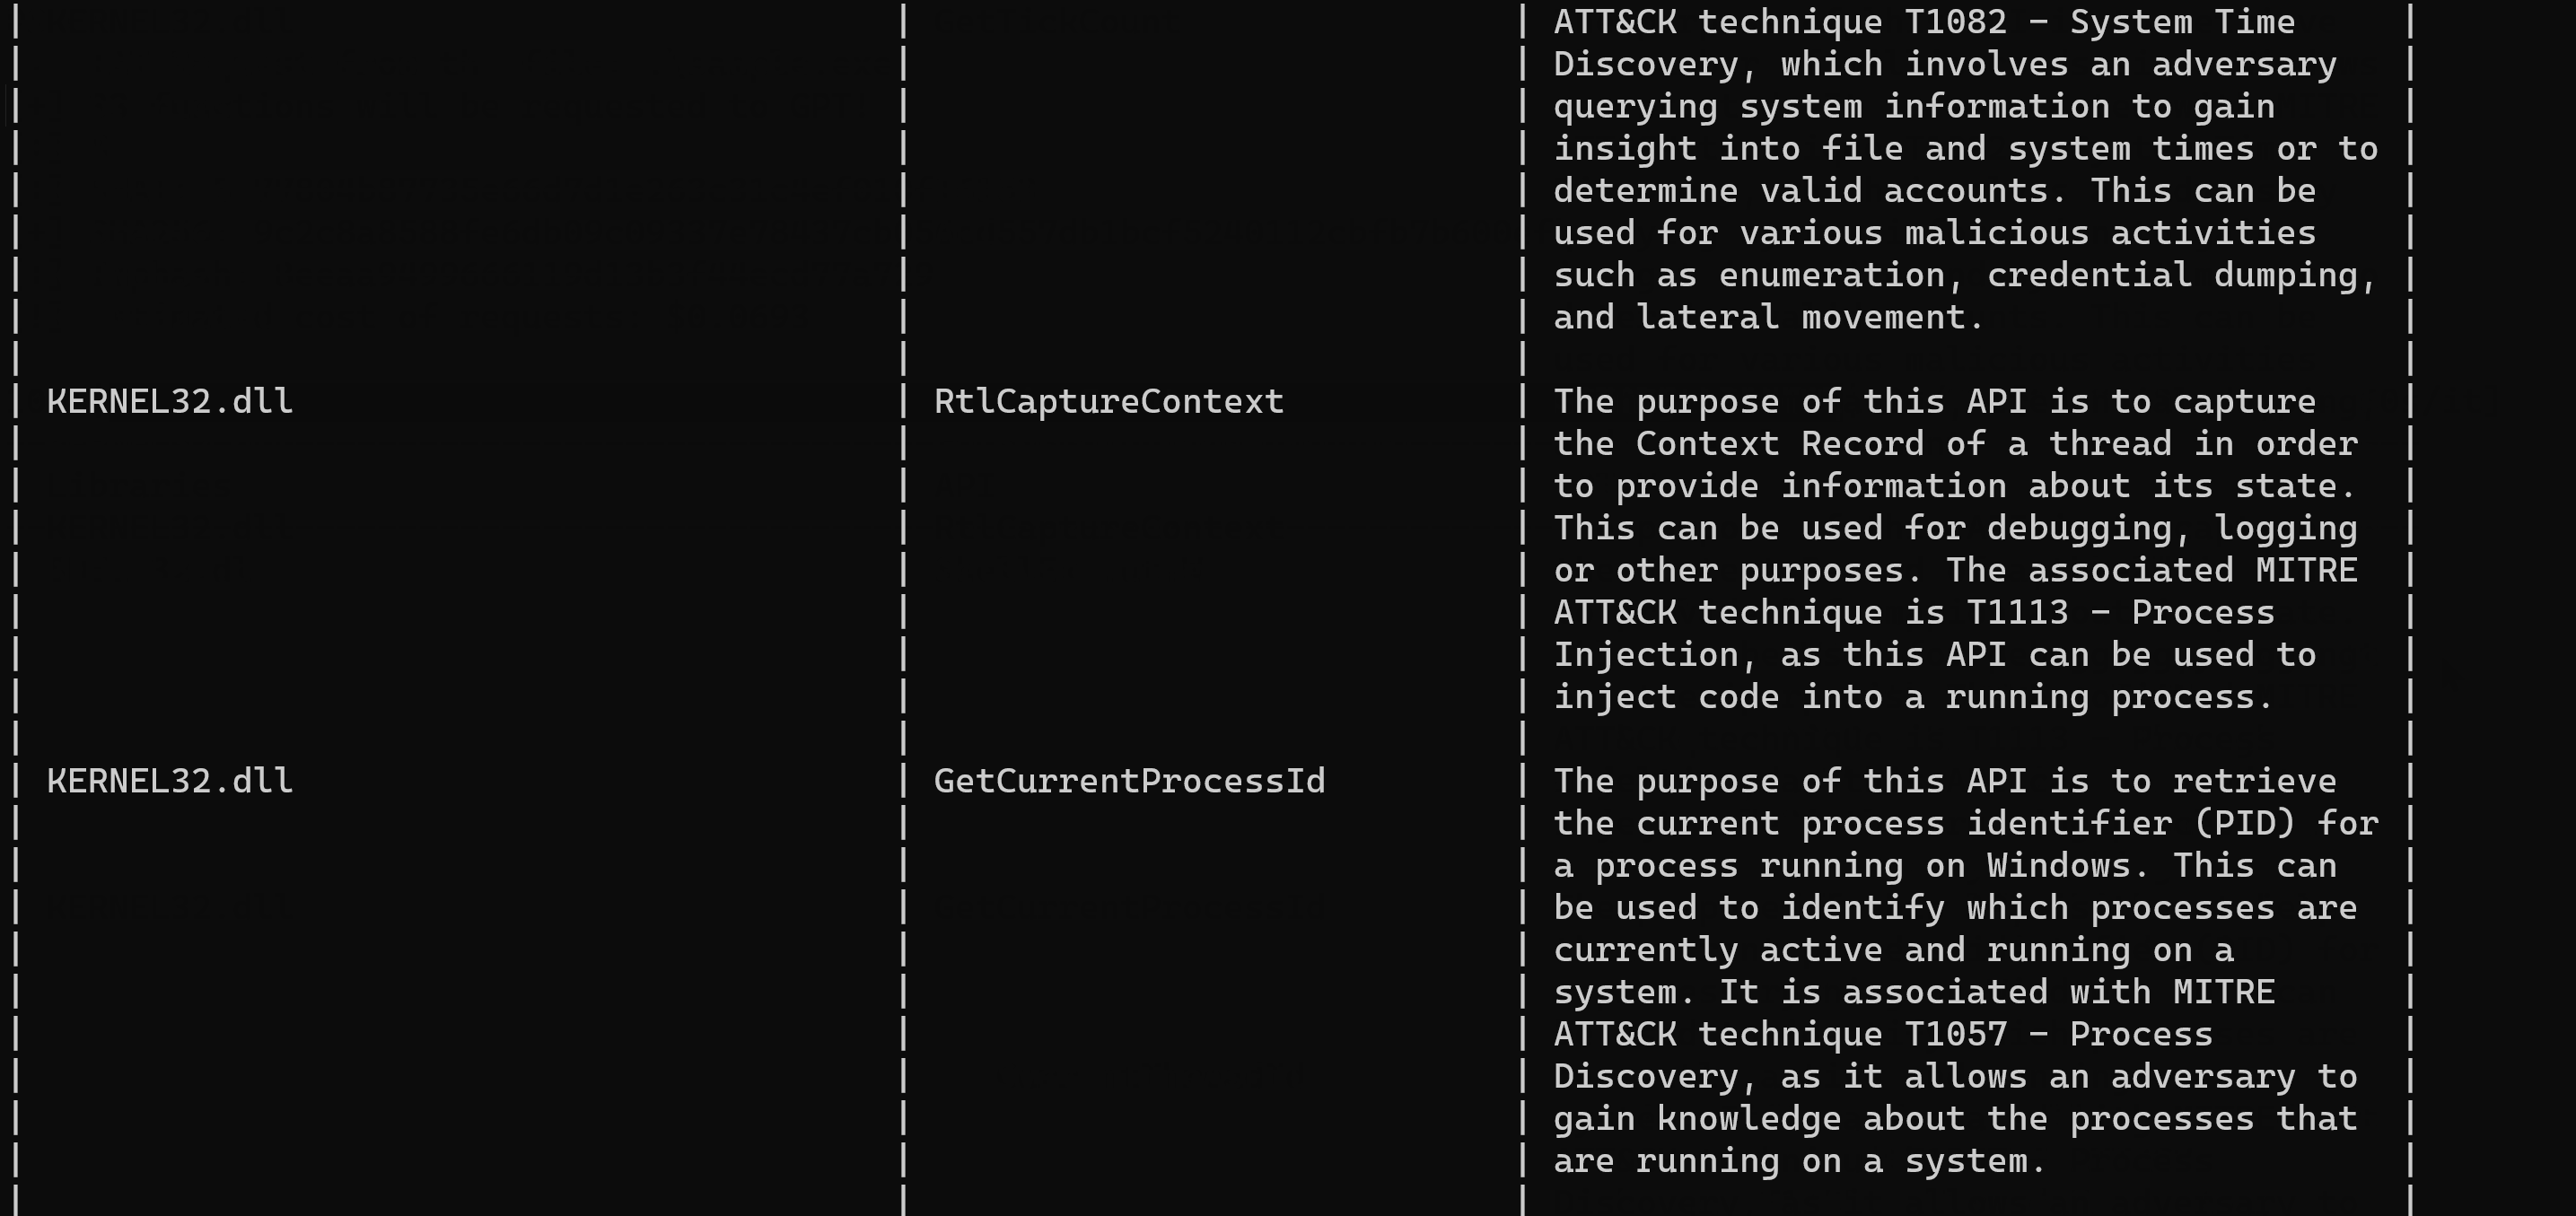
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…

ai-assisted-reversingbinary-analysismalware-analysis+3
3863 years ago
kratosminifilter preview

kratosminifilter

GitHubmukendi/kratosminifilter

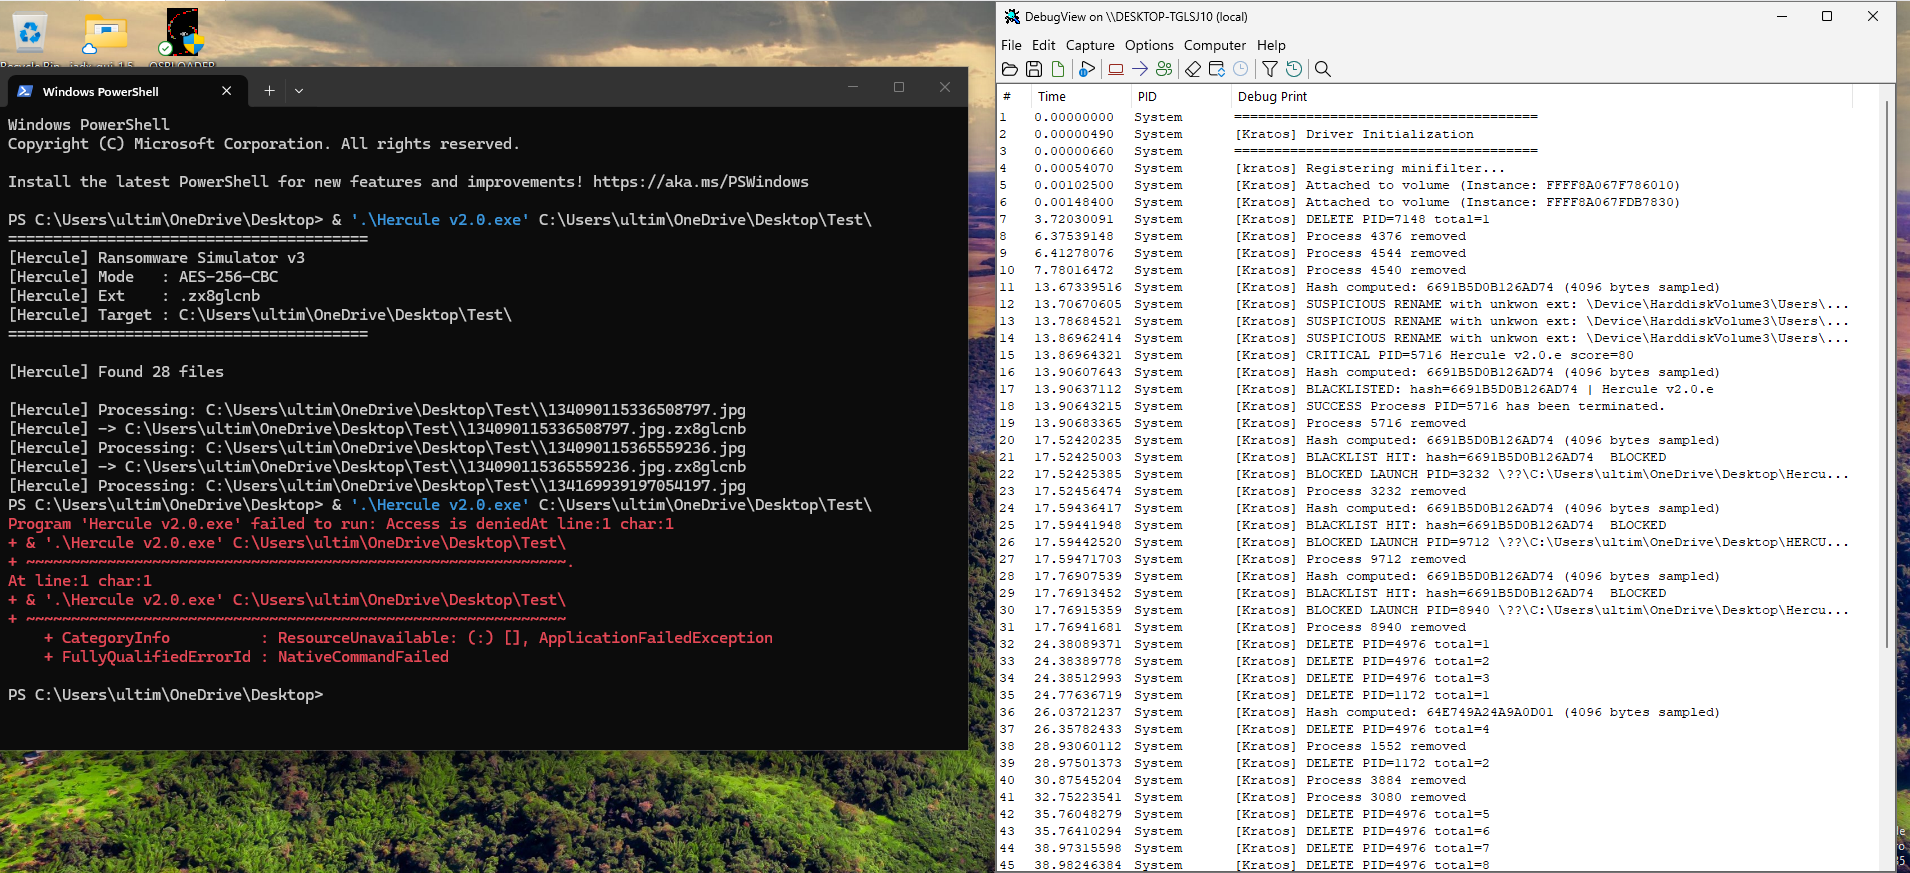
Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize

anomaly-detectiondefensive-toolsincident-response+2
419 days ago
FLAIR preview

FLAIR

GitHubwithsecurelabs/flair

Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…

digital-forensicsforensicsincident-response+2
165 years ago
WEFFLES preview

WEFFLES

GitHubjepaynemsft/weffles

Build a fast, free, and effective Threat Hunting/Incident Response Console with Windows Event Forwarding and PowerBI

incident-responselog-analysisthreat-intelligence
2028 years ago
DShield-SIEM preview

DShield-SIEM

GitHubbruneaug/dshield-siem

DShield Sensor Log Collection with ELK

defensive-toolsincident-responseintrusion-detection+4
501 month ago
CVE-2022-29072 preview

CVE-2022-29072

GitHubsentinelblue/cve-2022-29072

** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…

exploitationincident-responselog-analysis+3
84 years ago
CVE-2025-50154 preview

CVE-2025-50154

GitHubzenzue/cve-2025-50154

PowerShell toolkit to audit, harden, and hunt for insecure NTLM/SMB usage, addressing CVE-2025-50154 credential leak risks with event log analysis…

authenticationconfiguration-auditingdefensive-tools+7
31 year ago
Previous12…13Next