
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
122 results
refinery preview

refinery

GitHubbinref/refinery

High Octane Triage Analysis

binary-analysiscryptographyforensics+4
87112h 9m ago
freki preview

freki

GitHubcristianzsh/freki

Open-source malware analysis platform with static PE analysis, YARA pattern matching, VirusTotal integration, REST API, and Docker deployment for…
binary-analysismalware-analysisreverse-engineering+2
4462 years ago
IATelligence preview

IATelligence

GitHubfr0gger/iatelligence

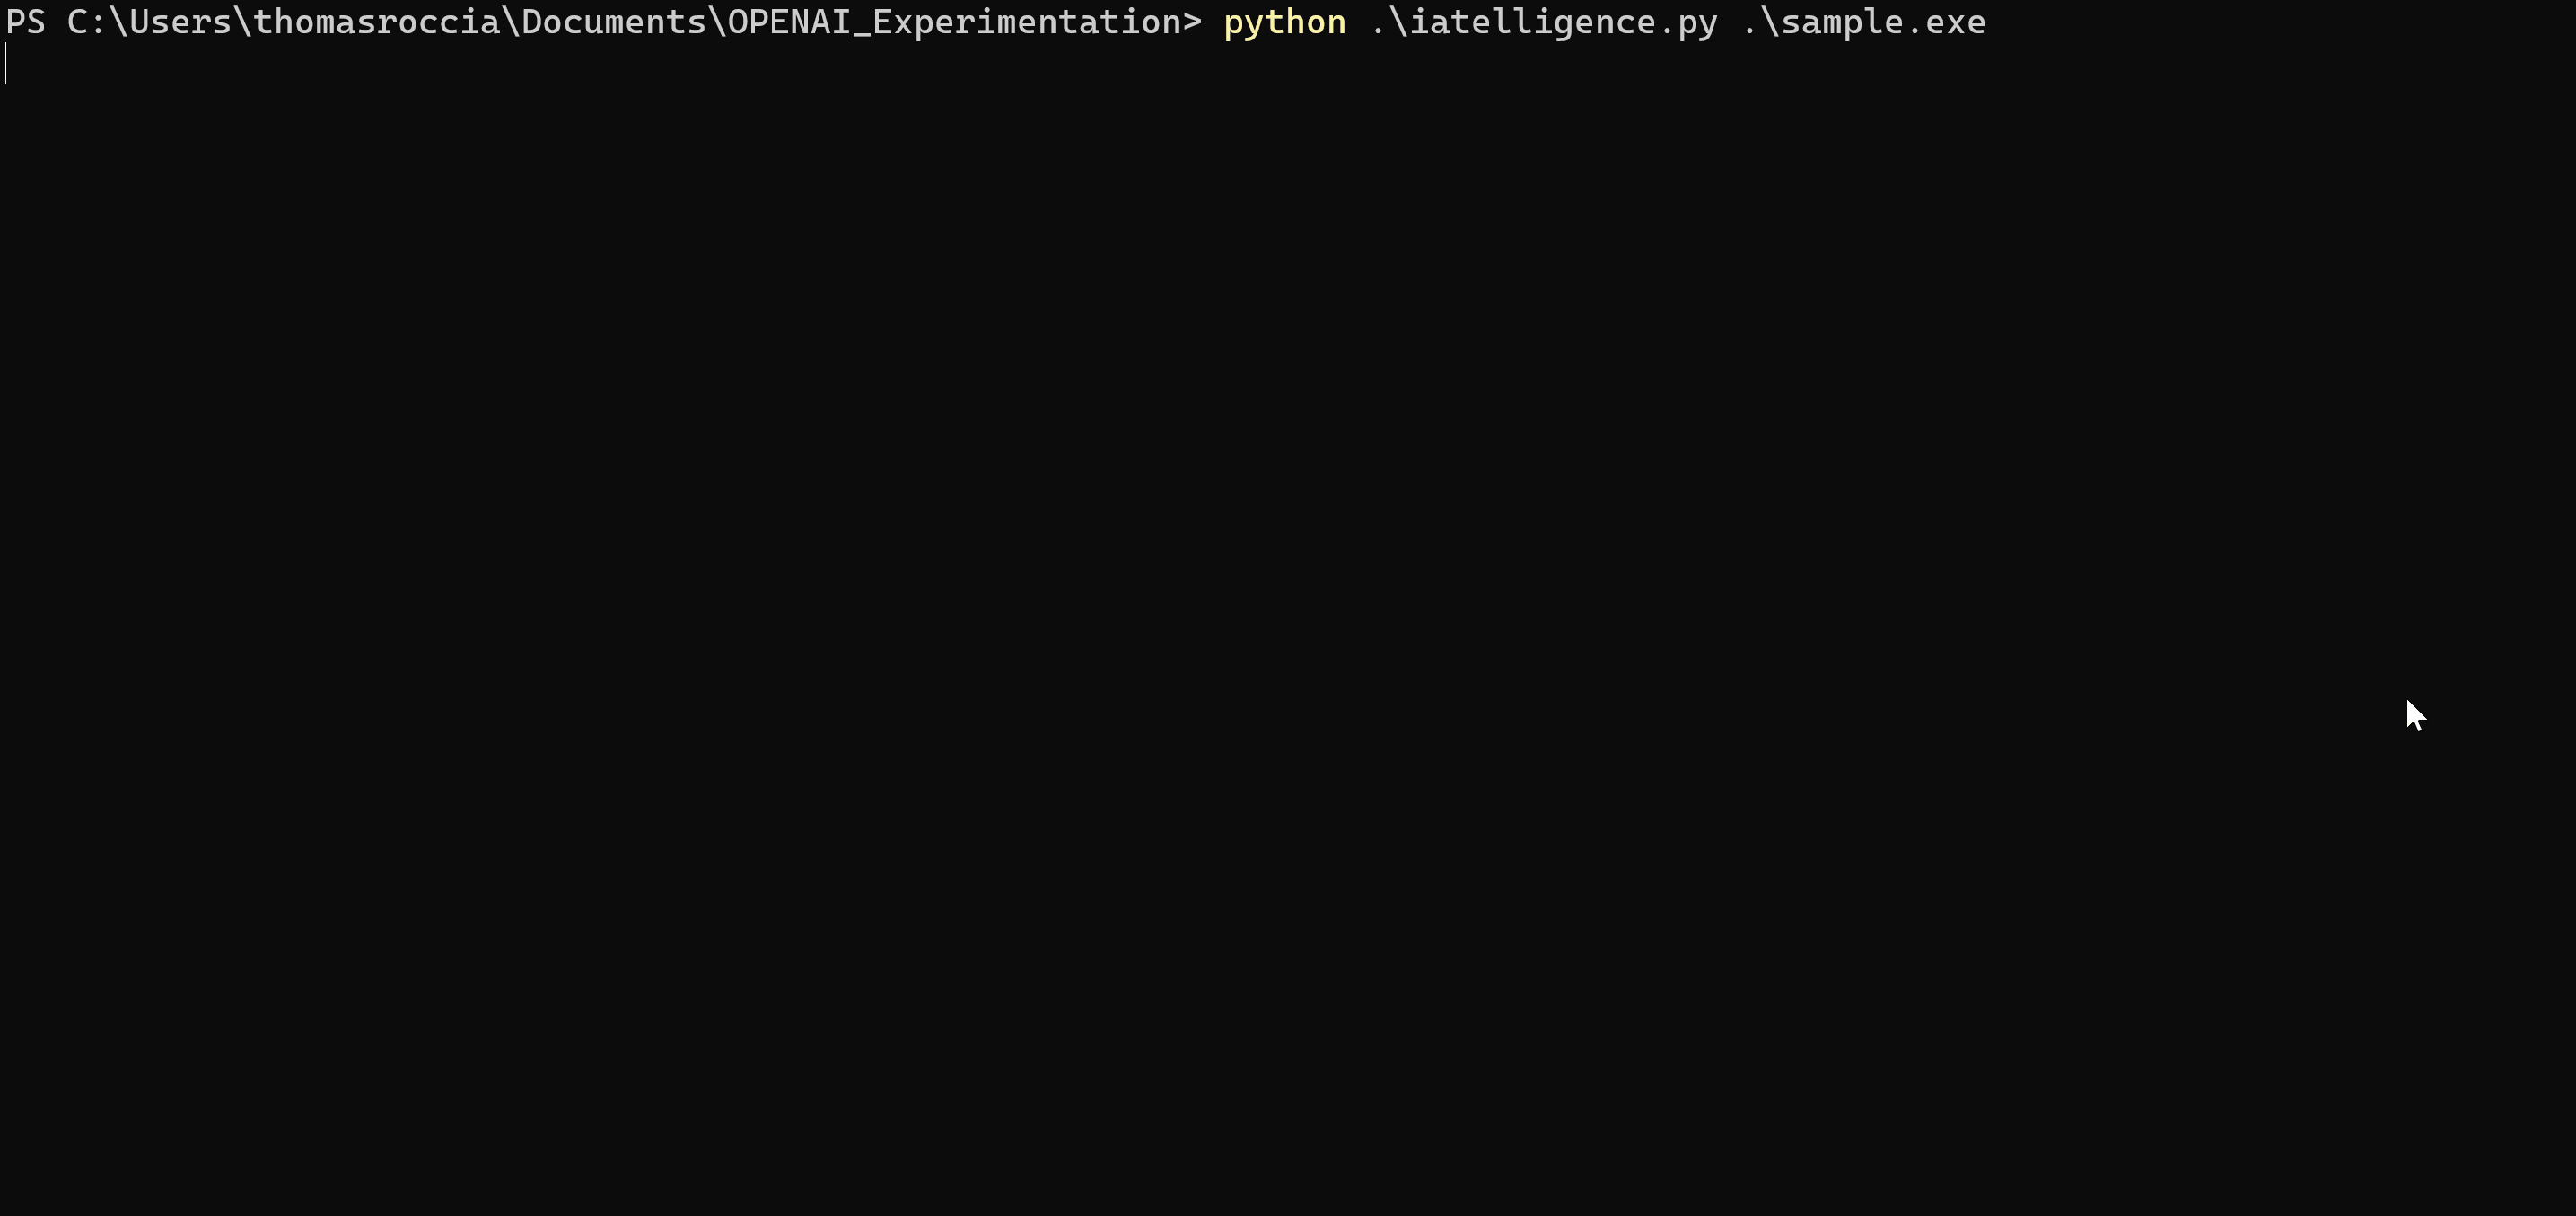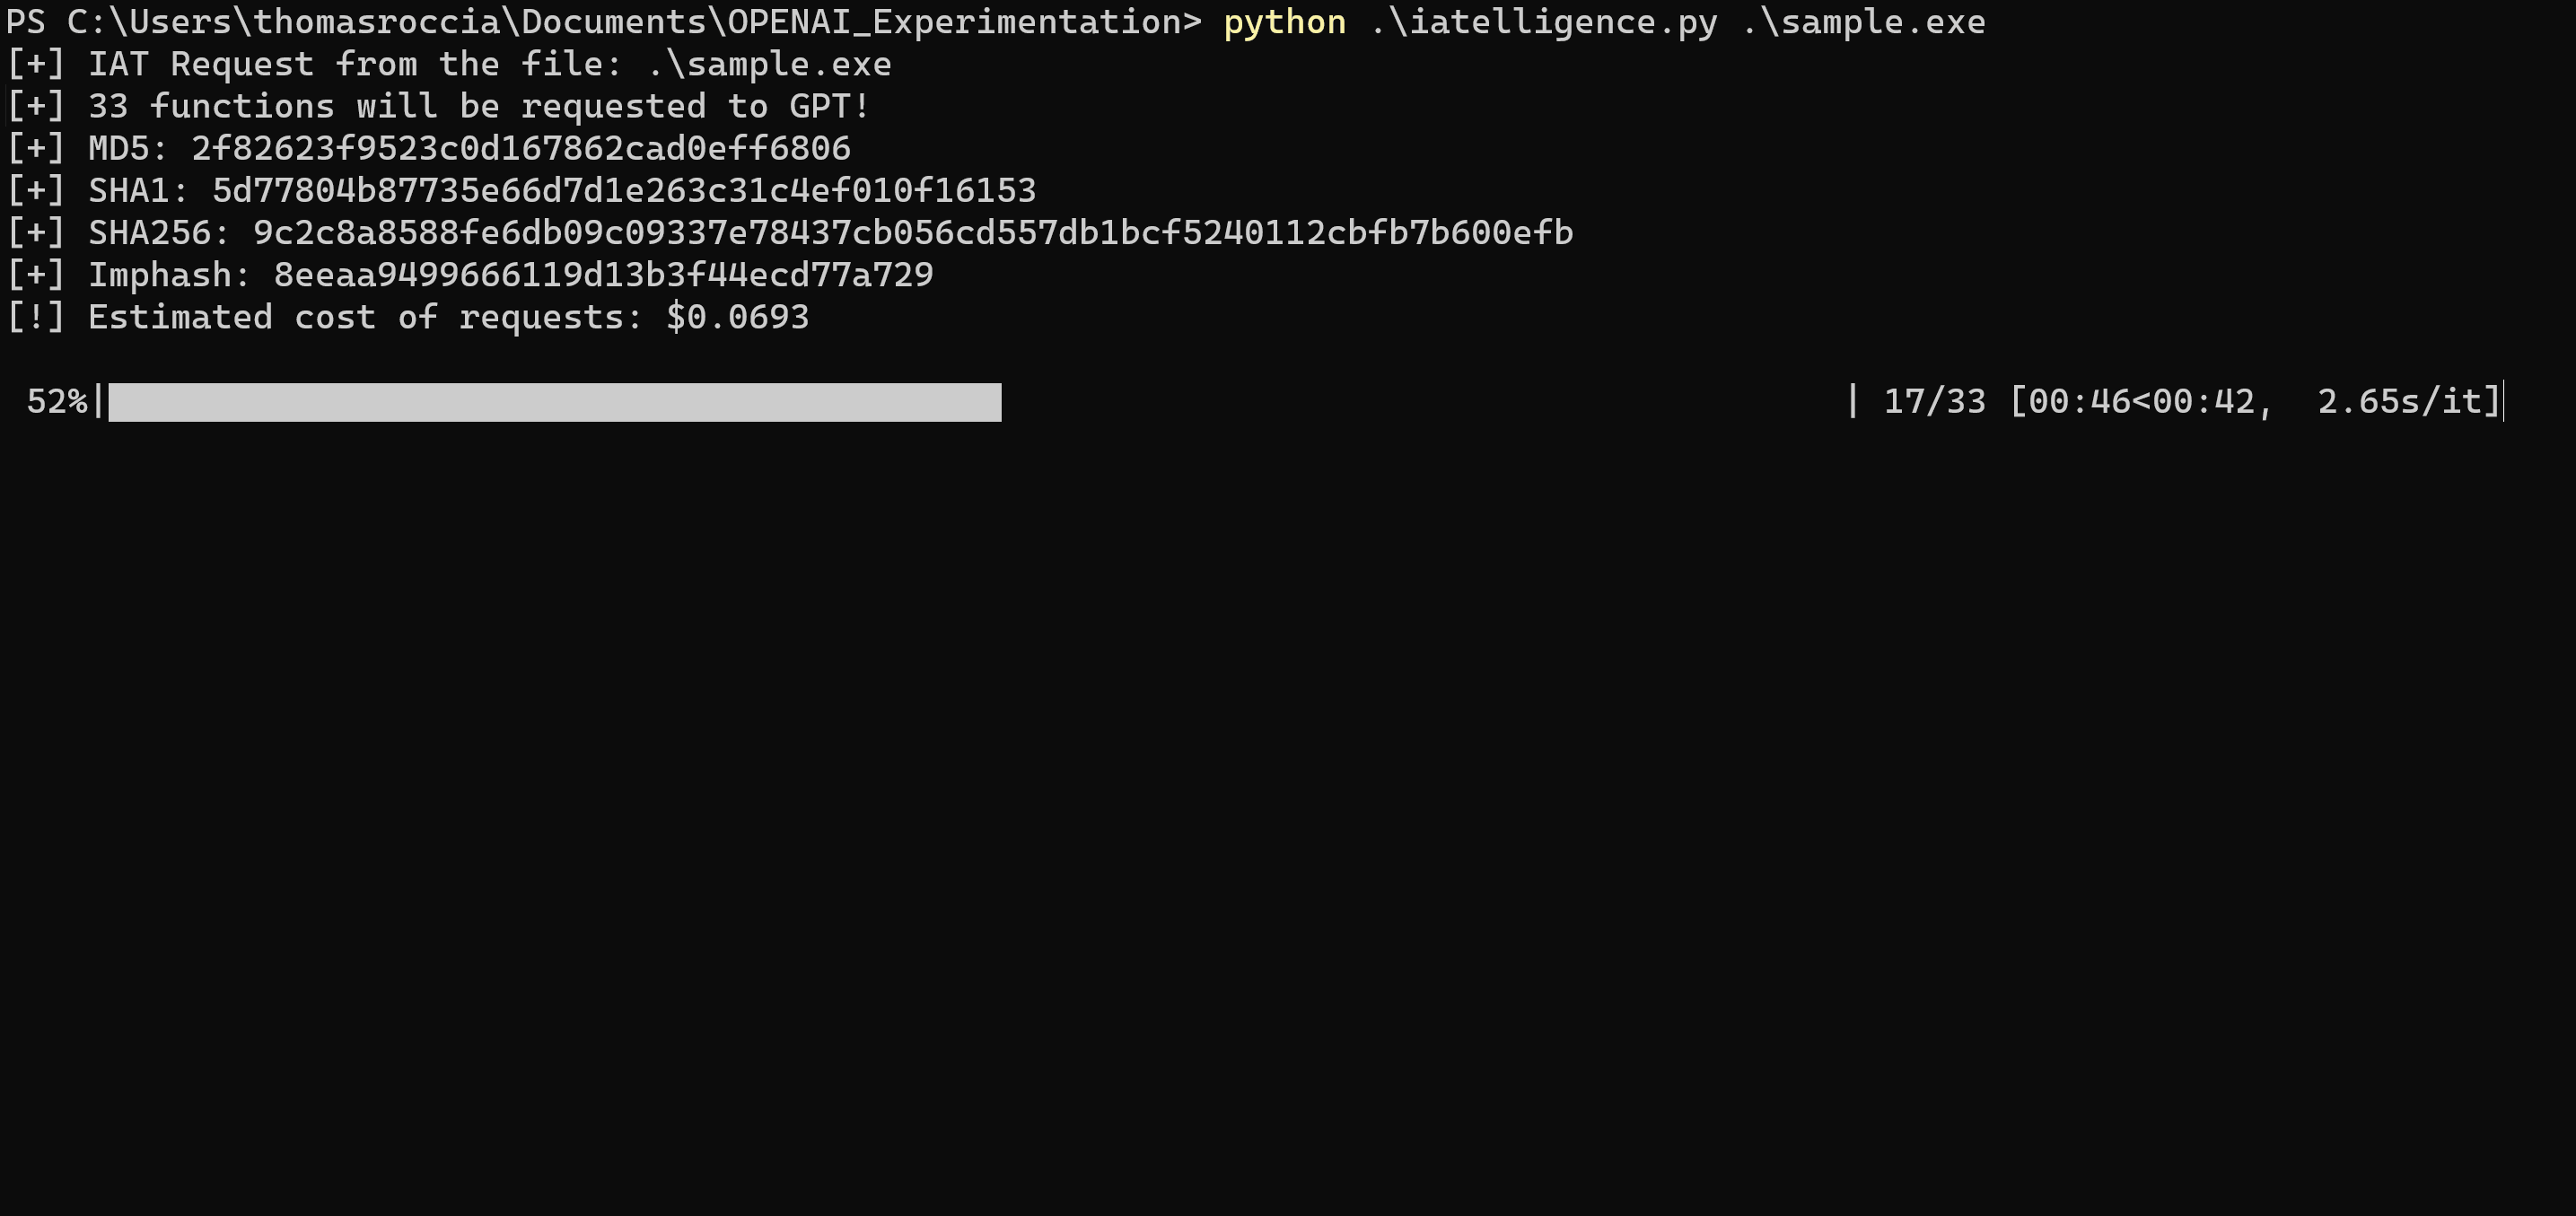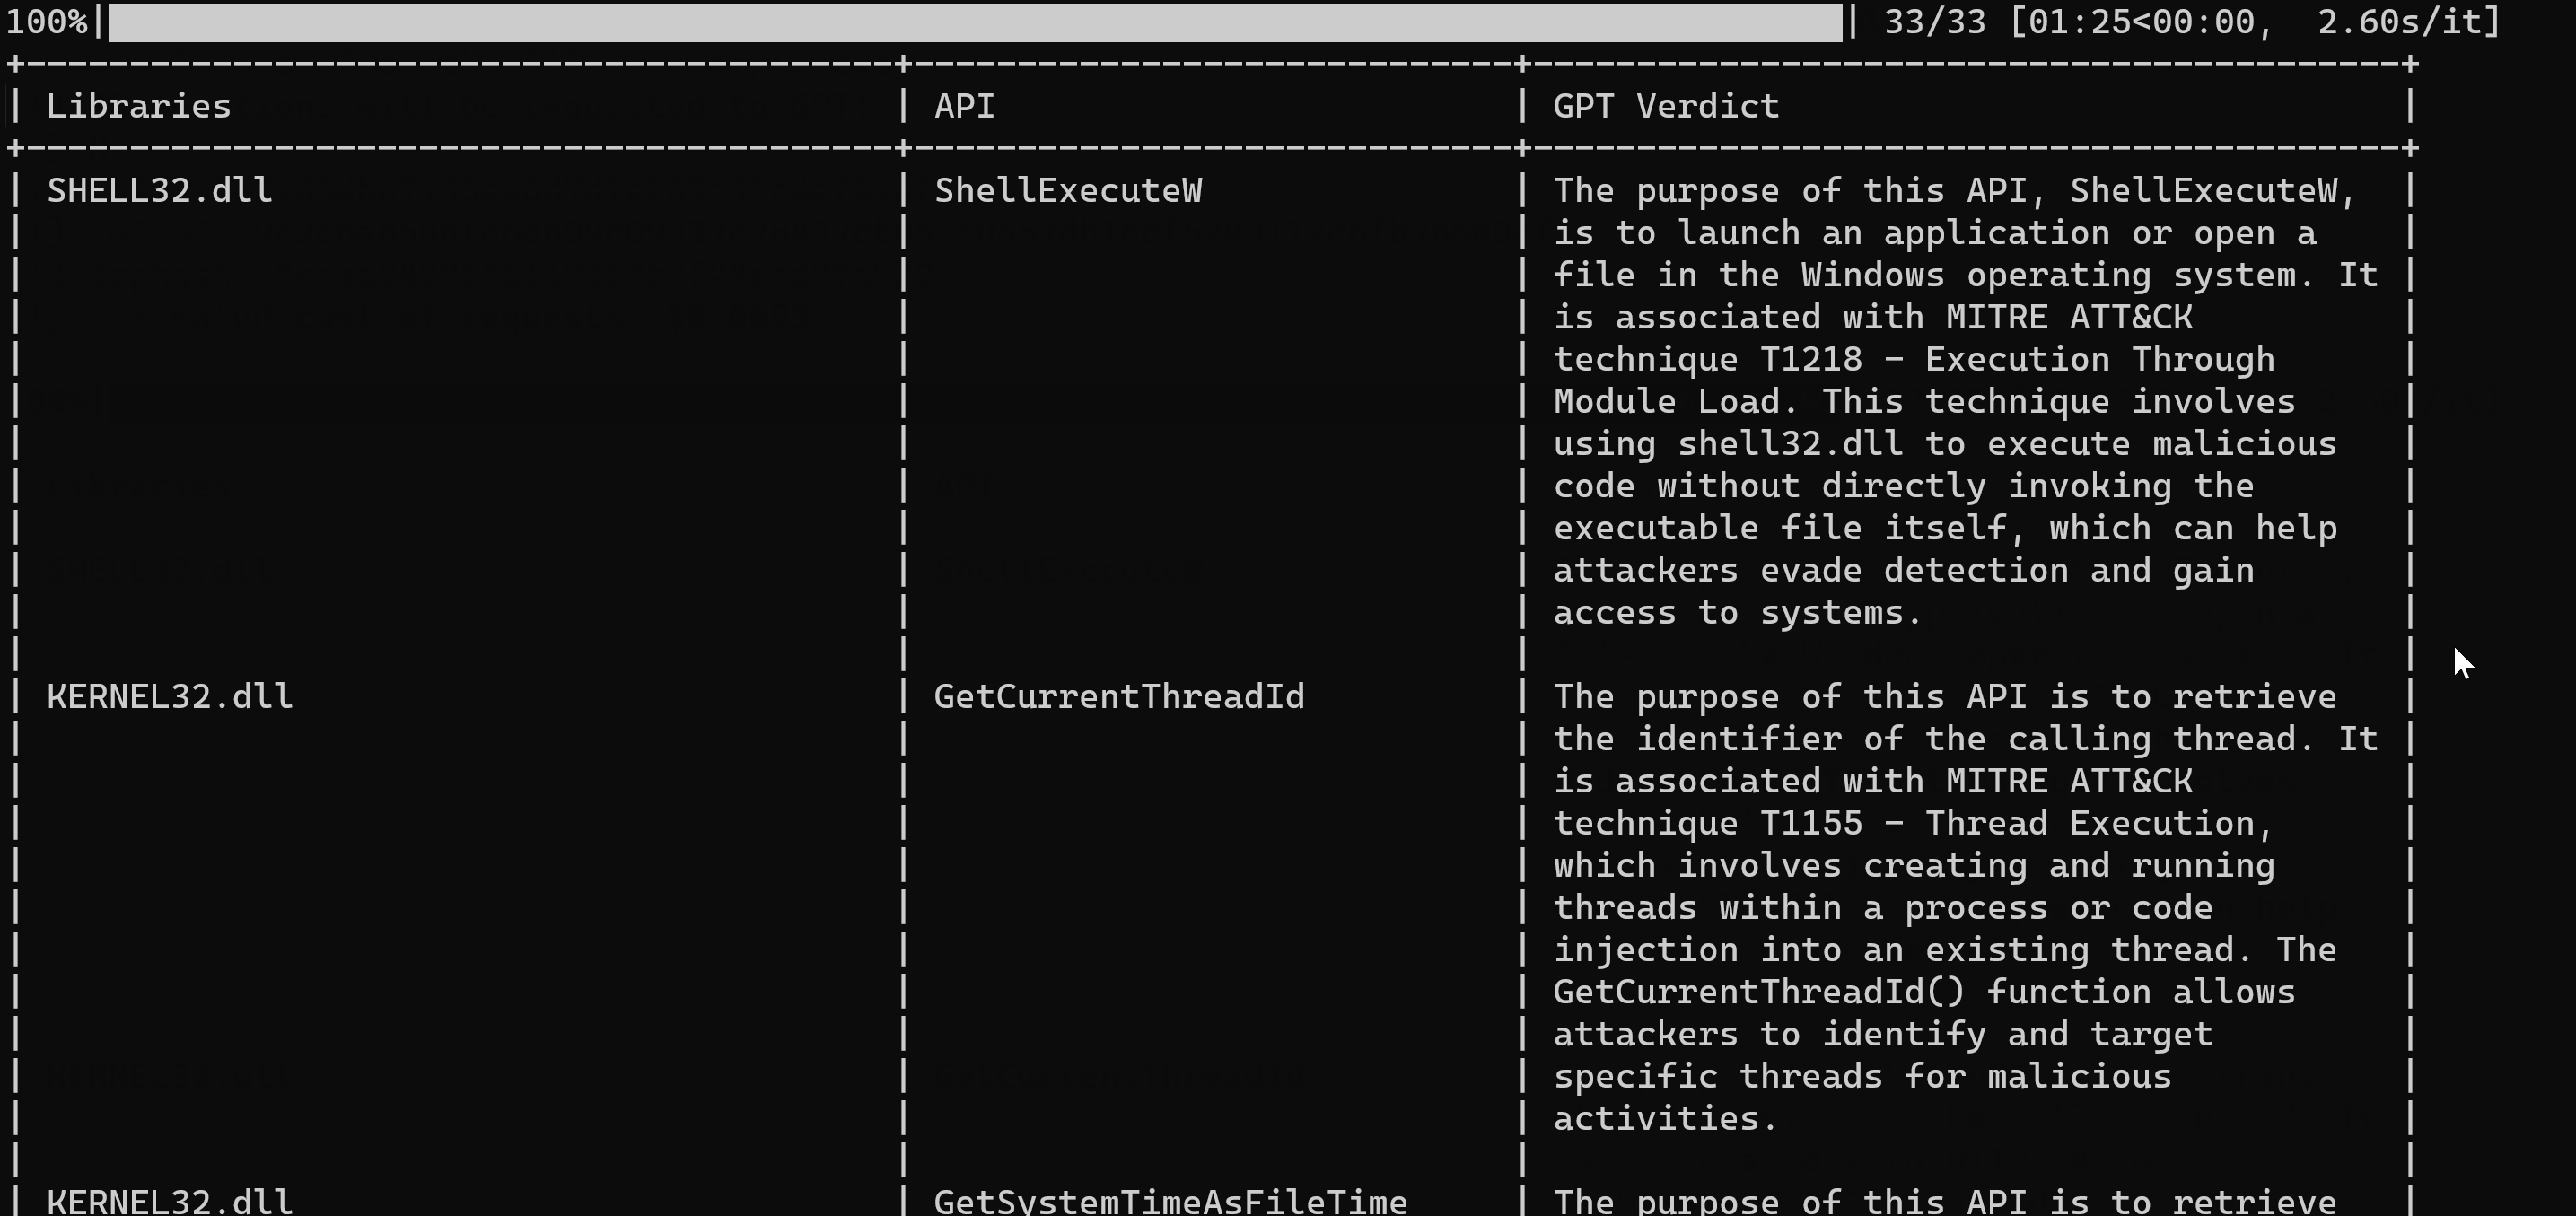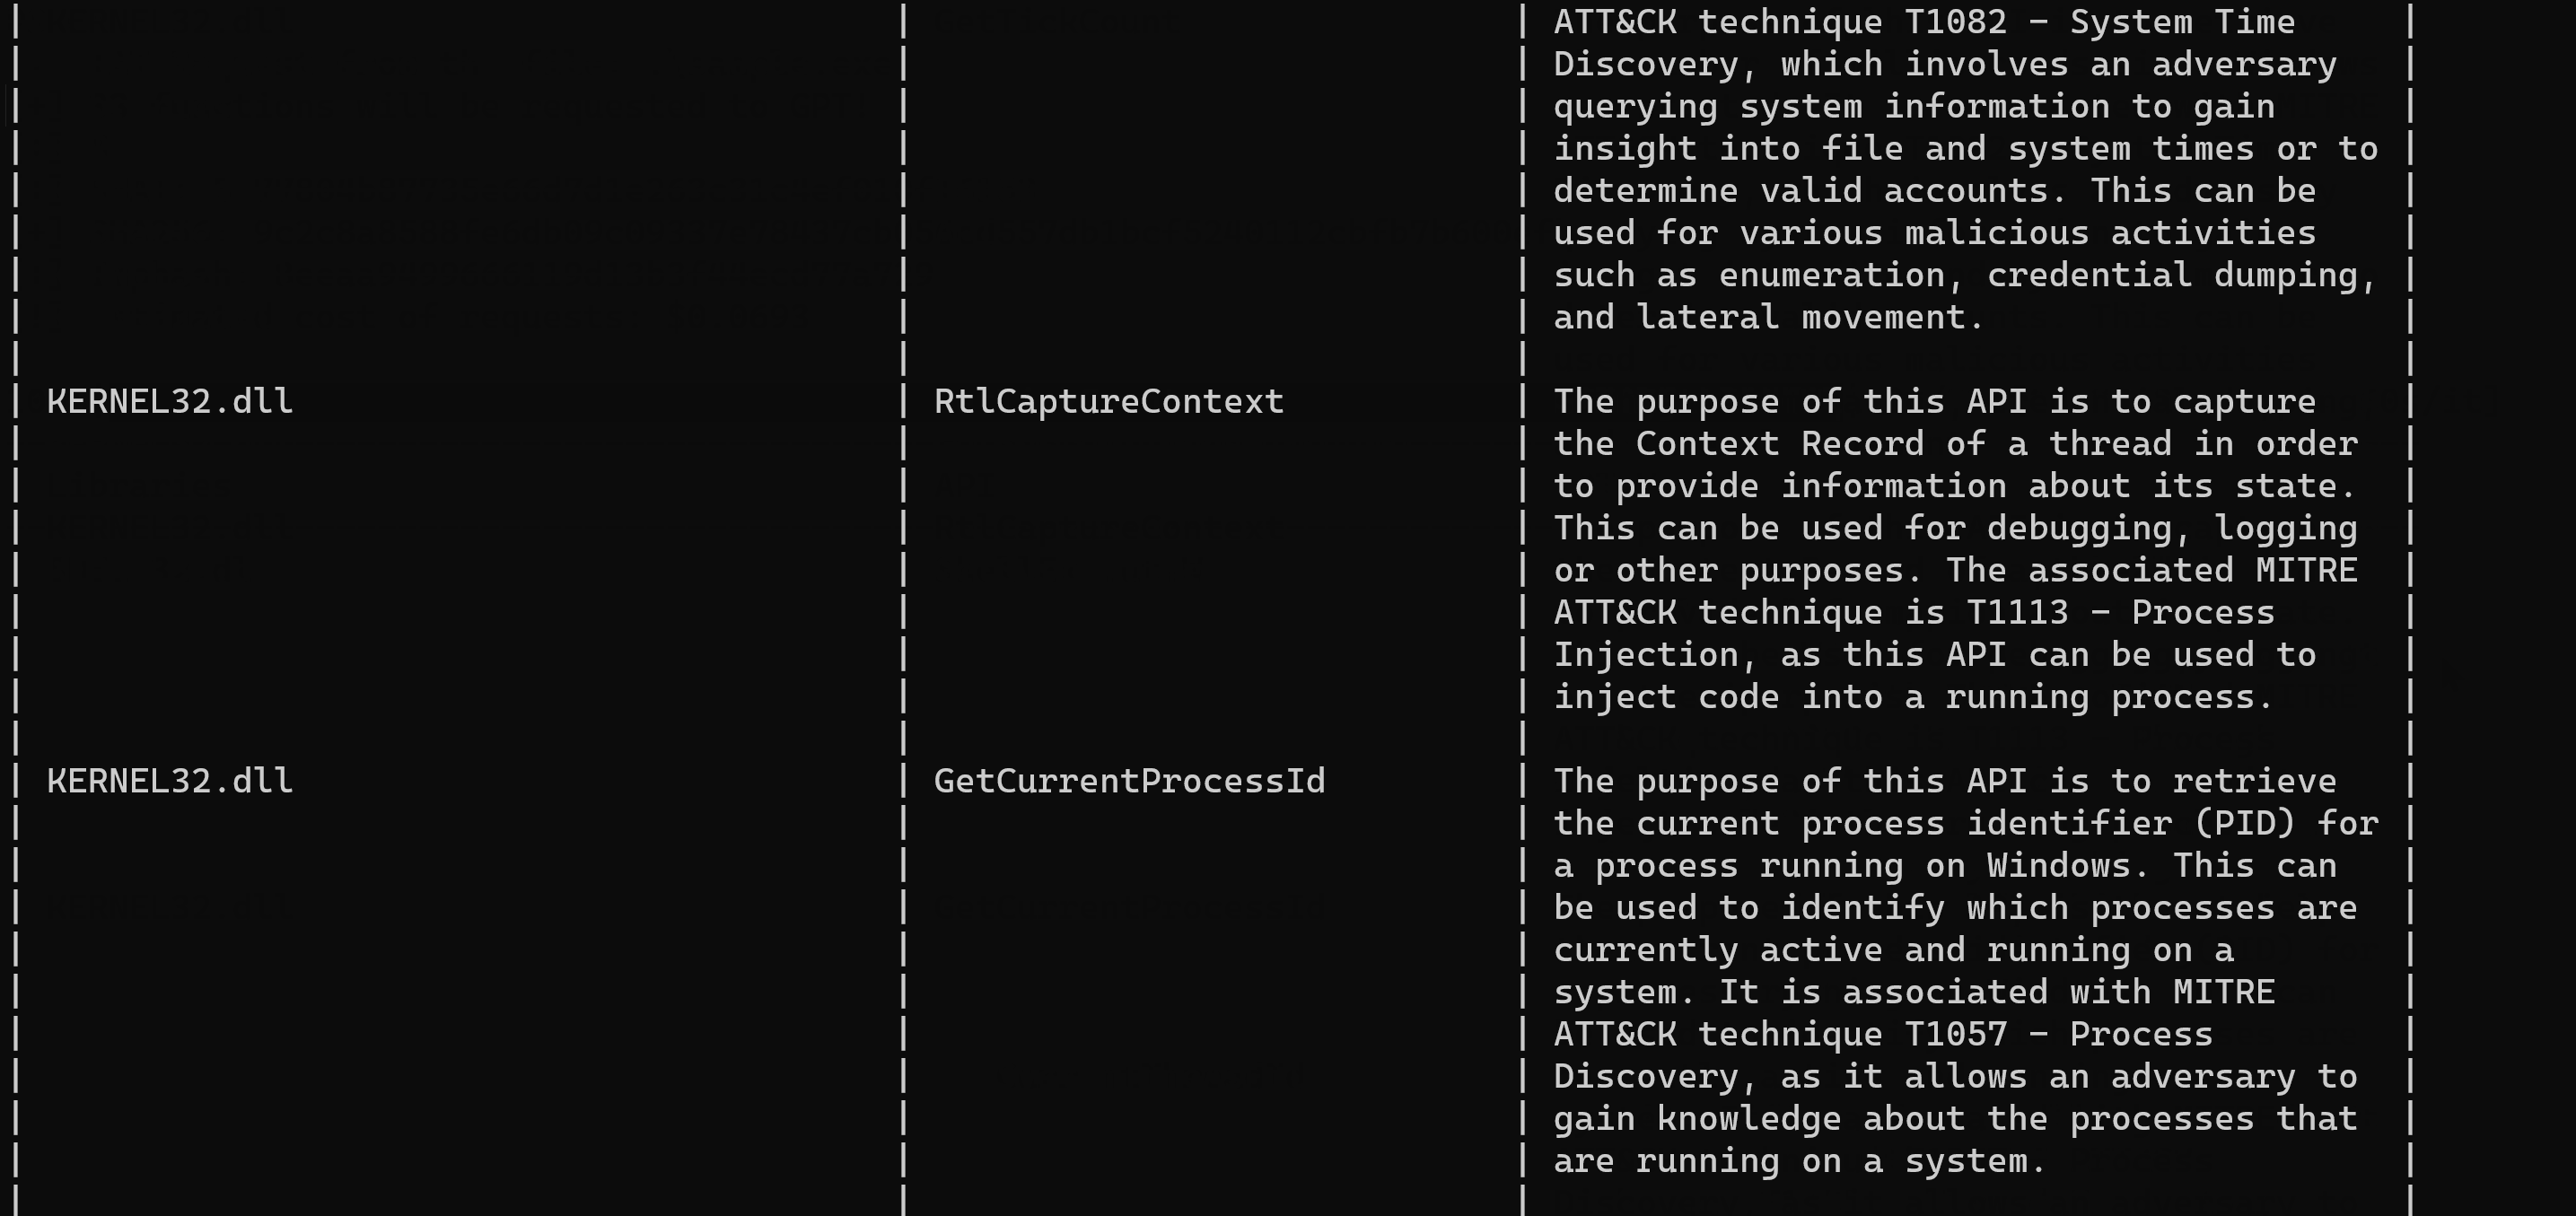
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
ai-assisted-reversingbinary-analysismalware-analysis+3
3853 years ago
Configuration_extractors preview

Configuration_extractors

GitHubpandare9x/configuration_extractors

Configuration Extractors for Malware
digital-forensicsincident-responsemalware-analysis+3
1281 year ago
mwcfg preview

mwcfg

GitHubc3rb3ru5d3d53c/mwcfg

A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
binary-analysisdefensive-toolsmalware-analysis+3
1342 years ago
ThreatResearch preview

ThreatResearch

GitHubsecurityjoes/threatresearch

Python config extractors for malware families including PlugX, Remcos, templateX, and RedLine Stealer, supporting C2 configuration extraction for…
malware-analysisreverse-engineeringthreat-intelligence
603 years ago
IcedID preview

IcedID

GitHubpr0xylife/icedid
malware-analysisreverse-engineeringthreat-intelligence
322 years ago
Icedid-file-decryptor preview

Icedid-file-decryptor

GitHubembee-research/icedid-file-decryptor

Static Decryptor for IcedID Malware

binary-analysiscryptographymalware-analysis+2
183 years ago
Asyncrat-Venom-Dcrat-Config-Extractor preview

Asyncrat-Venom-Dcrat-Config-Extractor

GitHubembee-research/asyncrat-venom-dcrat-config-extractor

Config Extractor for Asyncrat/Dcrat/VenomRat
cryptographymalware-analysisreverse-engineering+2
13 years ago
pridelocker-analysis preview

pridelocker-analysis

GitHubsynacktiv/pridelocker-analysis

This repository contains a IDA Python script to recover PrideLocker ESX encryptor strings and a YARA rule
binary-analysismalware-analysisreverse-engineering+2
13 years ago
flare-learning-hub preview

flare-learning-hub

GitHubmandiant/flare-learning-hub

Free educational content on reverse engineering and malware analysis from the FLARE team
binary-analysisdebuggerseducation+4
1.5k5 months ago
awesome-reverse-engineering-and-malware-analysis preview

awesome-reverse-engineering-and-malware-analysis

GitHubzx41r/awesome-reverse-engineering-and-malware-analysis

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
binary-analysisbinary-exploitationctf+8
9116 days ago
kernagent preview

kernagent

GitHubkarib0u/kernagent

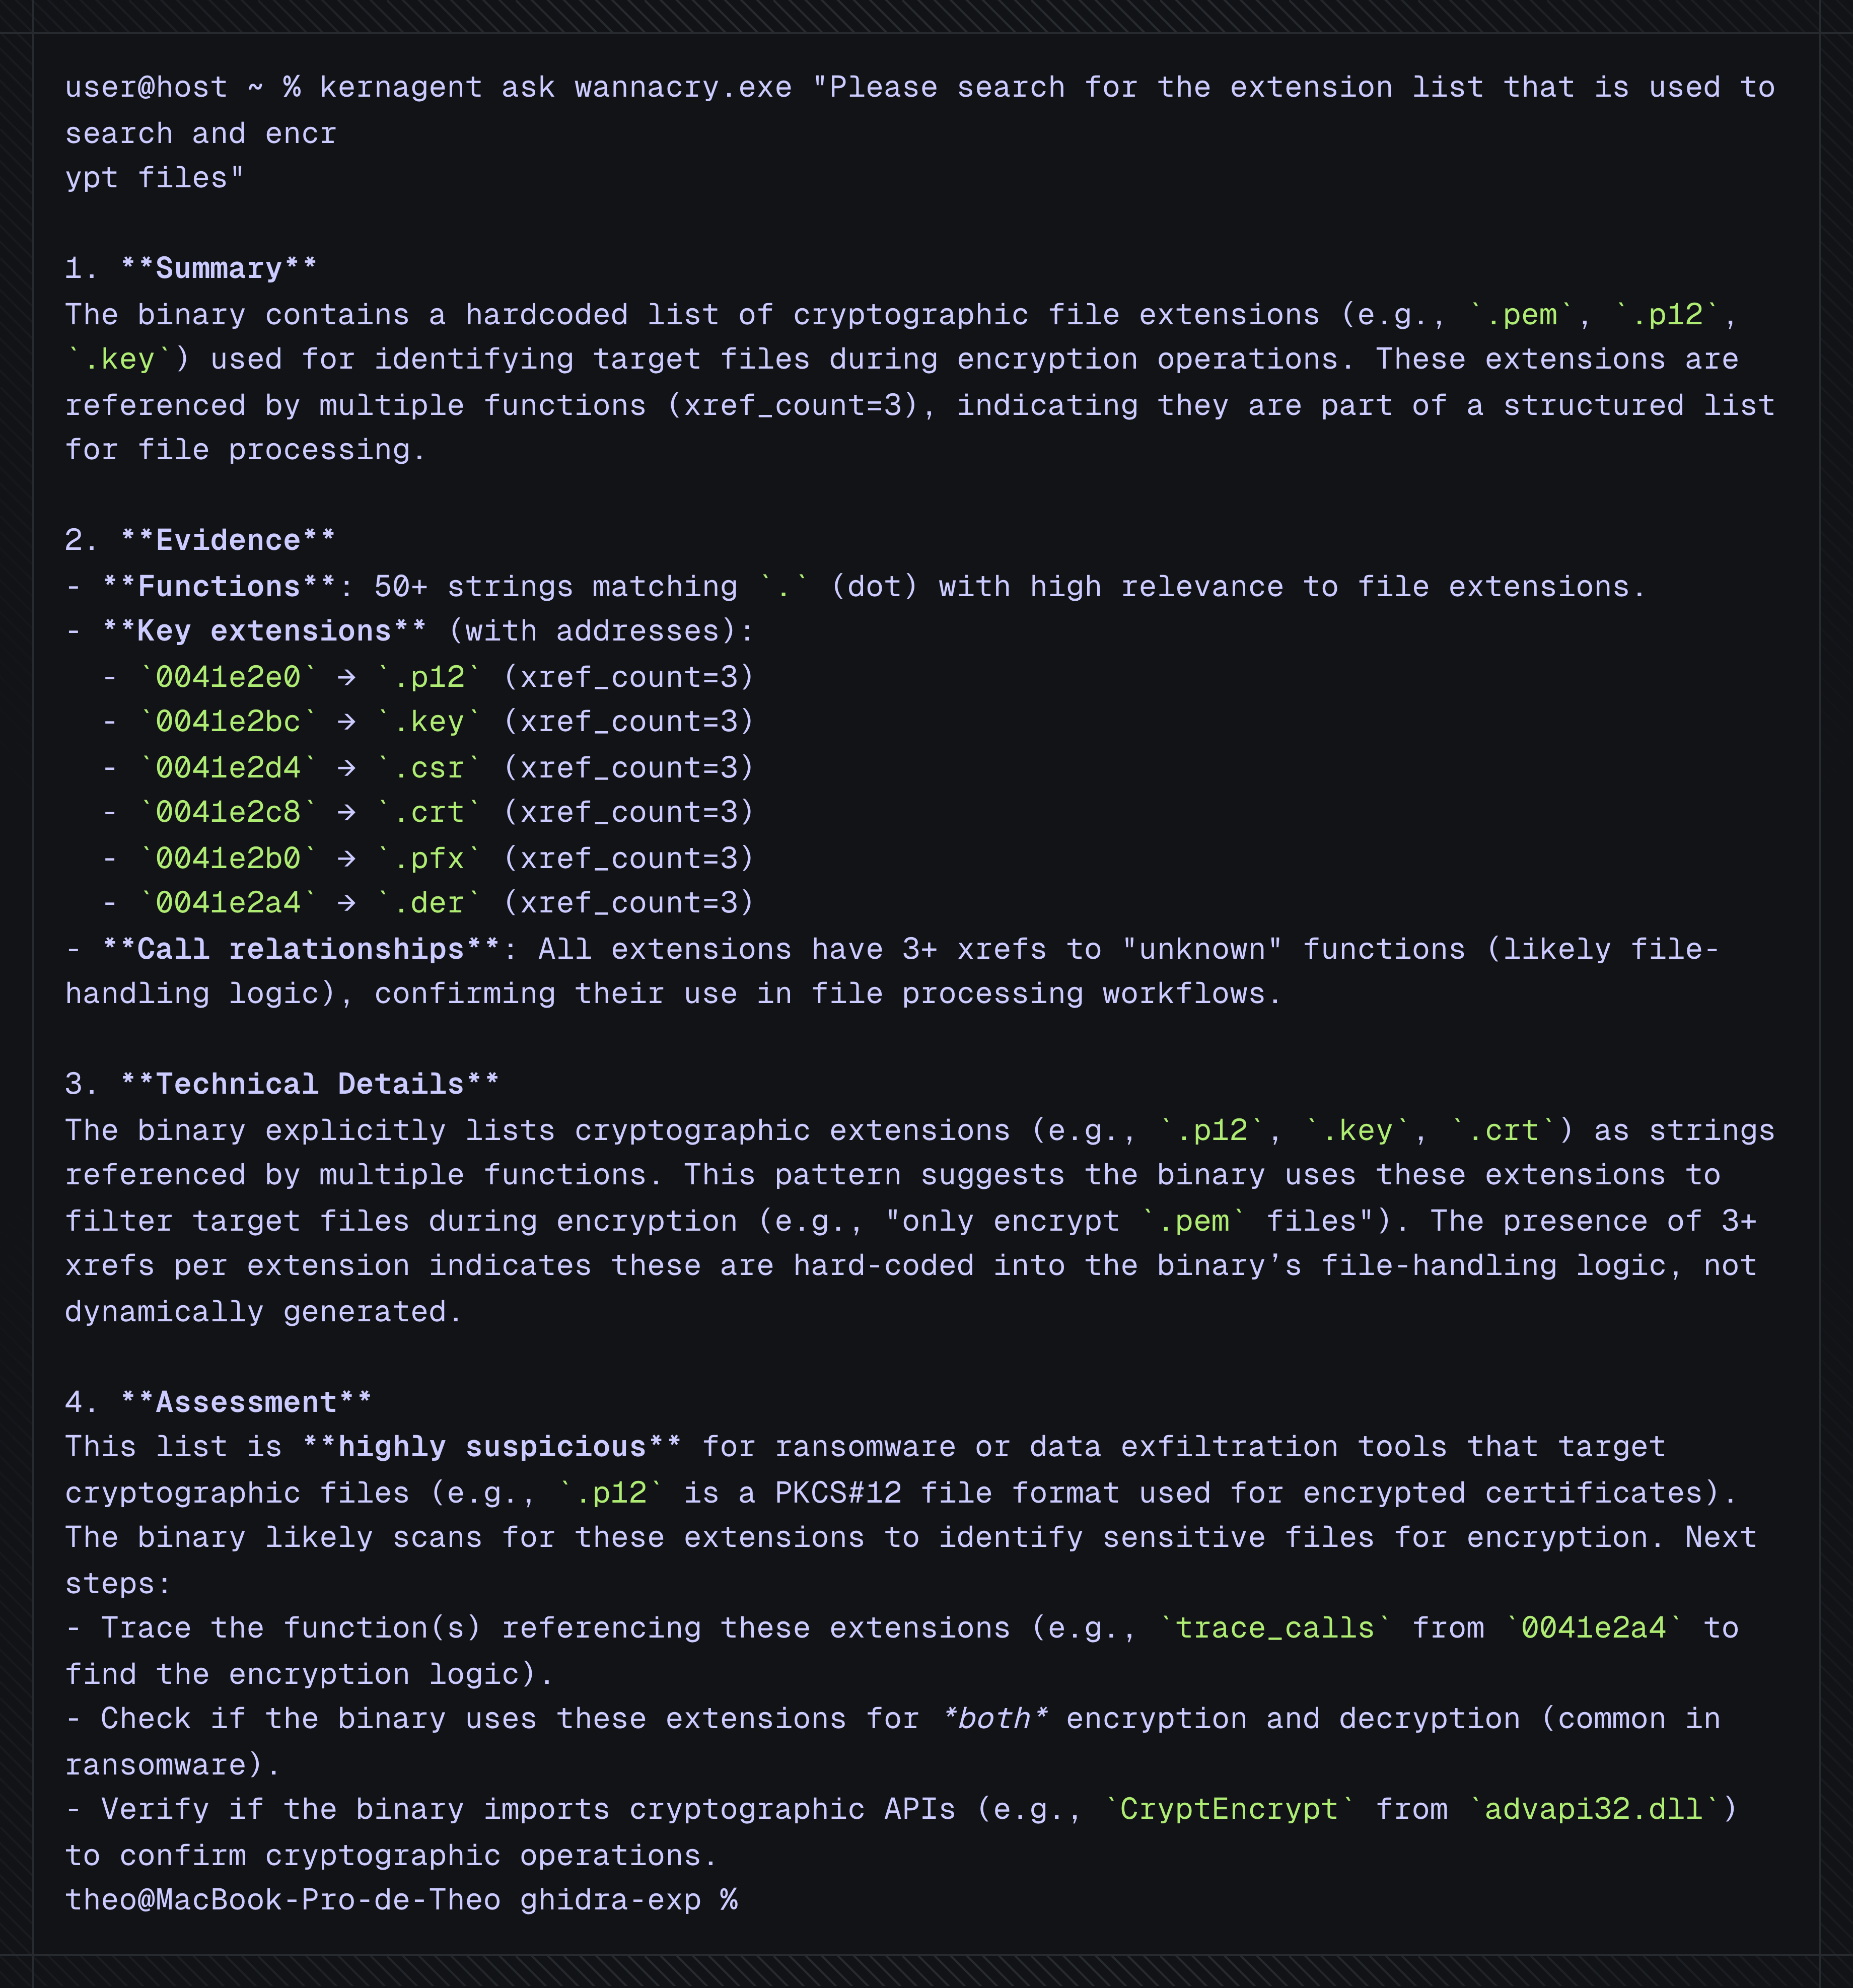
Headless AI agent for deterministic reverse engineering.
ai-assisted-reversingbinary-analysisforensics+4
10310 months ago
AIDebug preview

AIDebug

GitHubanpa1200/aidebug

Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
ai-securitybinary-analysisdebuggers+7
111 month ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
binary-analysiscommand-and-controleducation+6
51 month ago
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

binary-analysiscommand-and-controldata-exfiltration+6
526 days ago
Vidar-Stealer-Reverse-Engineering preview

Vidar-Stealer-Reverse-Engineering

GitHubkaandemir993/vidar-stealer-reverse-engineering

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…

binary-analysiseducationforensics+7
22 months ago
Malware-Bible preview

Malware-Bible

GitHubperkins-fund/malware-bible

Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills,…

digital-forensicseducationincident-response+4
60623 days ago
Previous1234567Next