
SDK
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
api-security-testinginformation-gatheringosint+2
555
intelligencex/sdkSDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
 thecyberfairy/cve-lfi-lab
A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…
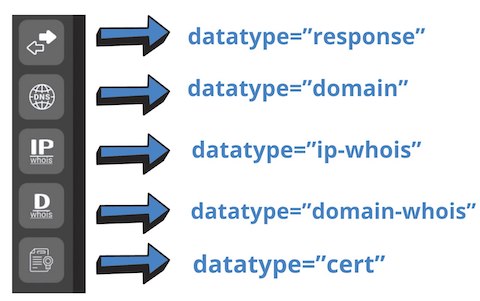 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
 st2labs/sipi
Simple IP Information Tools for Reputation Data Analysis
 digitalshadows/cve-2019-19781_iocs
Curated indicators of compromise (IOCs) for CVE-2019-19781, including IP addresses and whois data from honeypot logs to aid threat detection and…
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
 jonrau1/syntheticsun
Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
 hahasagined/cve-2024-3400
External Dynamic List (EDL) of IP addresses actively exploiting CVE-2024-3400, for use in firewall and SIEM blocklists to defend against ongoing…
 00gxd14g/misp-extractor
Extracts selected MISP attributes, including IP addresses, URLs, and hashes, into reusable output files.
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
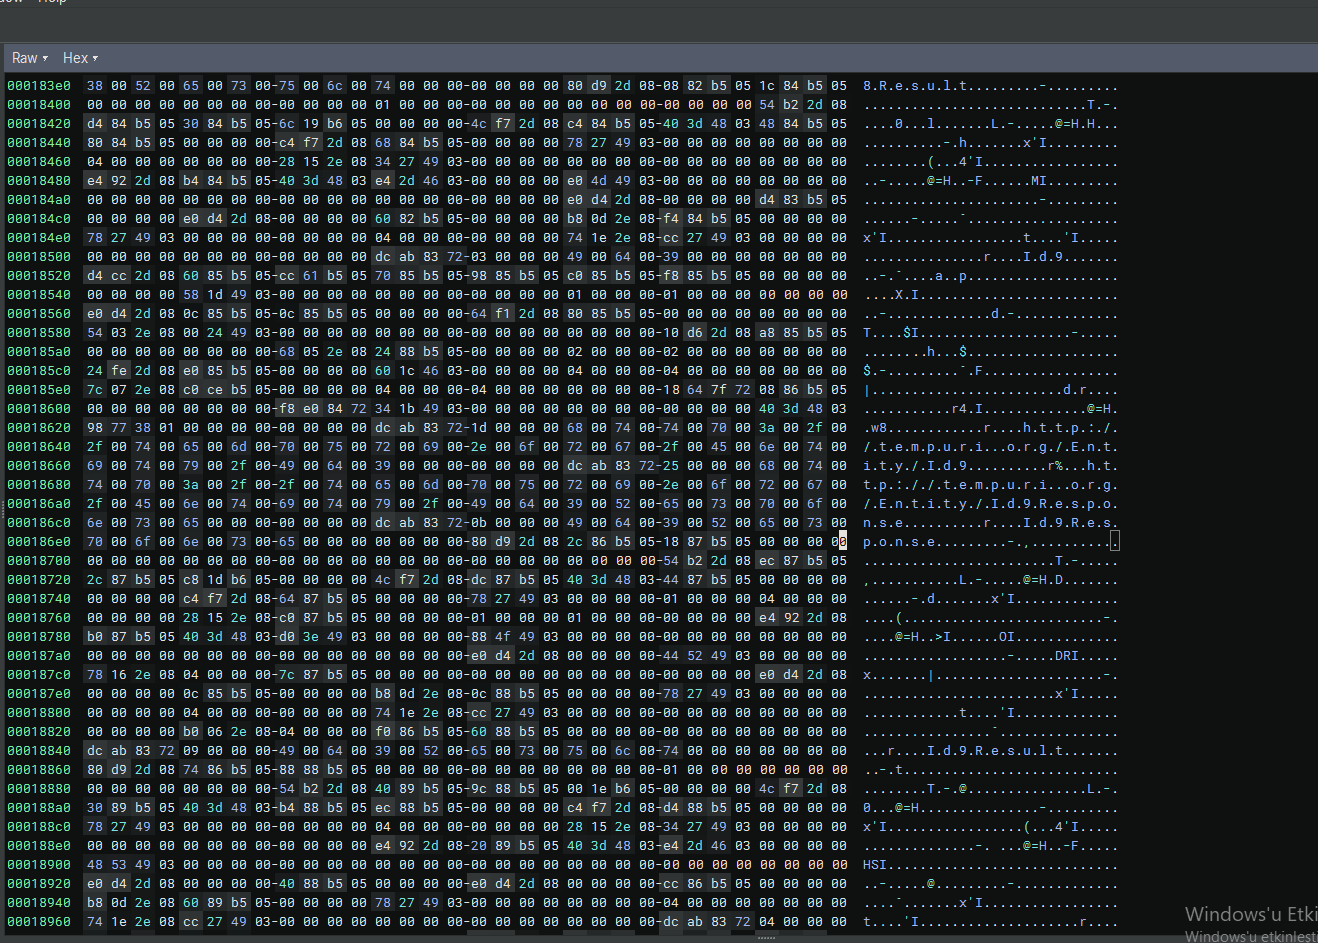 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
 kolya5544/bearftp
Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.
 brets0150/stickyexim
Exim Honey Pot for CVE-2019-10149 exploit attempts.
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
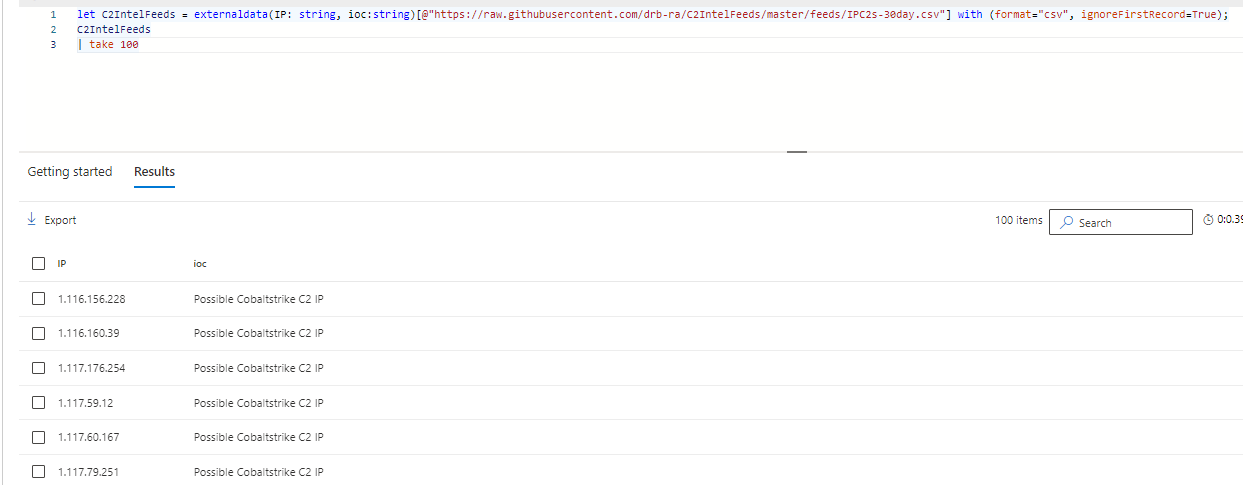 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 bhavsec/reconspider
🔎 Most Advanced Open Source Intelligence (OSINT) Framework for scanning IP Address, Emails, Websites, Organizations.
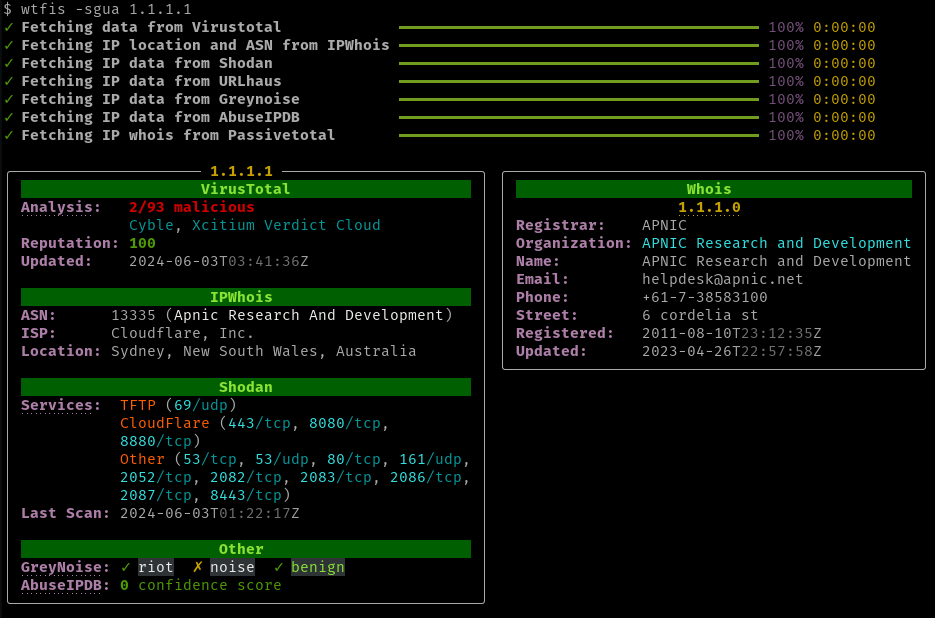 pirxthepilot/wtfis
Passive hostname, domain and IP lookup tool for non-robots