

mvt
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
13.4k
mvt-project/mvtForensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
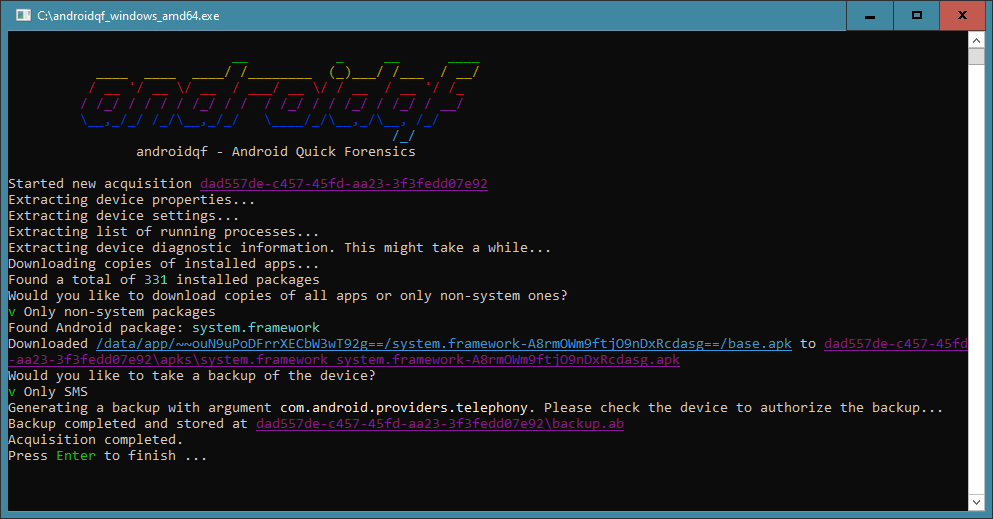 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
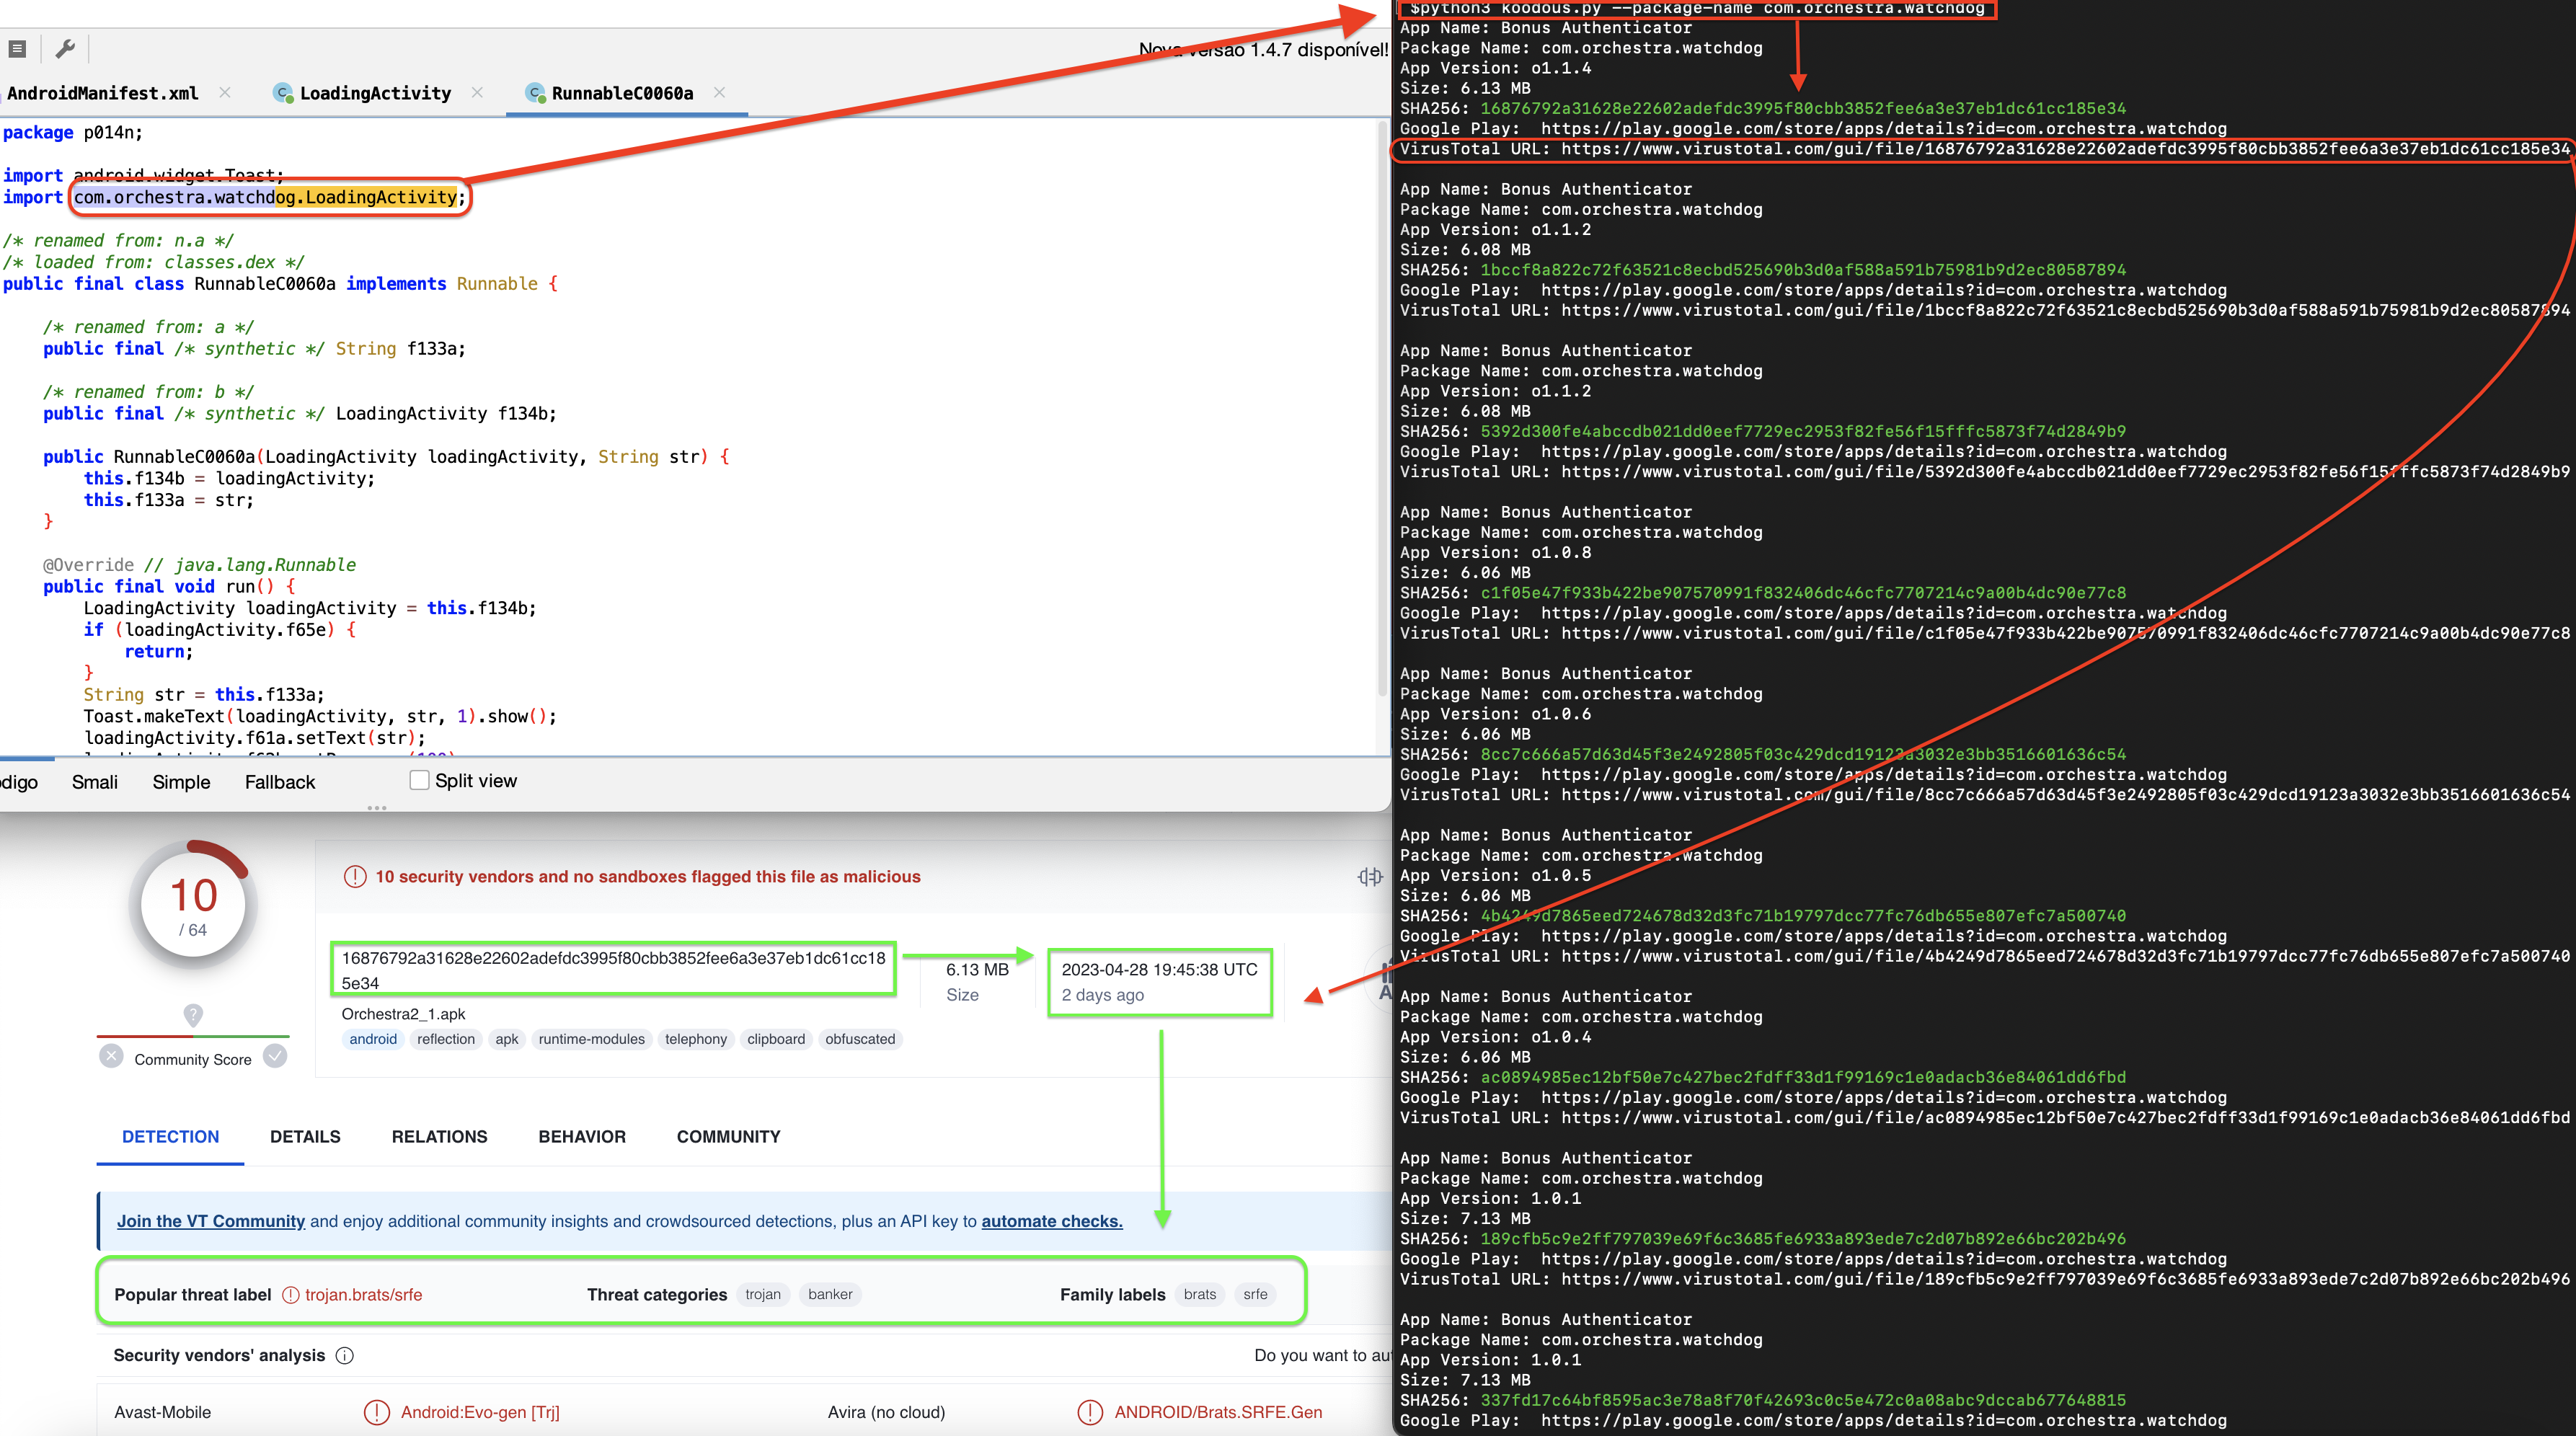 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 horizon-software-development/cve-2024-3094
Advisory and analysis repository for CVE-2024-3094, detailing a critical backdoor in Linux SSH library with mitigation steps for servers and Android…
 cyberhatcoil/acf
Android Connections Forensics
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 danielcuthbert/trackers
A collection of online trackers, advertising networks, telemetry collectors and general 'we like to watch' lists for you to use to get better control…
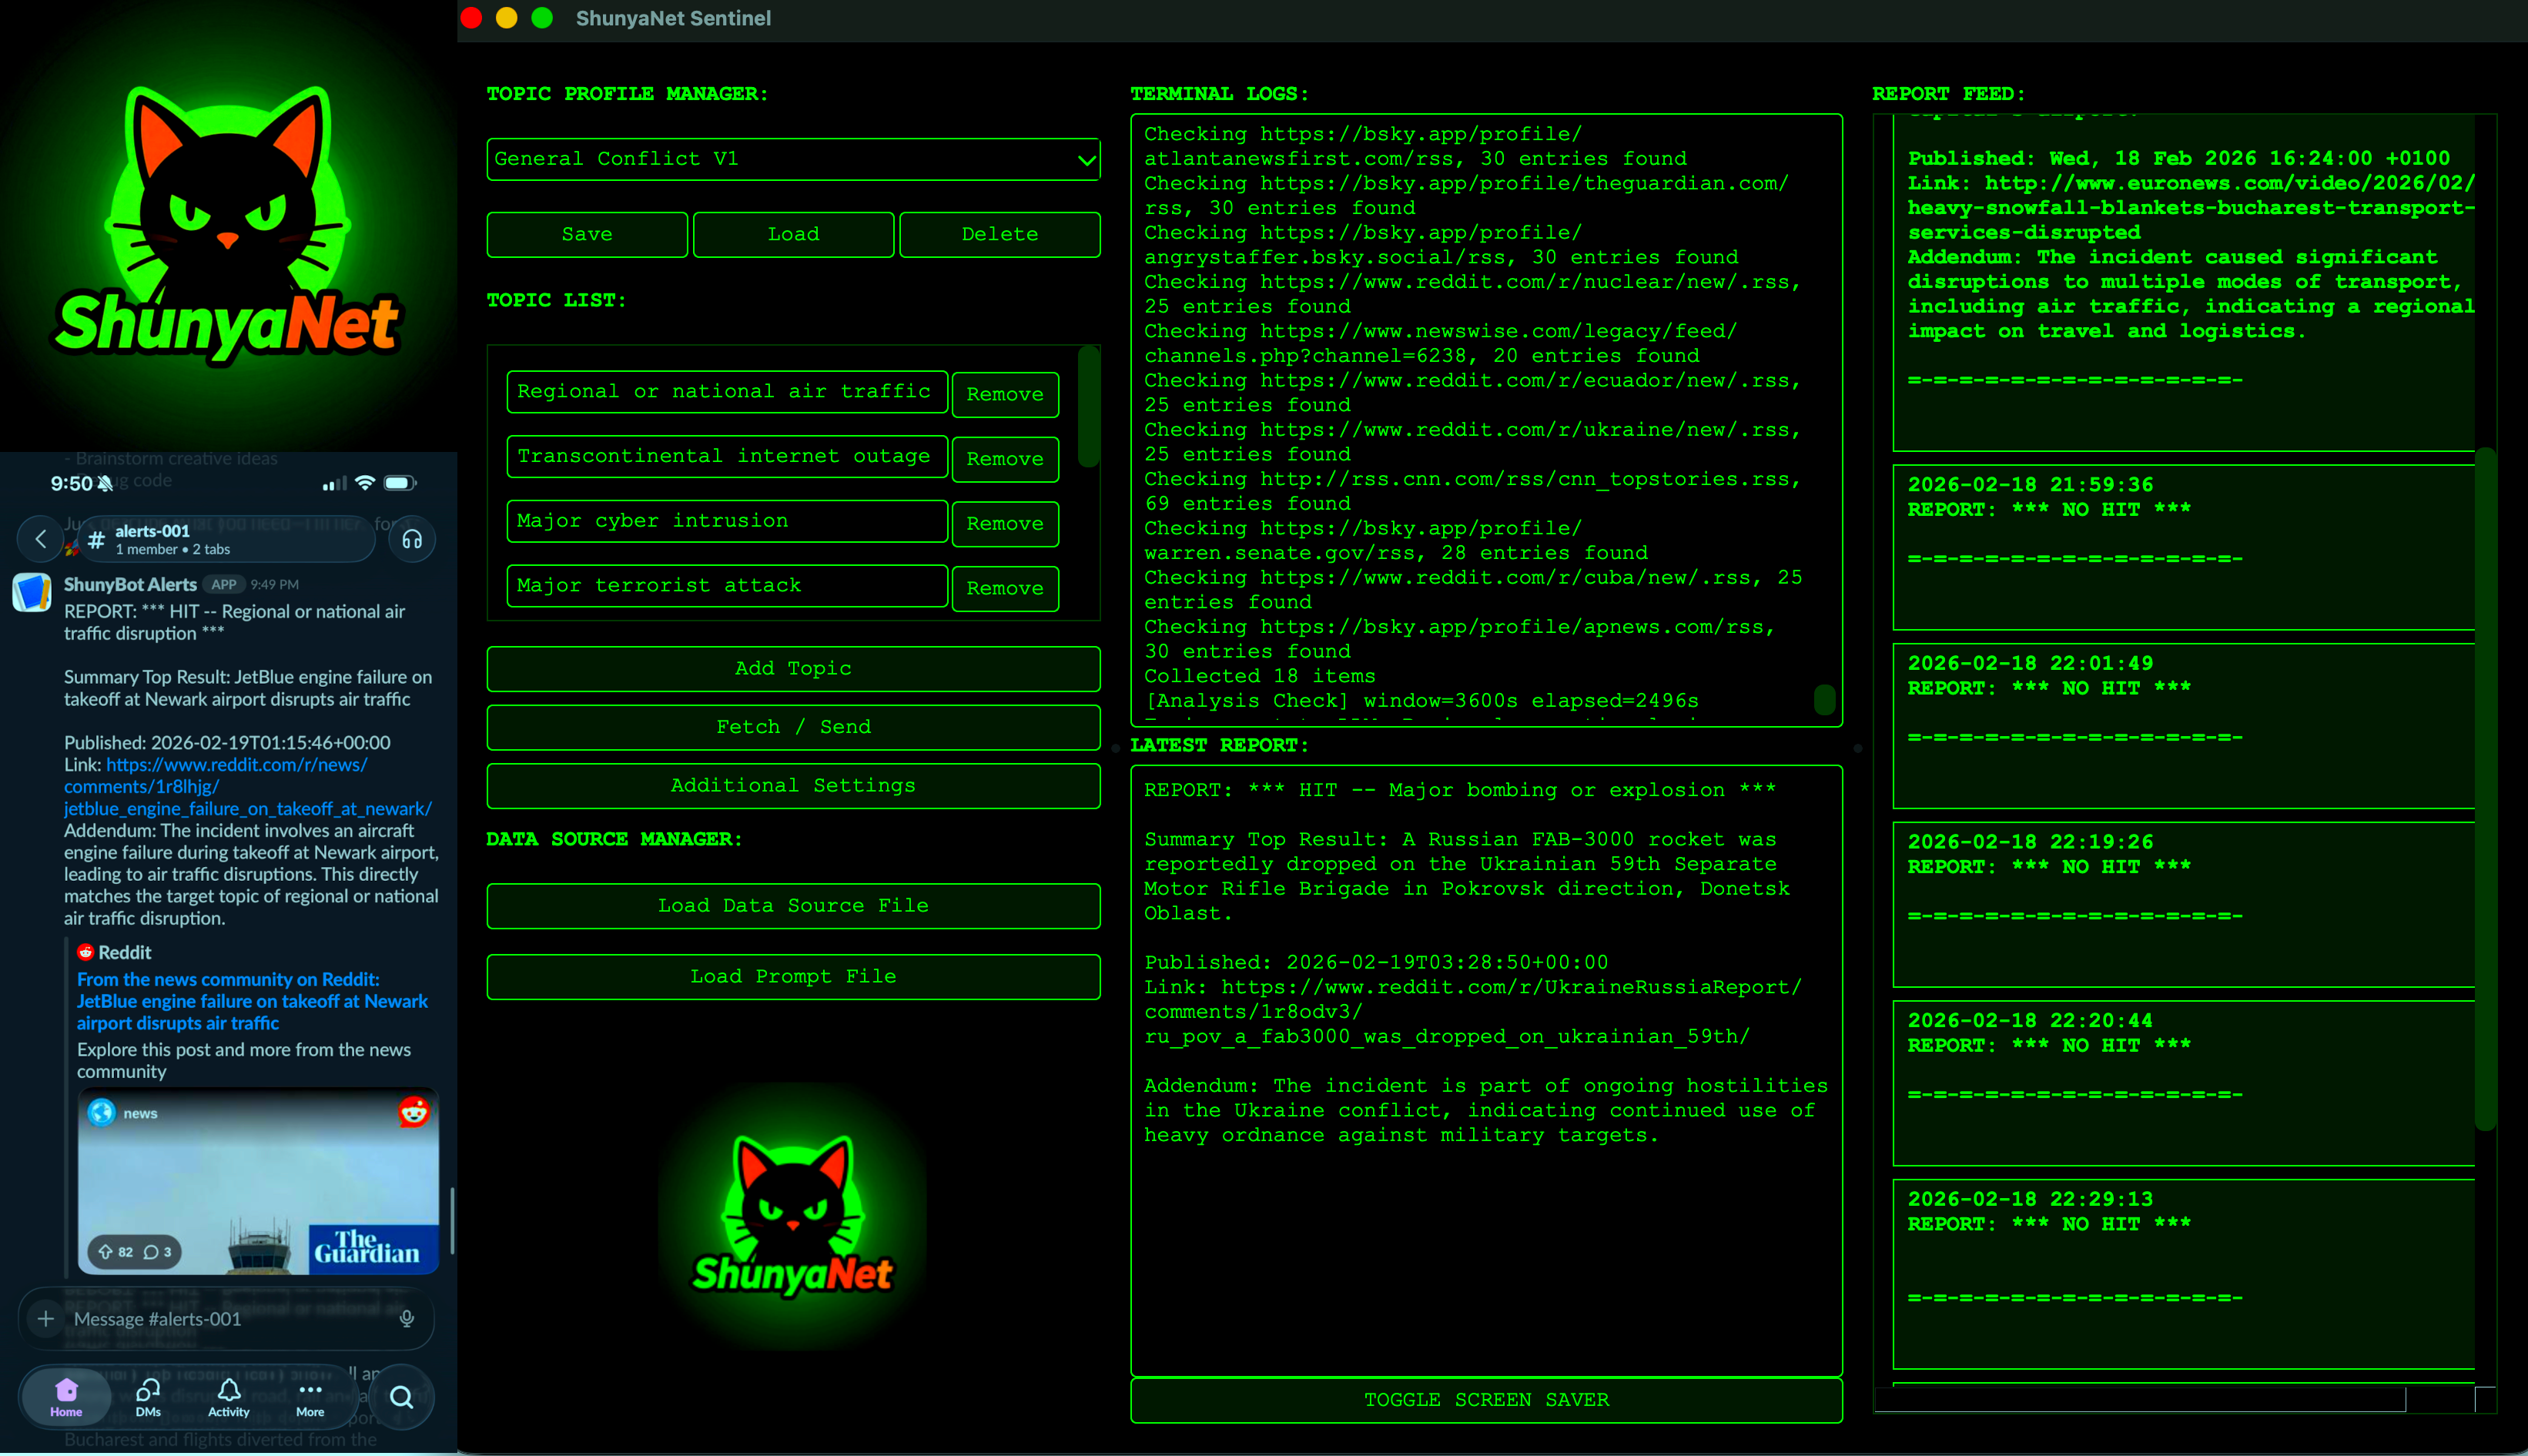 everythingscomputer/shunyanet-sentinel
ShunyaNet Sentinel is a lightweight program that monitors RSS feeds, sends them to an LLM for analysis, and delivers summaries or alerts directly to…
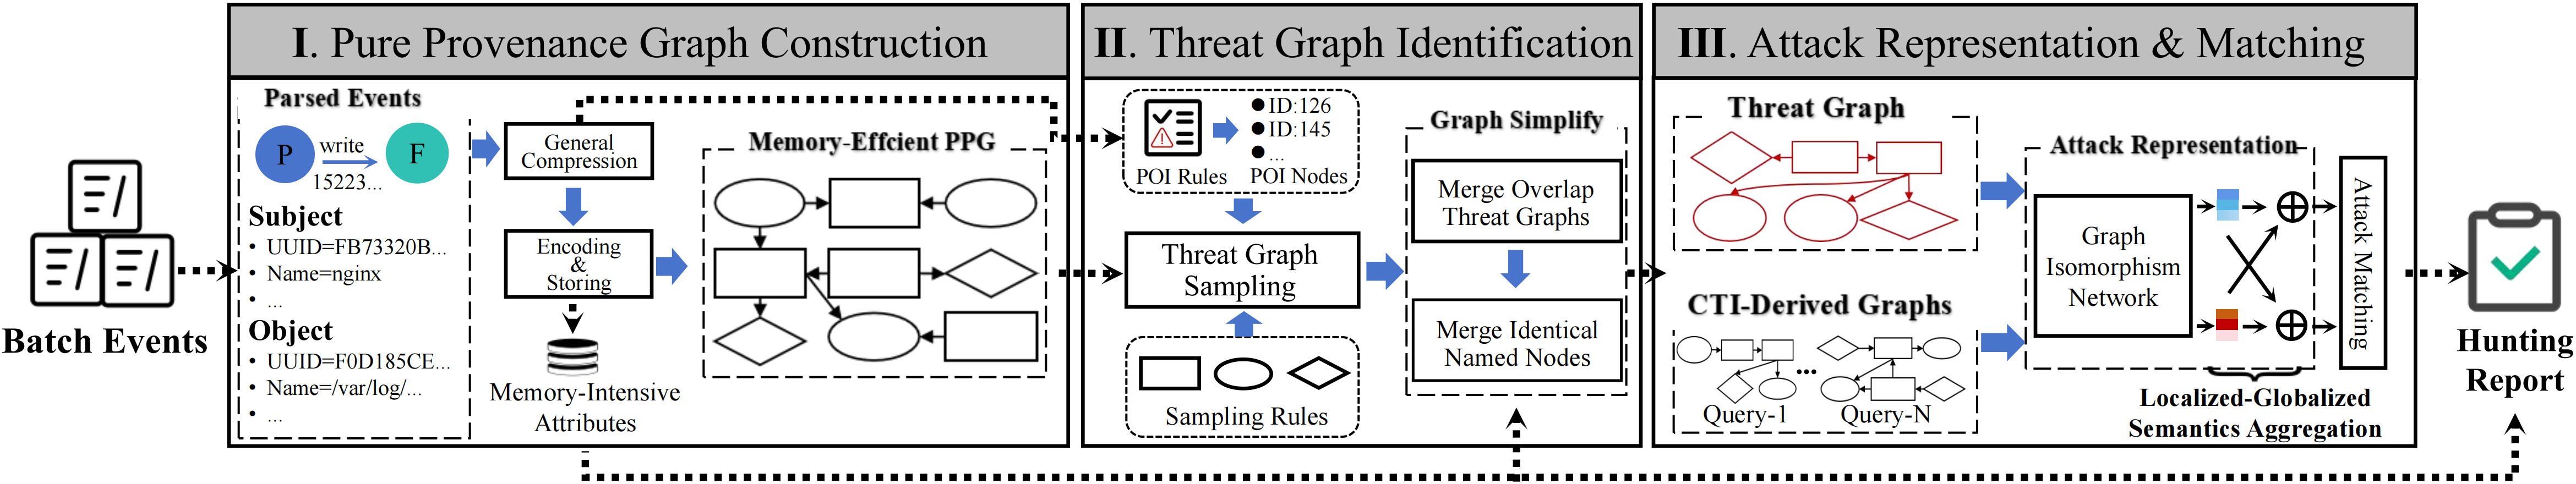 xueboqiu/prohunter
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
 roxanne_ardary/safeforge
SafeForge is an open-source mobile app hub built on GitLab that enables developers to build, upload, and share applications in a secure, AI-verified…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
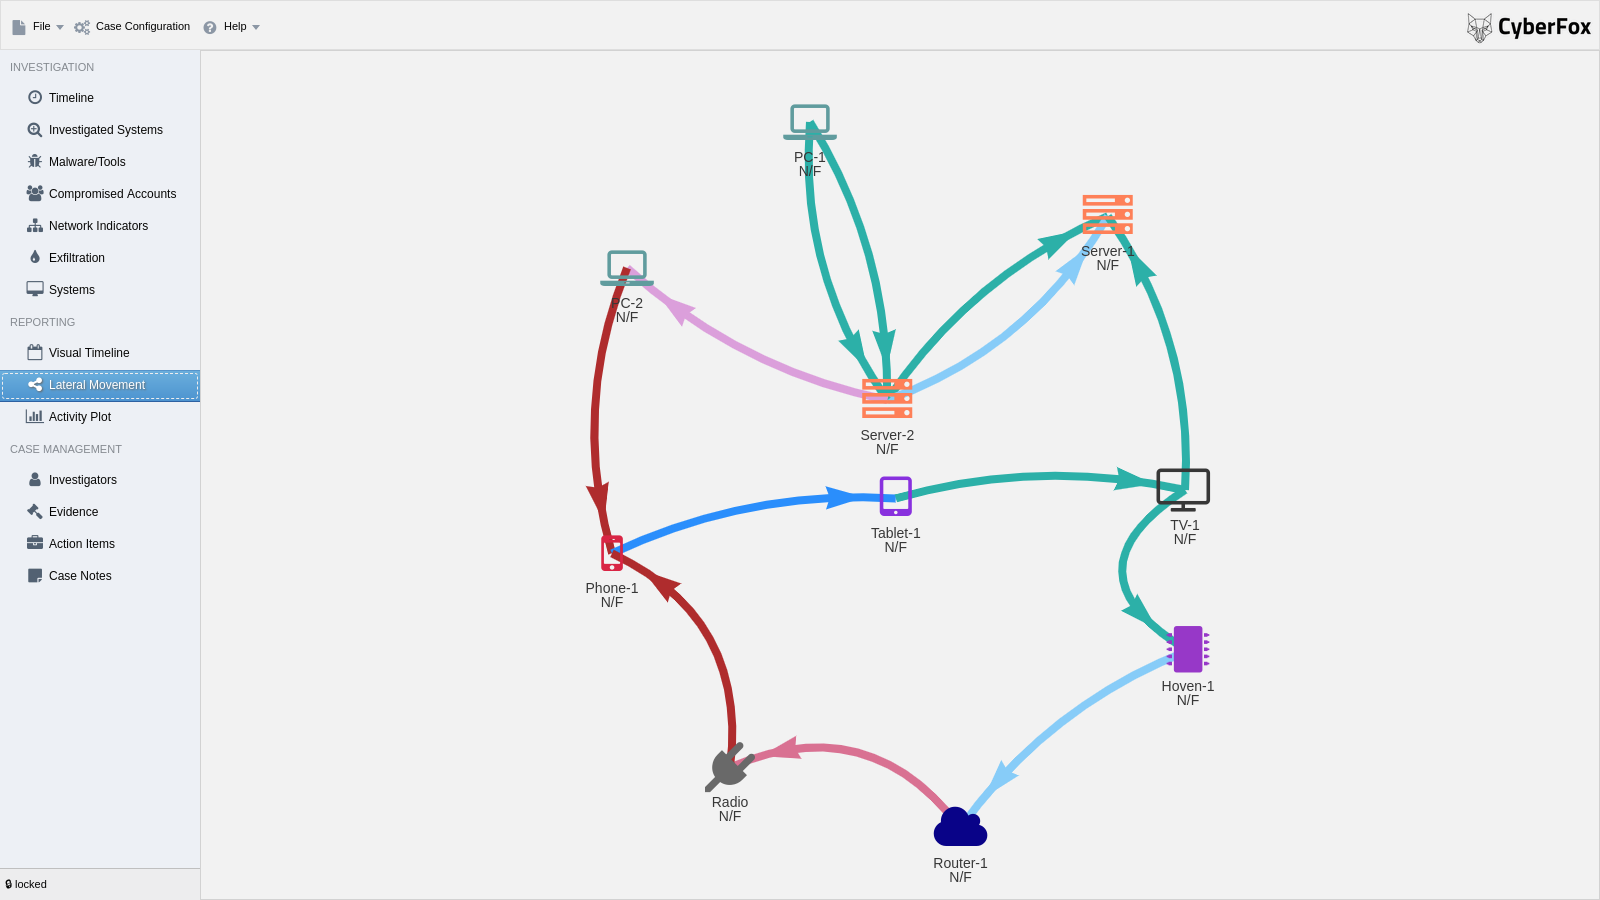 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders