

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
102 results
FIASSE preview

FIASSE

GitHubowasp/fiasse

A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
code-analysiscurated-resourcesdevsecops+7
143 days ago
RemotePSpy preview

RemotePSpy

GitHubwithsecurelabs/remotepspy

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
defensive-toolsdigital-forensicsincident-response+3
196 years ago
ProHunter preview

ProHunter

GitHubxueboqiu/prohunter

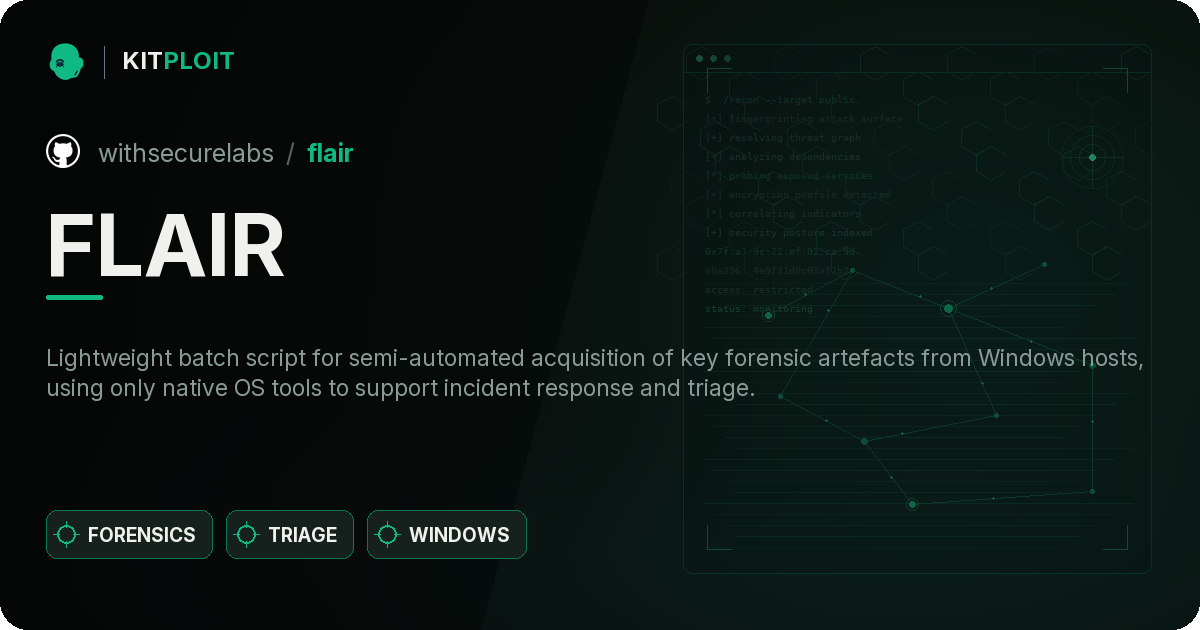
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
anomaly-detectioninformation-gatheringmachine-learning+3
1210 months ago
FLAIR preview

FLAIR

GitHubwithsecurelabs/flair

Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
digital-forensicsforensicsincident-response+2
165 years ago
icannTLD preview

icannTLD

GitHubcorelight/icanntld

Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
dns-analysisinformation-gatheringintrusion-detection+3
81 year ago
AI-driven-MITRE-Attack preview

AI-driven-MITRE-Attack

GitHubmouna23/ai-driven-mitre-attack

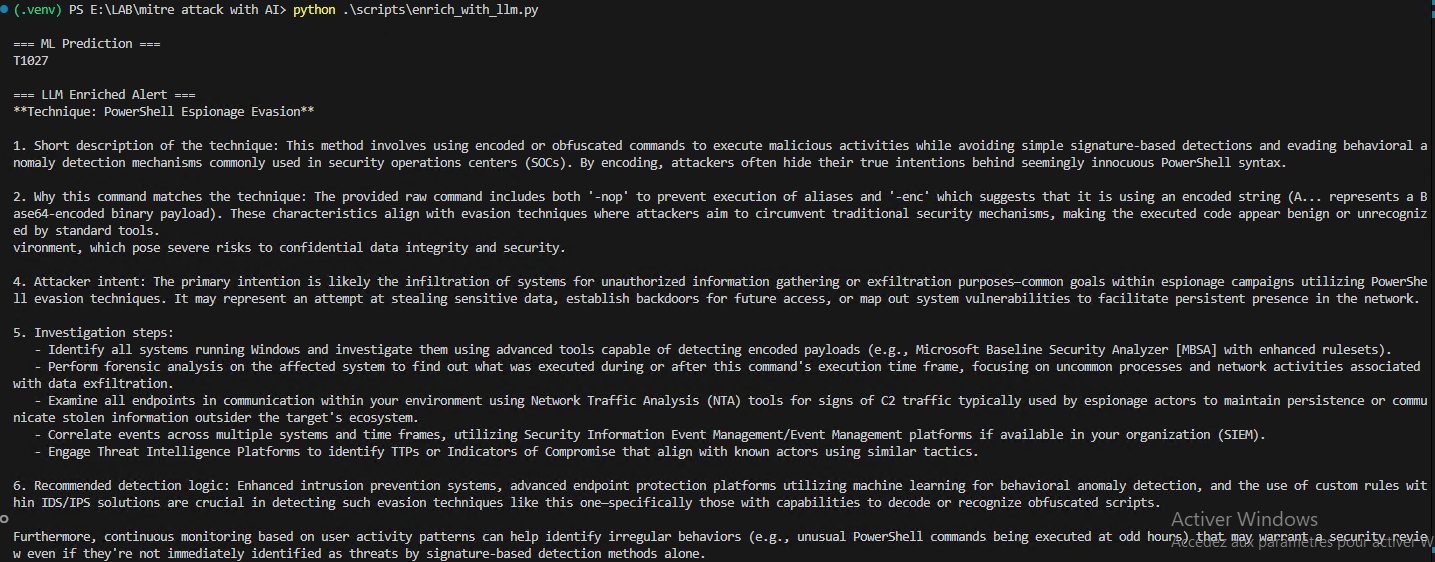
This repository demonstrates a machine learning pipeline for detecting MITRE ATT&CK techniques from logs and enriching the output using a local LLM.
anomaly-detectioneducationintrusion-detection+3
811 months ago
log4j-cve-code-search-resources preview

log4j-cve-code-search-resources

GitHubsourcegraph/log4j-cve-code-search-resources

Using code search to help fix/mitigate log4j CVE-2021-44228
code-analysiscurated-resourceseducation+3
14 years ago
SkyProfile preview

SkyProfile

GitHubalsatianconsulting/skyprofile

A lightweight aviation intelligence tool that queries ADSB-Exchange flight data using tail numbers or ICAO identifiers to quickly profile aircraft…
data-exfiltrationinformation-gatheringosint+3
99 months ago
Mahoraga-Webapp-Defender preview

Mahoraga-Webapp-Defender

GitHubageofalgorithms/mahoraga-webapp-defender

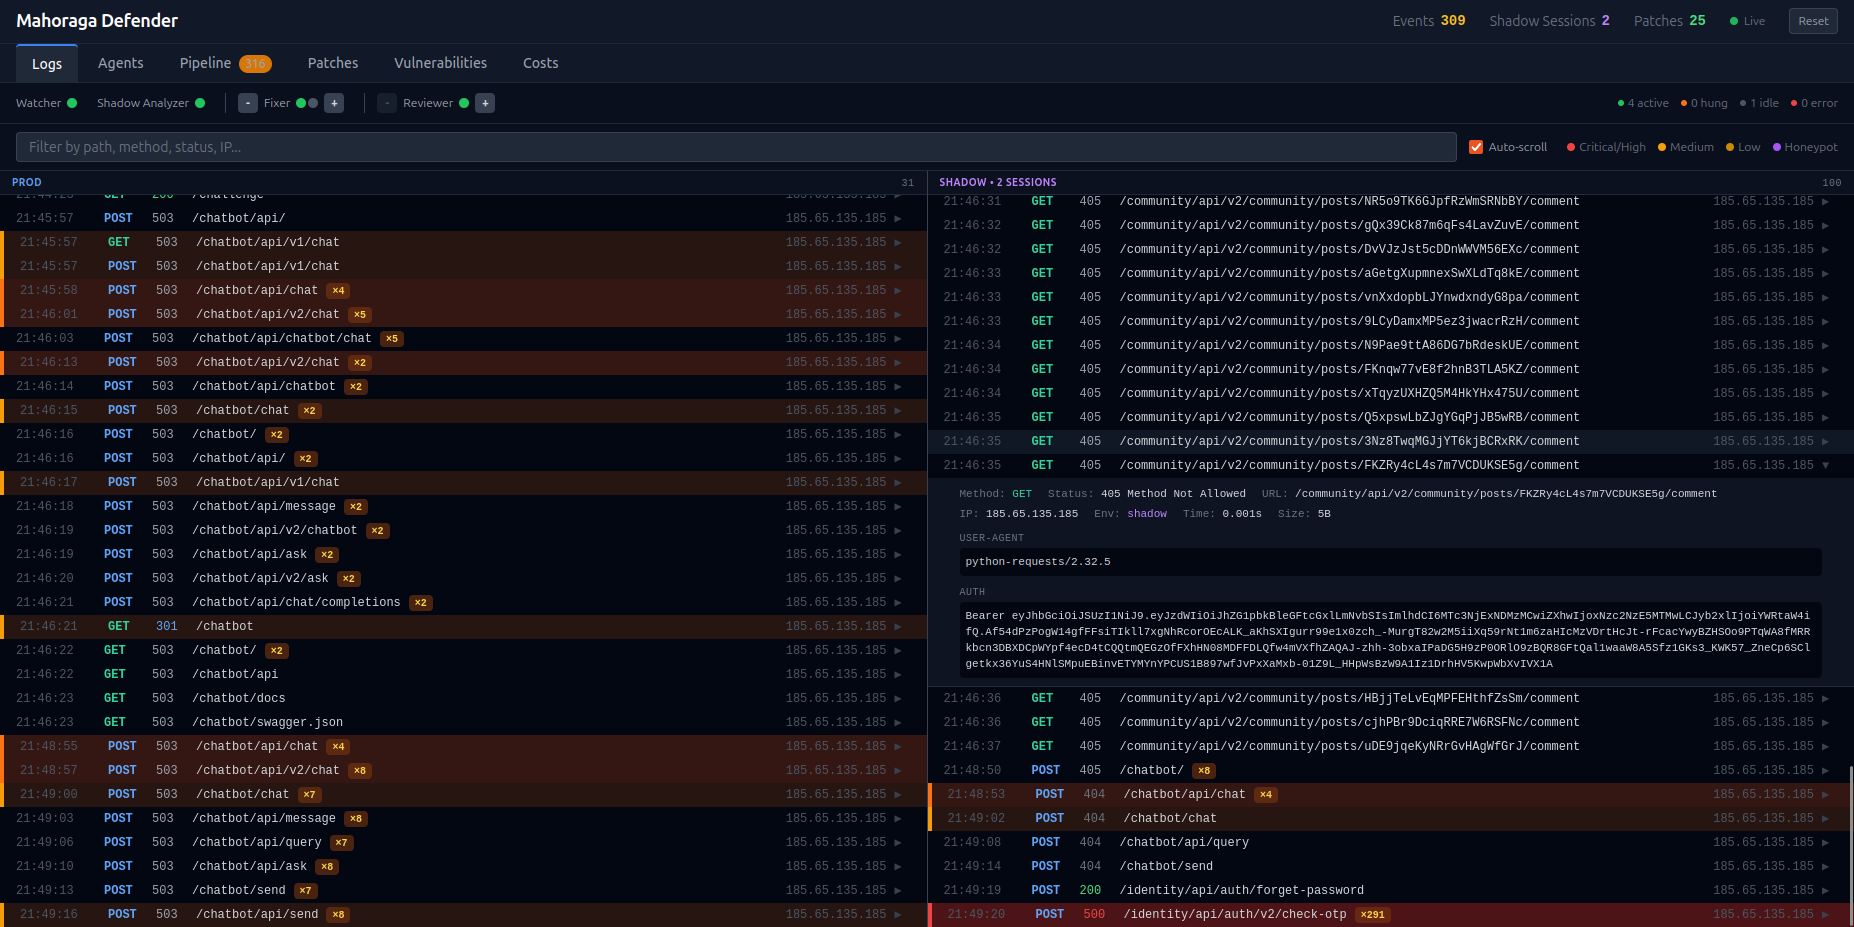
AI-powered reactive website defense system that detects attacks, analyzes them, and autonomously patches source code in real-time using LLM agents.
ai-securityapi-securityctf+6
45 months ago
Sharepoint-cve-2023-29375-incident-response preview

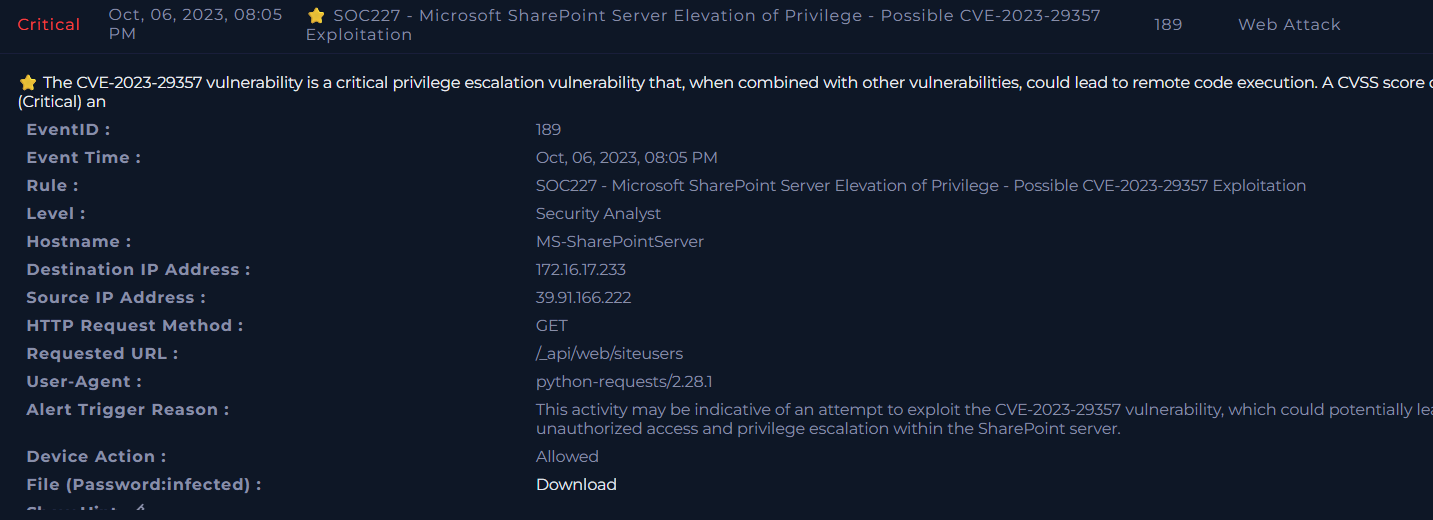
Sharepoint-cve-2023-29375-incident-response

GitHubzedocun/sharepoint-cve-2023-29375-incident-response

End-to-end SOC incident analysis and threat hunting playbook targeting Microsoft SharePoint privilege escalation (CVE-2023-29357) using SIEM logs,…
digital-forensicseducationincident-response+3
14 days ago
standalone_tdo preview

standalone_tdo

GitHubblevene/standalone_tdo

Extracts structured Cyber Threat Intelligence (CTI) from PDF, DOCX, and TXT documents using LLMs. Generates MITRE ATT&CK attack flows, detection…
educationinformation-gatheringmachine-learning+3
49 months ago
Wireshark preview

Wireshark

GitHubkirkdjohnson/wireshark

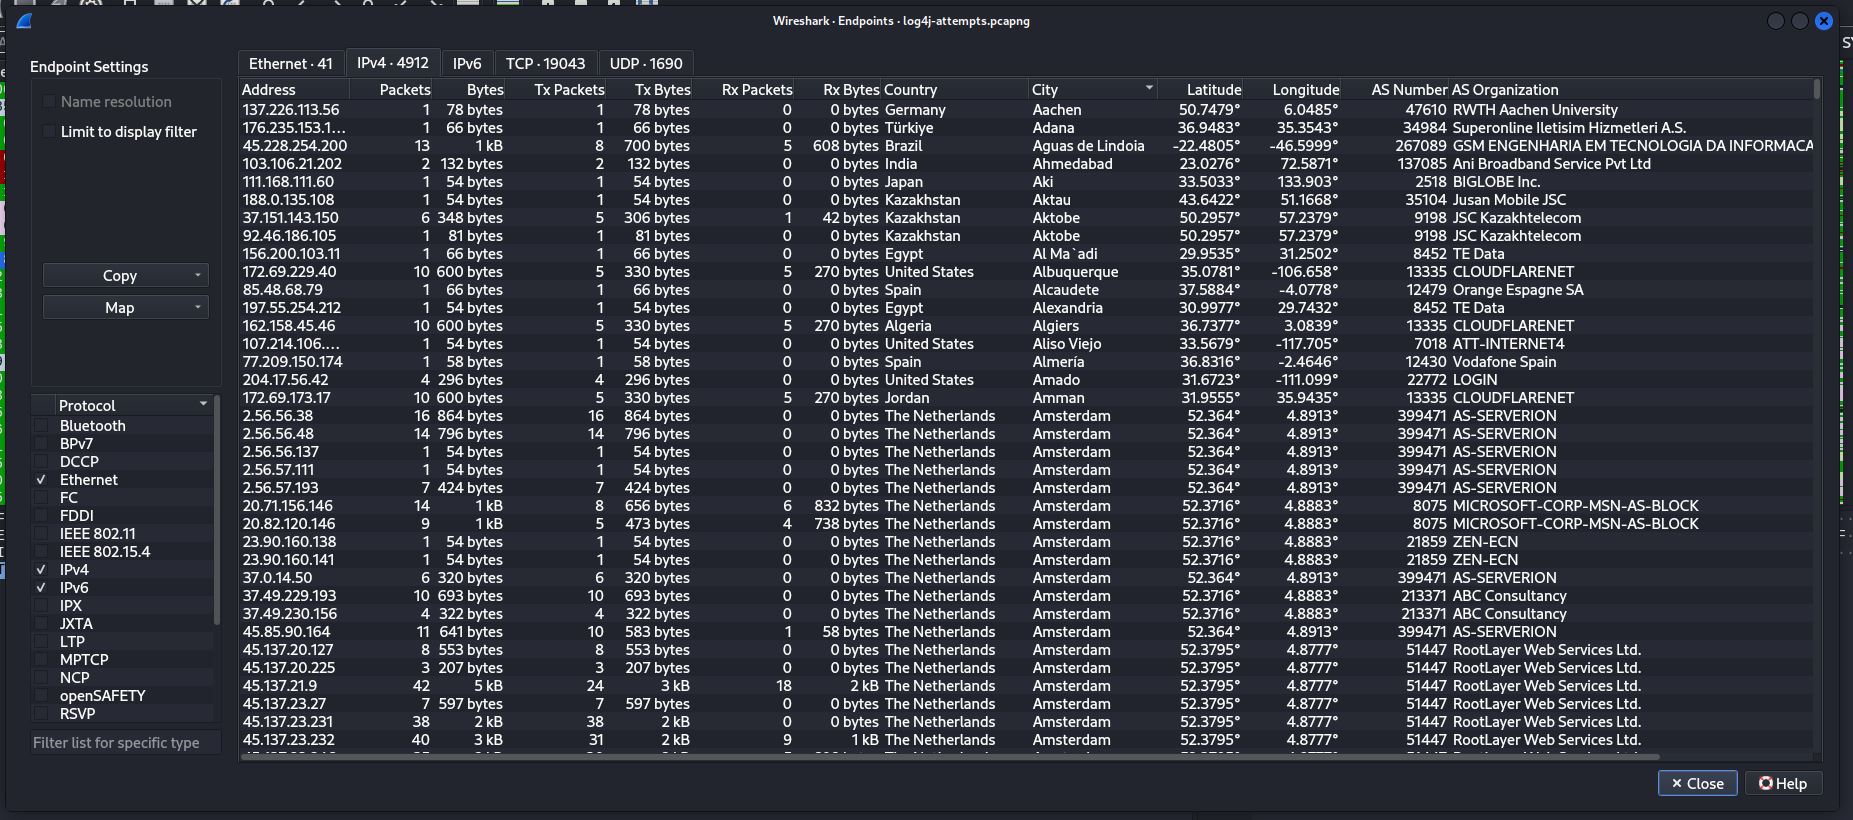
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
command-and-controldigital-forensicseducation+9
32 years ago
follina-msdt-threat-investigation preview

follina-msdt-threat-investigation

GitHubzavikhttak/follina-msdt-threat-investigation

🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…
digital-forensicseducationincident-response+4
3 months ago
cve-2023-23397-detection-lab preview

cve-2023-23397-detection-lab

GitHubzhoucc-cpu/cve-2023-23397-detection-lab

Detection and mitigation research lab for CVE-2023-23397 using network and endpoint security telemetry.
educationincident-responsenetwork-security+2
1 month ago
SOC335-CVE-2024-49138-Investigation preview

SOC335-CVE-2024-49138-Investigation

GitHubnadineelliottcyber/soc335-cve-2024-49138-investigation

SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.
curated-resourcesdigital-forensicseducation+3
1 month ago
OWASP-MCP-Threat-Modeling preview

OWASP-MCP-Threat-Modeling

GitHubowasp/owasp-mcp-threat-modeling

OWASP tool for systematic threat modeling using the Model Context Protocol to identify and mitigate security risks in software architecture.
curated-resourceseducationthreat-intelligence+1
12 months ago
CTWall preview

CTWall

GitHubcybergabisoft/ctwall

CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
cloud-securitycontainer-securitydevsecops+6
13 months ago
class_struggle preview

class_struggle

GitHubartur-augustyniak/class_struggle

Autoencoder-based anomaly detection for identifying phishing domains using CERT Polska warning list data, with Jupyter notebooks for research and…

anomaly-detectiondns-analysiseducation+4
211 months ago
Previous123456Next