
Fennec
 abdulrhmanalfaifi/fennec
Artifact collection tool for *nix systems
digital-forensicsforensicsincident-response+3
abdulrhmanalfaifi/fennecArtifact collection tool for *nix systems
 vulncheck-oss/cli
VulnCheck's official command line tool
 yousseflahouifi/moniorg
Passive domain monitoring tool leveraging Certificate Transparency logs to discover and track newly issued domains for an organization, with Slack…
 redsiege/just-metadata
Just-Metadata is a tool that gathers and analyzes metadata about IP addresses. It attempts to find relationships between systems within a large…
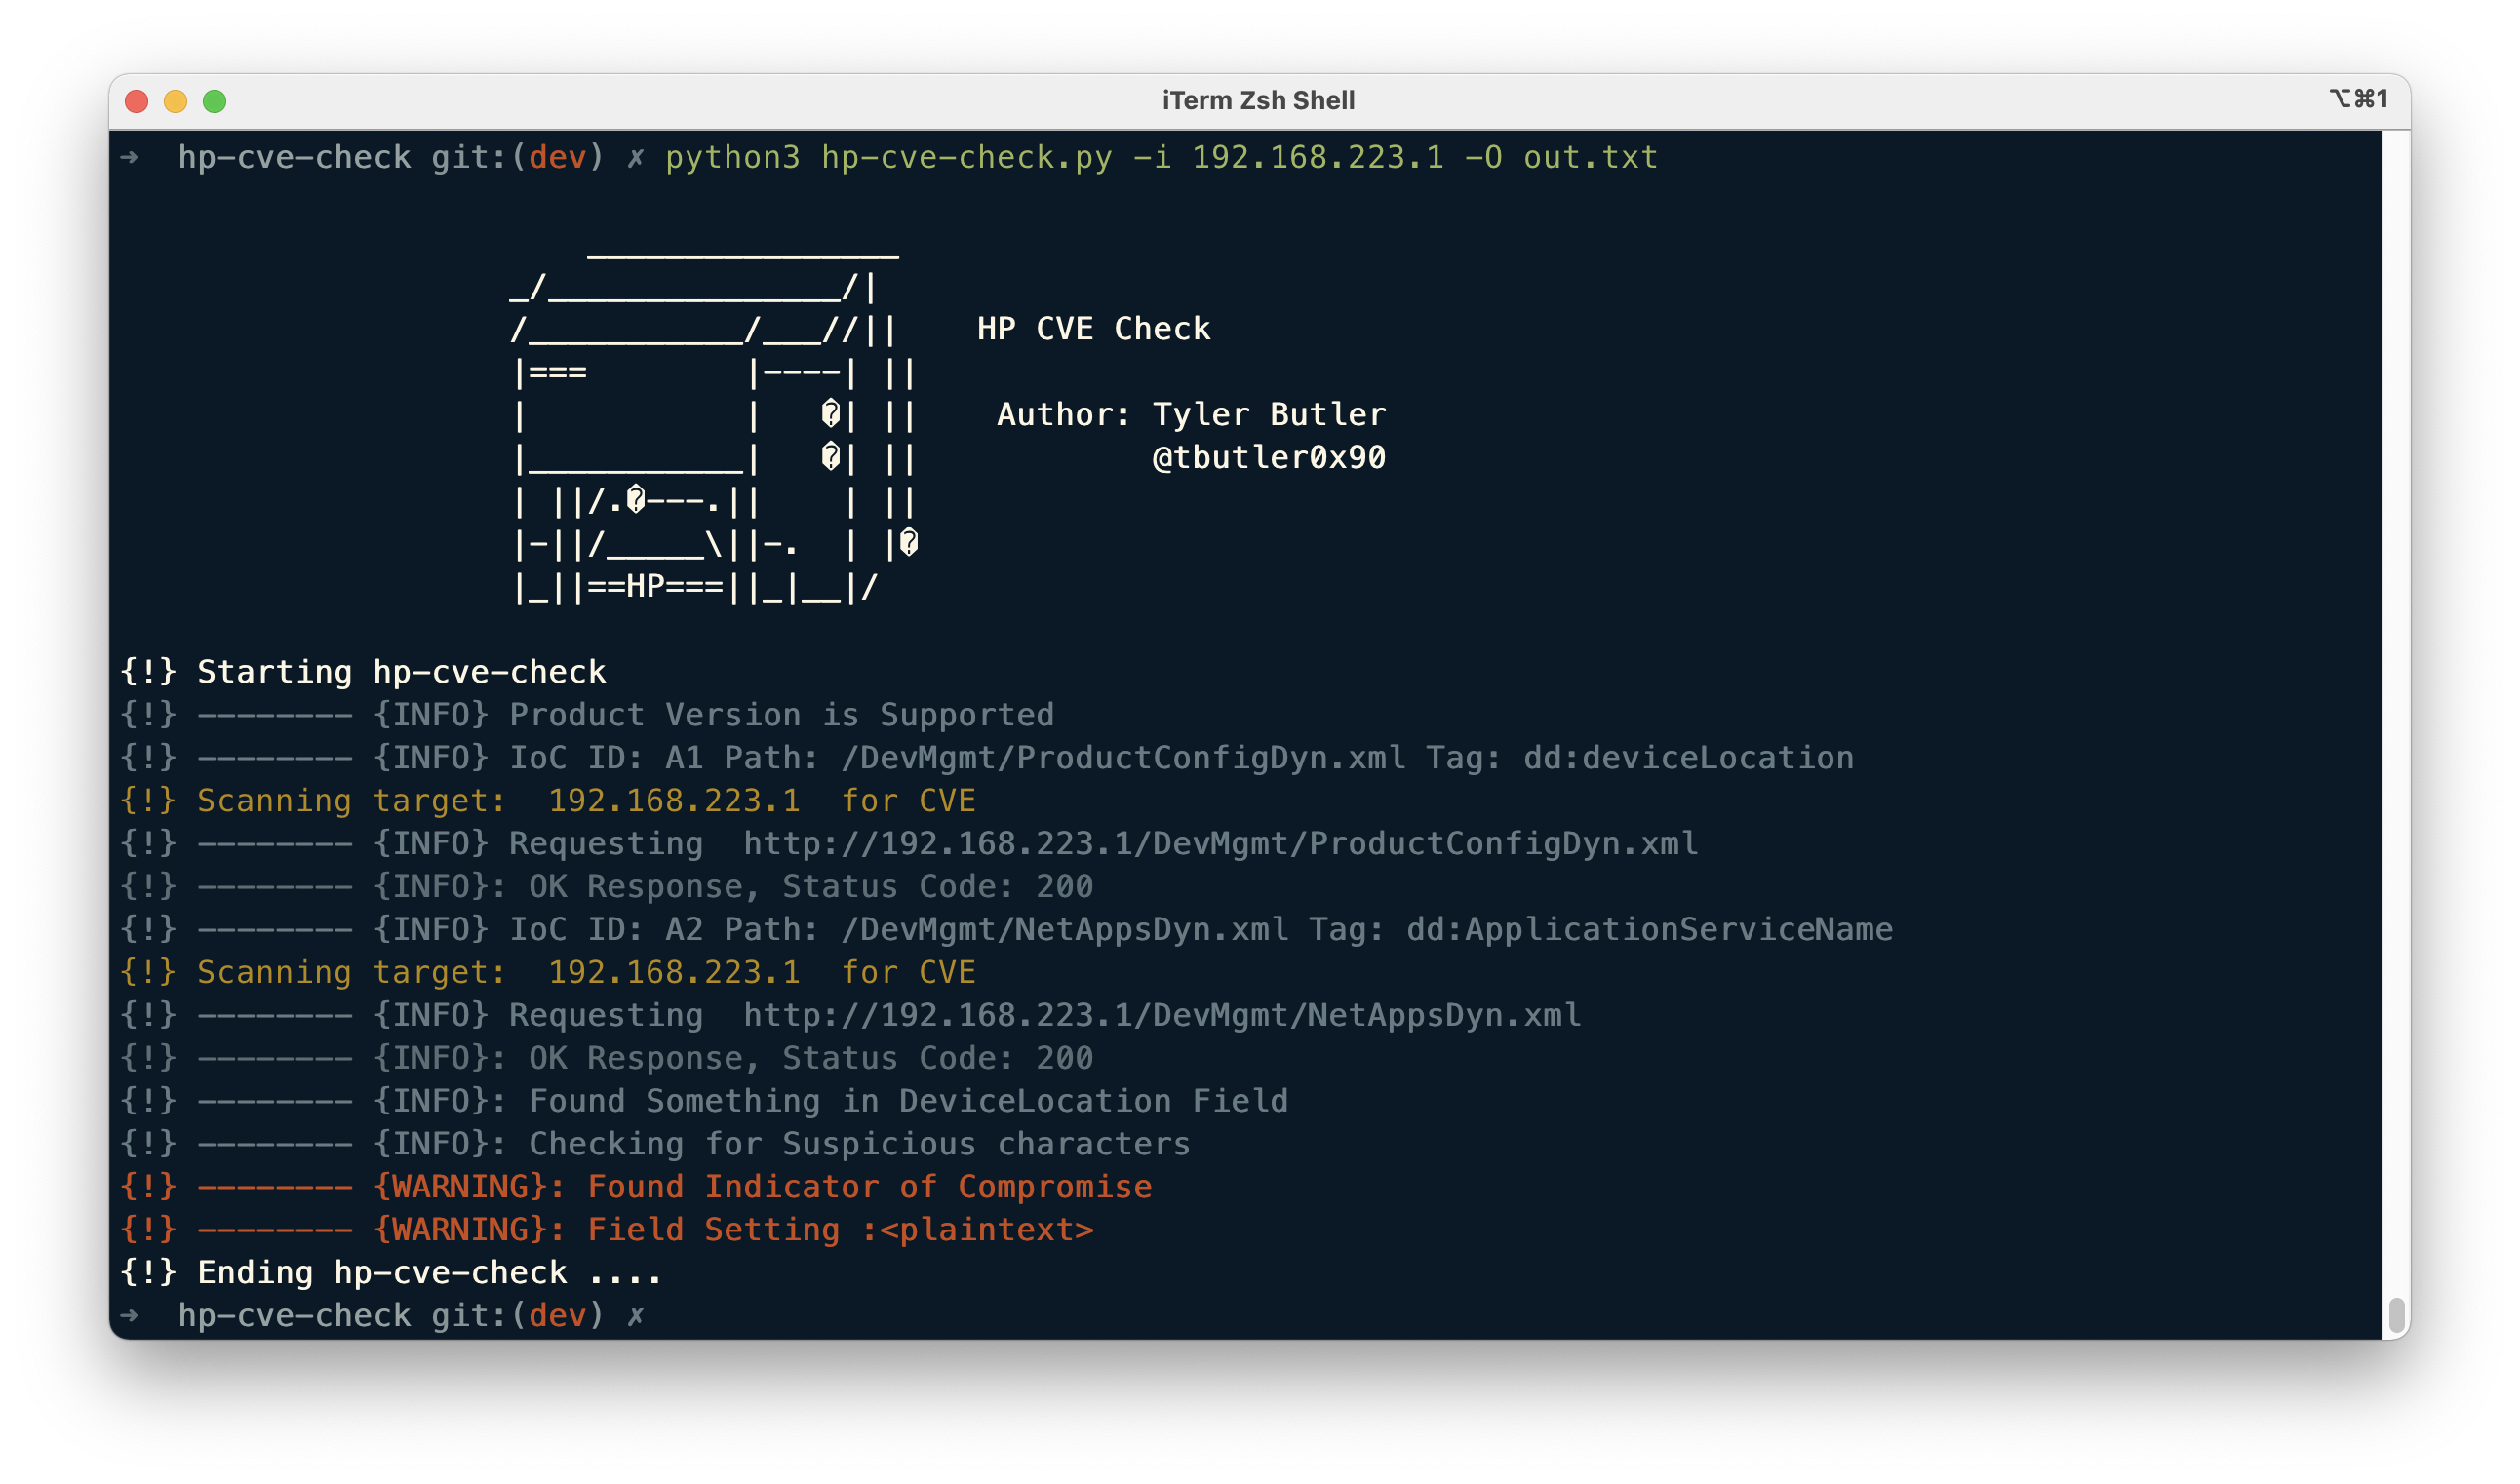 tcbutler320/cve-2021-3441-check
CVE-2021-3441 CVE Check is a python script to search targets for indicators of compromise to CVE-2021-3441
 salesforce/jarm
Active TLS server fingerprinting tool that sends crafted Client Hello packets to generate unique JARM hashes for identifying server configurations,…
 jxlil/pwndb
Tor-based leaked credential search tool that queries the pwndb2 hidden service to find emails and passwords exposed in data breaches, with wildcard…
 fr0gger/vthunting
Vthunting is a tiny script used to generate report about Virus Total hunting and send it by email, slack or telegram.
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 corelight/zeek-endpoint-enrichment
Zeek log enrichment tool that adds host information and known entity references to enhance network security monitoring and incident response.
 telefonicatc2tech/typodetect
Detects active domain mutations to prevent phishing and smishing. Uses IANA TLDs, blockchain DNS validation, and DoH malware reports. Outputs JSON or…
 jeet-ganguly/birdy-edwards
Automated AI powered Facebook intelligence tool for target profiling, network analysis and threat reporting. Runs entirely on-device via Ollama.…
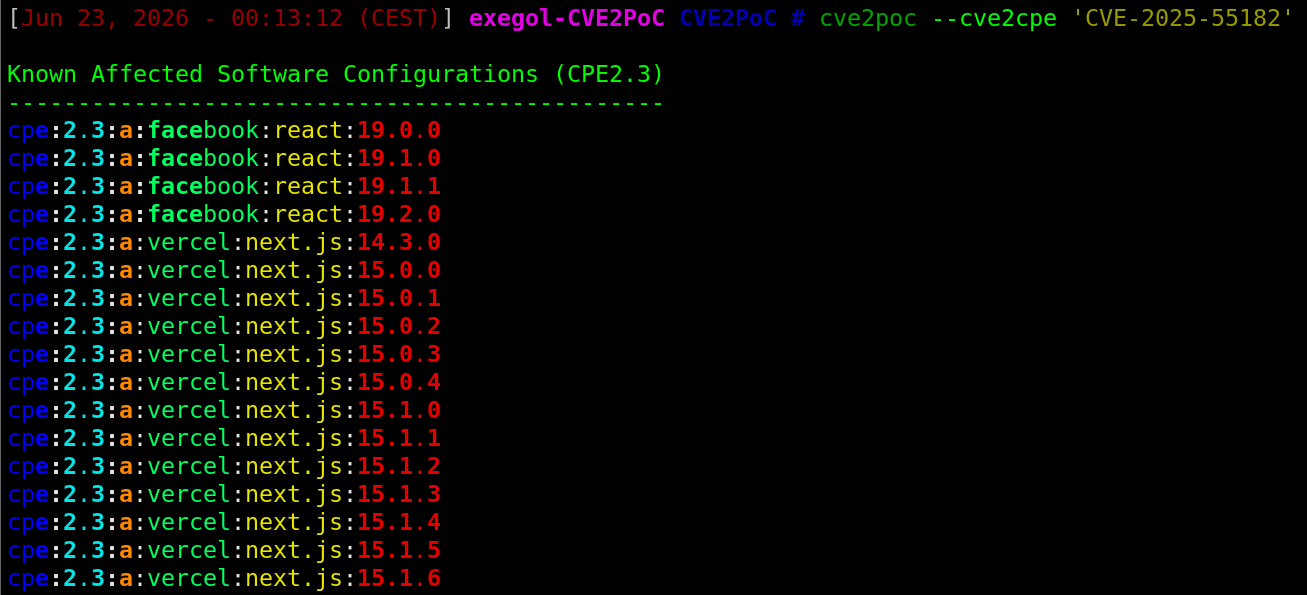 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
 alsatianconsulting/skyprofile
A lightweight aviation intelligence tool that queries ADSB-Exchange flight data using tail numbers or ICAO identifiers to quickly profile aircraft…
 te-k/harpoon
CLI tool for open source and threat intelligence
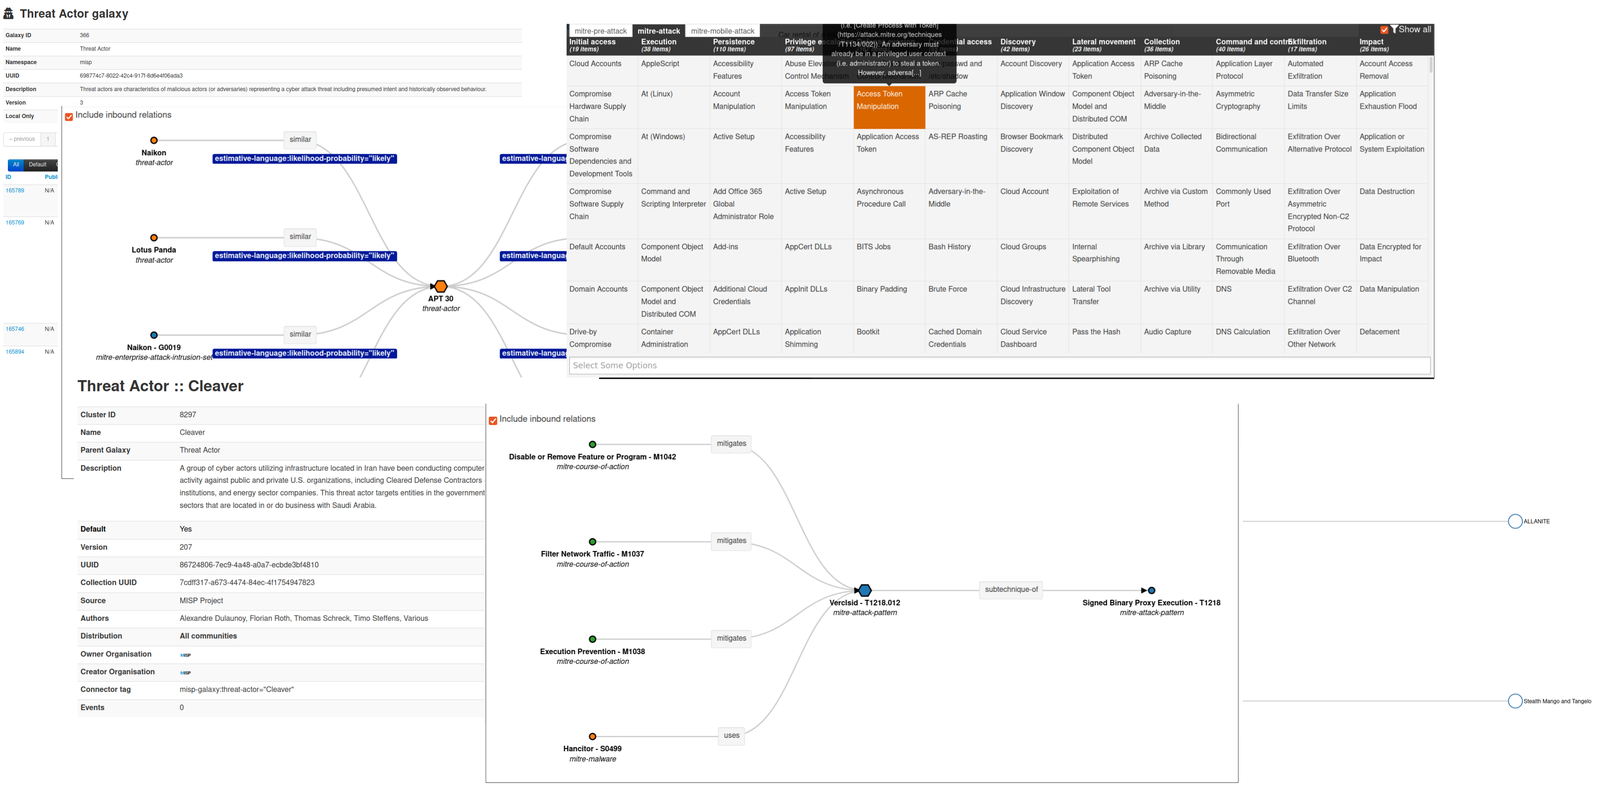 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…