Threat-Intelligence-Alerts

Welcome to the NCC Group Threat Intelligence Alert repo, here you will find the alerts which we have raised to our customers regarding intelligence…

Welcome to the NCC Group Threat Intelligence Alert repo, here you will find the alerts which we have raised to our customers regarding intelligence…

React2Shell, CVE-2025-55182, RCE Vulnerability: A critical breakdown of the unsafe deserialization flaw in React Server Components that enables…

Tools, tips, tricks, and more for exploring ICS Security.

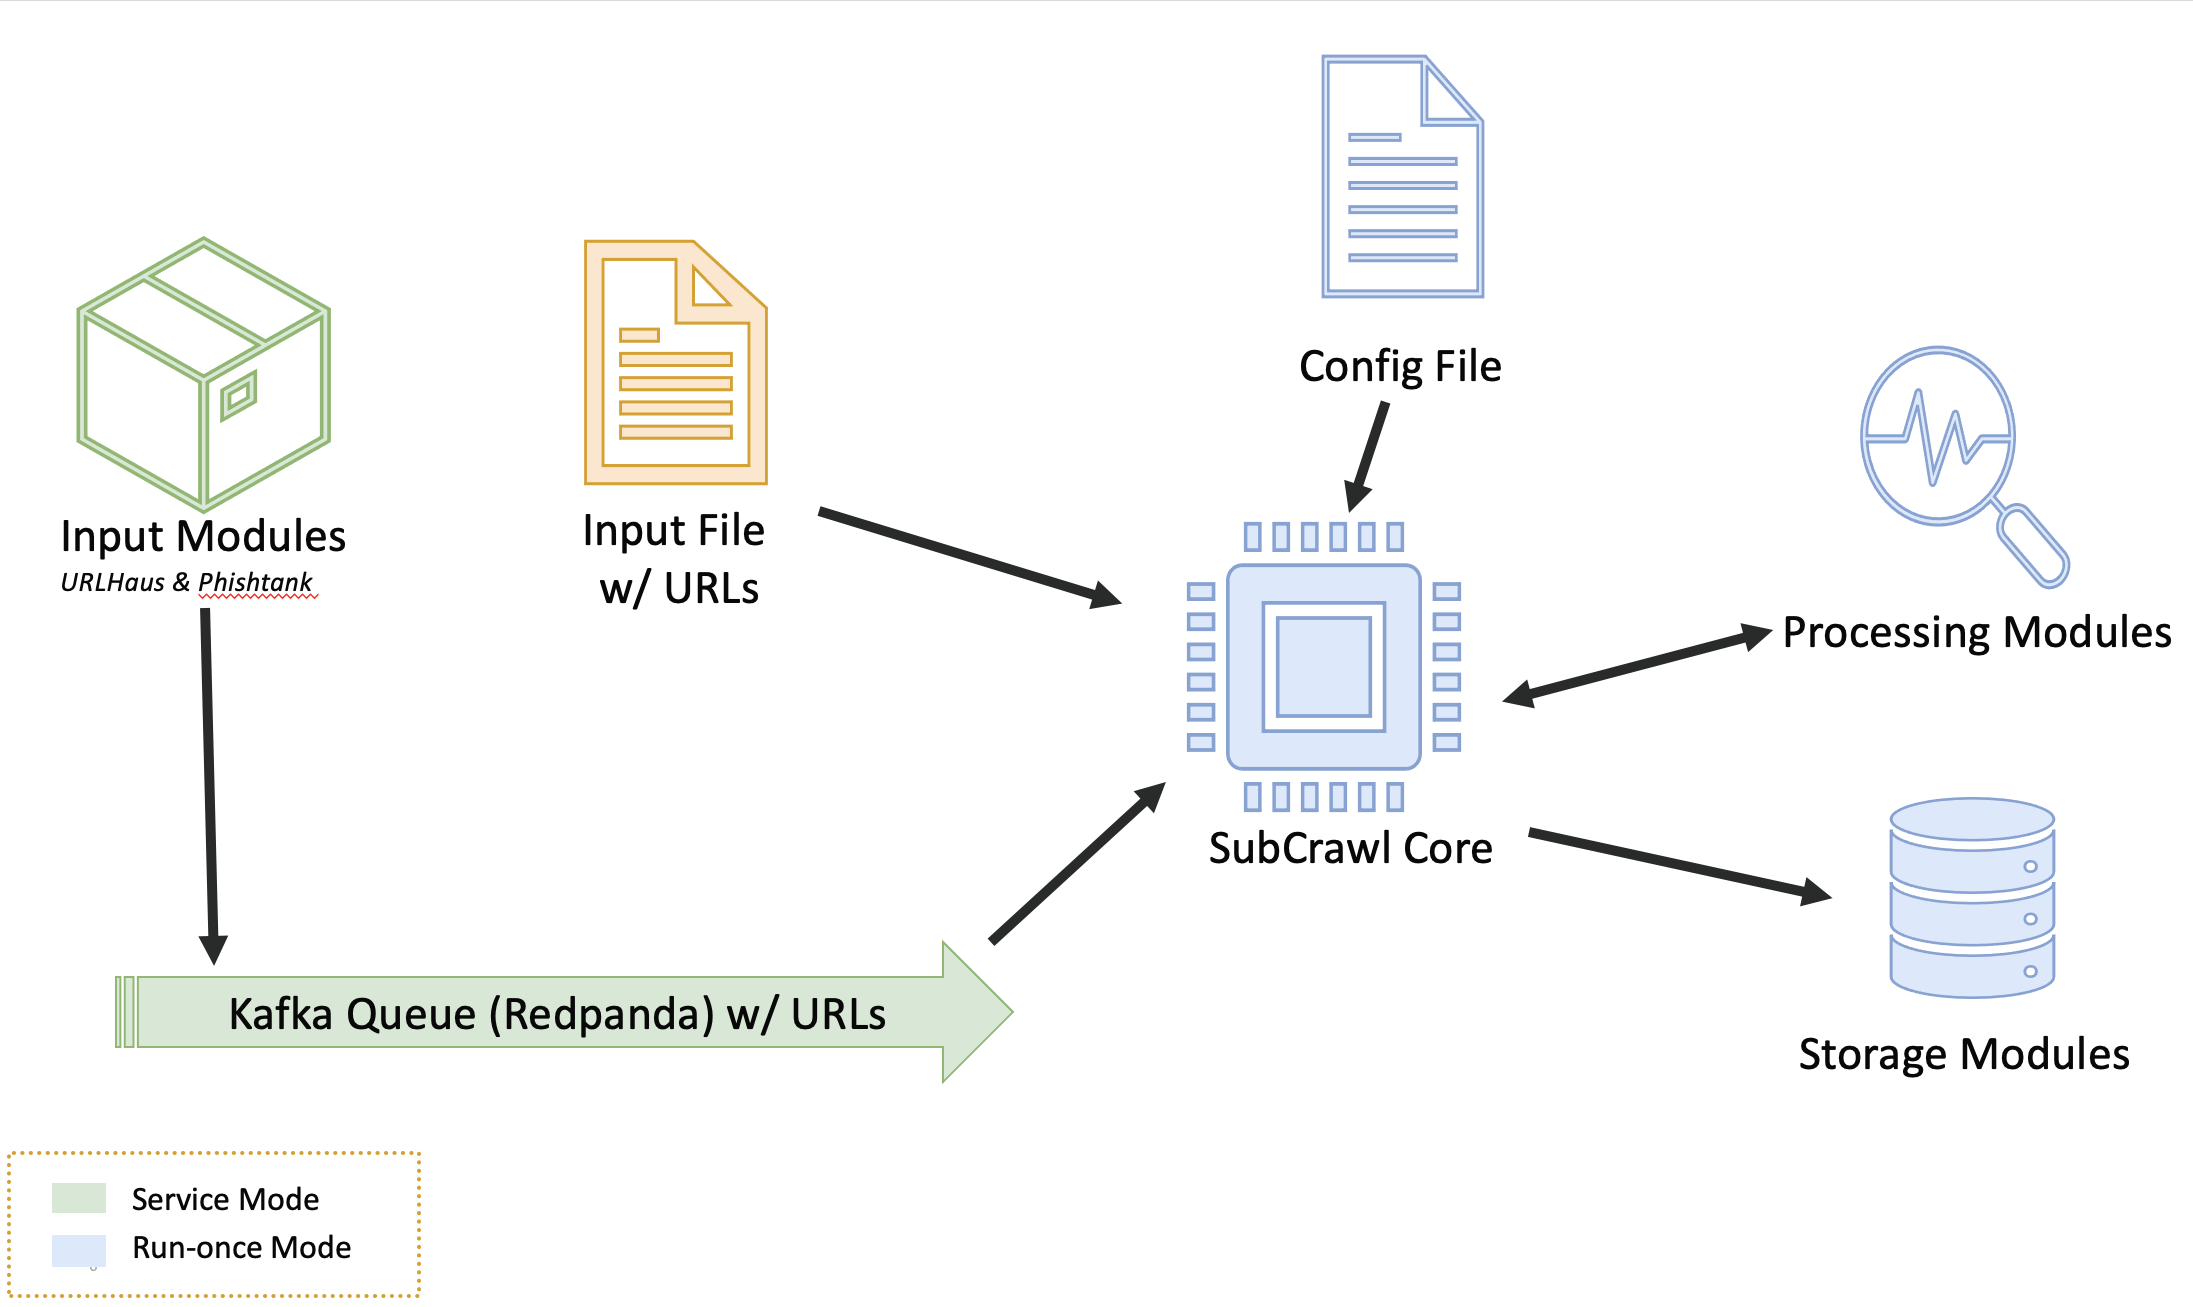
Modular framework for discovering and analyzing open directories on the web. Crawls URLs, extracts content, applies YARA/ClamAV scanning, and outputs…

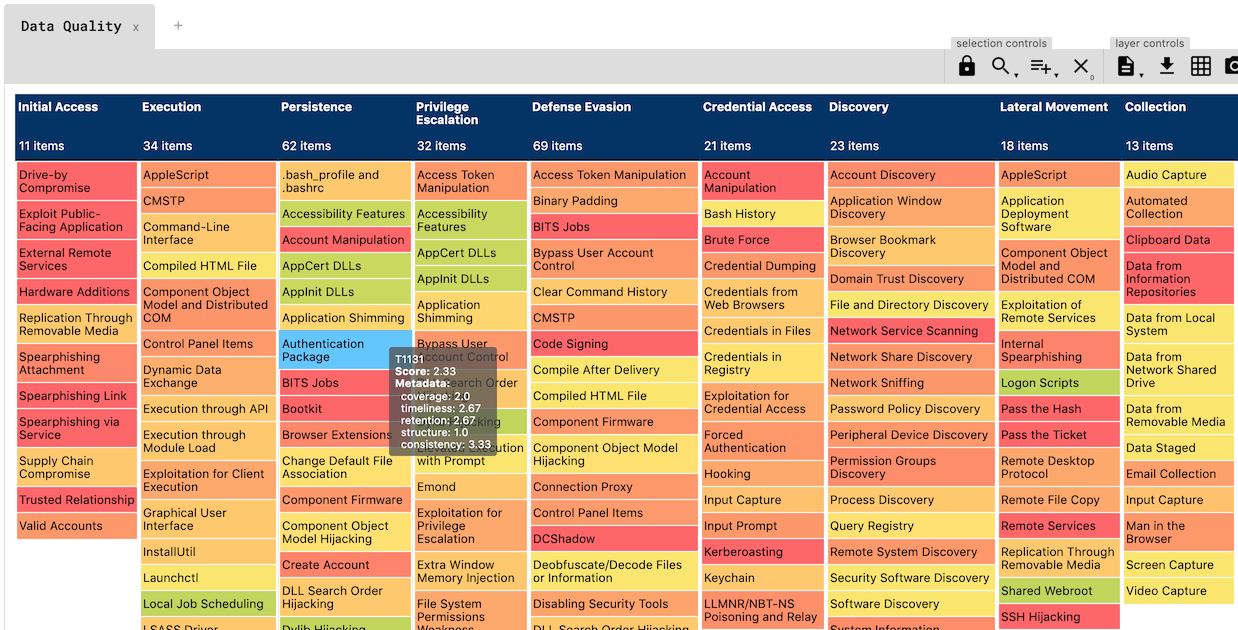
A tool to assess data quality, built on top of the awesome OSSEM.

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis

Analysis of the ransom demands from Shodan results

A high interaction SSH honeypot

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough

PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…

This project is a SIEM with SIRP and Threat Intel, all in one.

A python package for use in generating fake data for SOC and security automation.

CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…


LetsDefend SOC336 case study on CVE-2025-21298

L1 SOC Analysis: OSINT detection and risk validation of publicly exposed MikroTik RouterOS vulnerable to RCE | Tools: Shodan, NIST NVD