
HoneySAP
 owasp/honeysap
HoneySAP: SAP Low-interaction research honeypot
educationnetwork-securitythreat-intelligence
owasp/honeysapHoneySAP: SAP Low-interaction research honeypot
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 mkorman90/regipy
Regipy is an os independent python library for parsing offline registry hives
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
 s_r_e_e_r_a_j/netspecter
NetSpecter is a lightweight yet powerful asynchronous OSINT and reconnaissance engine built in Python.
 pduggusa/redis-cve-2026-23479-check
Safe read-only version checker + Sigma rule for Redis CVE-2026-23479 (authenticated use-after-free → RCE). Find exposed instances, patch…
 osintbuddy/web
Entity graphs, OSINT data mining, and plugins. Connect unstructured and public data for transformative insights 🌐 (Web version)
 ctxis/snitchdns
Database Driven DNS Server with a Web UI
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
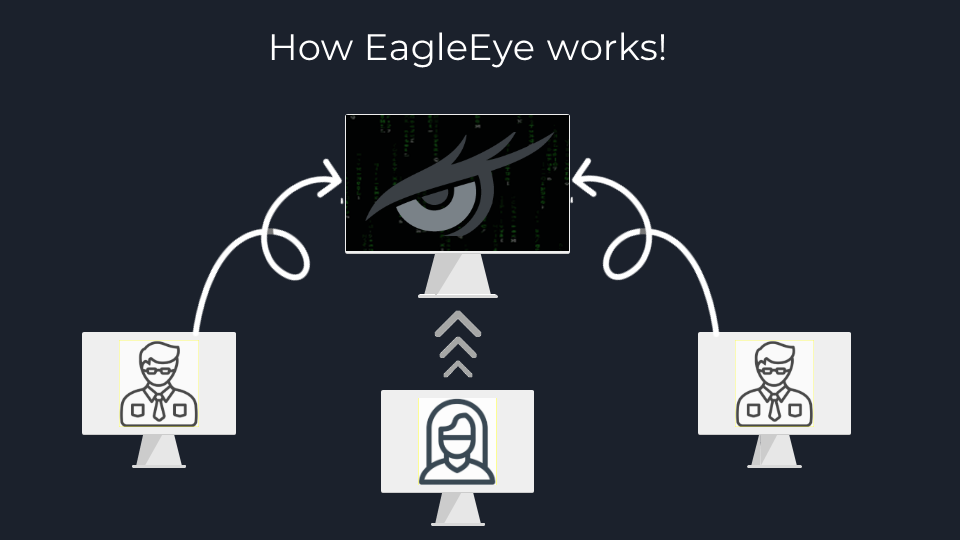 d4vinci/eagleeye
A host-based IDS and network monitoring system (My graduation project)
 corelight/corelight-ansible-roles
Corelight-Ansible-Roles are a collection of Ansible Roles and playbooks that install, configure, run and manage a variety of Corelight, Suricata and…