NWH-Stealer-Analysis-Fileless-Bun-Runtime-Execution-Clipboard-Image-Theft-Cloud-C2-AWS-R2-

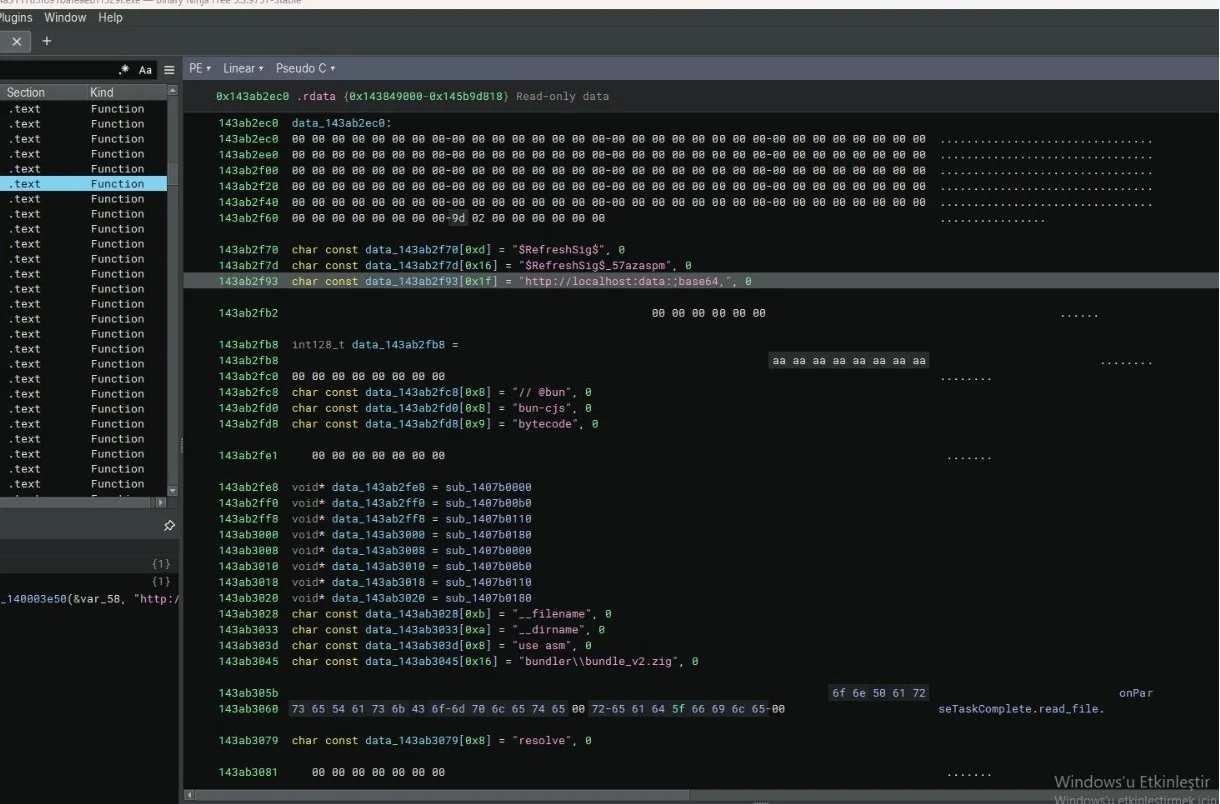
Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…

Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.

Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…

Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…

Code, aggregate data and LaTeX source for 'Who Patches the Lightning Network? Evidence from Release Lines in Gossip, 2023-2026' (arXiv:2610.30350)

Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.

A process monitoring tool that tries to detect exploitation

High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…

Indicators of compromise from to analysis and research by Nextron Threat Research team

Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.

OSINT identity investigation tool. Pivot from an e-mail, username, phone or wallet across 46 sources into one profile and relationship graph.

Python-based OSINT tool that gathers and analyzes publicly available data from open sources to support threat intelligence, vulnerability research,…

Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

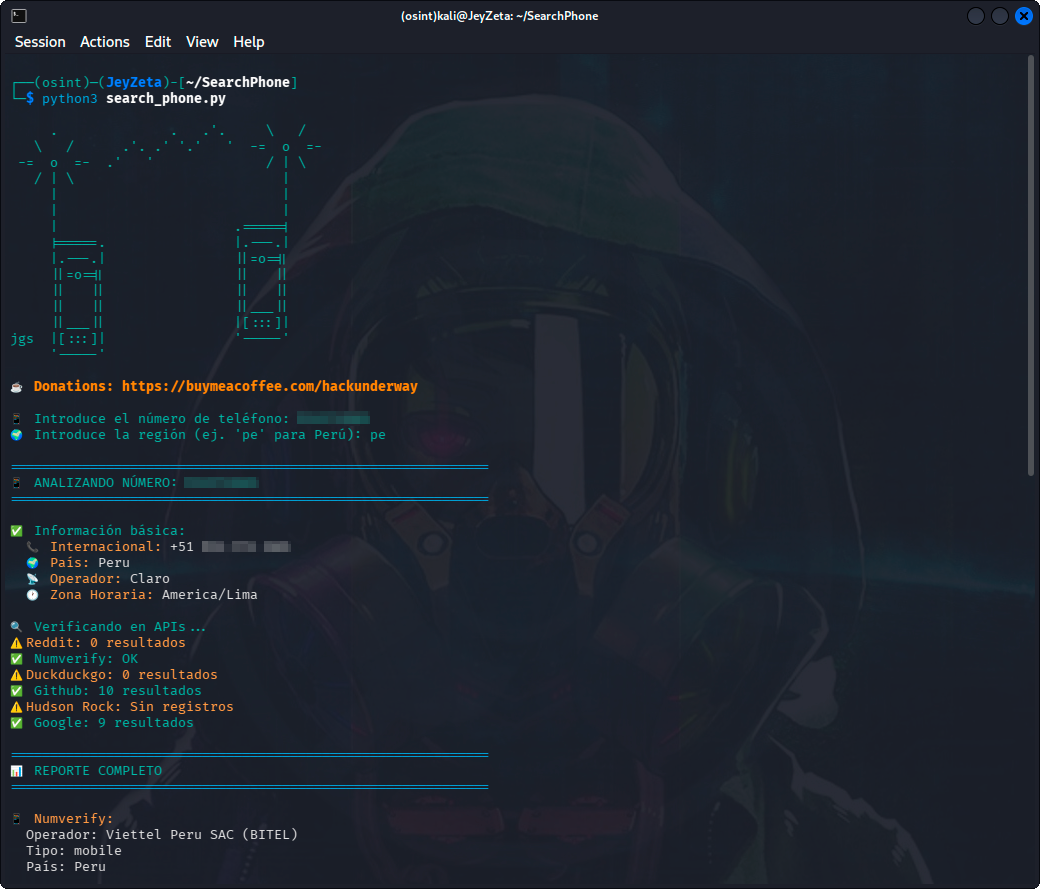
Phone number OSINT toolkit with multi-API search (Google, GitHub, Numverify, Reddit, DuckDuckGo), Hudson Rock infostealer intelligence, and automatic…

A repo to conduct vulnerability enrichment.

Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…