SOC235---Atlassian-Confluence-Broken-Access-Control-0-Day-CVE-2023-22515

SOC analyst walkthrough triaging a Confluence CVE-2023-22515 broken access control exploitation attempt, covering log analysis, MITRE ATT&CK mapping,…

SOC analyst walkthrough triaging a Confluence CVE-2023-22515 broken access control exploitation attempt, covering log analysis, MITRE ATT&CK mapping,…

Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.

Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…

Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…

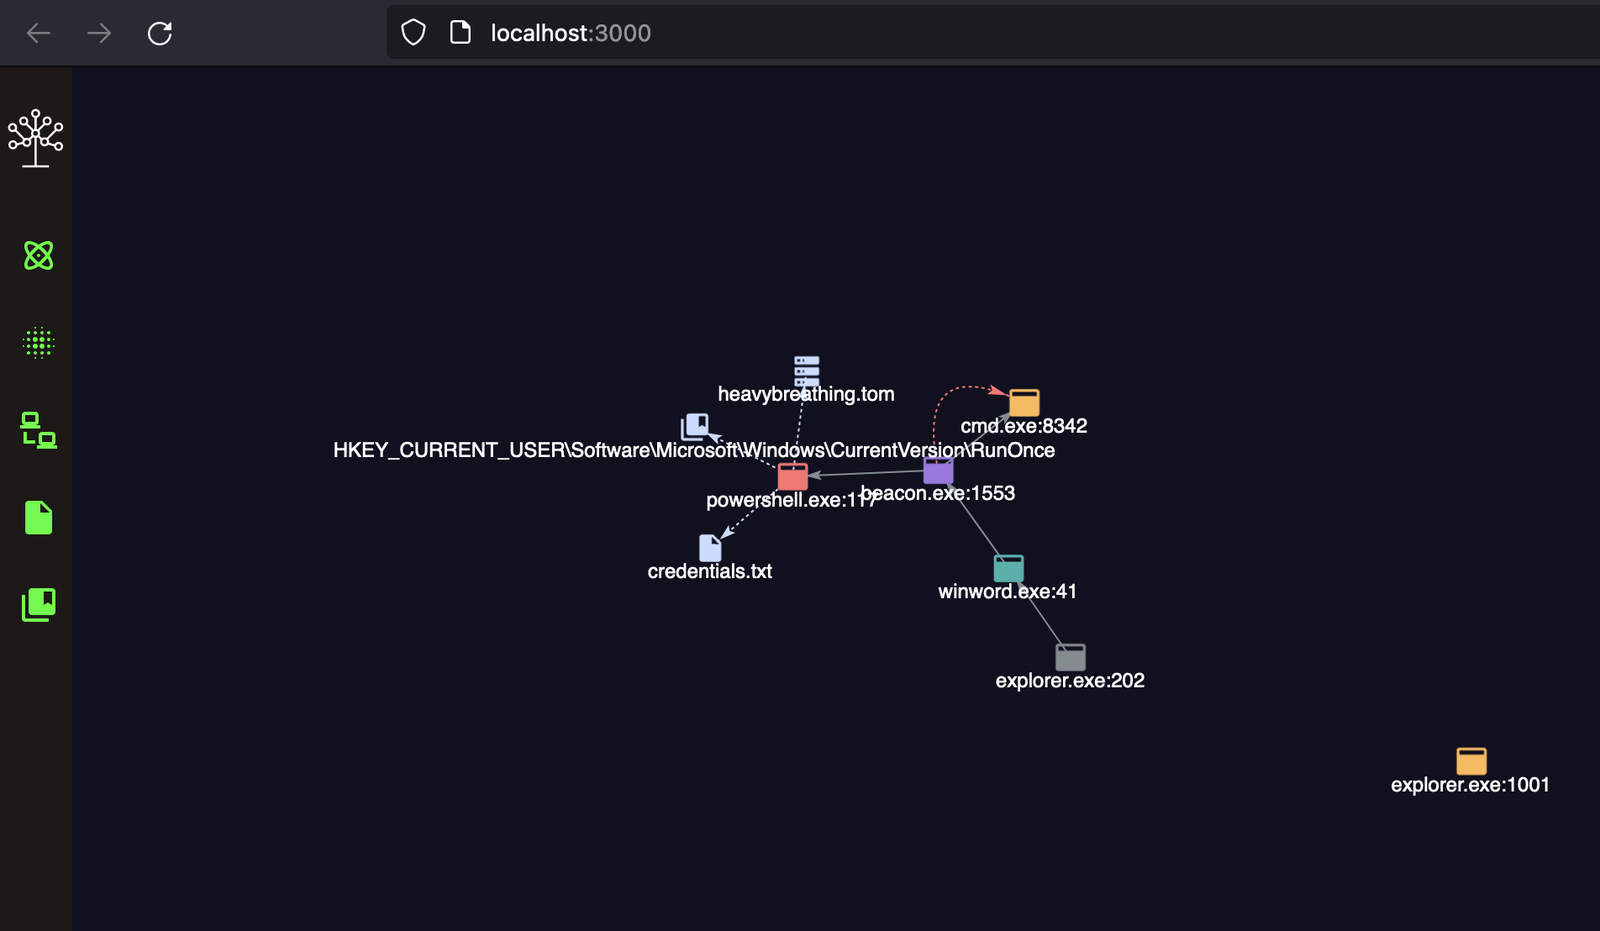
Interactive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…

Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…

Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…

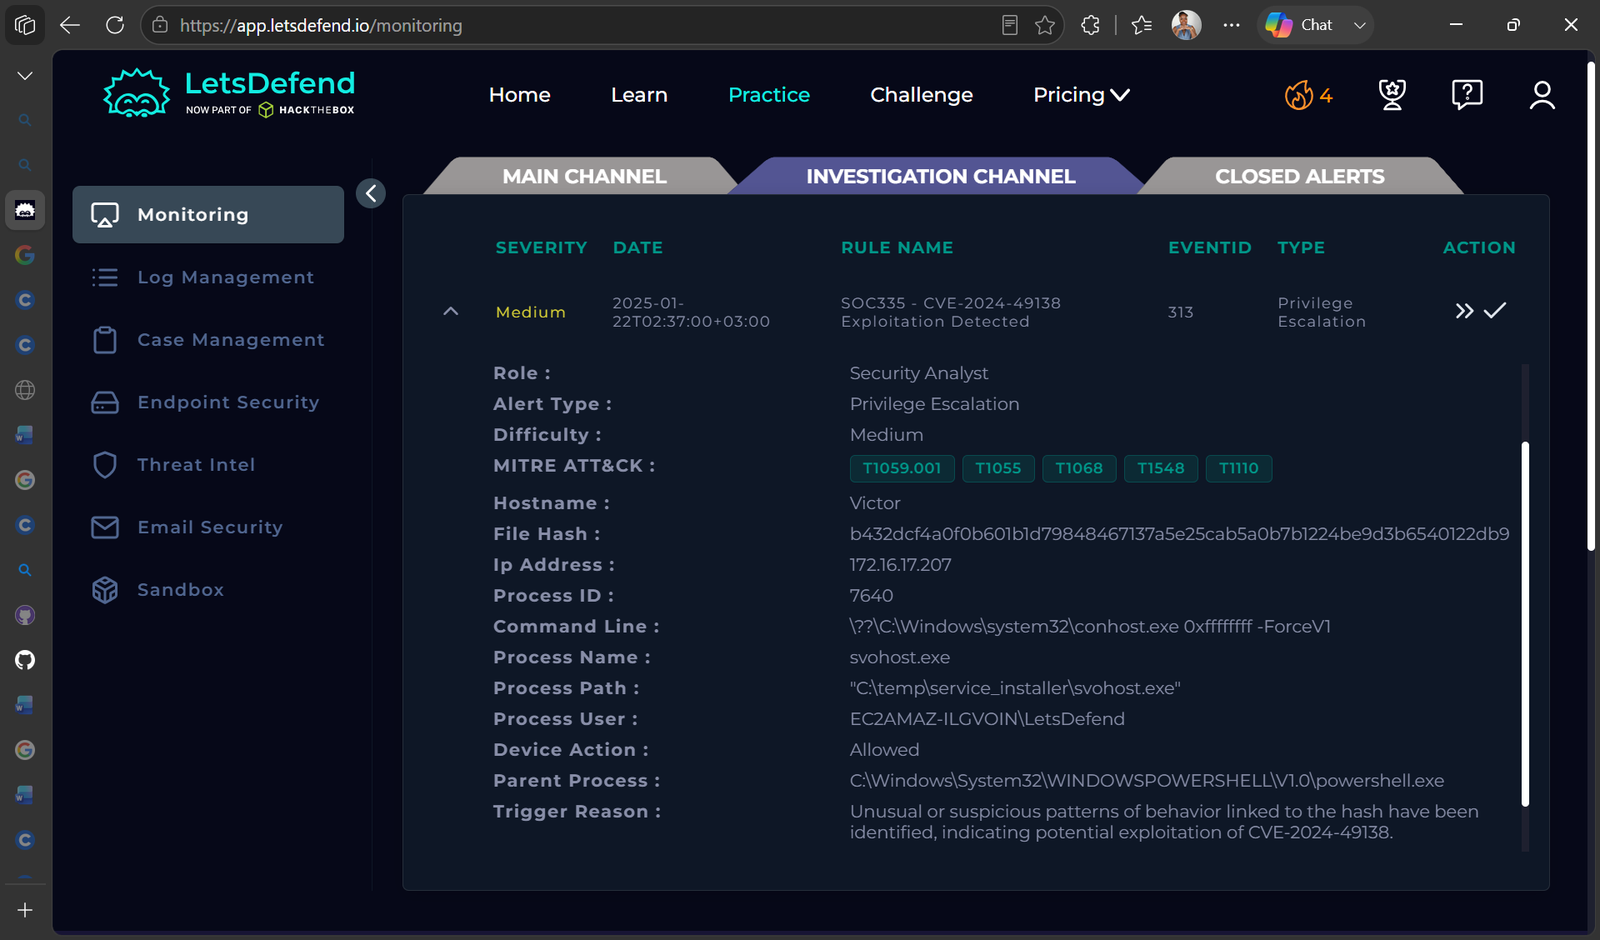
SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.

SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…

Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…

Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…

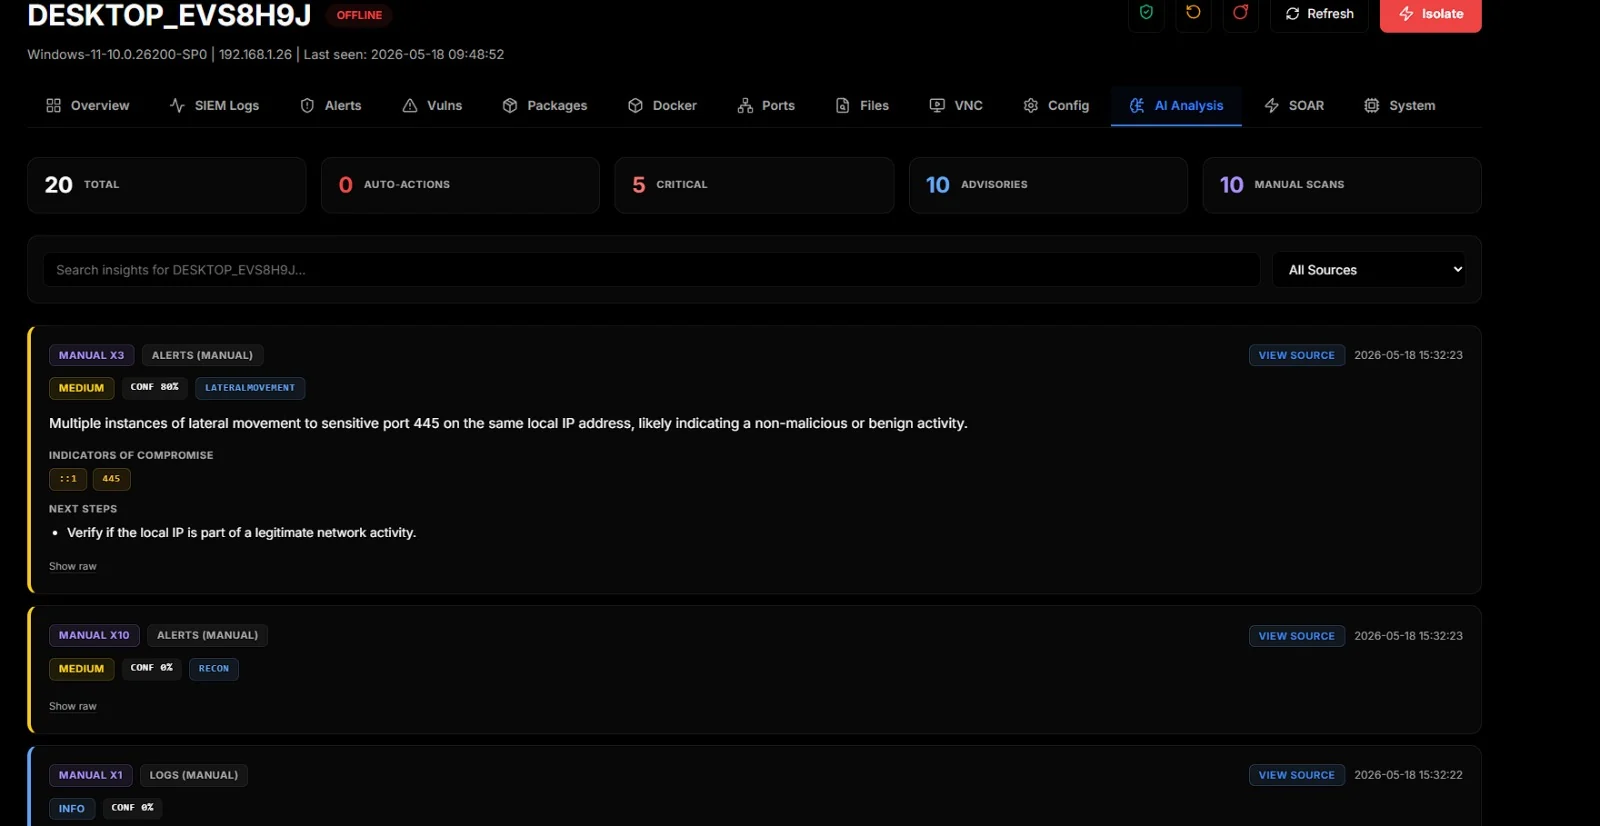
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.

Detection signatures for CVE-2026-41940 and shemas for cPanel logs

This is the office check script provided by cPanel for all the users who are using cPanel

Minimal Redis honeypot detecting RediShell (CVE-2025-49844) exploits.

Detection content for CVE-2026-22557 — UniFi Network Application unauthenticated path traversal (CVSS 10.0). Includes YARA, Sigma, KQL, Splunk SPL,…