
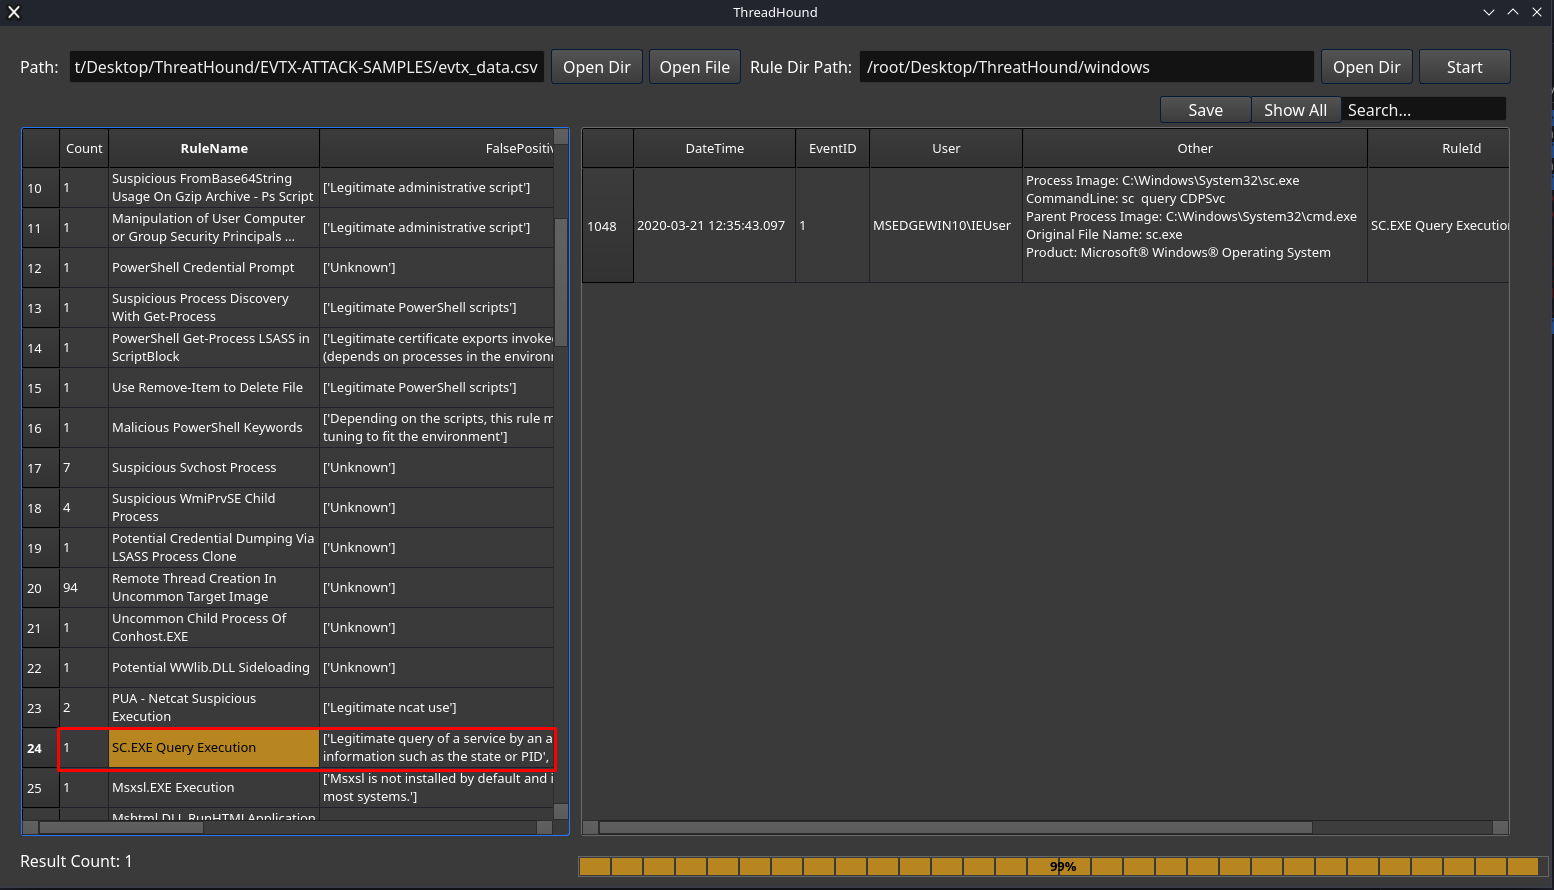
ThreatHound
 mazx0p/threathound
Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
digital-forensicsincident-responselog-analysis+1
159
mazx0p/threathoundAutomated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
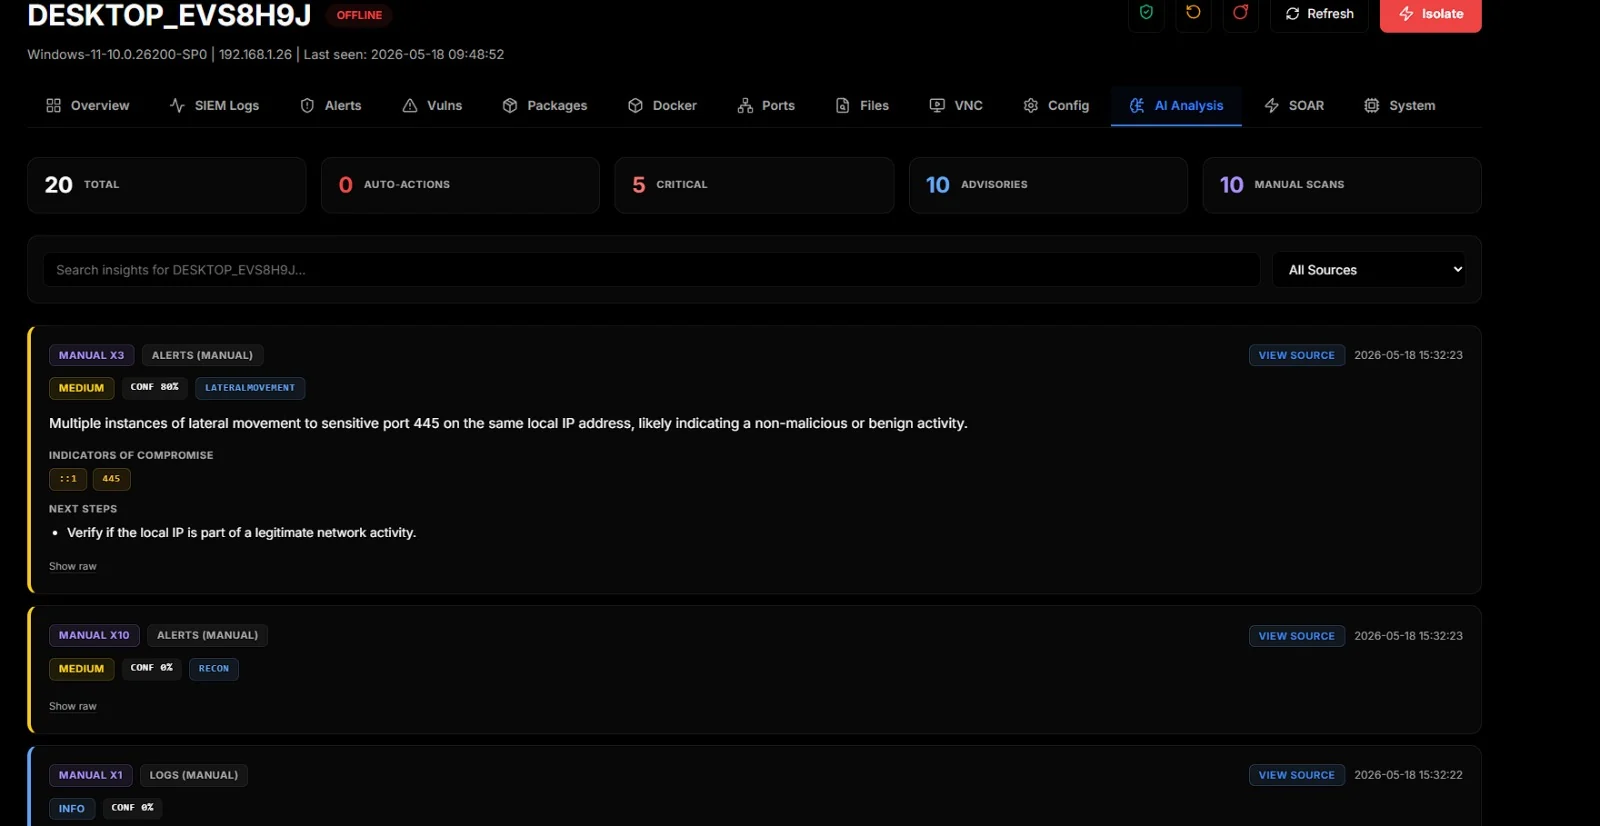 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
 permiso-io-tools/cloudgrappler
Query high-fidelity cloud detections for known threat actors across AWS, Azure, and GCP using CloudTrail logs and custom threat intelligence rules.
 pavel-odintsov/fastnetmon
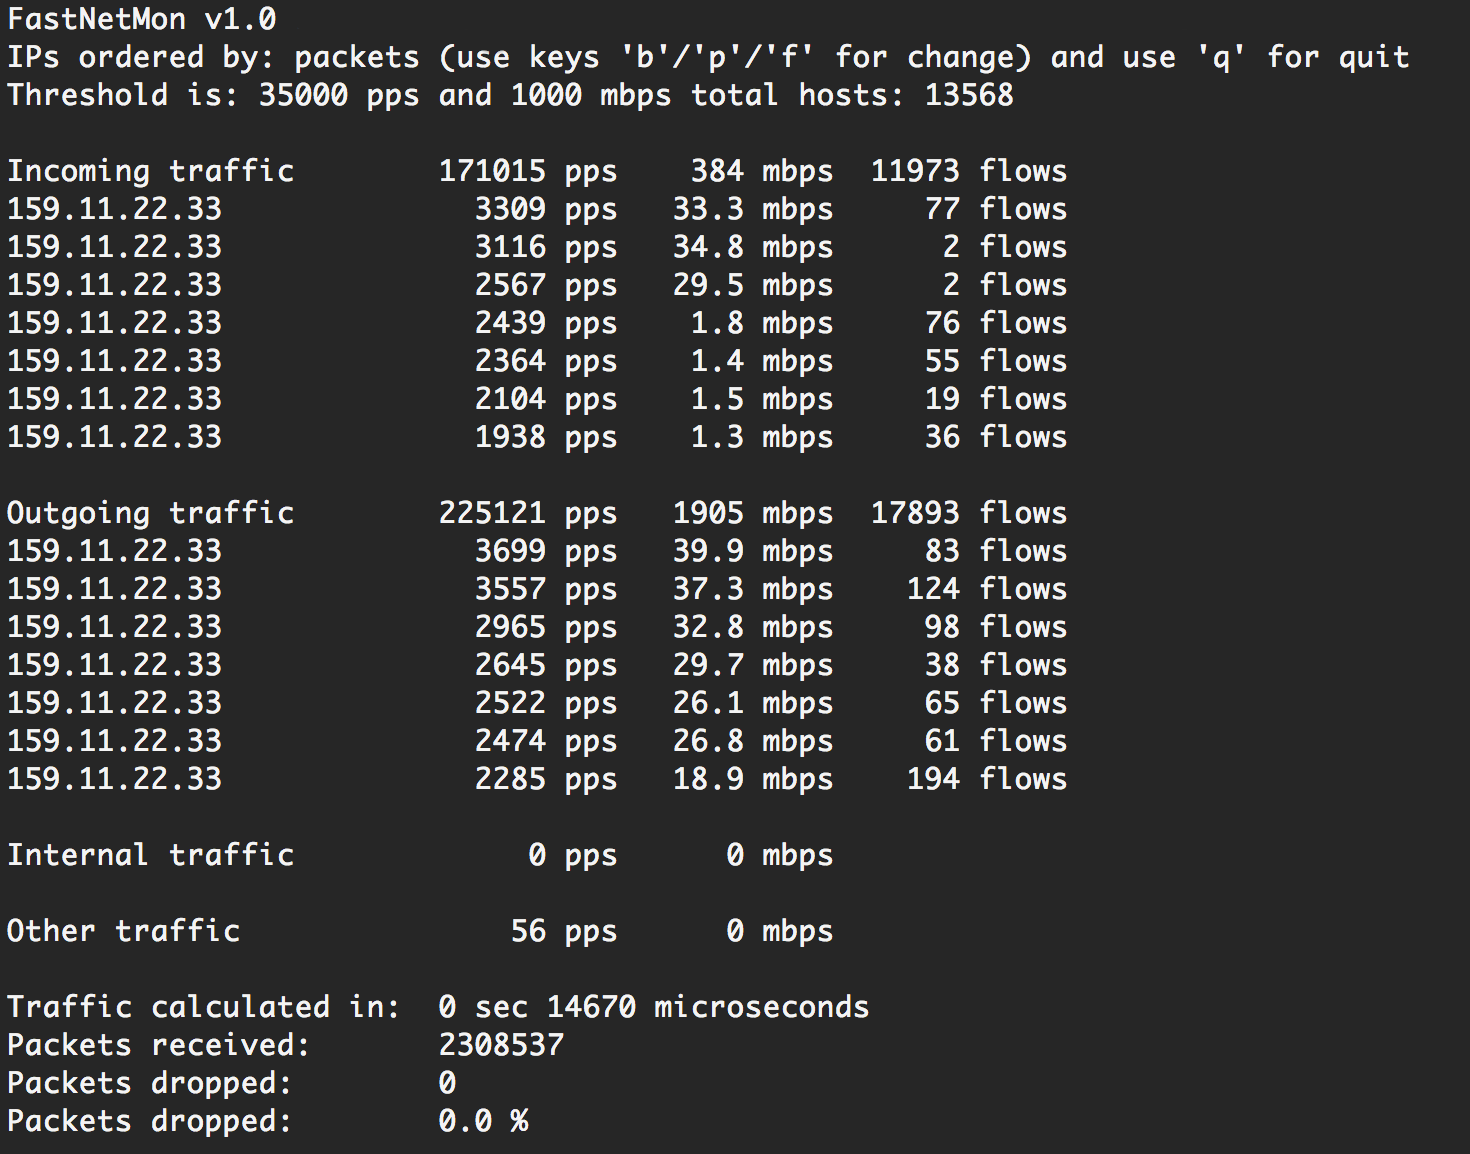
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 eshlomo1/microsoft-sentinel-secops
SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 datadog/hash
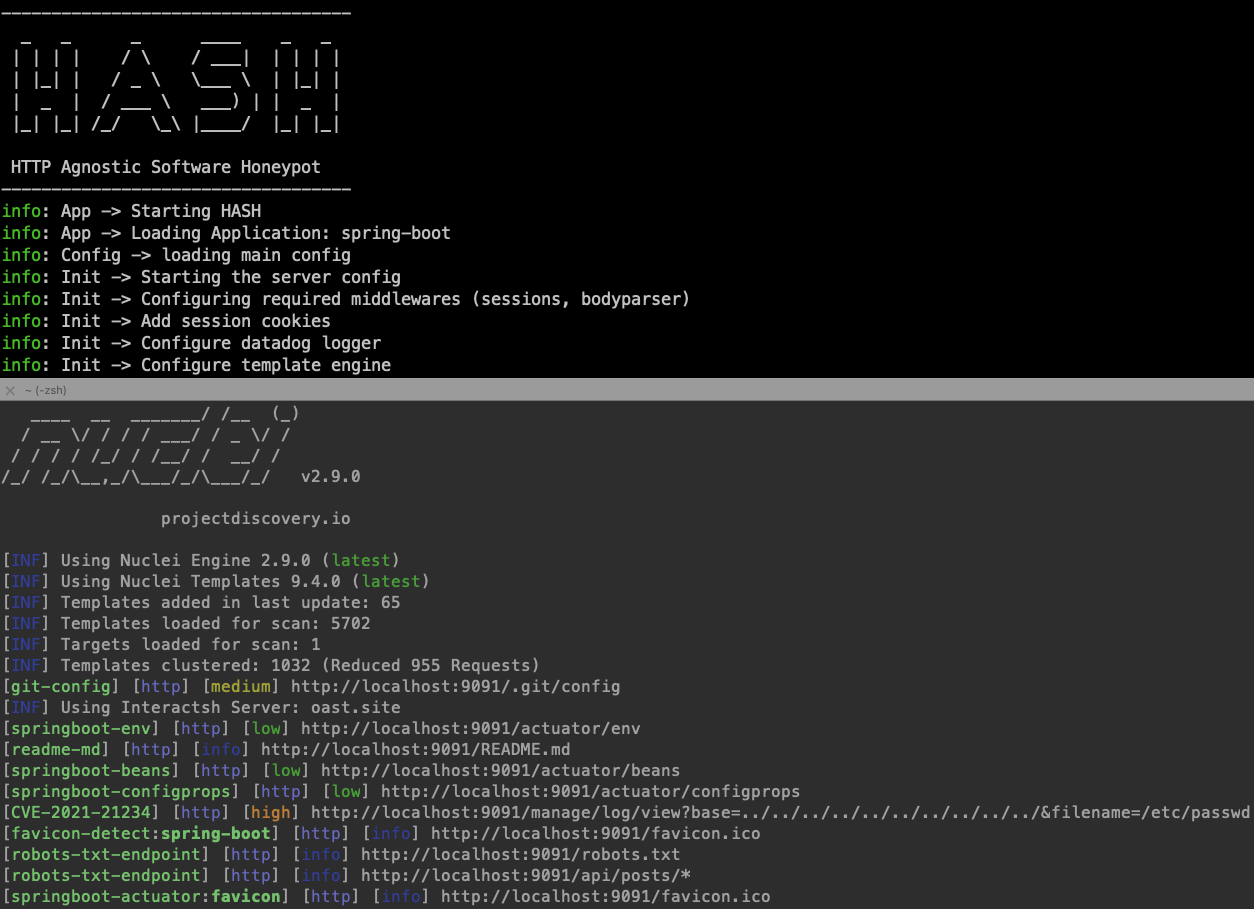
YAML-configurable low-interactive honeypot framework for deploying HTTP/HTTPS-based deception servers with built-in honeytraps and Datadog log…
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 cyberbibs/soc274---palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400-
Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…
 0x4d31/awesome-threat-detection
Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…
 pisut4152/sigma-rule-for-cve-2021-22005-scanning-activity
Sigma rule for detecting scanning activity targeting CVE-2021-22005, enabling threat detection and log-based intrusion analysis.
 al0ne/cloud-audit
Automated cloud security auditing tool that detects AK/SK credential misuse by periodically auditing cloud platform logs using anomaly detection,…