
androidqf
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
286
mvt-project/androidqfandroidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 flythenimbus/bramble
Local-first password manager with direct device-to-device sync
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 deepfield/public-research
DDoS botnet research and indicators of compromise from Nokia Deepfield ERT
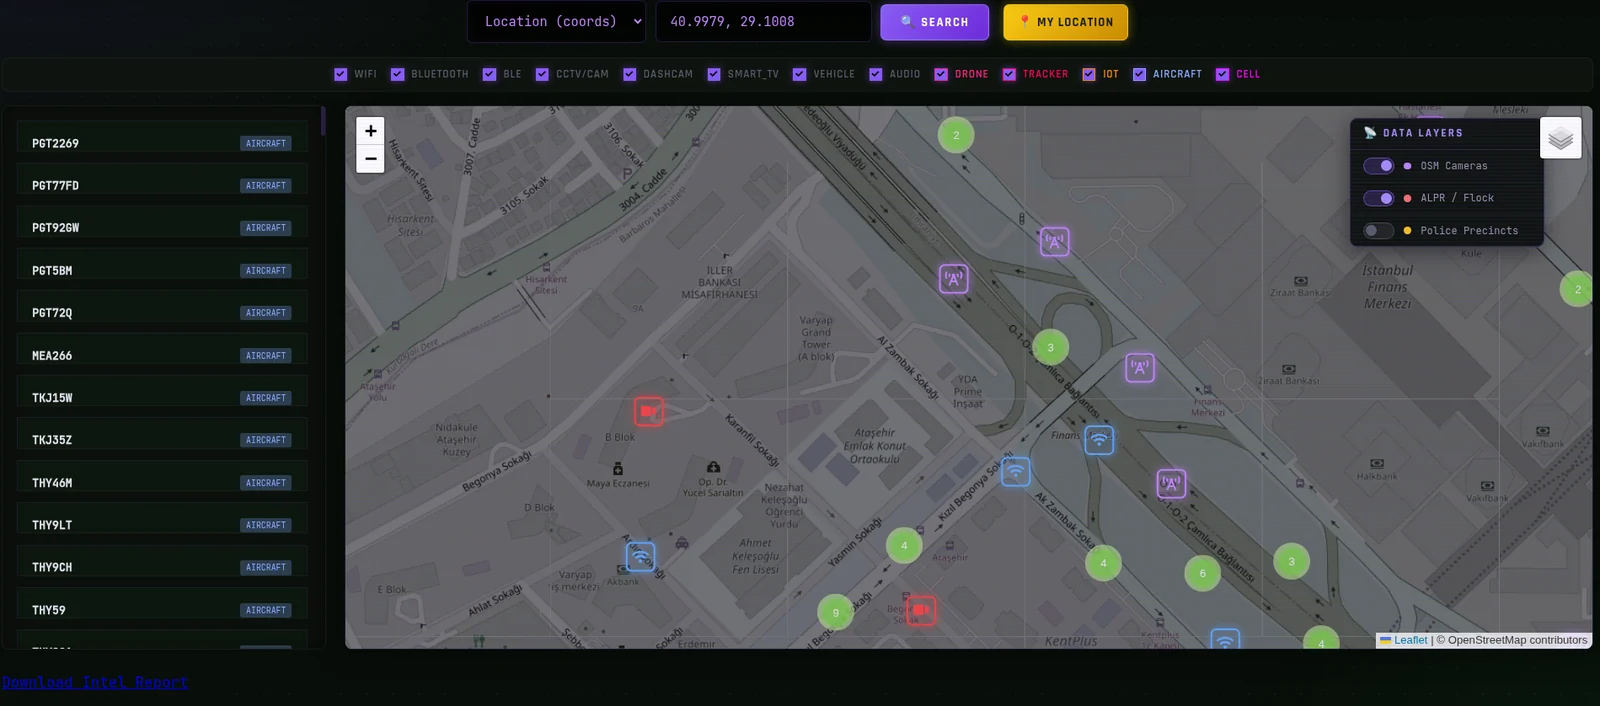 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
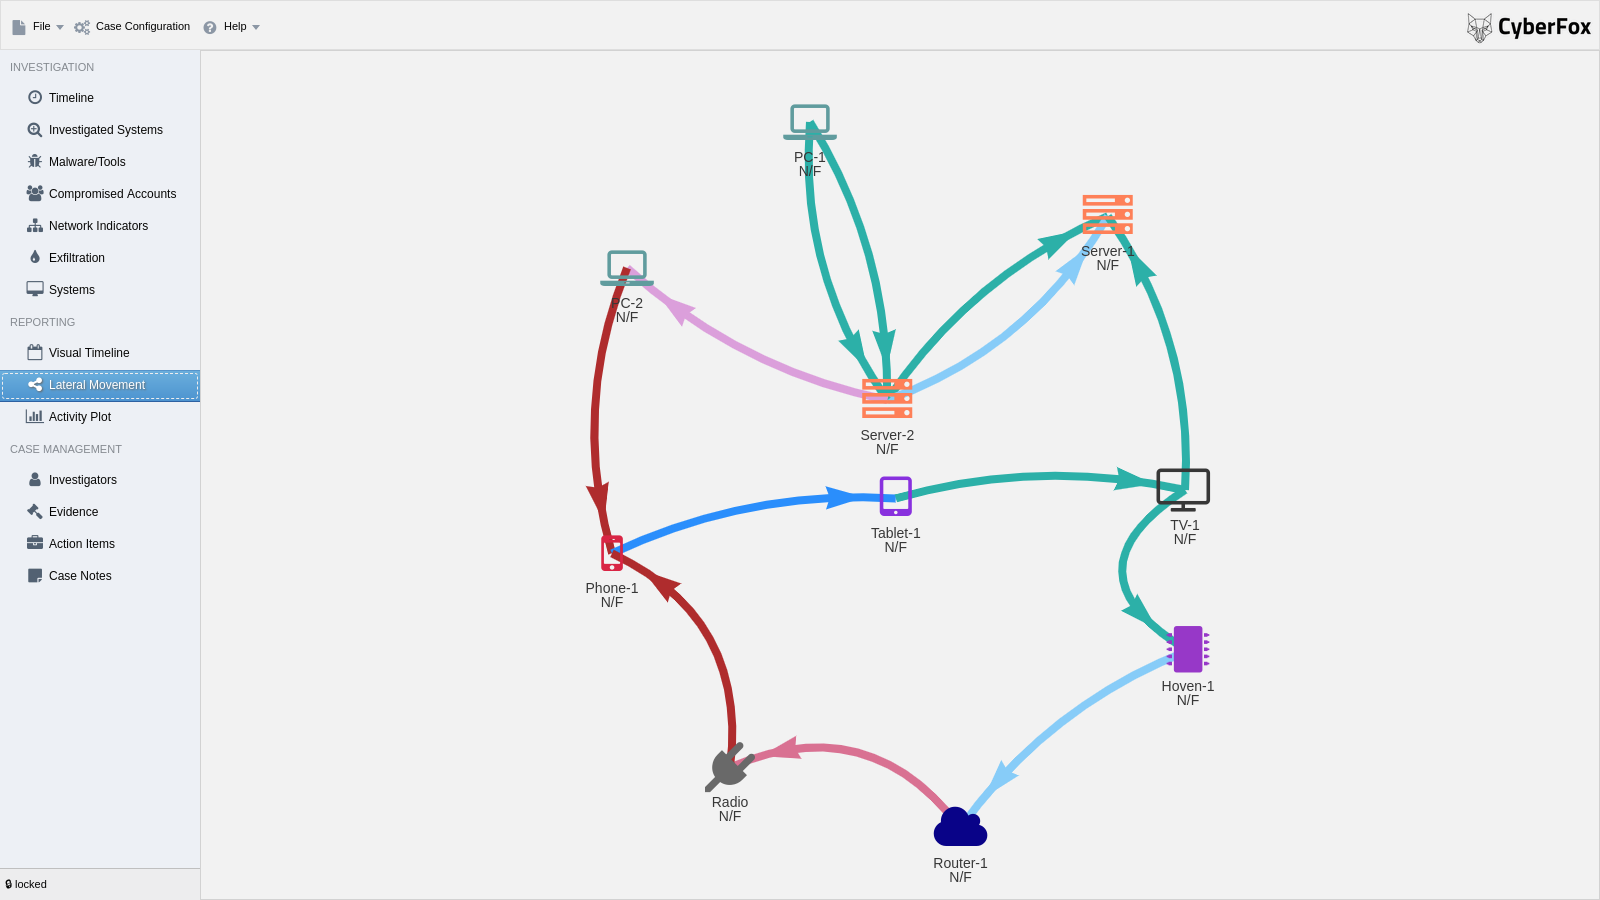 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
 tom0li/collection-document
Collection of quality safety articles. Awesome articles.
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
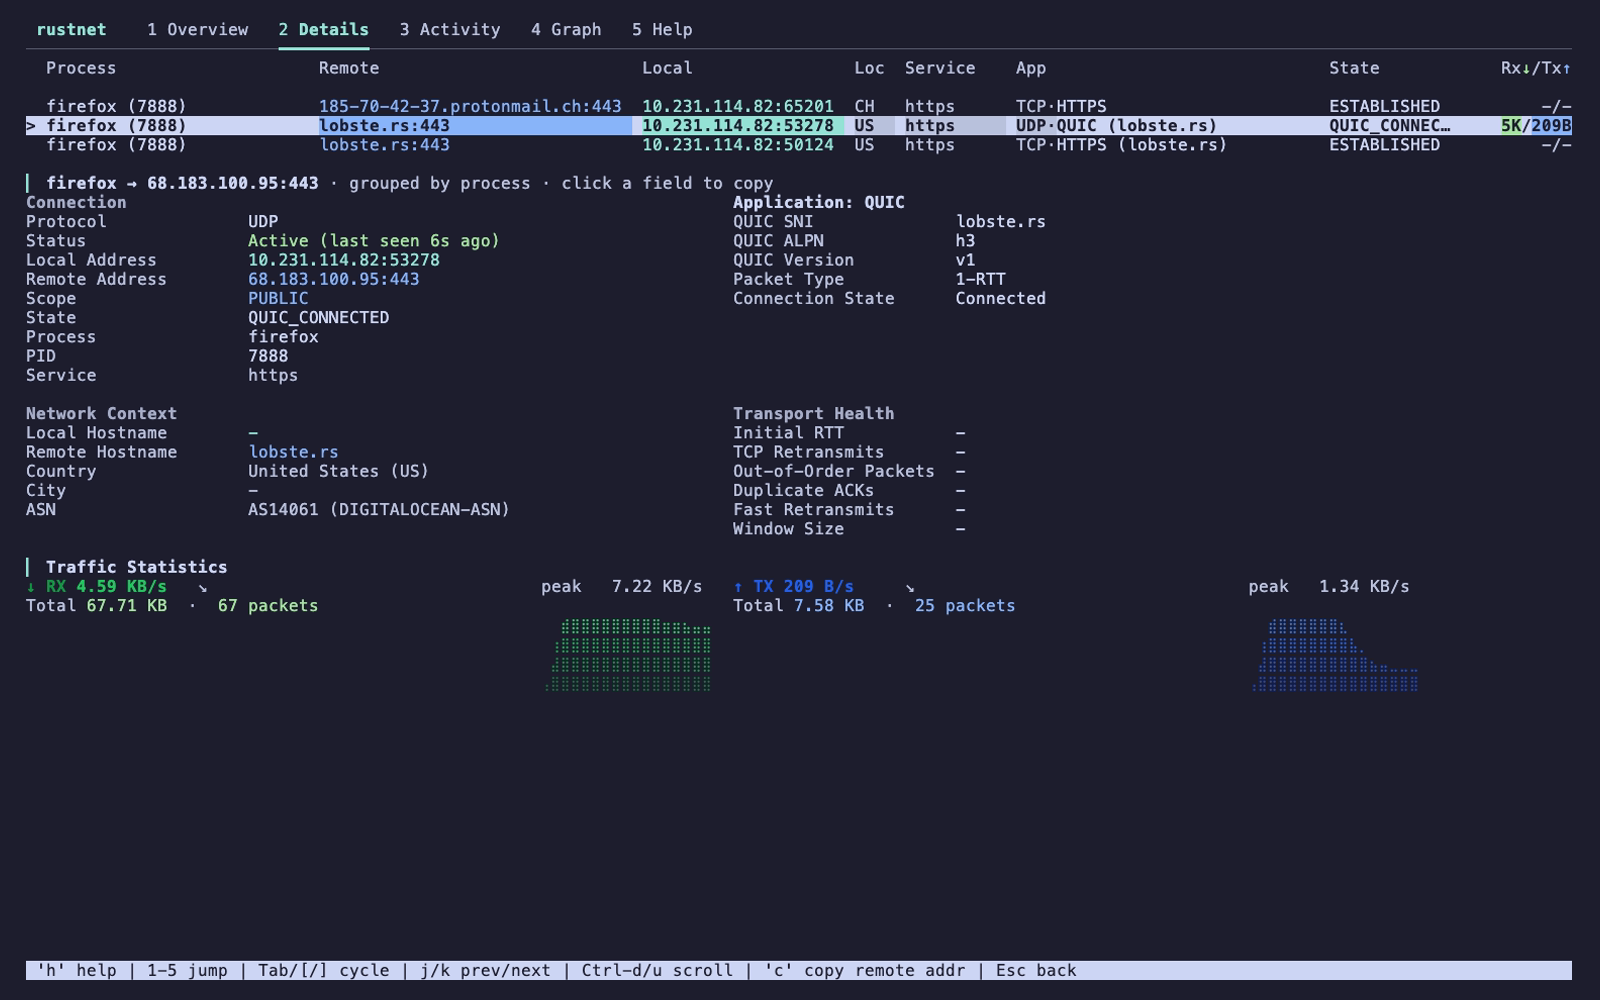 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
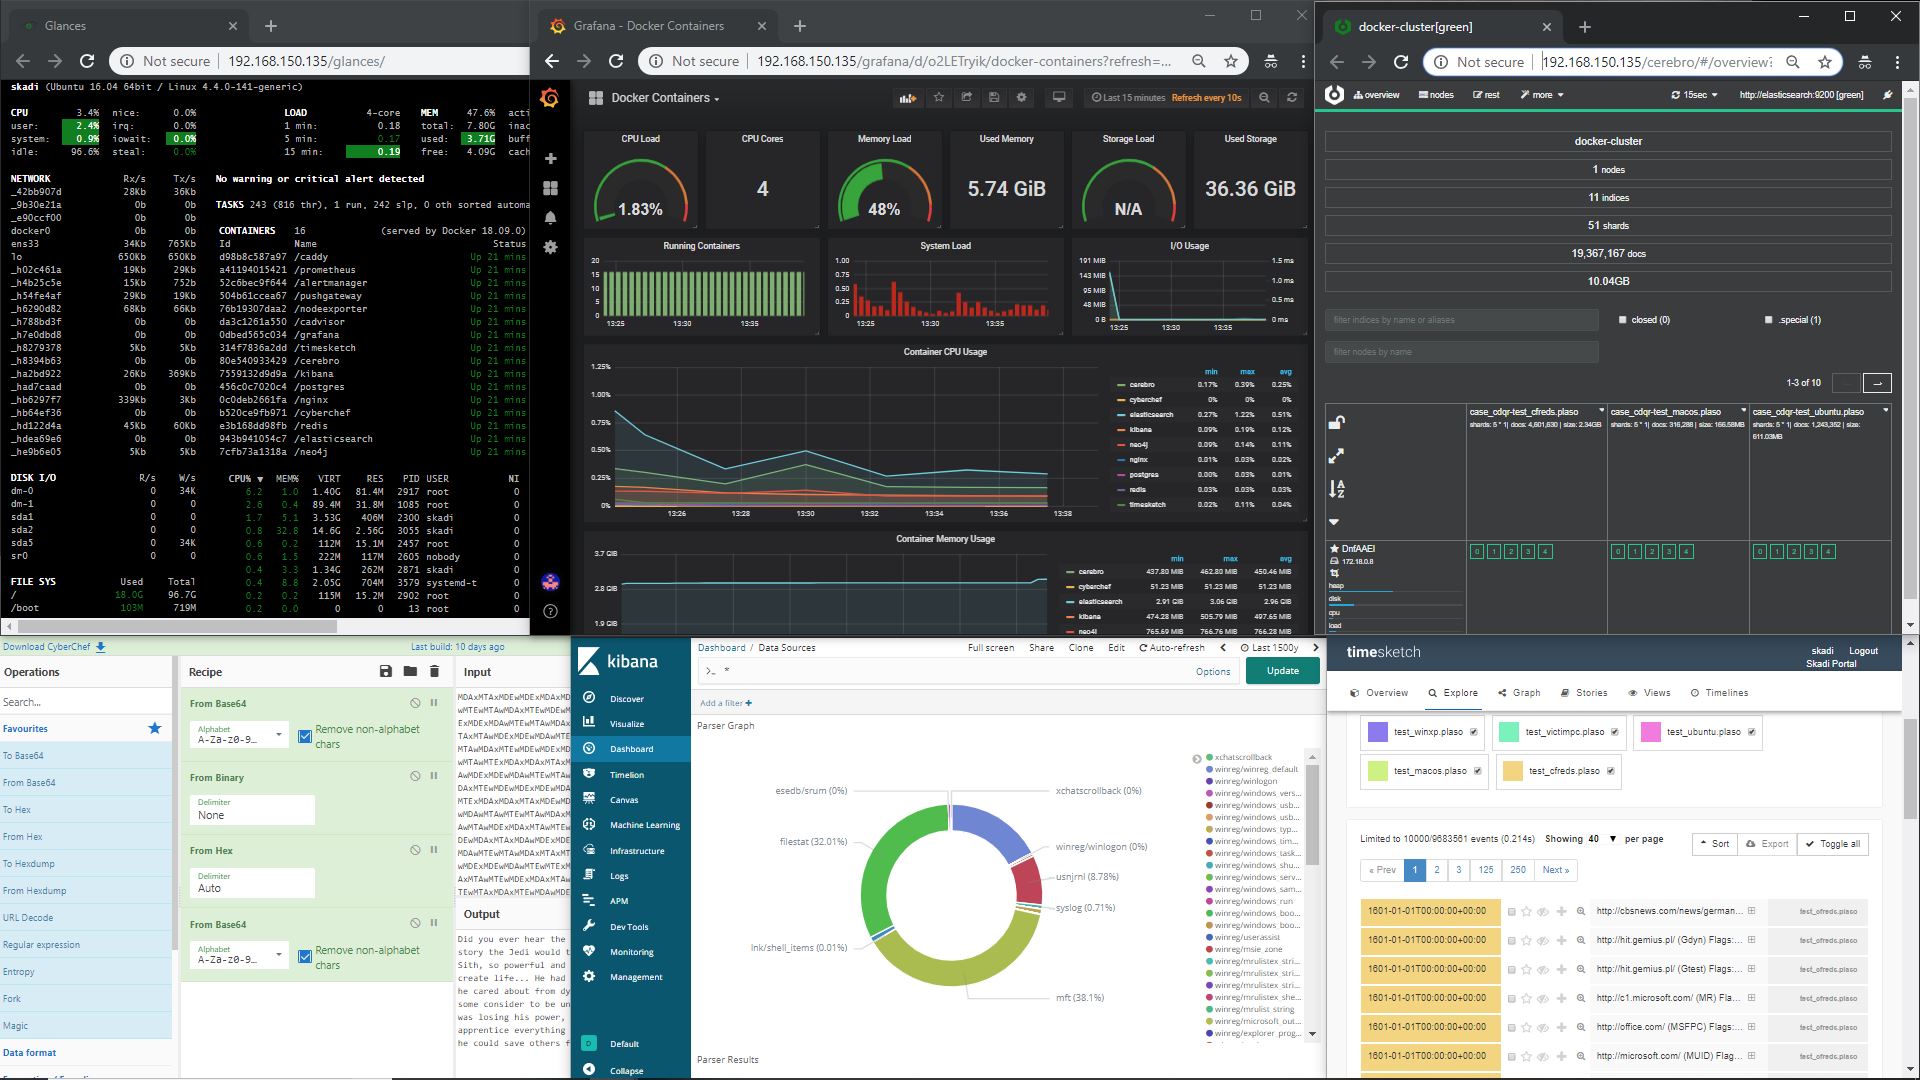 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 adityabhatt3010/cve-2025-8088-winrar-zero-day-path-traversal
An engaging walkthrough on uncovering, patching, and securing the WinRAR CVE-2025-8088 with a hands-on hacker’s twist.

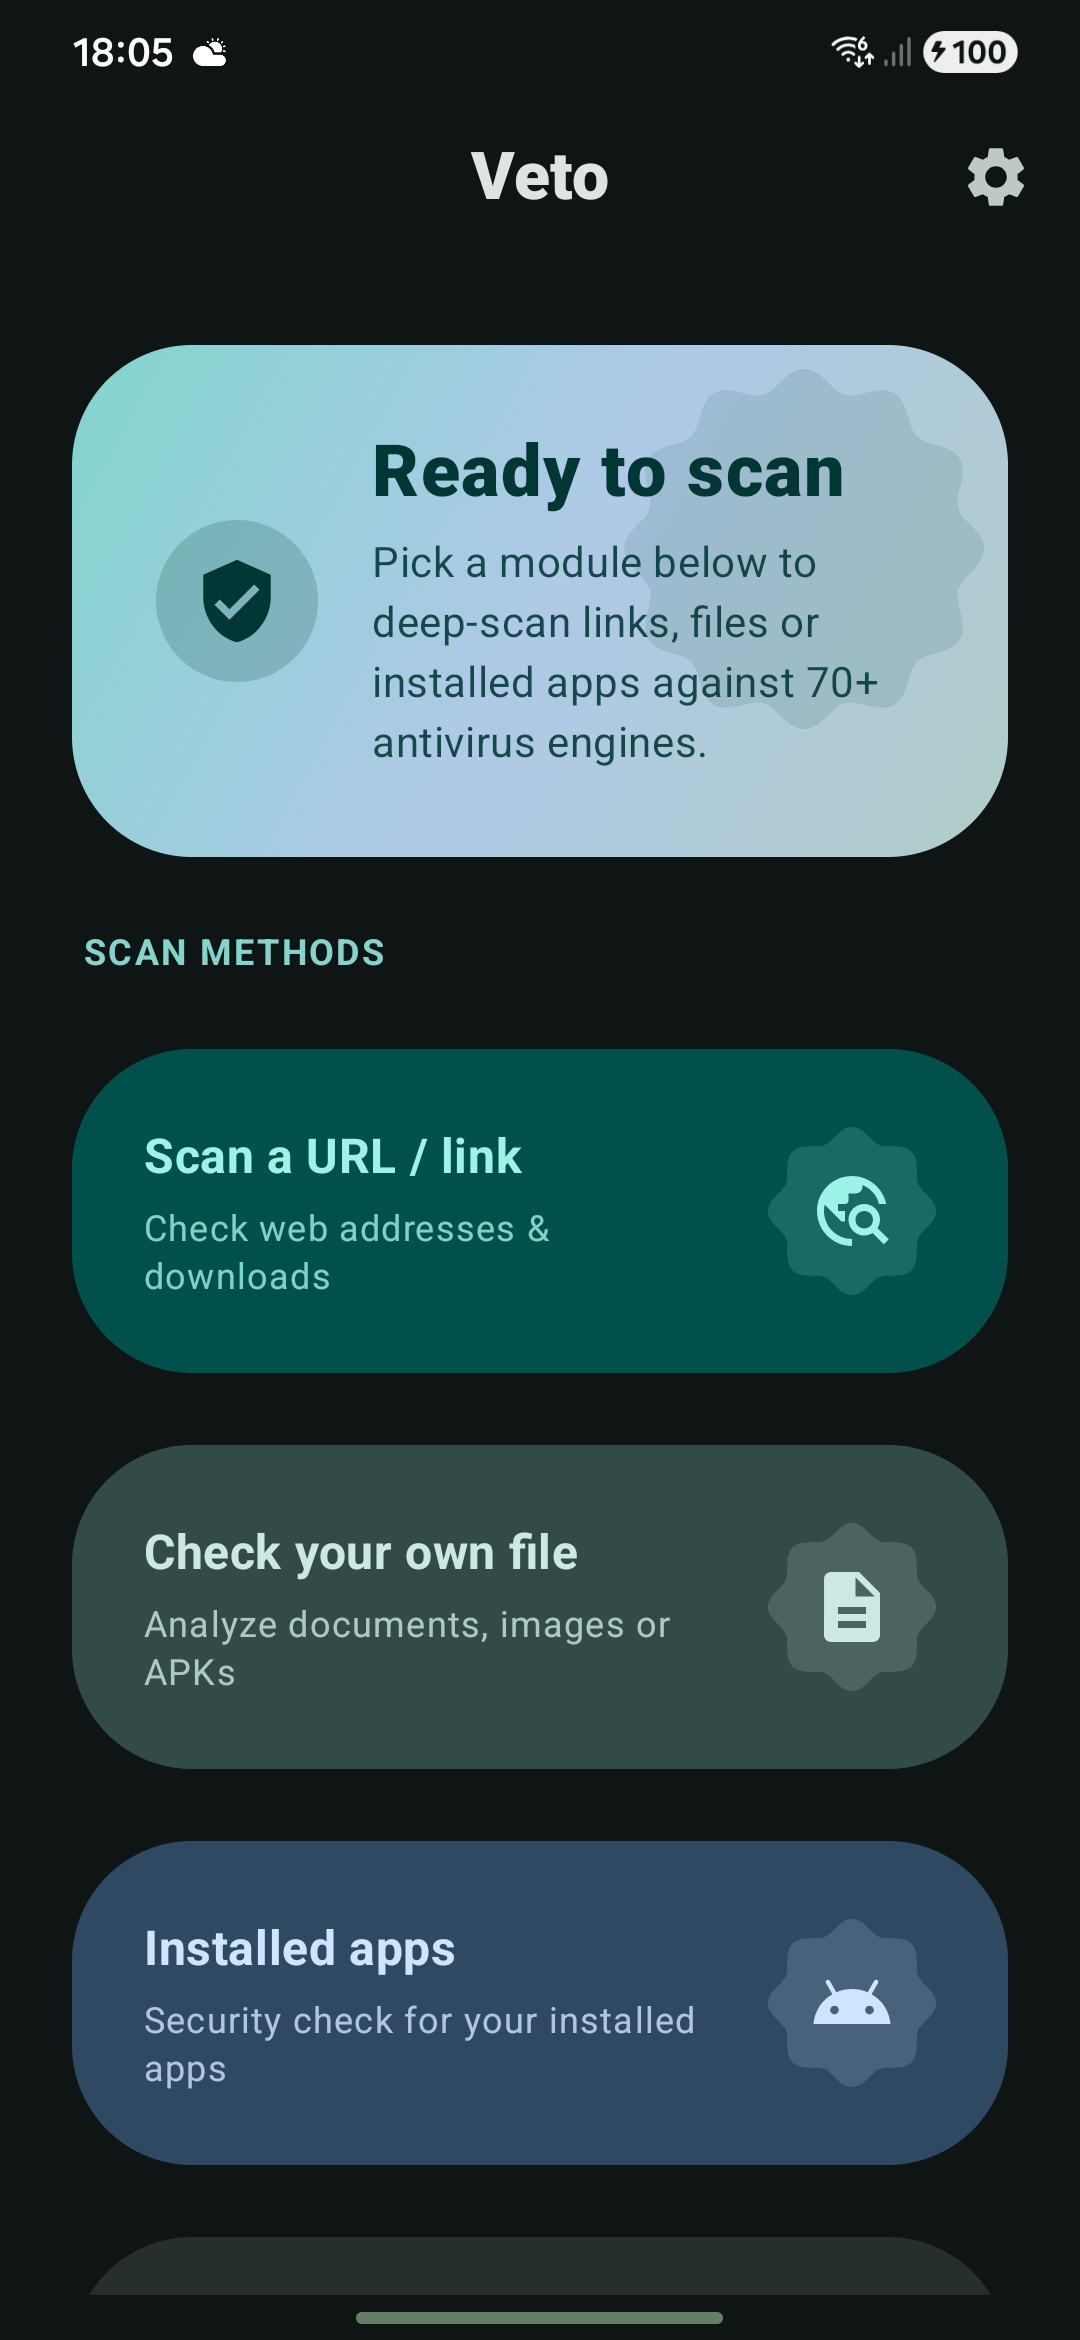 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…