pulledpork
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
configuration-auditingintrusion-detectionnetwork-security+2
4405 years ago
shirkdog/pulledporkPulled Pork for Snort and Suricata rule management (from Google code)
 ecstatic-nobel/osweep
Don't Just Search OSINT. Sweep It.

 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
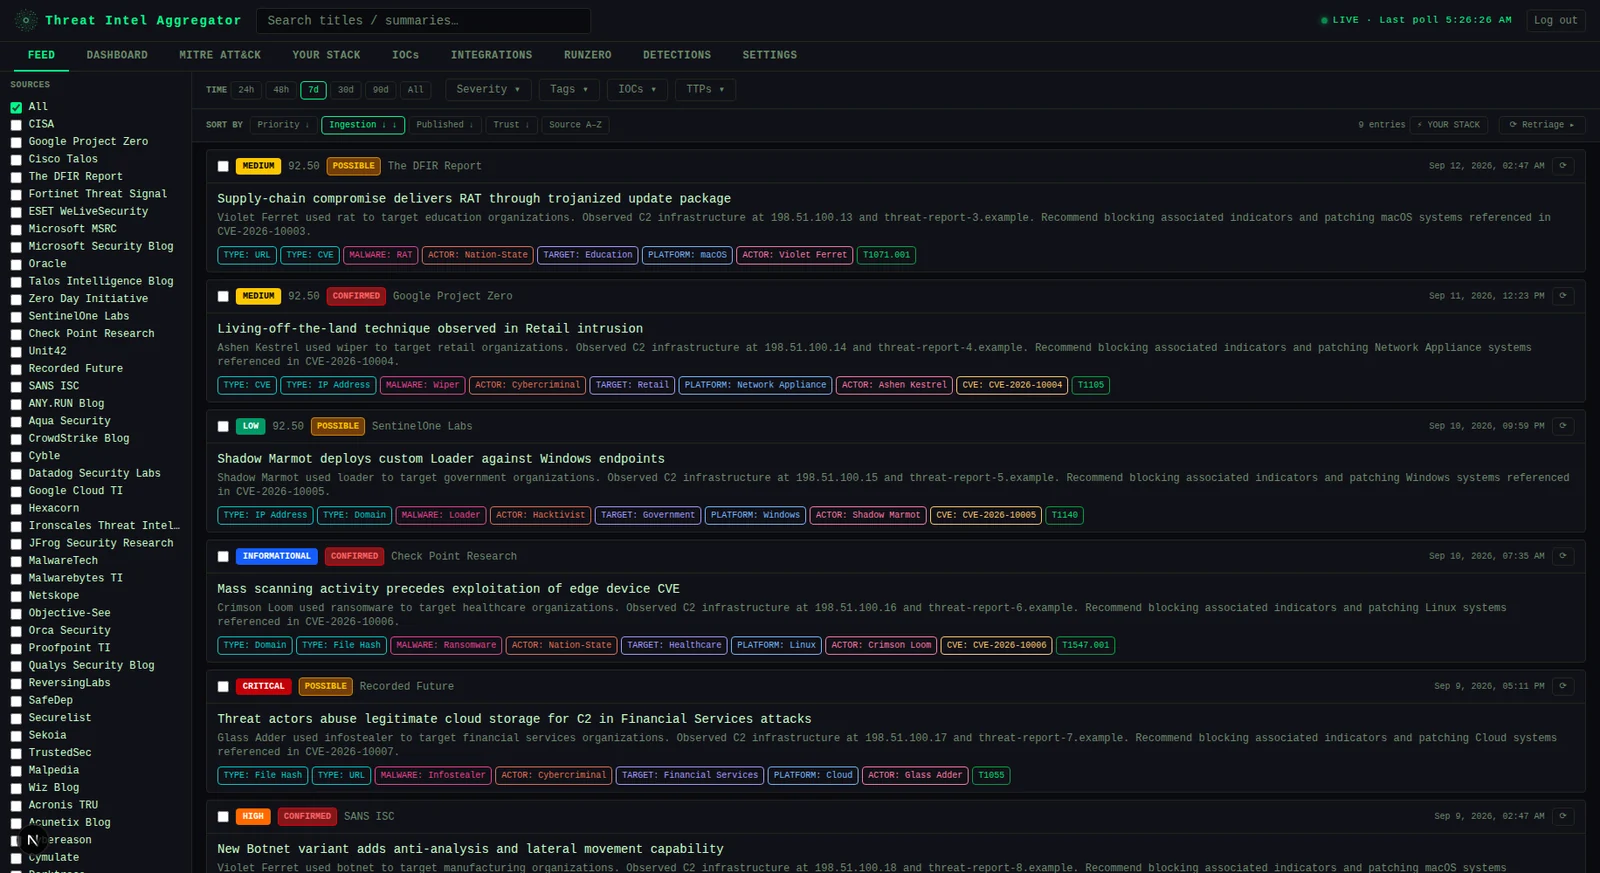 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 patrowl/patrowlhears
PatrowlHears - Vulnerability Intelligence Center / Exploits
 hurricanelabs/machinae
Automated security intelligence collector that queries public feeds and APIs for threat data on IPs, domains, URLs, hashes, and SSL fingerprints,…
 eclecticiq/opentaxii
TAXII server implementation in Python from EclecticIQ
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
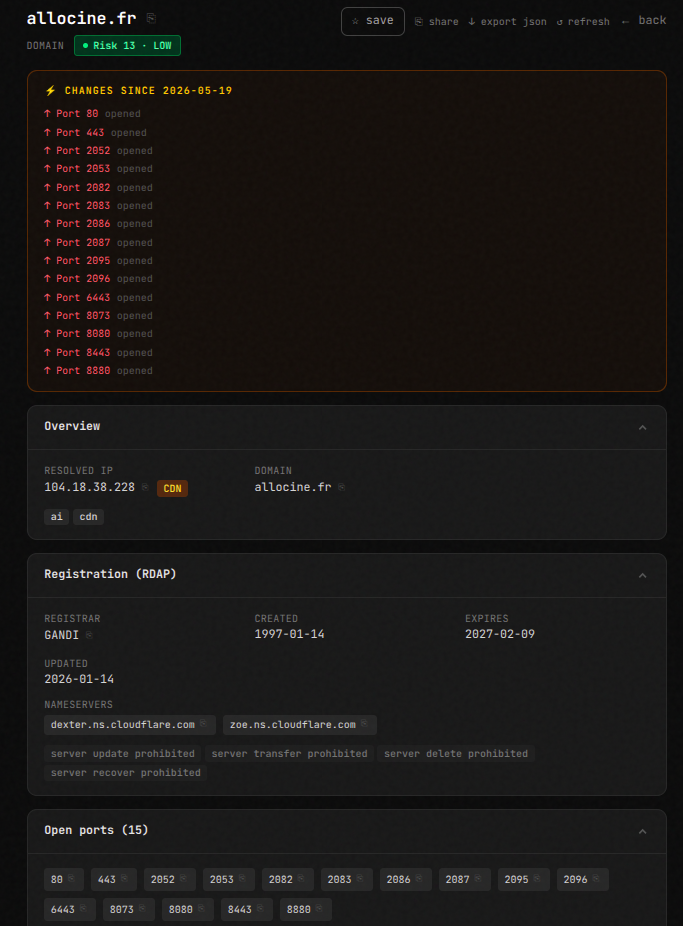 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
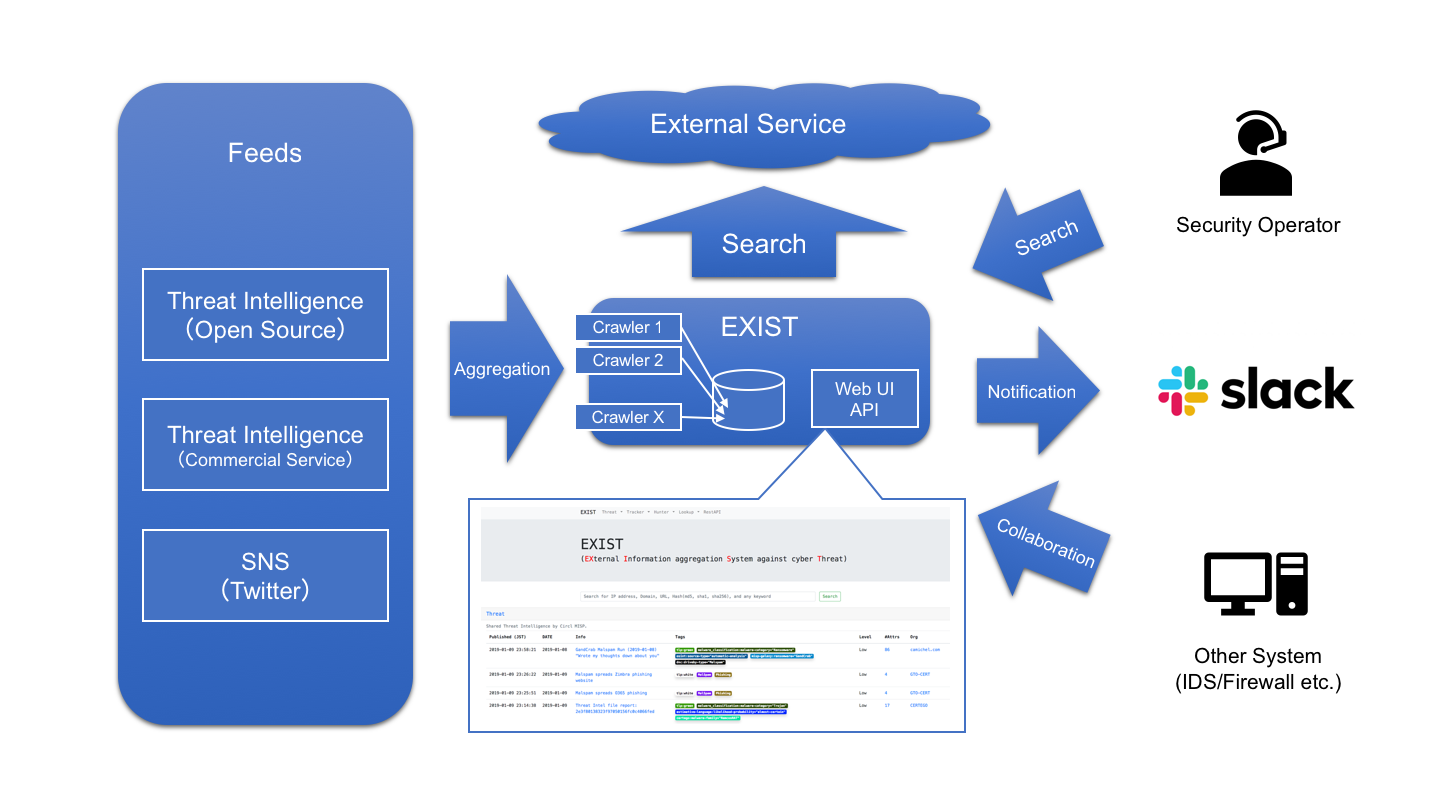 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
 ransomlook/ransomlook
Yet another Ransomware gang tracker
 guardicode/cve-2021-44228_iocs
Curated collection of public Indicators of Compromise (IoCs) for the Log4j vulnerability (CVE-2021-44228), aggregated from multiple sources for…
 olafhartong/attackdatamap
A datasource assessment on an event level to show potential coverage or the MITRE ATT&CK framework