

h4cker
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
ai-securityctfcurated-resources+8
29.9k
the-art-of-hacking/h4ckerCurated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
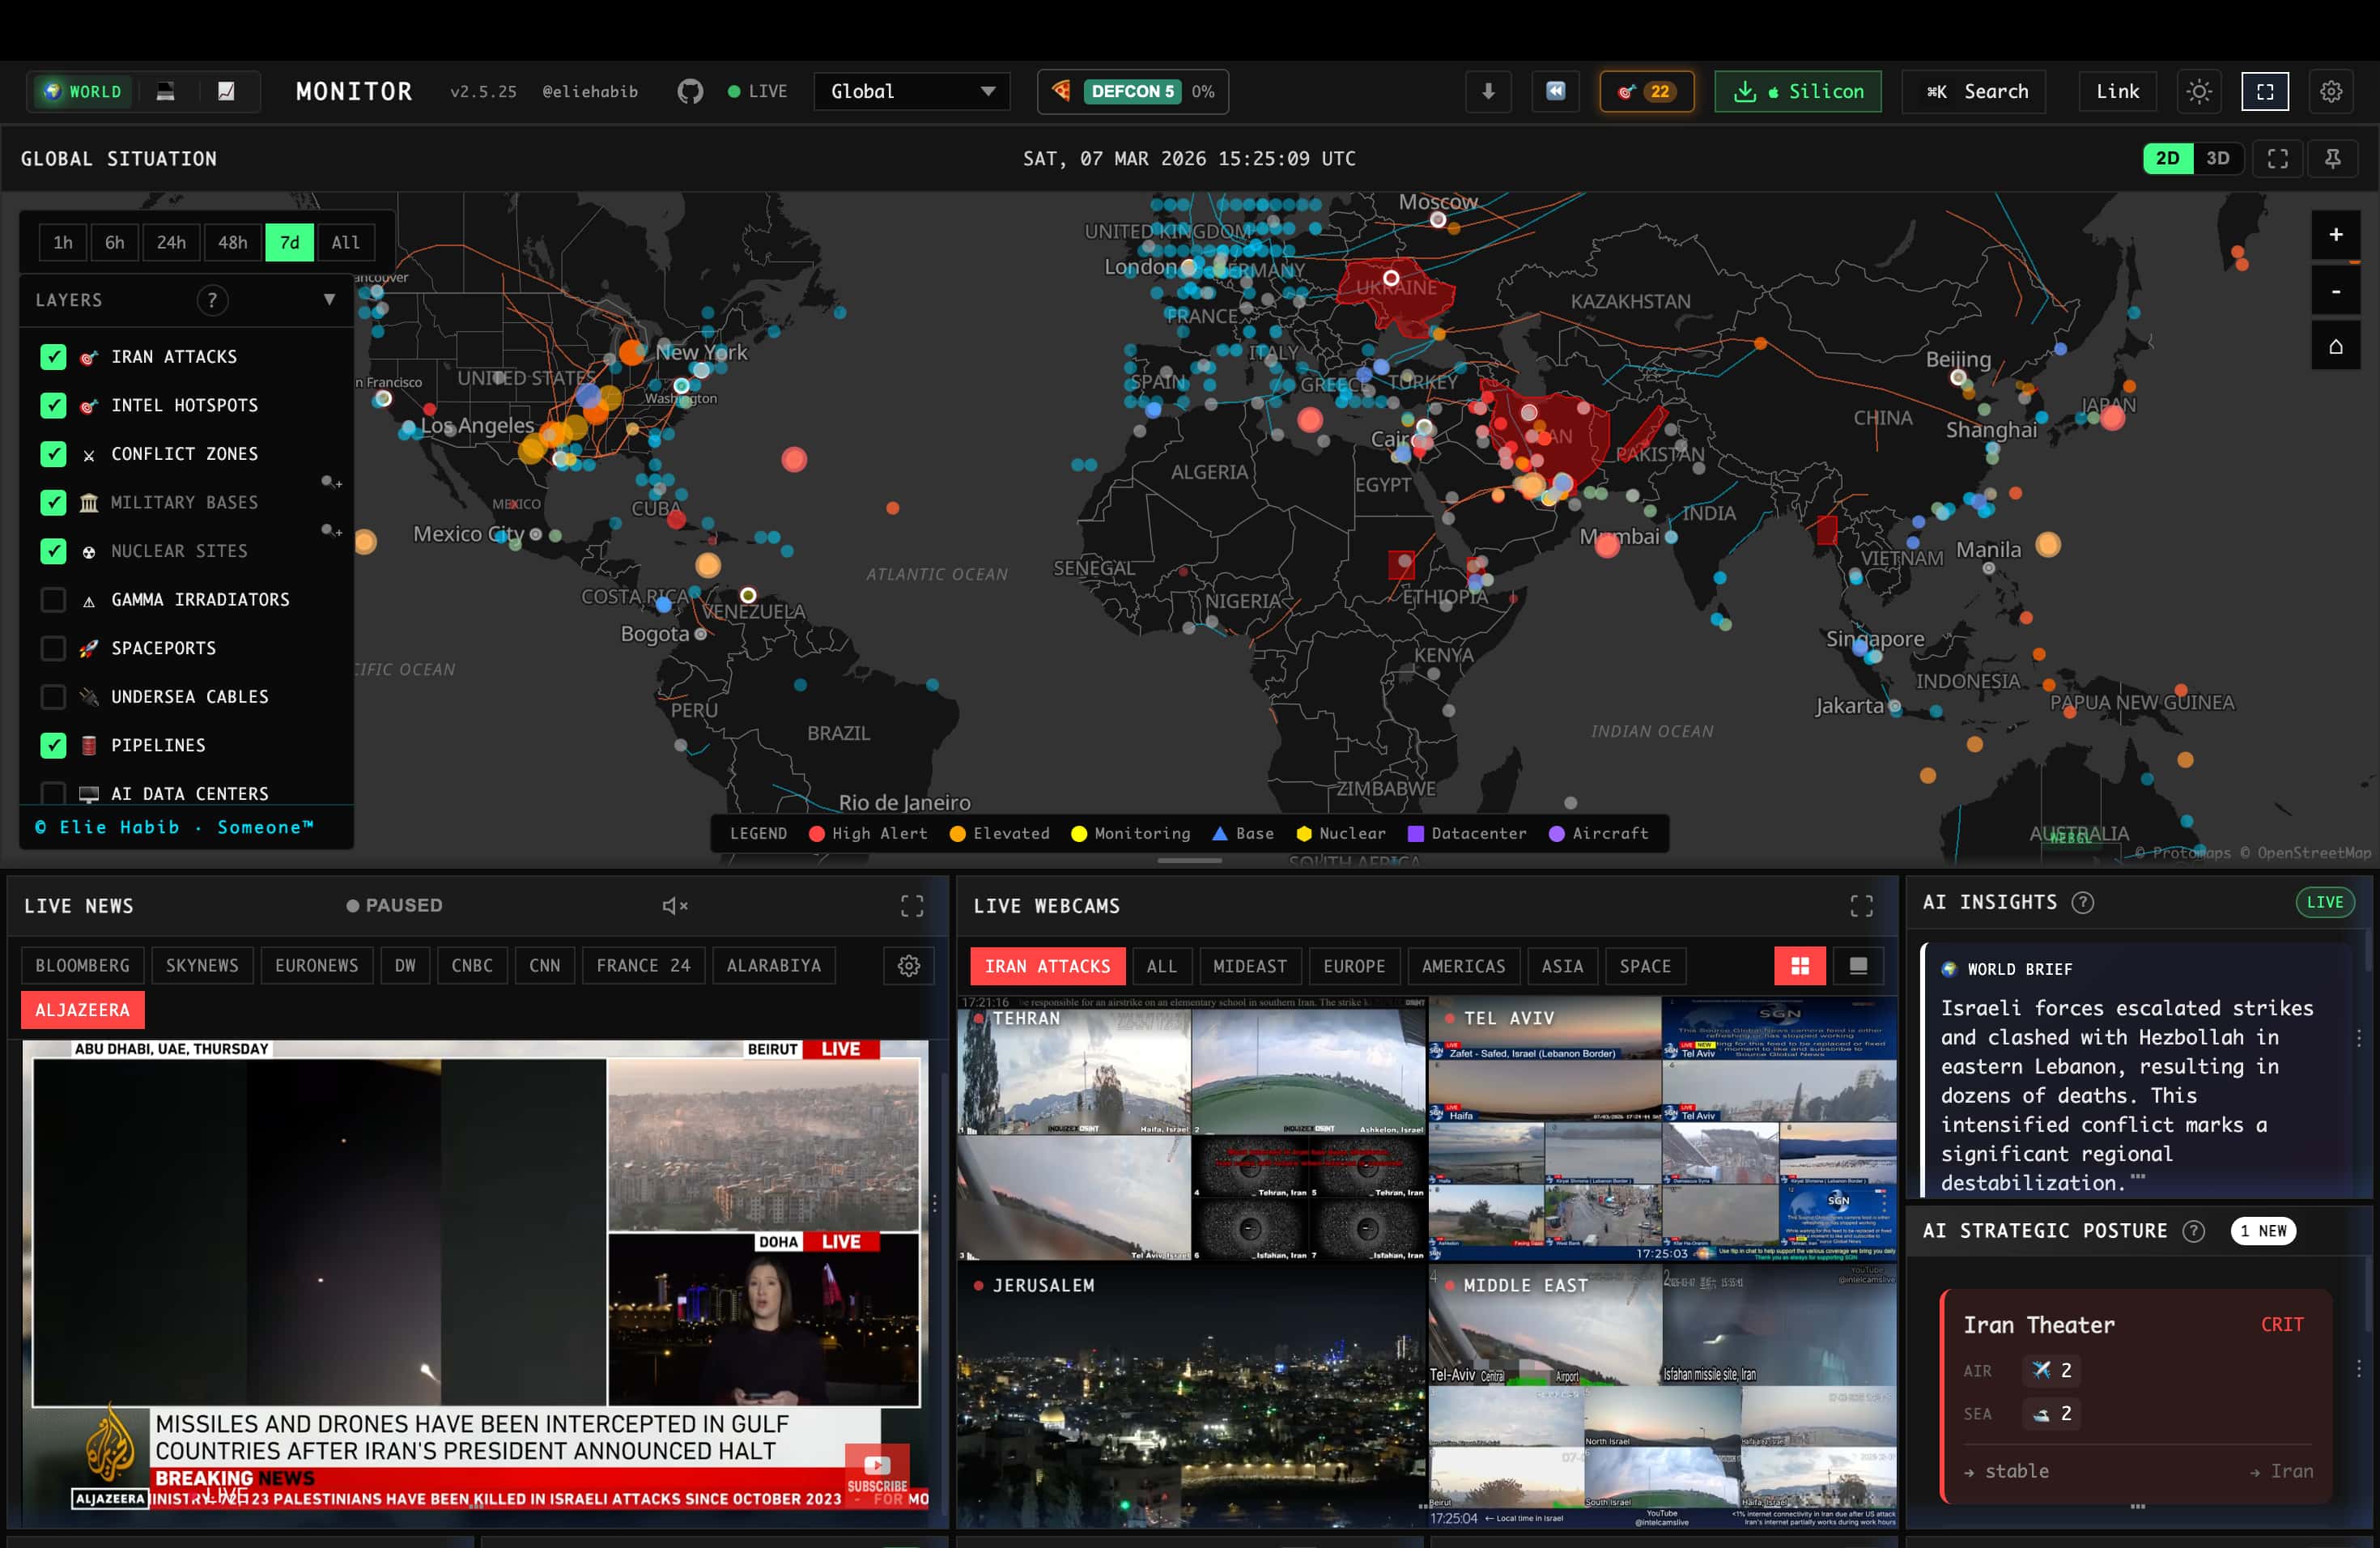 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
 fastfire/deepdarkcti
Collection of Cyber Threat Intelligence sources from the deep and dark web
 hslatman/awesome-threat-intelligence
Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 neo23x0/signature-base
YARA signature and IOC database for my scanners and tools
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 gendigitalinc/ioc
Threat Intel IoCs + bits and pieces of dark matter. Published by Gen Threat Labs.
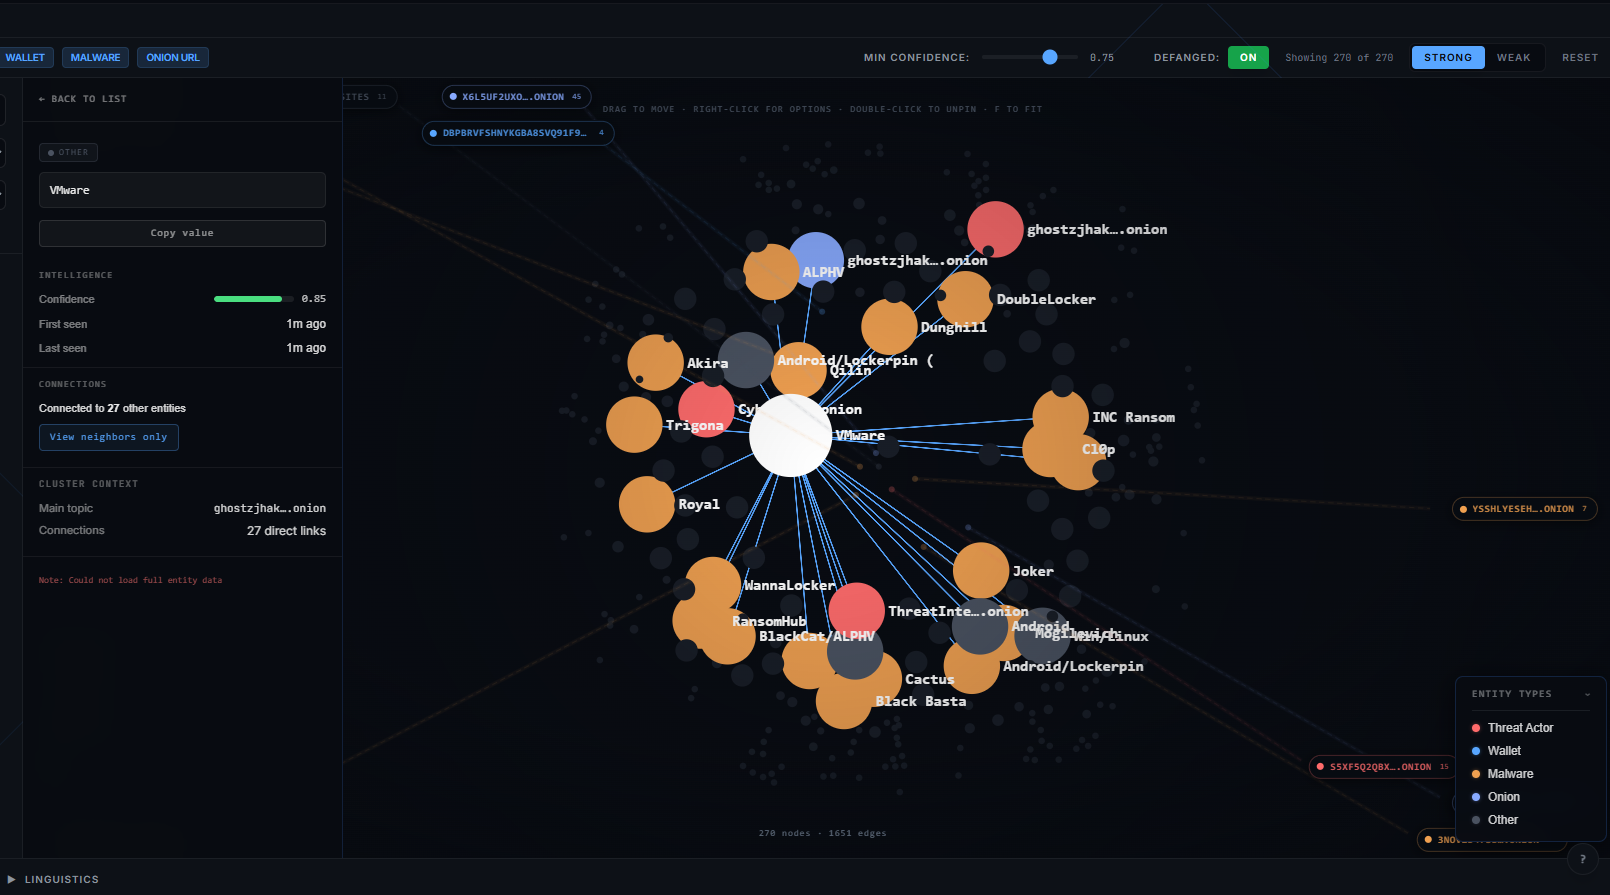 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…