
enterpriseattack
A lightweight Python module to interact with the [MITRE ATT&CK®](https://attack.mitre.org/) Enterprise dataset. Built for speed with minimal…

A lightweight Python module to interact with the [MITRE ATT&CK®](https://attack.mitre.org/) Enterprise dataset. Built for speed with minimal…

IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…


Curated collection of public Indicators of Compromise (IoCs) for the Log4j vulnerability (CVE-2021-44228), aggregated from multiple sources for…

Free, offline SOC Analyst Hub for Tier 1 — IR checklists, alert triage playbooks, threat hunting queries & analyst onboarding. Single HTML file, no…

A collection of IOCs for CVE-2021-44228 also known as Log4Shell

Collects vulnerability and advisory data from multiple public security feeds and stores it in a parsable, structured format for downstream security…

Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …

Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…

Graph platform for Detection and Response

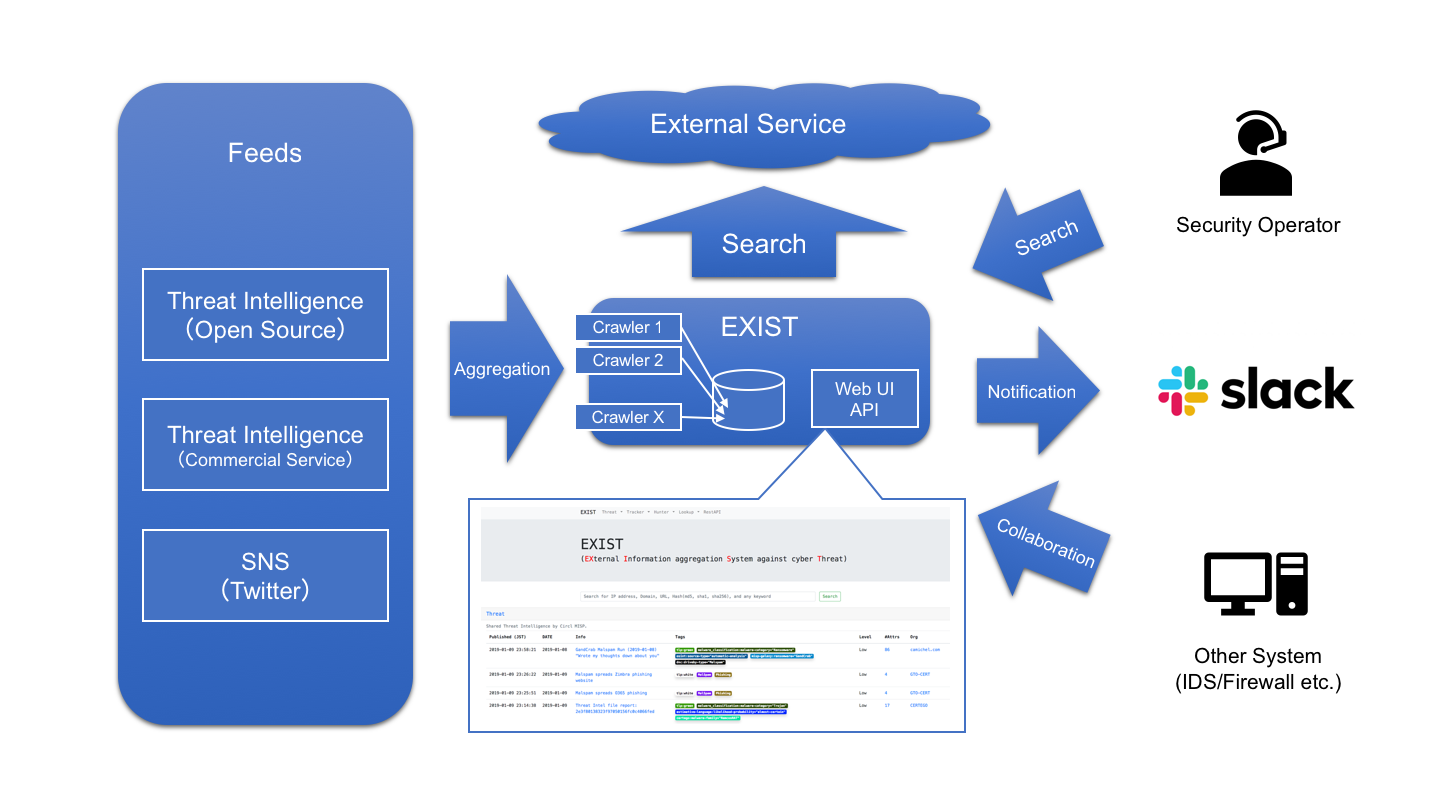
EXIST is a web application for aggregating and analyzing cyber threat intelligence.

The GOSINT framework is a project used for collecting, processing, and exporting high quality indicators of compromise (IOCs).

Look for un-sinkholed C&C IPs in your Bro logs (from Bambanek Consulting C&C master list)

Live Feed of C2 servers, tools, and botnets