
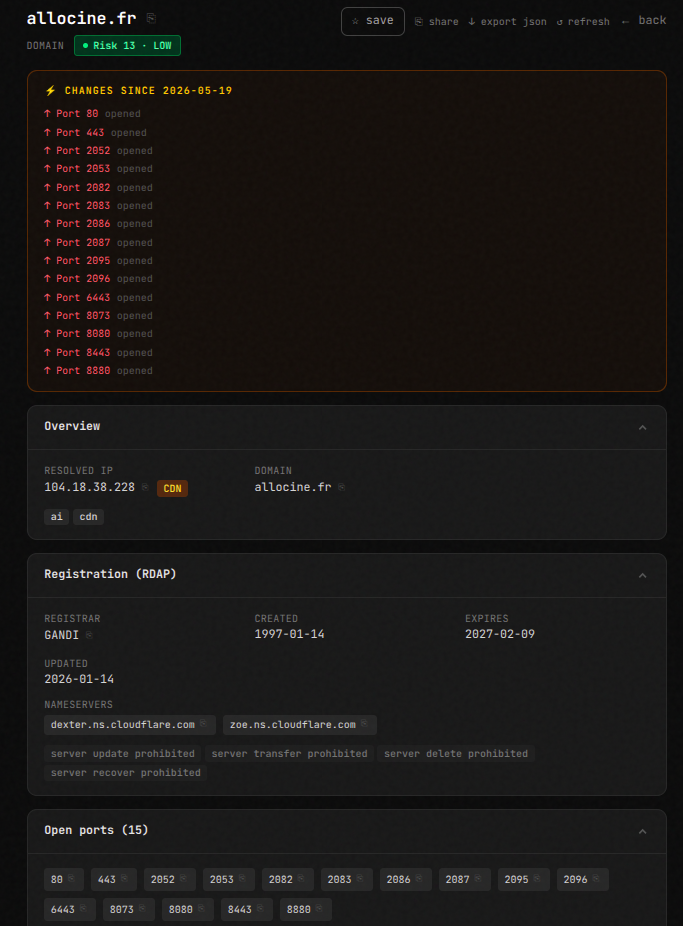
SeekYou
 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
cloud-securitycrawlerdns-analysis+9
teycir/seekyouOSINT intelligence on any IP, domain, or ASN
 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds

 cross-samuel1/soc-analyst-hub
Free, offline SOC Analyst Hub for Tier 1 — IR checklists, alert triage playbooks, threat hunting queries & analyst onboarding. Single HTML file, no…
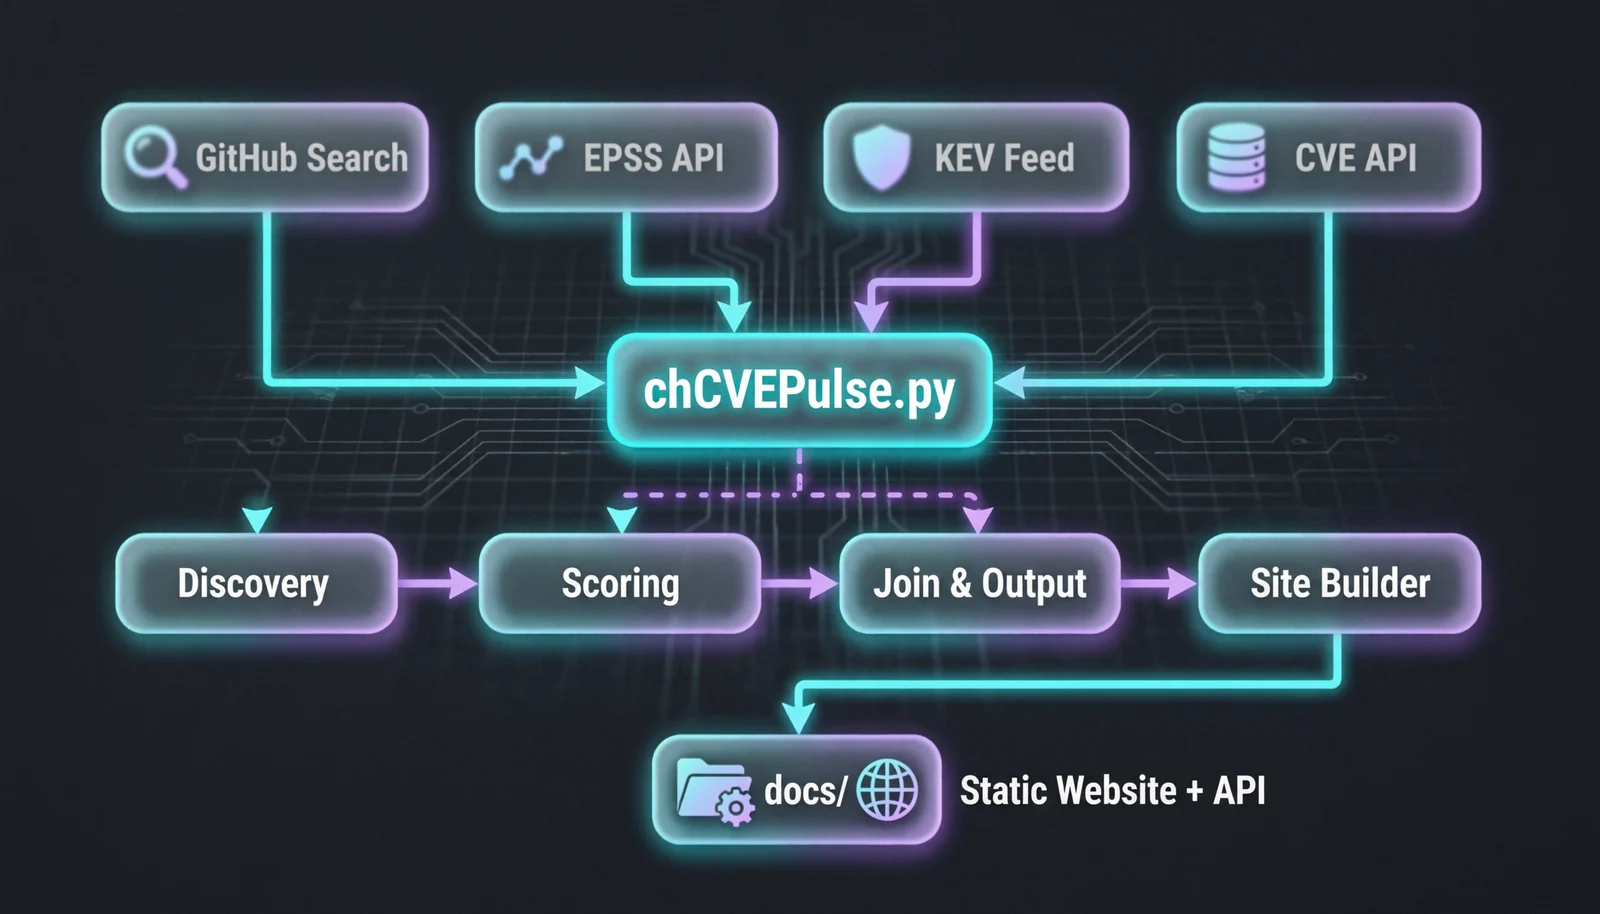 ch4120n/ch4120n-cve-pulse
Live CVE PoC (Proof-of-Concepts) Aggregator with Smart Search & Threat Intelligence
 phishdestroy/destroylist
Real-time phishing & scam domain blocklist - 205k+ curated threats, 1M+ community, free API, multiple formats

 paloaltonetworks/unit42-timely-threat-intel
A collection of files with indicators supporting social media posts from Palo Alto Network's Unit 42 team to disseminate timely threat intelligence.
 bfuzzy/auditd-attack
A Linux Auditd rule set mapped to MITRE's Attack Framework
 curated-intel/ukraine-cyber-operations
Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional…
 olafhartong/attackdatamap
A datasource assessment on an event level to show potential coverage or the MITRE ATT&CK framework
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 jpcertcc/phishurl-list
Phishing URL dataset from JPCERT/CC
 nomi-sec/nvd-database
📕NVD Database
