

awesome-lists
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
curated-resourcesdigital-forensicseducation+4
2.0k
mthcht/awesome-listsCurated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 drb-ra/c2intelfeeds
Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
 nextronsystems/iocs
Indicators of compromise from to analysis and research by Nextron Threat Research team
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
 threatlabz/iocs
This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports
 doctorwebltd/malware-iocs
Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
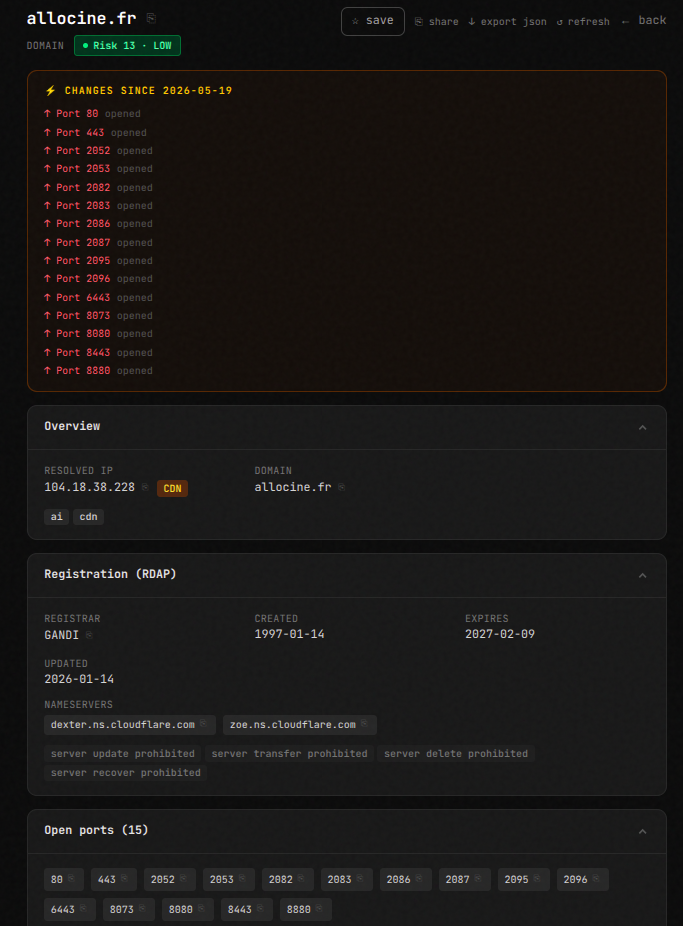 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 adham504/sentinelthread-forensics
High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…