

ThreatLens
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
defensive-toolsincident-responseinformation-gathering+7
25
abdaullahag/threatlensPython CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
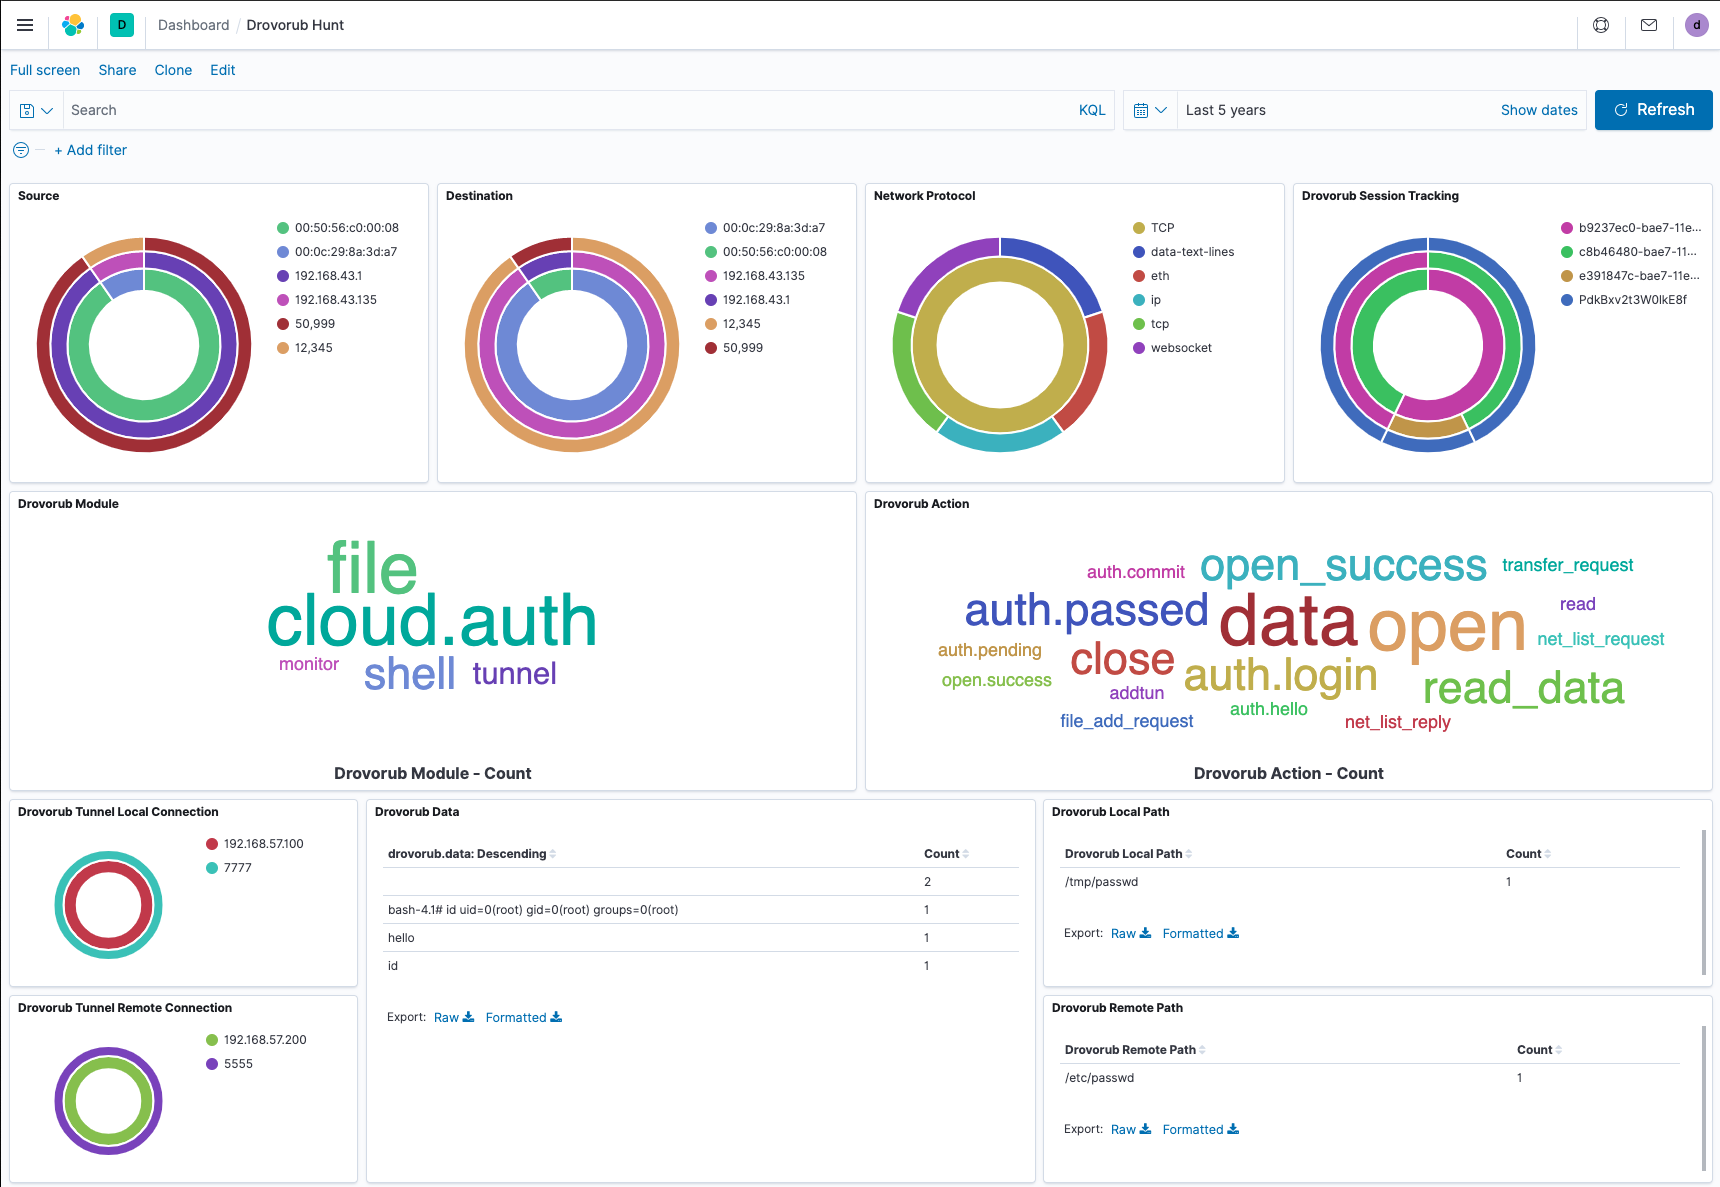 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2

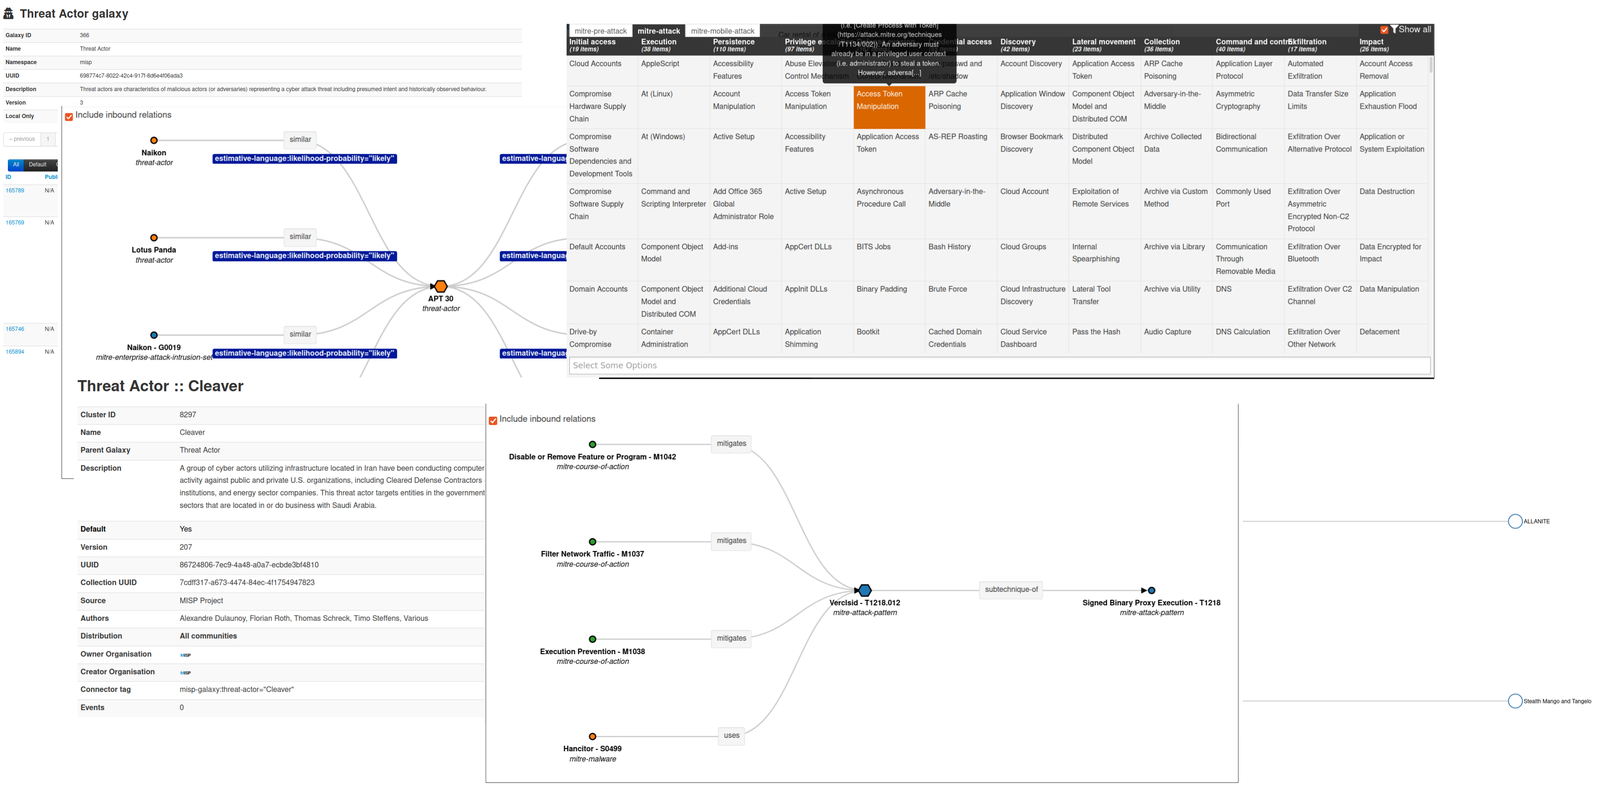 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
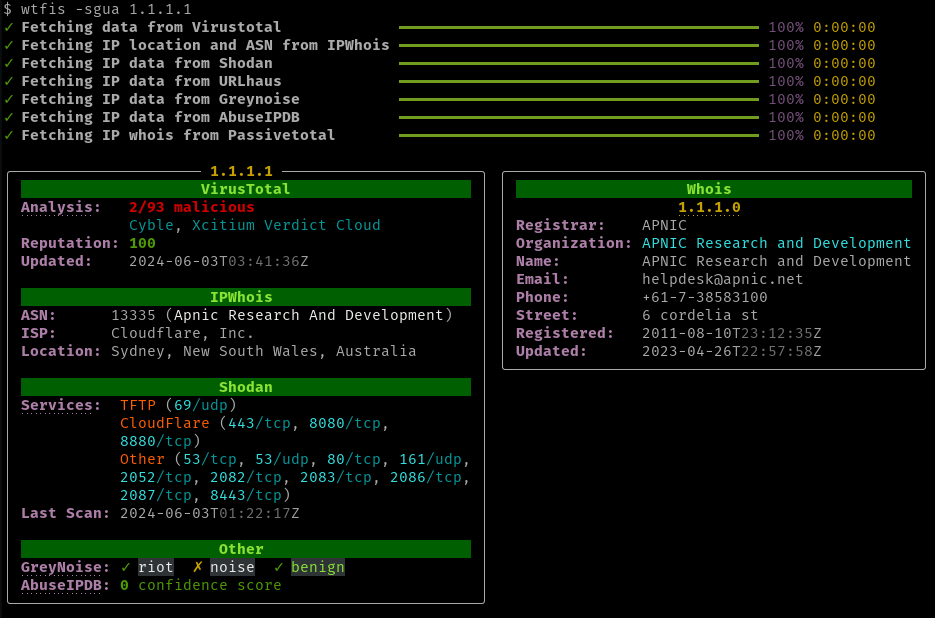 pirxthepilot/wtfis
Passive hostname, domain and IP lookup tool for non-robots
 1an0rmus/tekdefense-automater
Automater - IP URL and MD5 OSINT Analysis