

Exploit-Index
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
curated-resourcesexploitationinformation-gathering+8
97
securewithumer/exploit-indexZero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
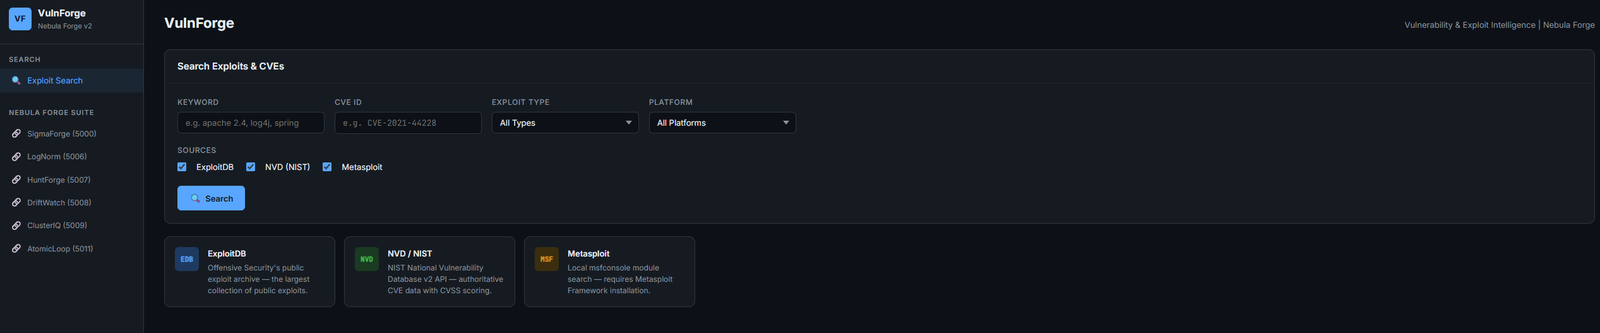 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
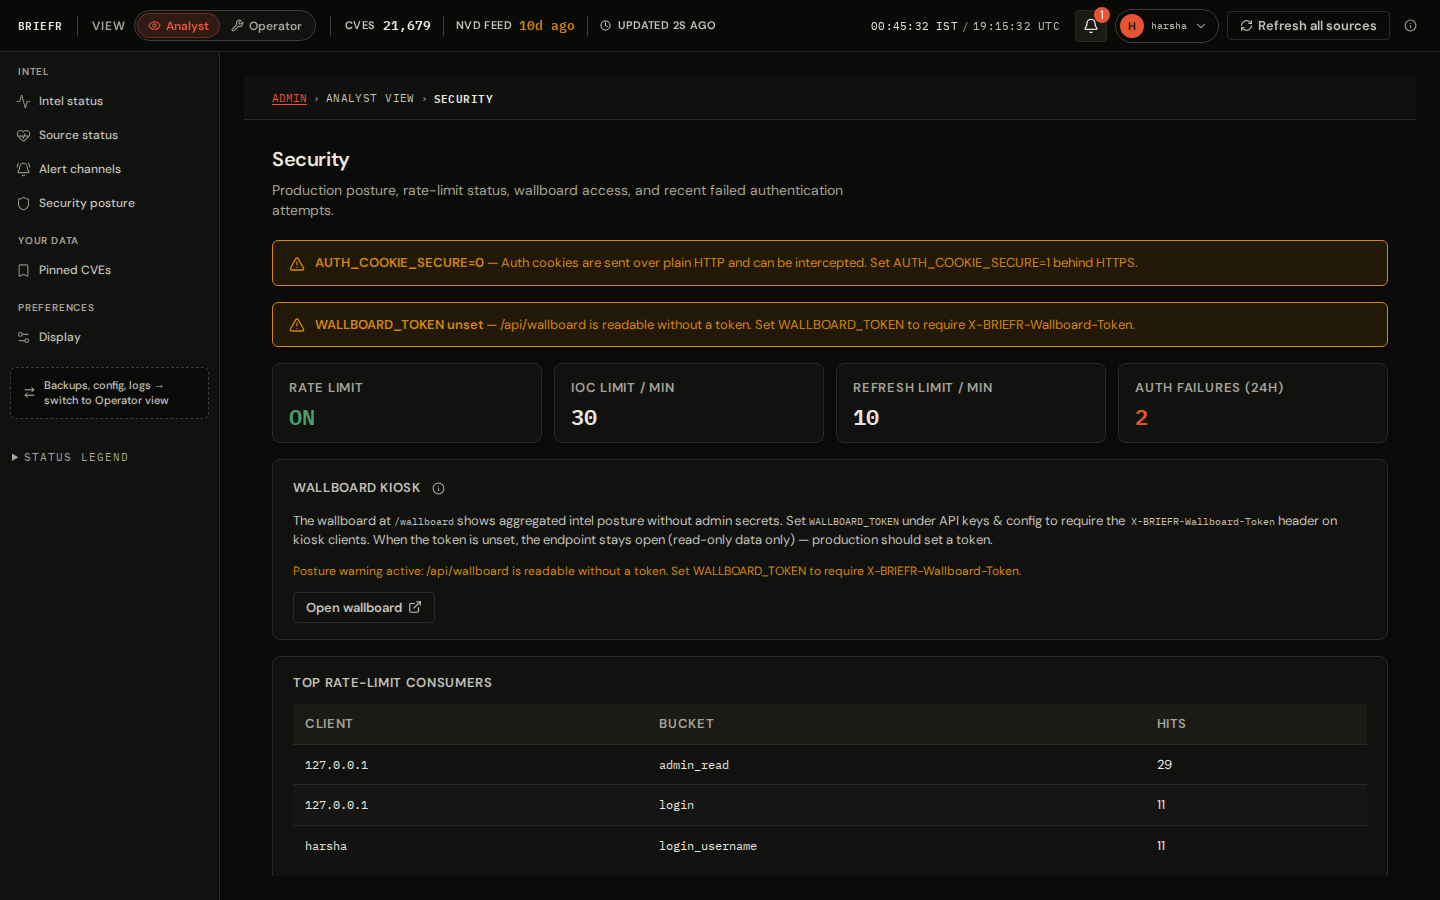 soldier0x0/briefr
Open Vulnerability Intelligence platform, aggregated intel in one dashboard, with correlation and IOC lookups, completely self hosted. All resources…
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon: real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
 patrowl/patrowlhears
PatrowlHears - Vulnerability Intelligence Center / Exploits
 renat0z3r0/notepadpp-supply-chain-iocs
IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…
 guardicode/cve-2021-44228_iocs
Curated collection of public Indicators of Compromise (IoCs) for the Log4j vulnerability (CVE-2021-44228), aggregated from multiple sources for…