scanner-for-CVE-2025-55182-vulnerability

CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…

CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…

Detailed disclosure of CVE-2025-68664, a critical deserialization vulnerability in LangChain core allowing secret exfiltration and potential RCE via…

Project Aura: Security auditing and code introspection

Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…

Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them

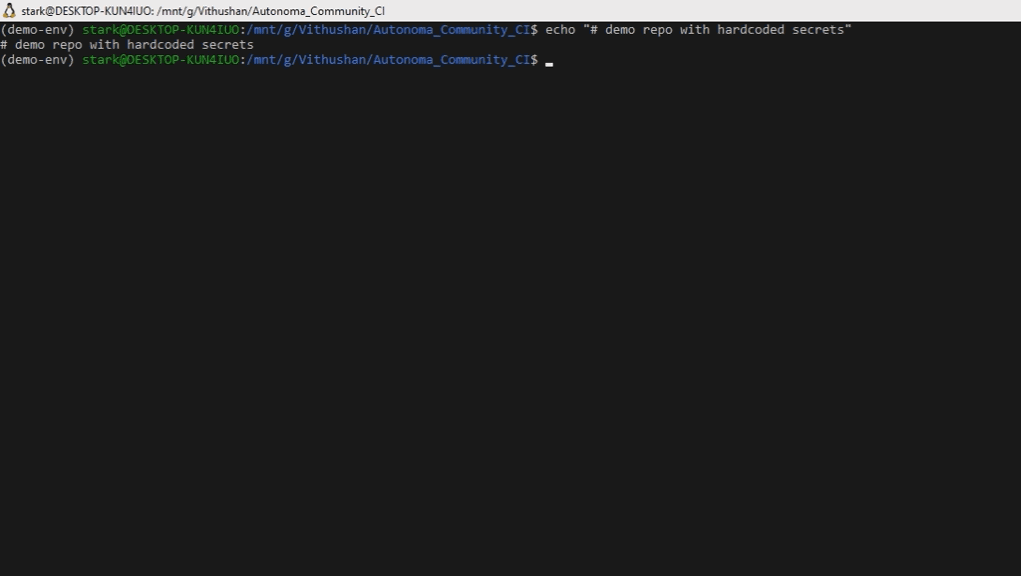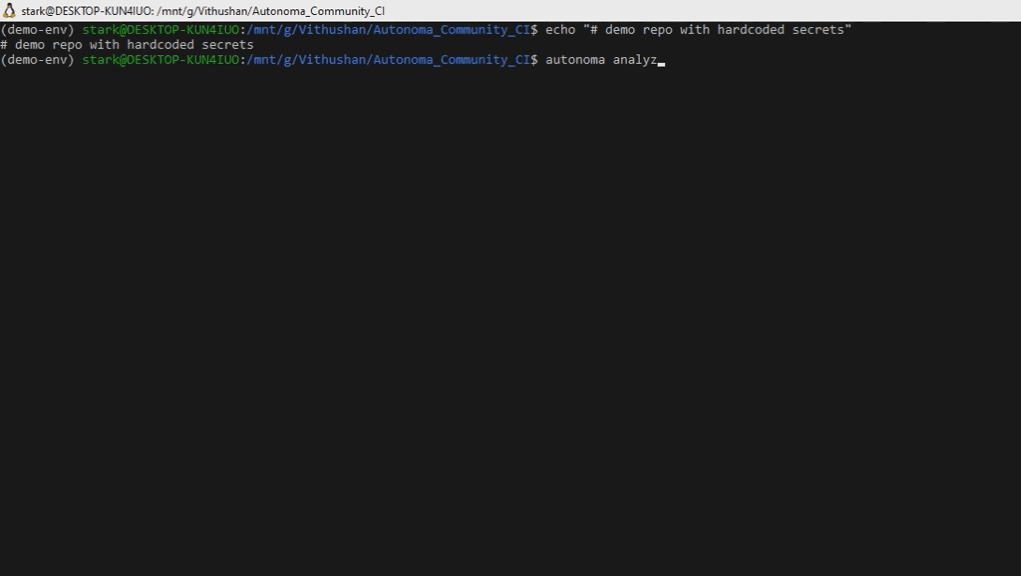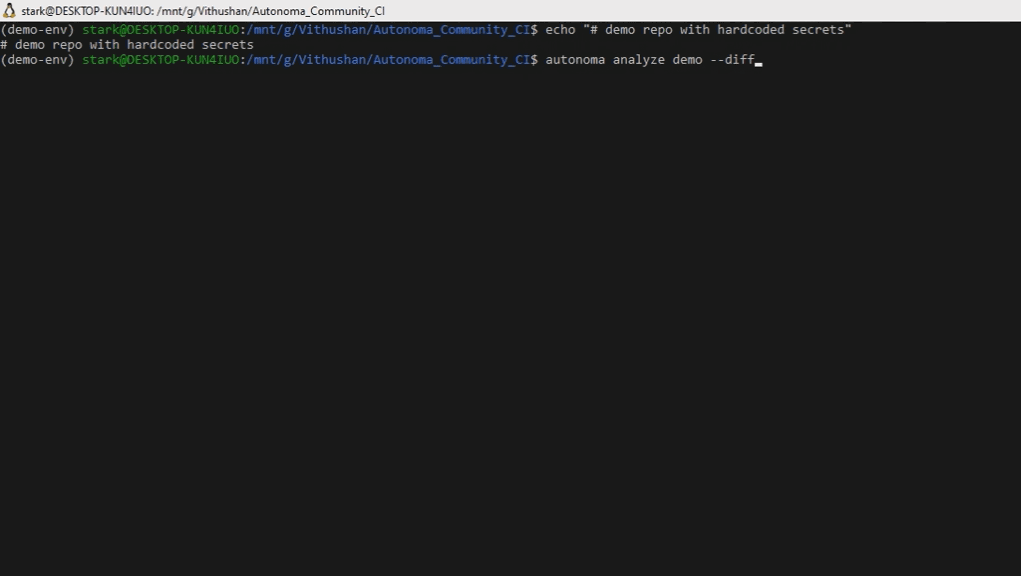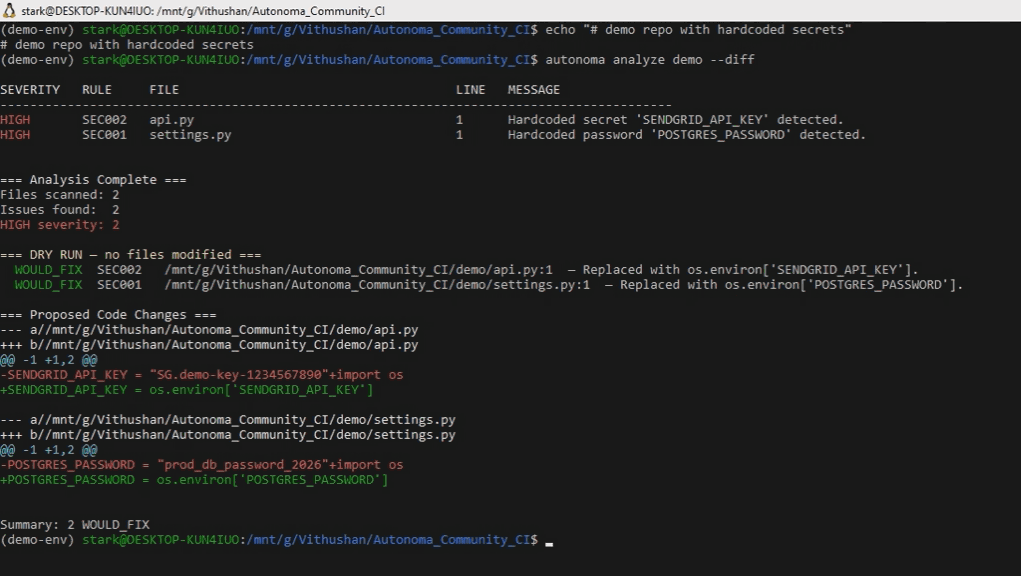
Detects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code

Find, verify, and analyze leaked credentials

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at…

Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…


Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.

Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…

Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…

CLI tool to scan codebases for quantum-vulnerable cryptography

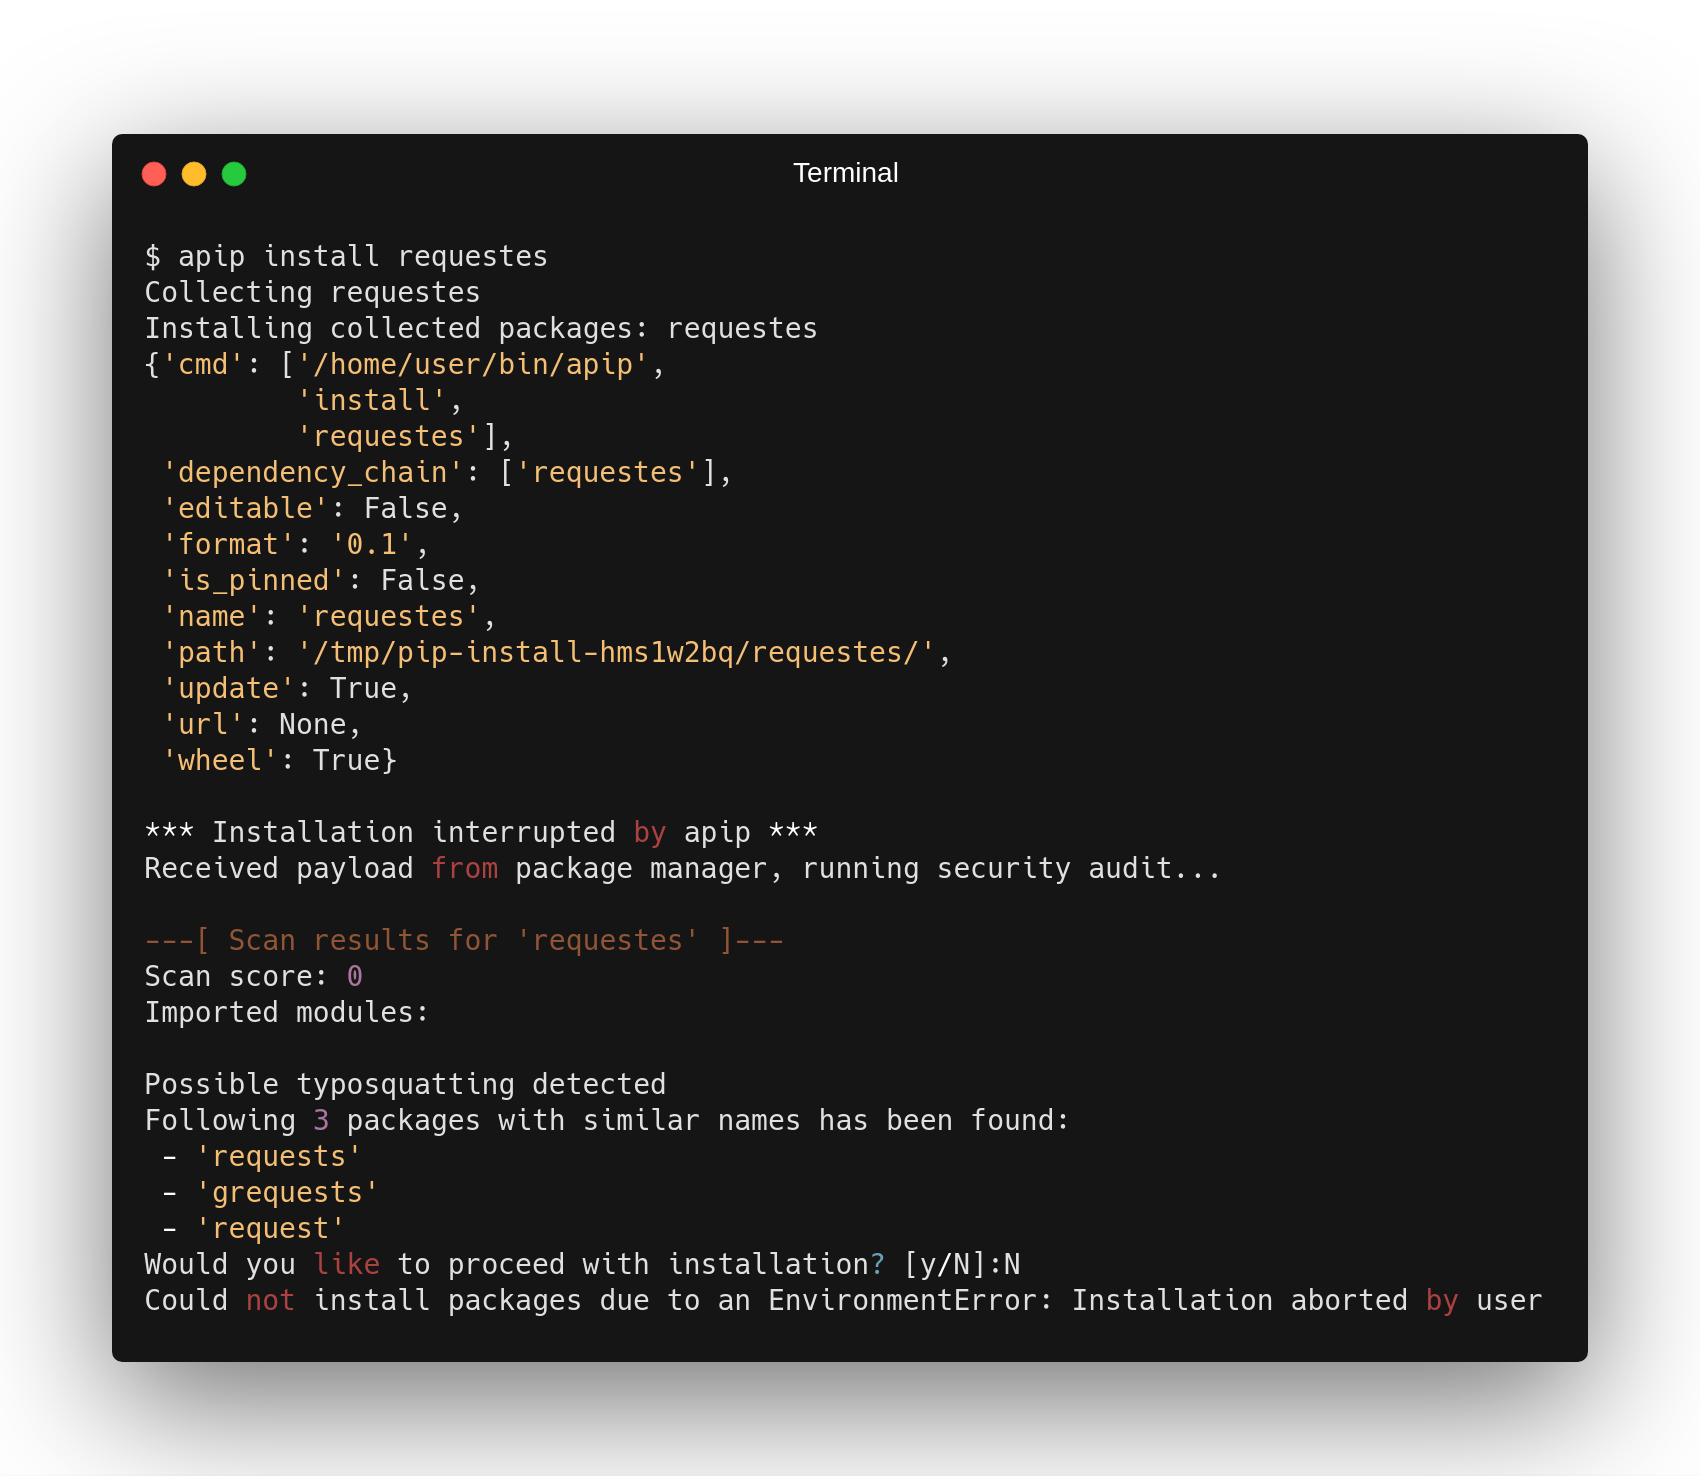
Automated dependency security layer for AI coding assistants that audits packages for CVEs, typosquats, abandonment, version-age issues, and hash…

Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.

The dependency-check repository has moved: