jeremylong__DependencyCheck_CVE-2018-12036_3-1-2

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

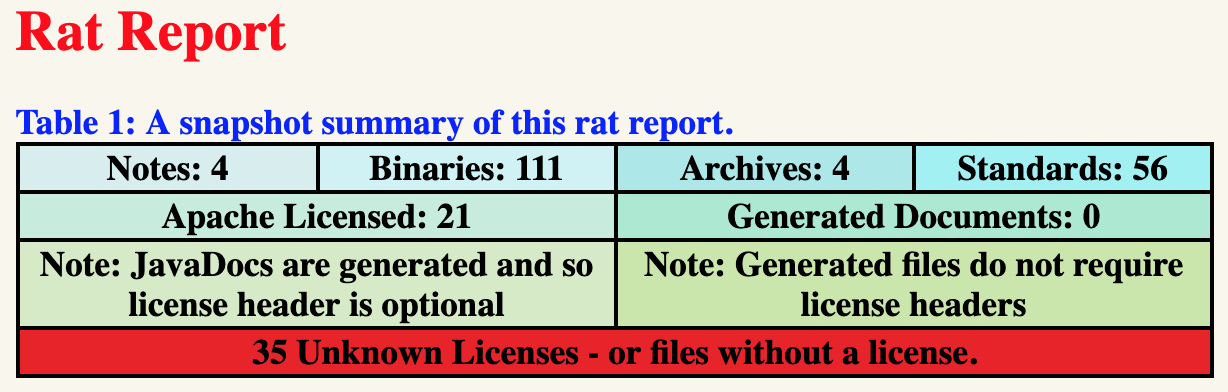
Apache RAT (Release Audit Tool) Gradle Plugin

Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…

Sample project that uses VEX to supress CVE-2024-29415.

AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.

Find the version that the project you currently develop or audit uses and quickly check which are the known smart contract security vulnerabilities…

🐺 Vulfy – Fast Rust based package version scanner

A macOS app to scan Xcode project files for possible security issues.

Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…

Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

Maintains the TUF repository that securely delivers the Sigstore trust root (trusted_root.json) to clients, using keyholder threshold signing, KMS…

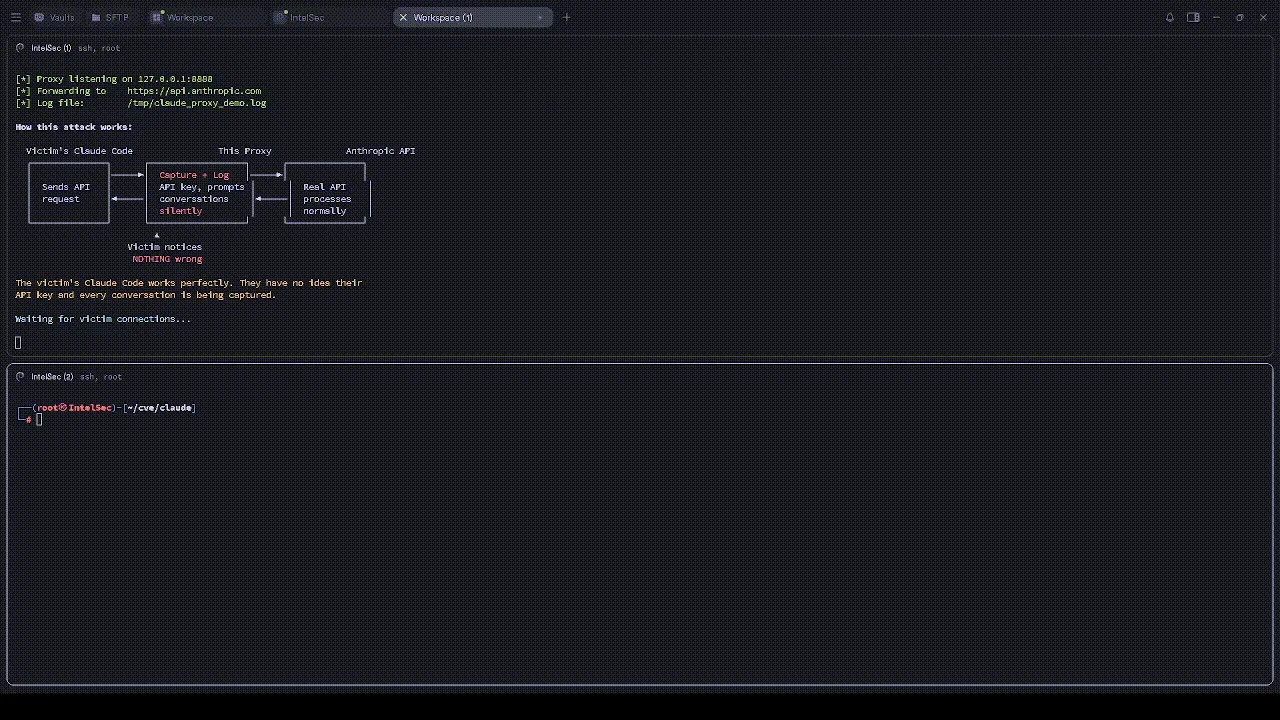
Educational demo of three Claude Code vulnerabilities (hooks bypass, MCP injection, API key exfiltration) with attacker server, MITM proxy, and…

Proof-of-concept demonstrating arbitrary command execution via malicious virtual environment activation scripts in PyCharm before 2020.3.4,…

OpenSSL toolkit providing TLS/SSL protocols and general-purpose cryptographic library with command-line tools for key generation, certificate…

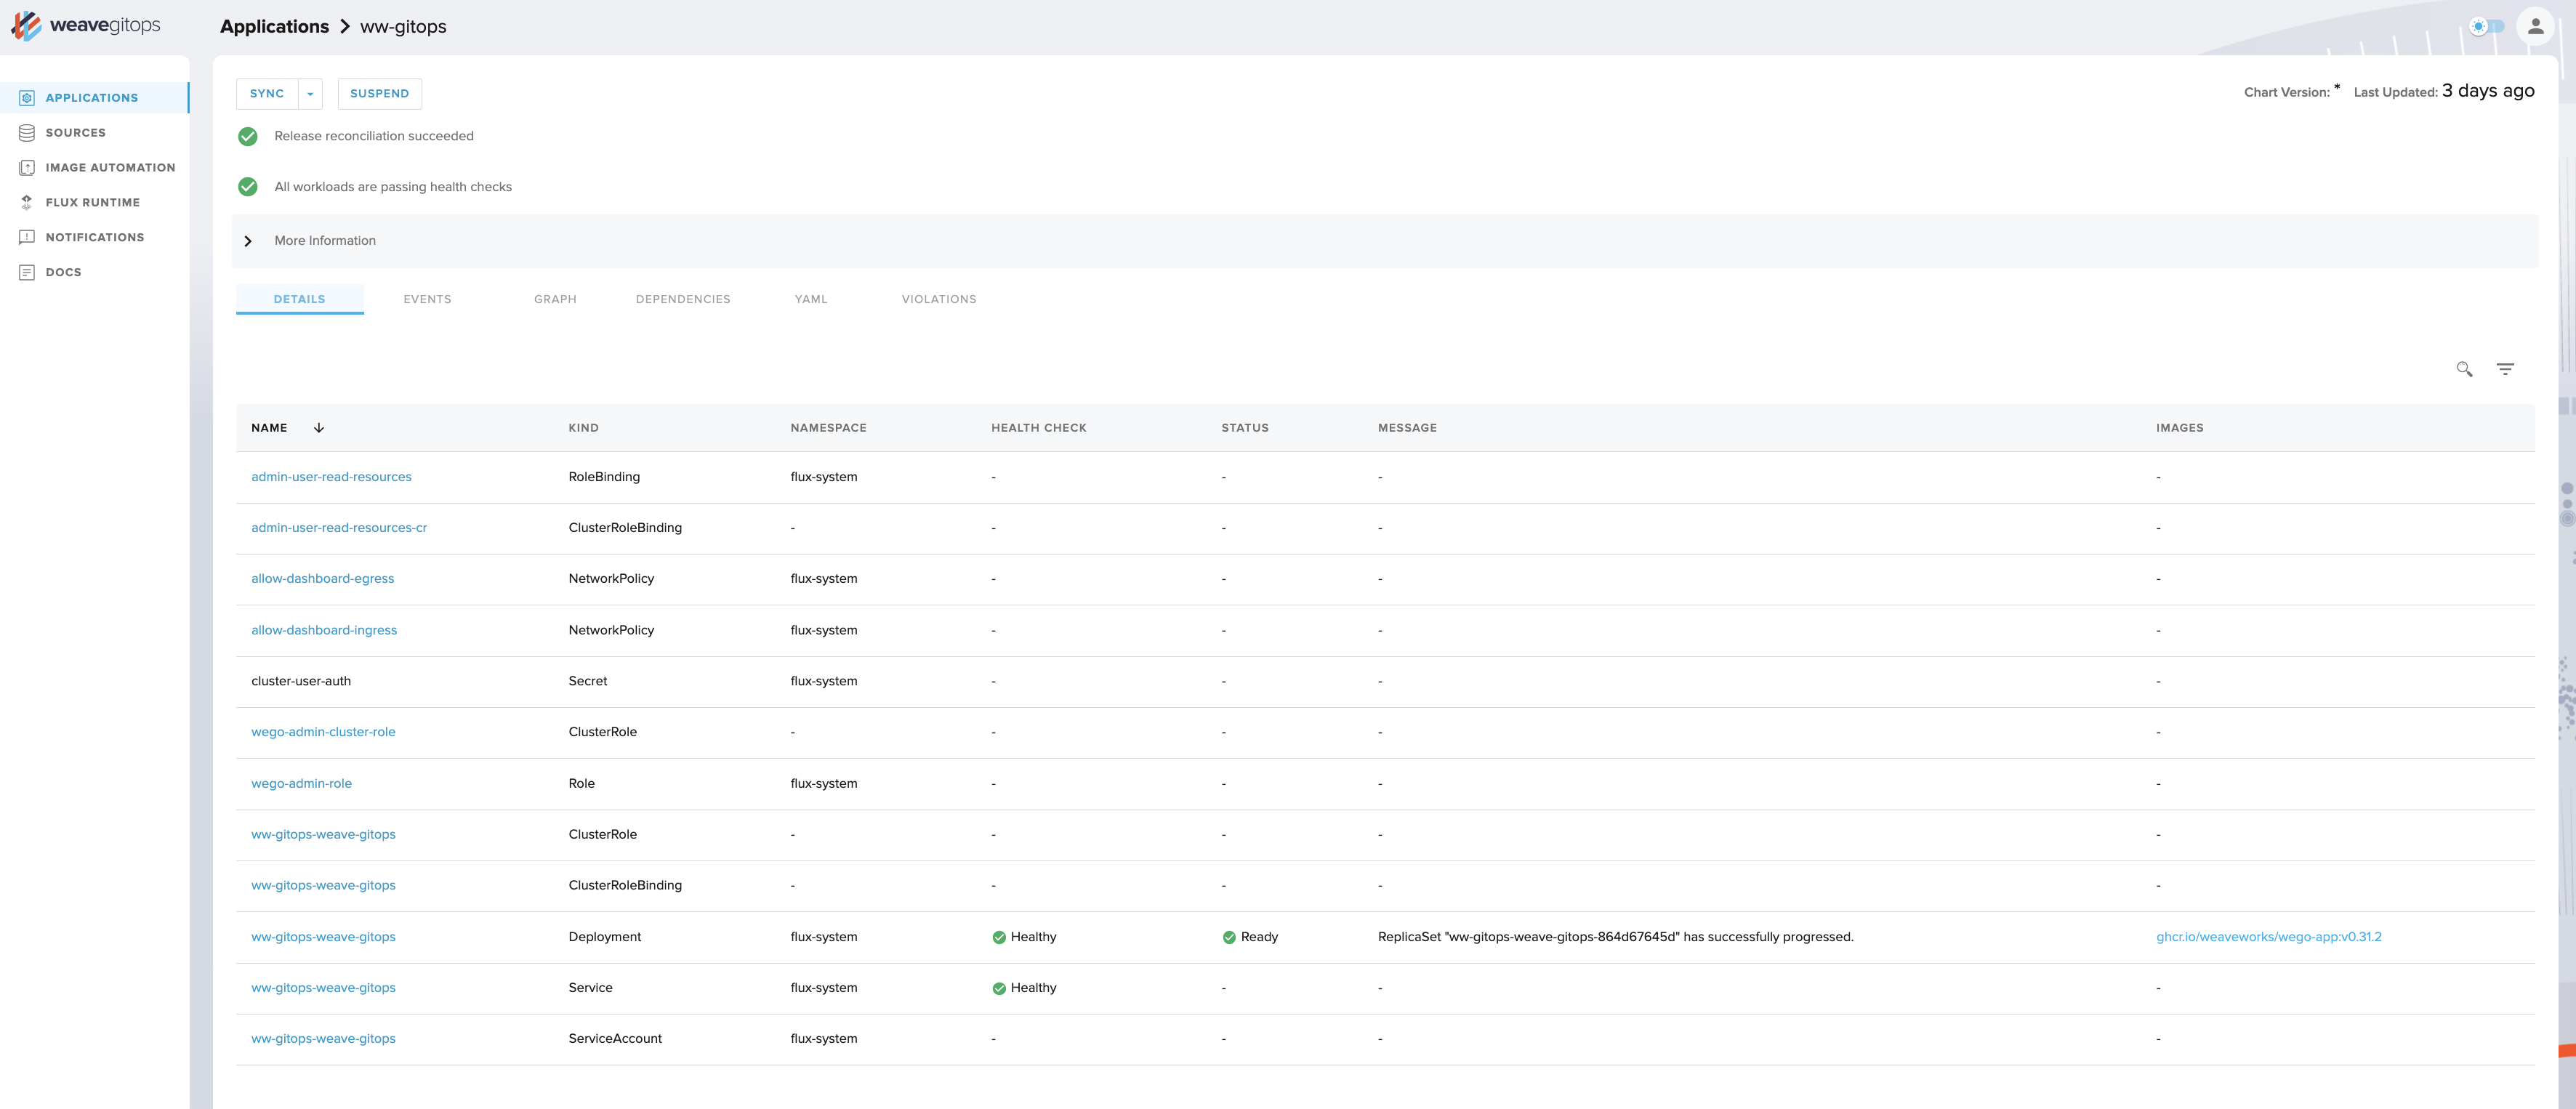
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…

Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…

enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…