
sh4d0wup
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework
command-and-controlexploitationpayload-development+3
kpcyrd/sh4d0wupSigning-key abuse and update exploitation framework
 grassplatypus/cve-2026-45033-class
CVE-2026-45033 PoC for Claude Code, not Github Copilot. Worked for Haiku 4.5.
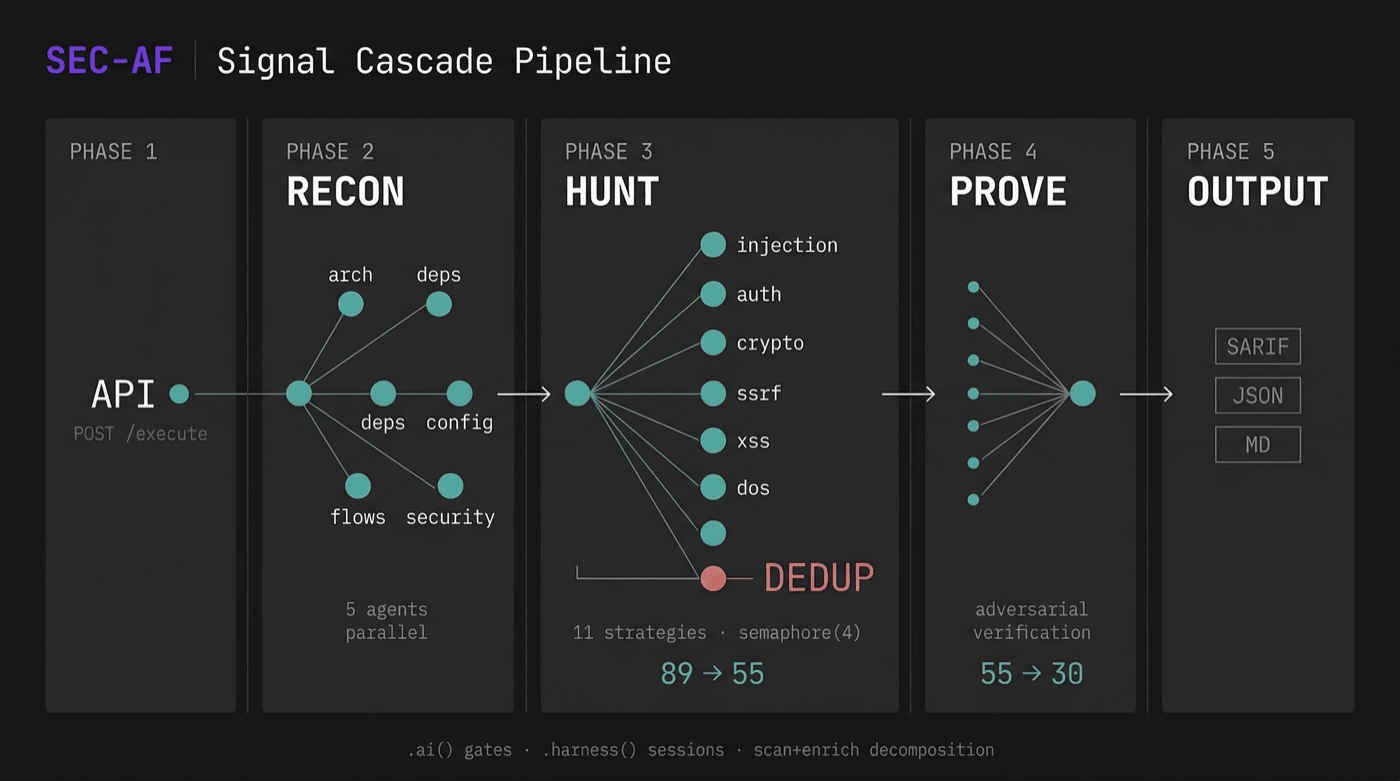 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 doyensec/malicious-devfile-registry
CVE-2024-0402 exploit for GitLab Workspaces using a malicious Devfile Registry with path-traversal archive to overwrite authorized_keys and gain SSH…
 0x3a/cve-2014-4936
Repository for CVE-2014-4936 POC code.
 wise-security/cve-2025-69599
Proof-of-concept exploit for CVE-2025-69599, demonstrating uncontrolled search path element in RayVentory Scan Engine's rvia and ndtrack binaries,…
 h4mr3r/cve-2024-5082
Proof-of-concept exploit for CVE-2024-5082, a remote code execution vulnerability in Sonatype Nexus Repository Manager 2 via crafted Maven artifacts…
 reefspek/cocoapods-rce_cve-2024-38366
CocoaPods RCE Vulnerability CVE-2024-38366
 simoesctt/sovereign-echo-33017
Exploit for CVE-2026-33017, an unauthenticated RCE in Langflow 1.8.1 via the build_public_tmp endpoint, enabling Python code injection through…
 nn0nkey/repo
CVE-2025-65964 PoC - Malicious Git Hooks
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 frostsaberx/cve-2020-27955
Git-LFS RCE Test
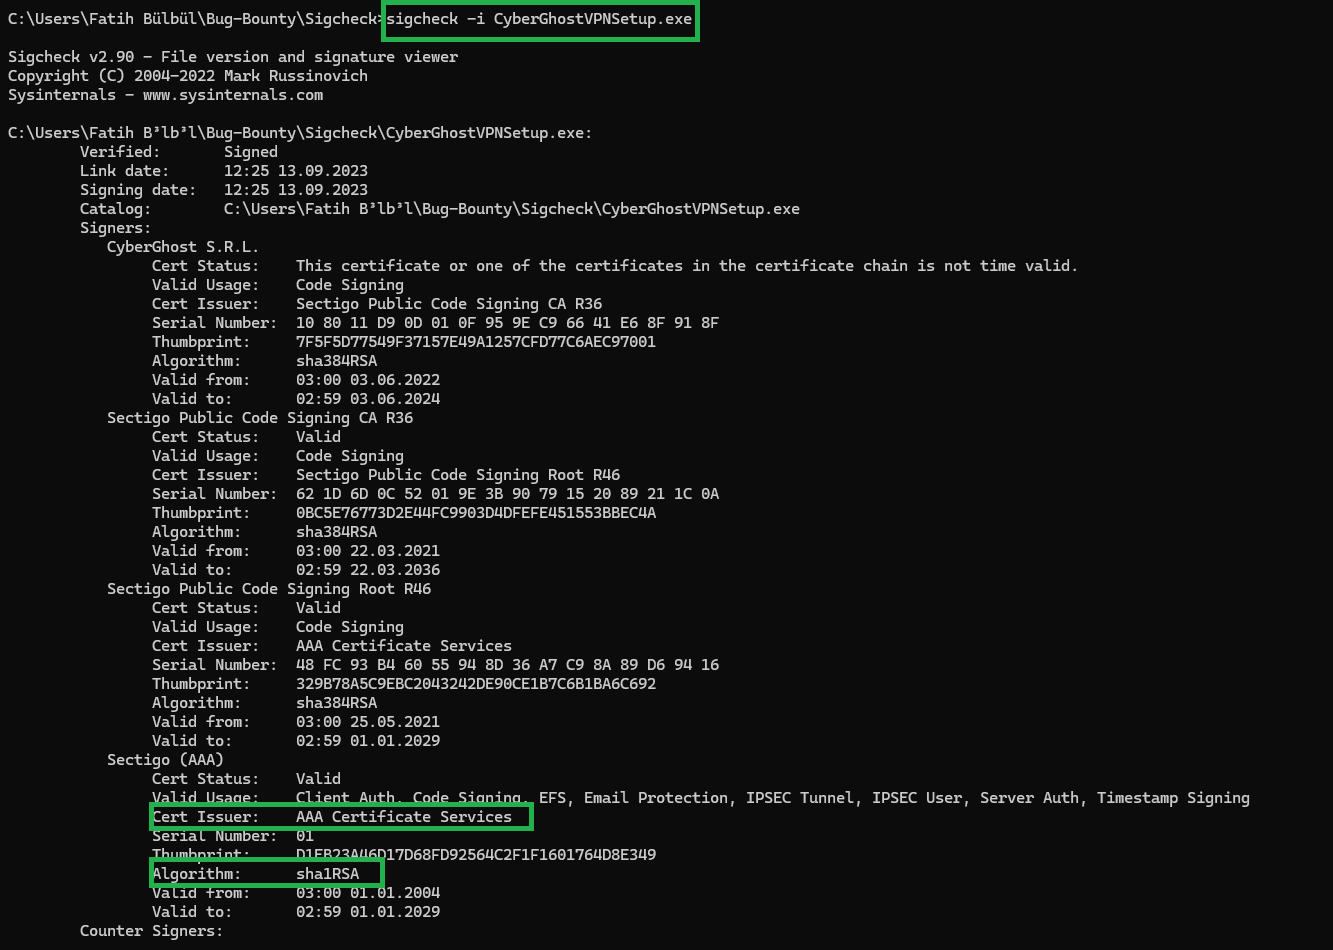 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 internero/debian-lenny-bash_3.2.52-cve-2014-6271
Debian Lenny Bash packages with cve-2014-6271 patches (i386 and amd64)
 vulnbe/poc-rebar3
Shell injection in Rebar3
 owasp/apts
OWASP Autonomous Penetration Testing Standard
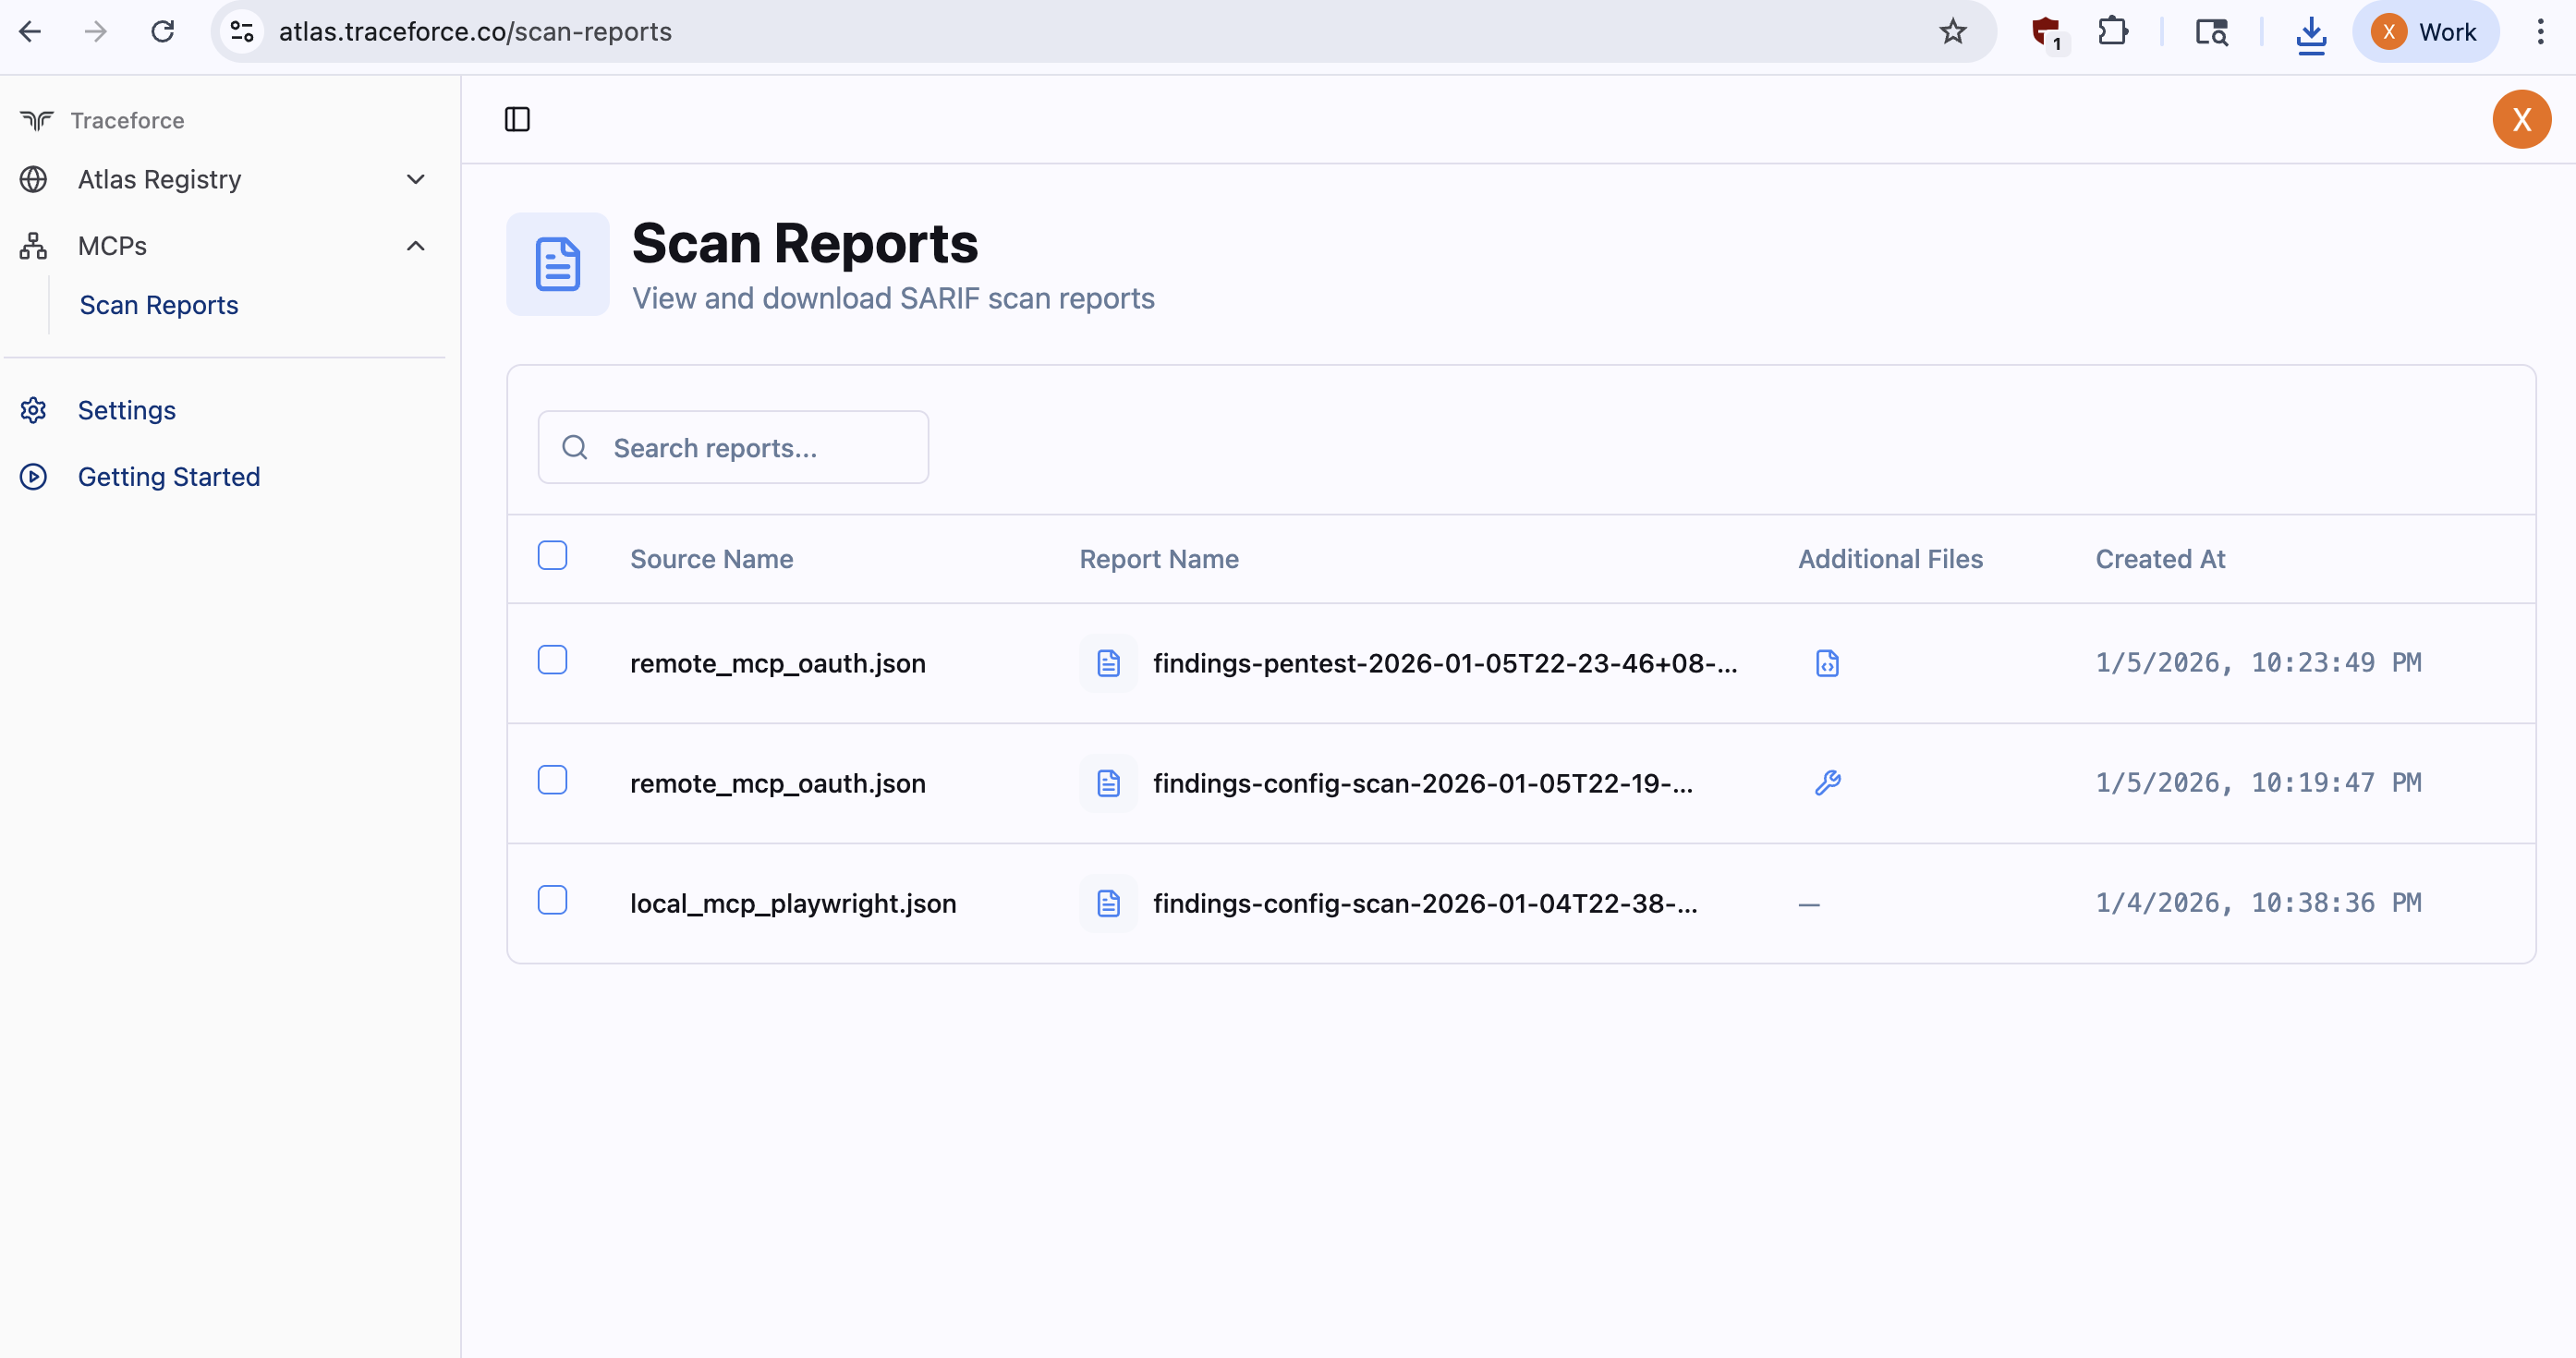 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.