
remic
 knqyf263/remic
Vulnerability Scanner for Detecting Publicly Disclosed Vulnerabilities in Application Dependencies
supply-chain-securityvulnerability-scanners
knqyf263/remicVulnerability Scanner for Detecting Publicly Disclosed Vulnerabilities in Application Dependencies
 scabench/jsonorg-fn1
simple application with a CVE-2022-45688 vulnerability
 scabench/jsonorg-tp1
simple application with a CVE-2022-45688 vulnerability
 scabench/jsonorg-fp3
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 scabench/jsonorg-fp1
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 scabench/jsonorg-fp2
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 snyk/snyk-scan
Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.
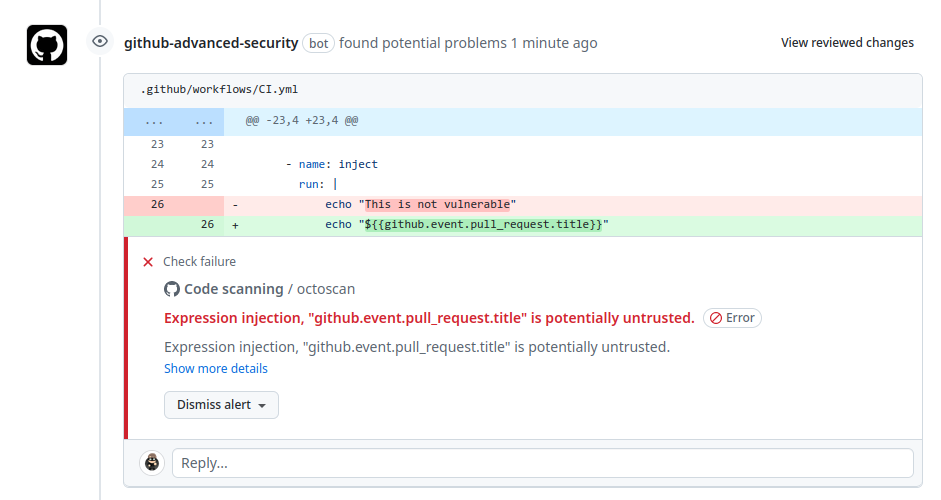 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 logpresso/cve-2021-44228-scanner
Vulnerability scanner and mitigation patch for Log4j2 CVE-2021-44228
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 dpomnean/log4j_scanner_wrapper
log4j vulnerability wrapper scanner for CVE-2021-44228
 devops-kung-fu/bomber
Scans Software Bill of Materials (SBOMs) for security vulnerabilities
 barrersoftware/opencode-secure
Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch
 xiaoqimikko/spring-cvss-check
Scans Java artifacts and source for Spring/Tomcat CVEs, compares vendor vs NVD CVSS scores, verifies exploitability conditions, and checks if fix…
 george0papasotiriou/cve-2026-22018-jenkins-pipeline-shared-library-code-execution-via-grab-
PoC for CVE-2026-22018, a critical Jenkins Pipeline Shared Library RCE via Groovy @Grab, demonstrating supply-chain code injection and mitigation…