
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
113 results
pqaudit preview

pqaudit

GitHubpqcworld/pqaudit

Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.

code-analysiscryptographydevsecops+5
36 months ago
LeitWacht preview

LeitWacht

GitLableitwacht/leitwacht

Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
anomaly-detectioncloud-infrastructure-securitycloud-security+9
1 month ago
CVE-2026-8888-Printer-Firmware-Unsigned-Update-via-HTTP preview

CVE-2026-8888-Printer-Firmware-Unsigned-Update-via-HTTP

GitHubgeorge0papasotiriou/cve-2026-8888-printer-firmware-unsigned-update-via-http

Demonstrates CVE-2026-8888, an unsigned printer firmware update over HTTP, including a malicious update server and vulnerable printer emulator for…
embedded-systems-securityexploitationfirmware-analysis+4
2 months ago
clawdstrike preview

clawdstrike

GitHubbackbay-labs/clawdstrike

Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
ai-securitycloud-securitycontainer-security+5
2969 days ago
guardskill preview

guardskill

GitHubsoemoescode/guardskill

Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
ai-securitycode-analysisconfiguration-auditing+4
123 days ago
bumblebee preview

bumblebee

GitHubperplexityai/bumblebee

Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
devsecopsincident-responseinformation-gathering+3
5.1k5 days ago
Harden-Windows-Security preview

Harden-Windows-Security

GitHubhotcakex/harden-windows-security

Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
configuration-auditingdefensive-toolsencryption-decryption-tools+3
4.8k4h 8m ago
criticality_score preview

criticality_score

GitHubossf/criticality_score

Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.
information-gatheringpapers-researchsupply-chain-security+1
1.5k1 month ago
pipelock preview

pipelock

GitHubluckypipewrench/pipelock

Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
ai-securityapi-securitycloud-security+8
9204h 26m ago
puncia preview

puncia

GitHubarpsyndicate/puncia

Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
exploit-frameworksinformation-gatheringosint+6
6662 days ago
prismor preview

prismor

GitHubprismorsec/prismor

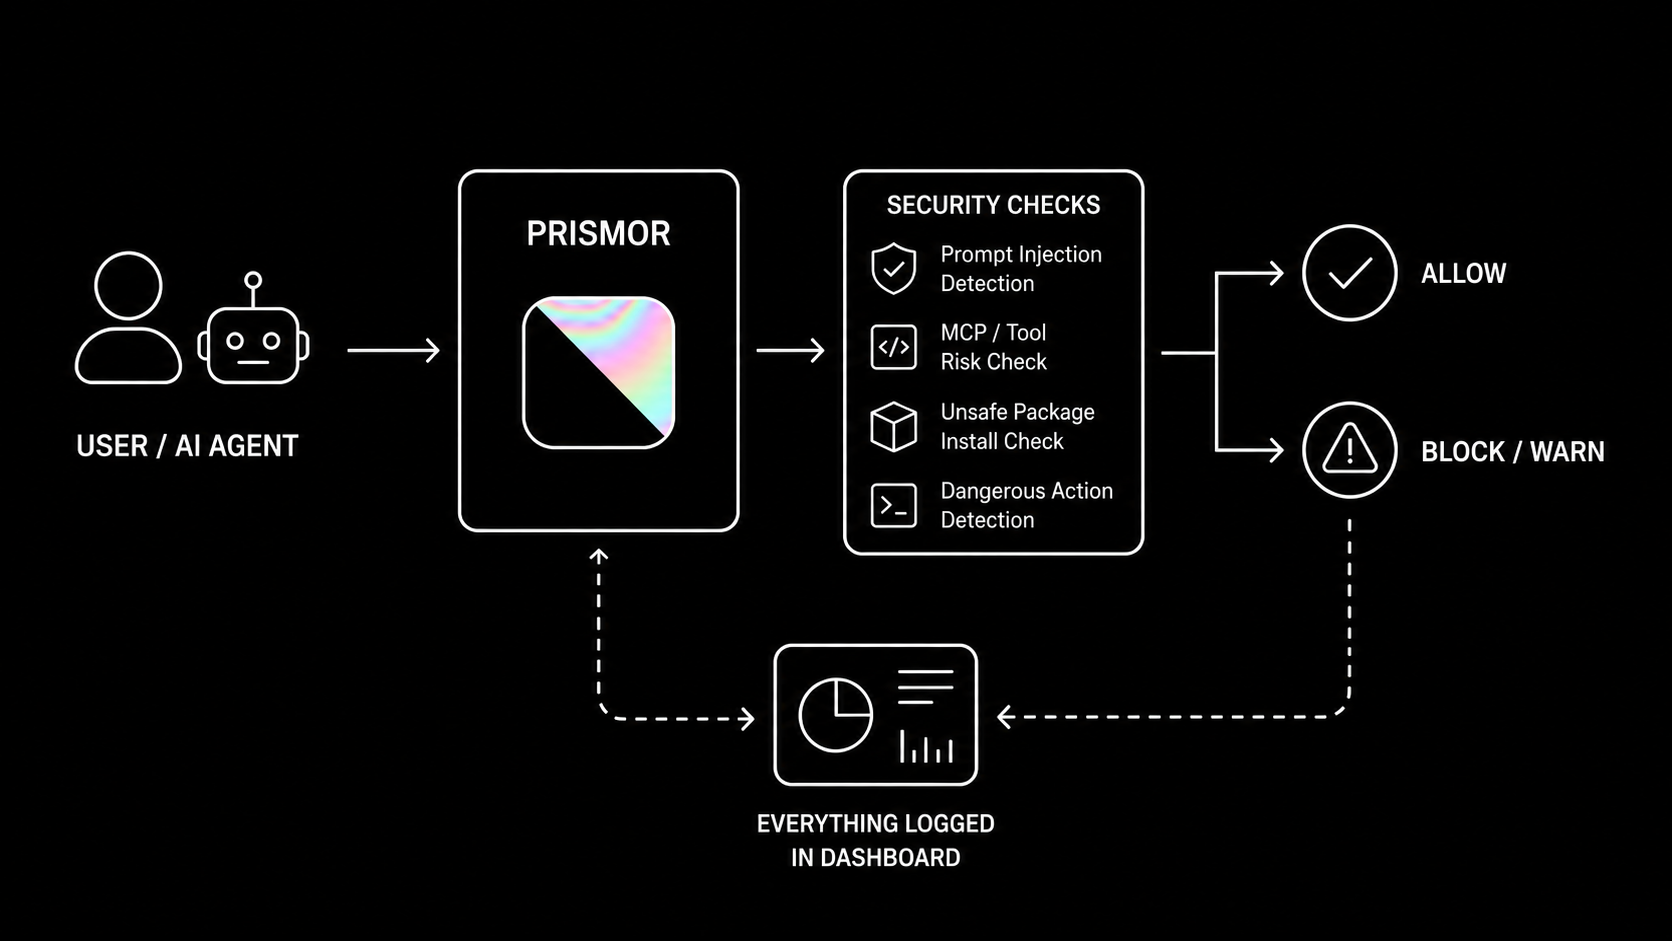
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…

ai-securitycontainer-securitydefensive-tools+5
40612h 13m ago
hijagger preview

hijagger

GitHubfirefart/hijagger

Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
dns-analysisosintreconnaissance+3
3085h 55m ago
smokedmeat preview

smokedmeat

GitHubboostsecurityio/smokedmeat

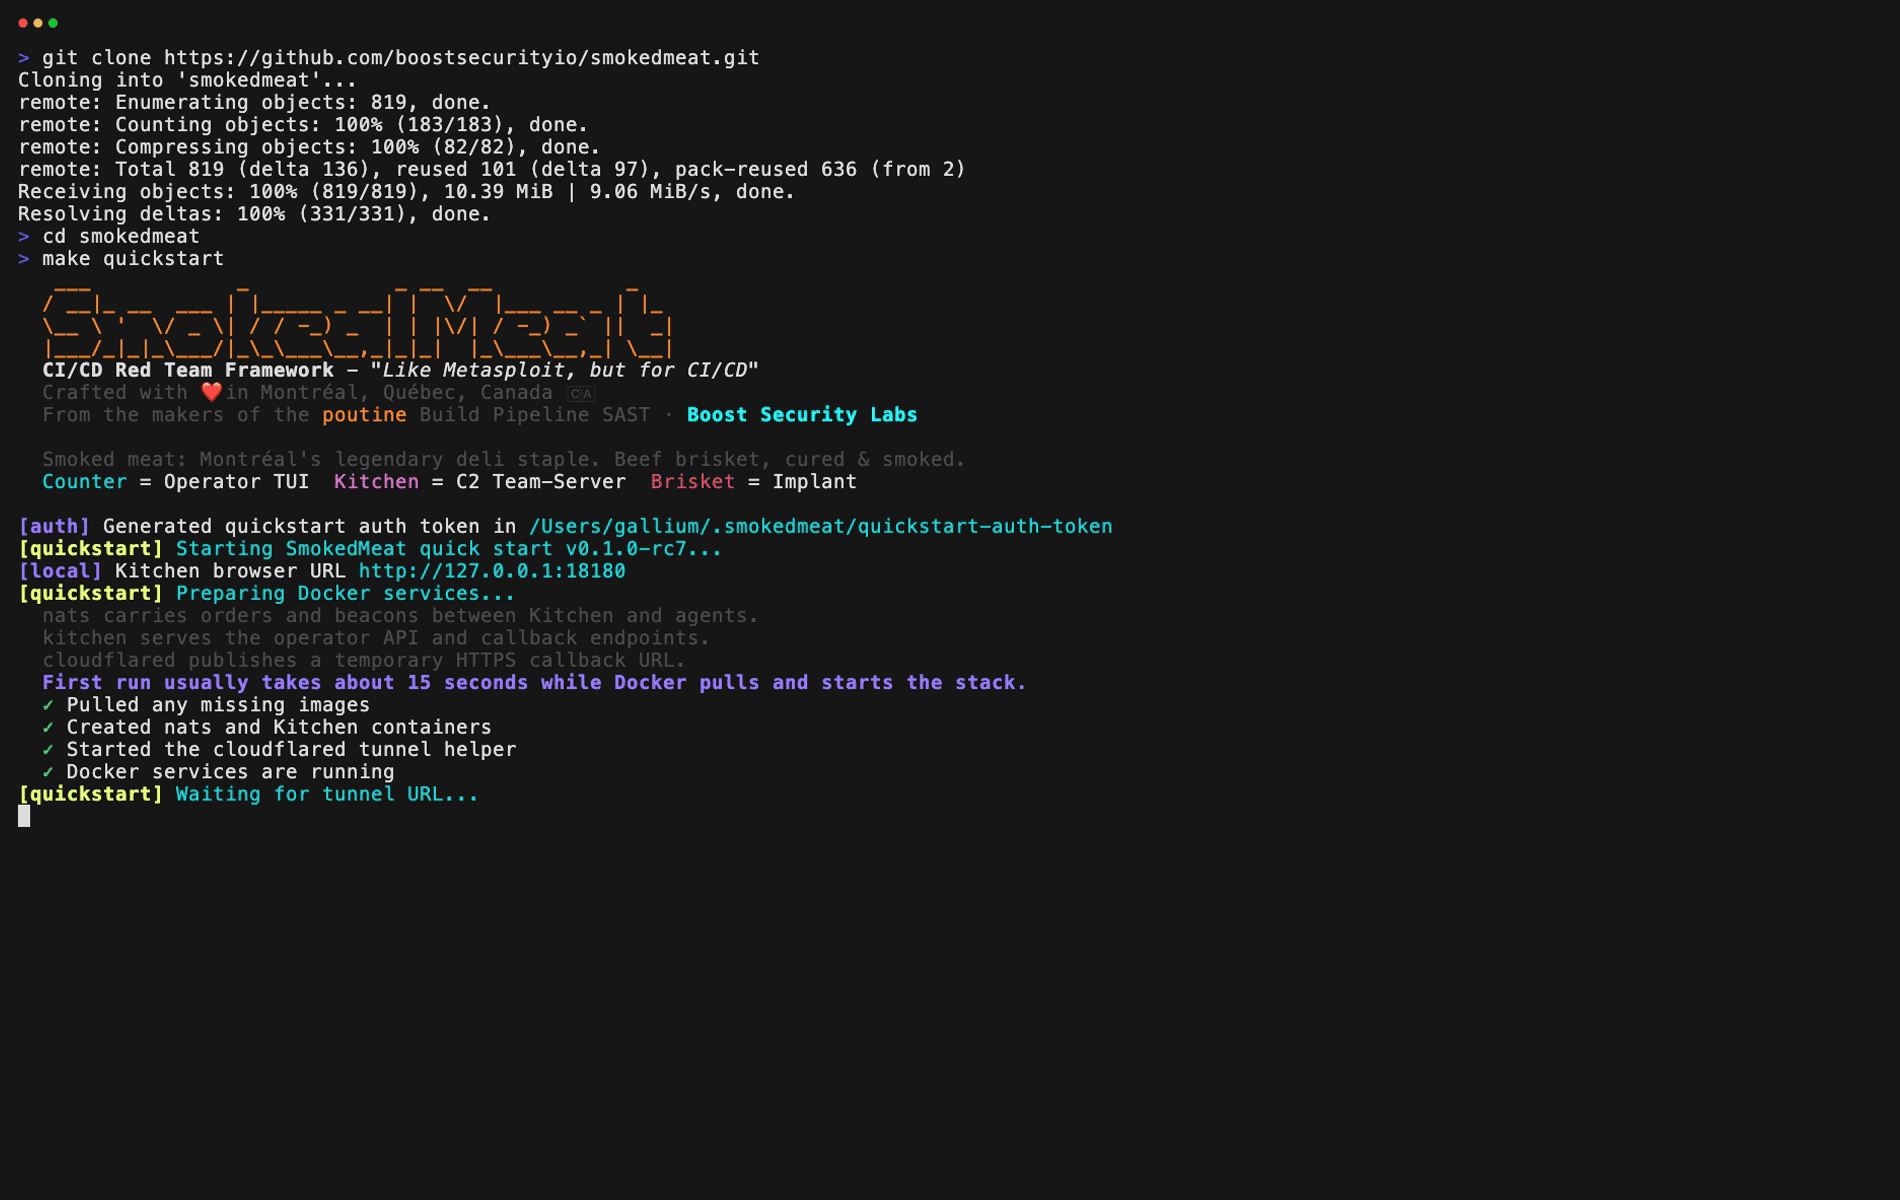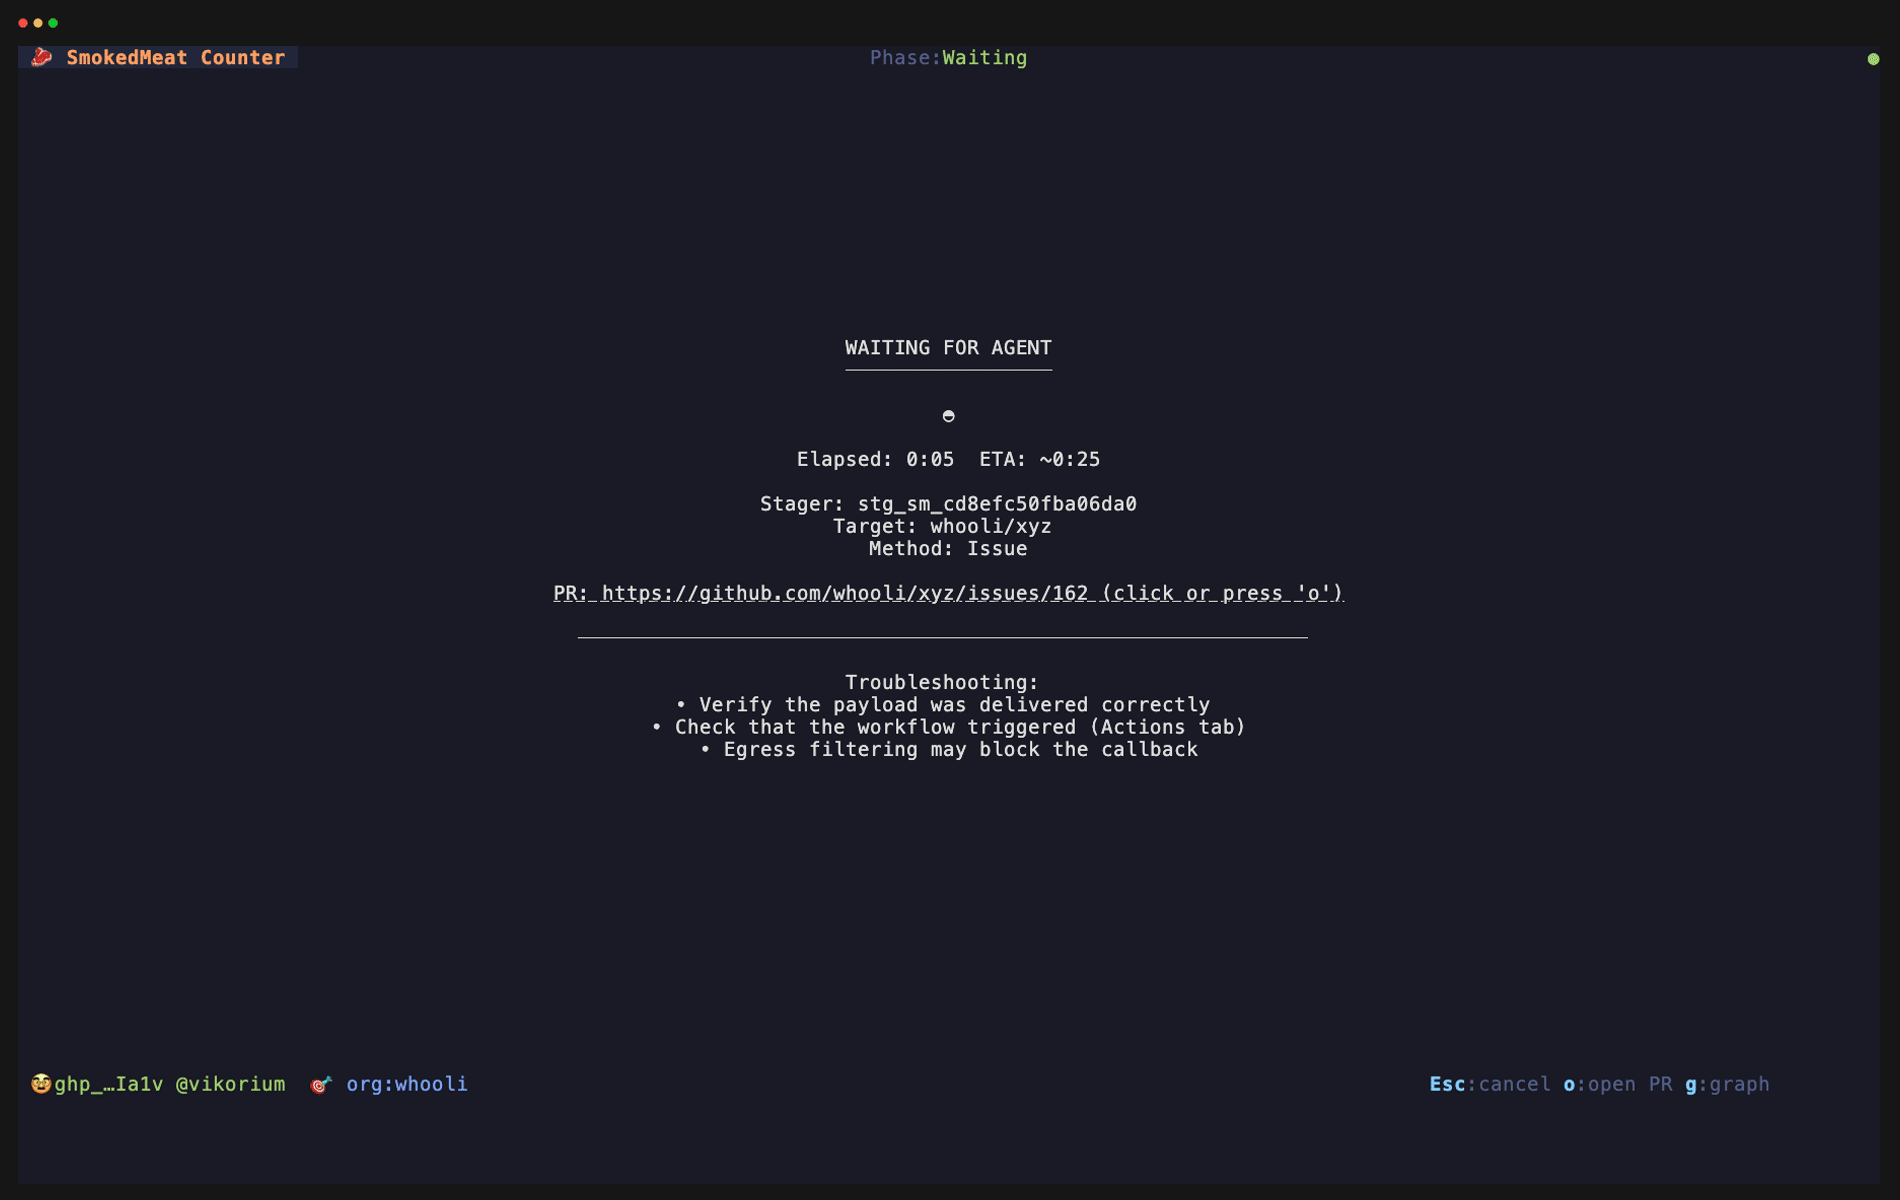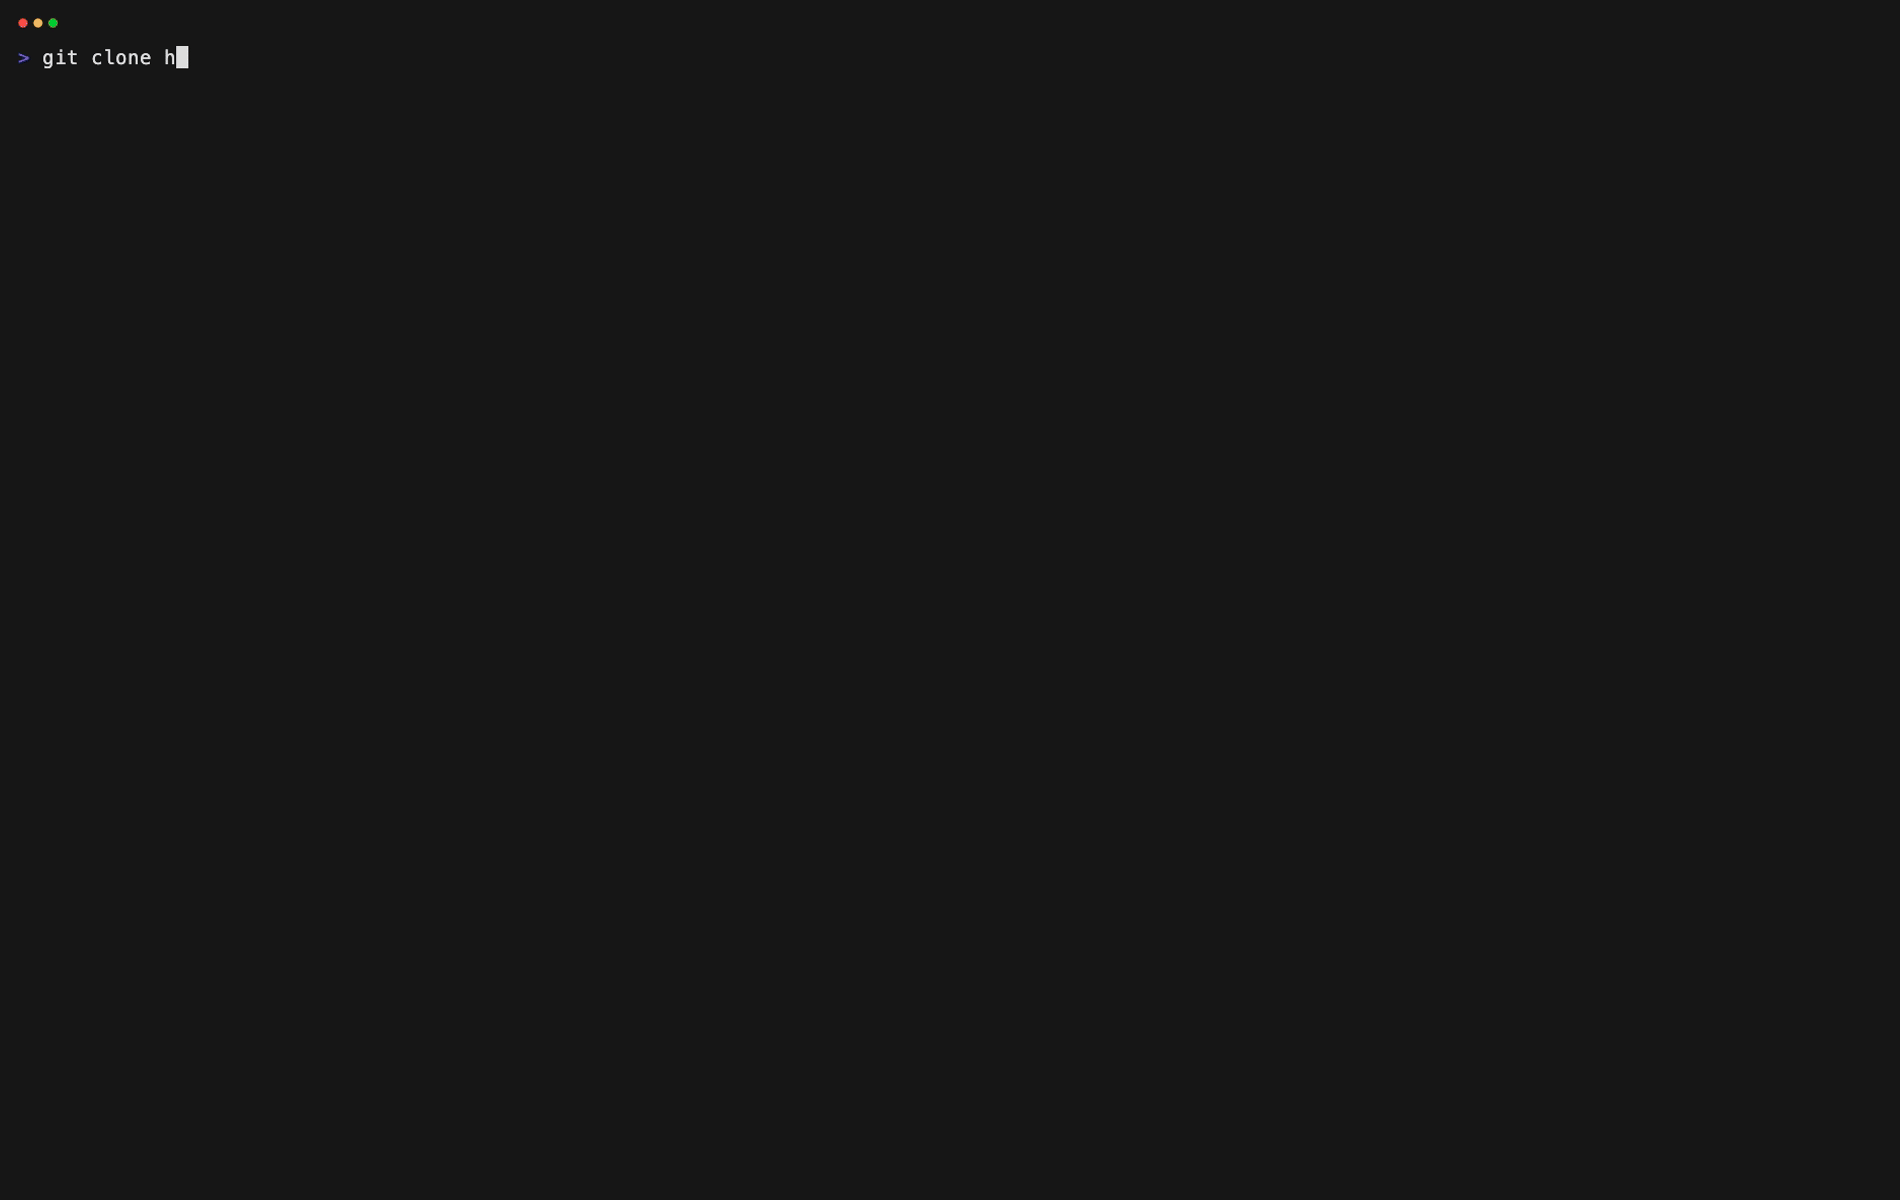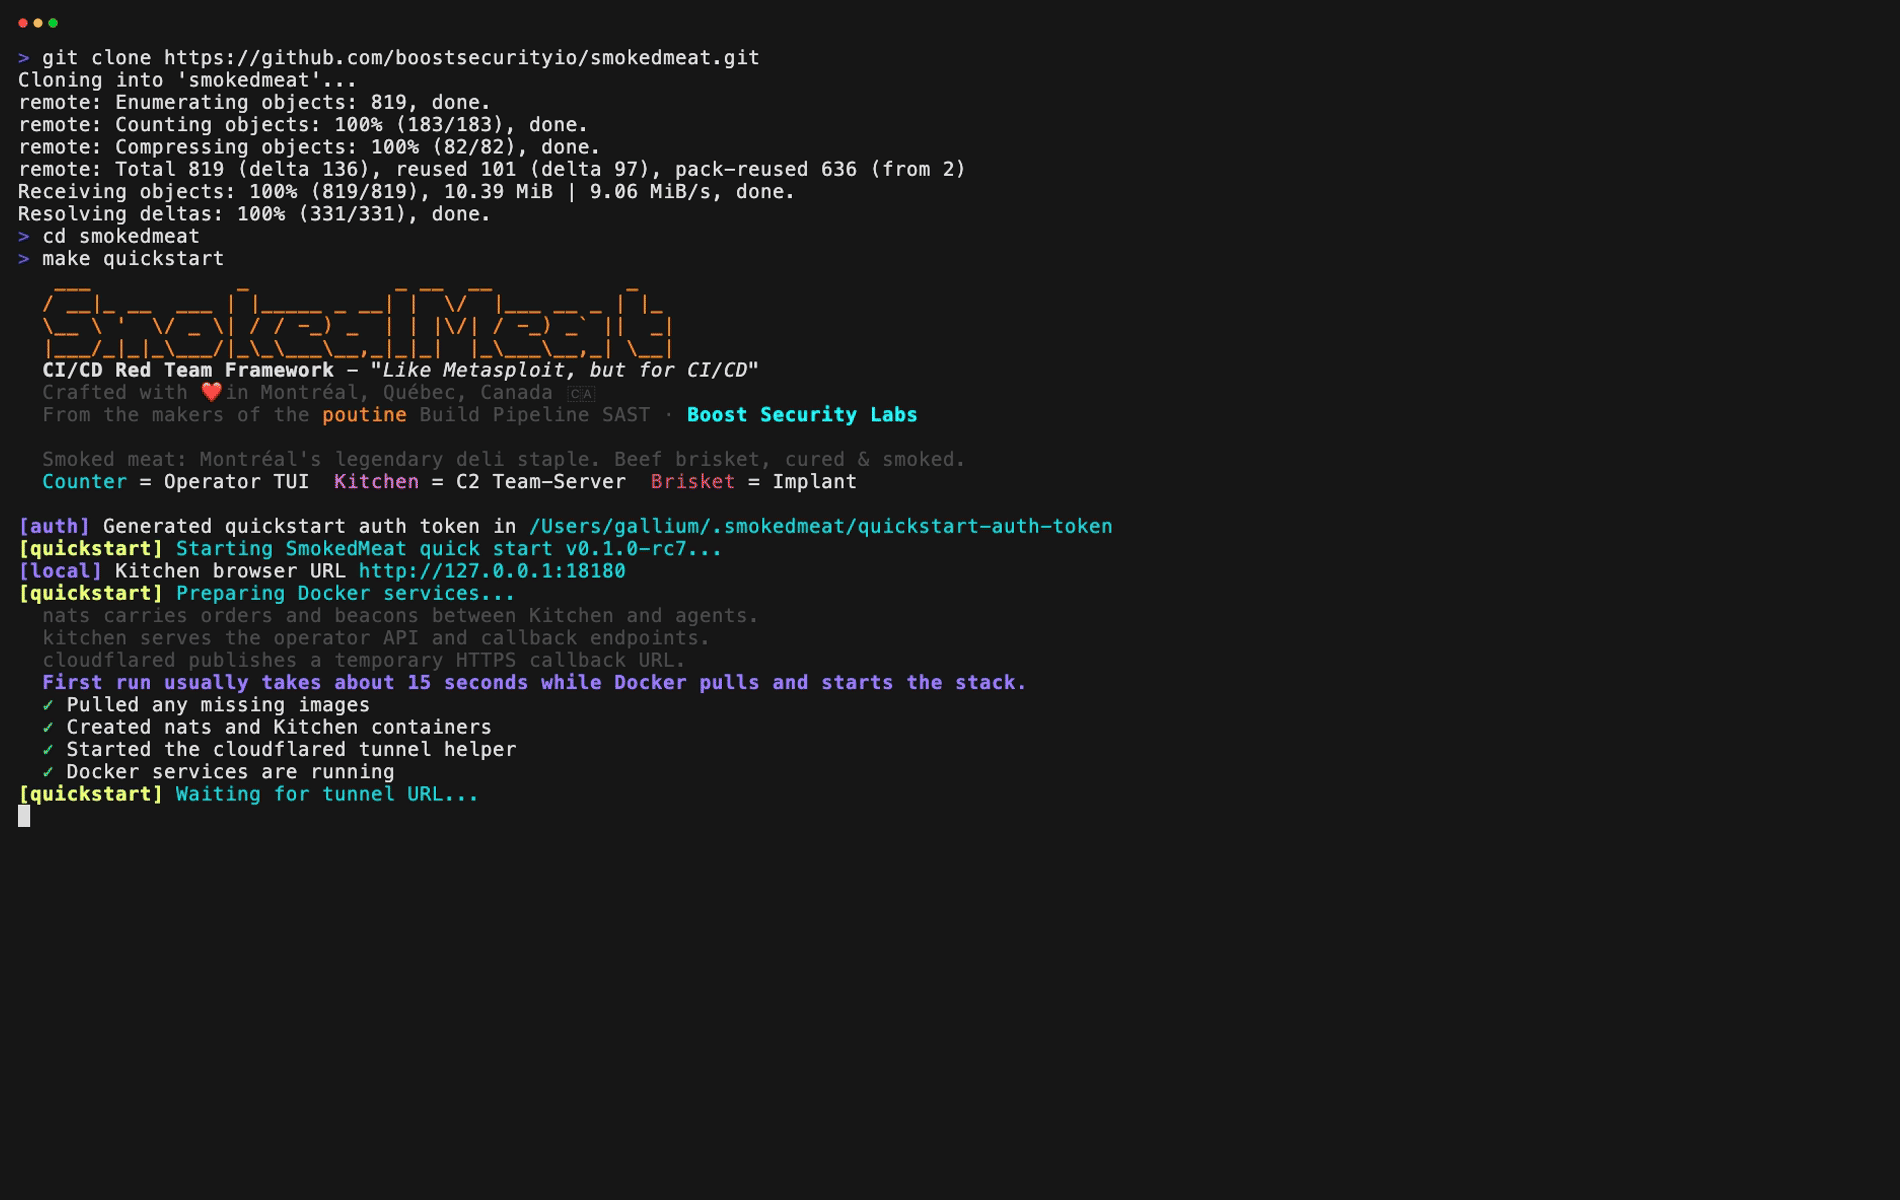
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
cloud-securitycommand-and-controleducation+9
38820 days ago
smart-tree preview

smart-tree

GitHub8b-is/smart-tree

Smart Tree: not just a tree, a philosophy. A context-aware, AI-crafted replacement for 20+ tools with MEM8 quantum compression, semantic search,…
curated-resourceseducationgeneral-purpose-utilities+3
27026 days ago
agentseal preview

agentseal

GitHubgetagentseal/agentseal

Security toolkit for AI agents. Scan your machine for dangerous skills and MCP configs, monitor for supply chain attacks, test prompt injection…
ai-securitycommand-and-controldata-exfiltration+7
3773 months ago
node9-proxy preview

node9-proxy

GitHubnode9-ai/node9-proxy

Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…

ai-securitycloud-securitycommand-and-control+7
2173 days ago
cplt preview

cplt

GitHubnavikt/cplt

Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
ai-securitycommand-and-controlconfiguration-auditing+7
1281 day ago
GitHound preview

GitHound

GitHubspecterops/githound

BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…

cloud-securityidentity-access-managementinformation-gathering+4
1481 month ago
Previous1234567Next