
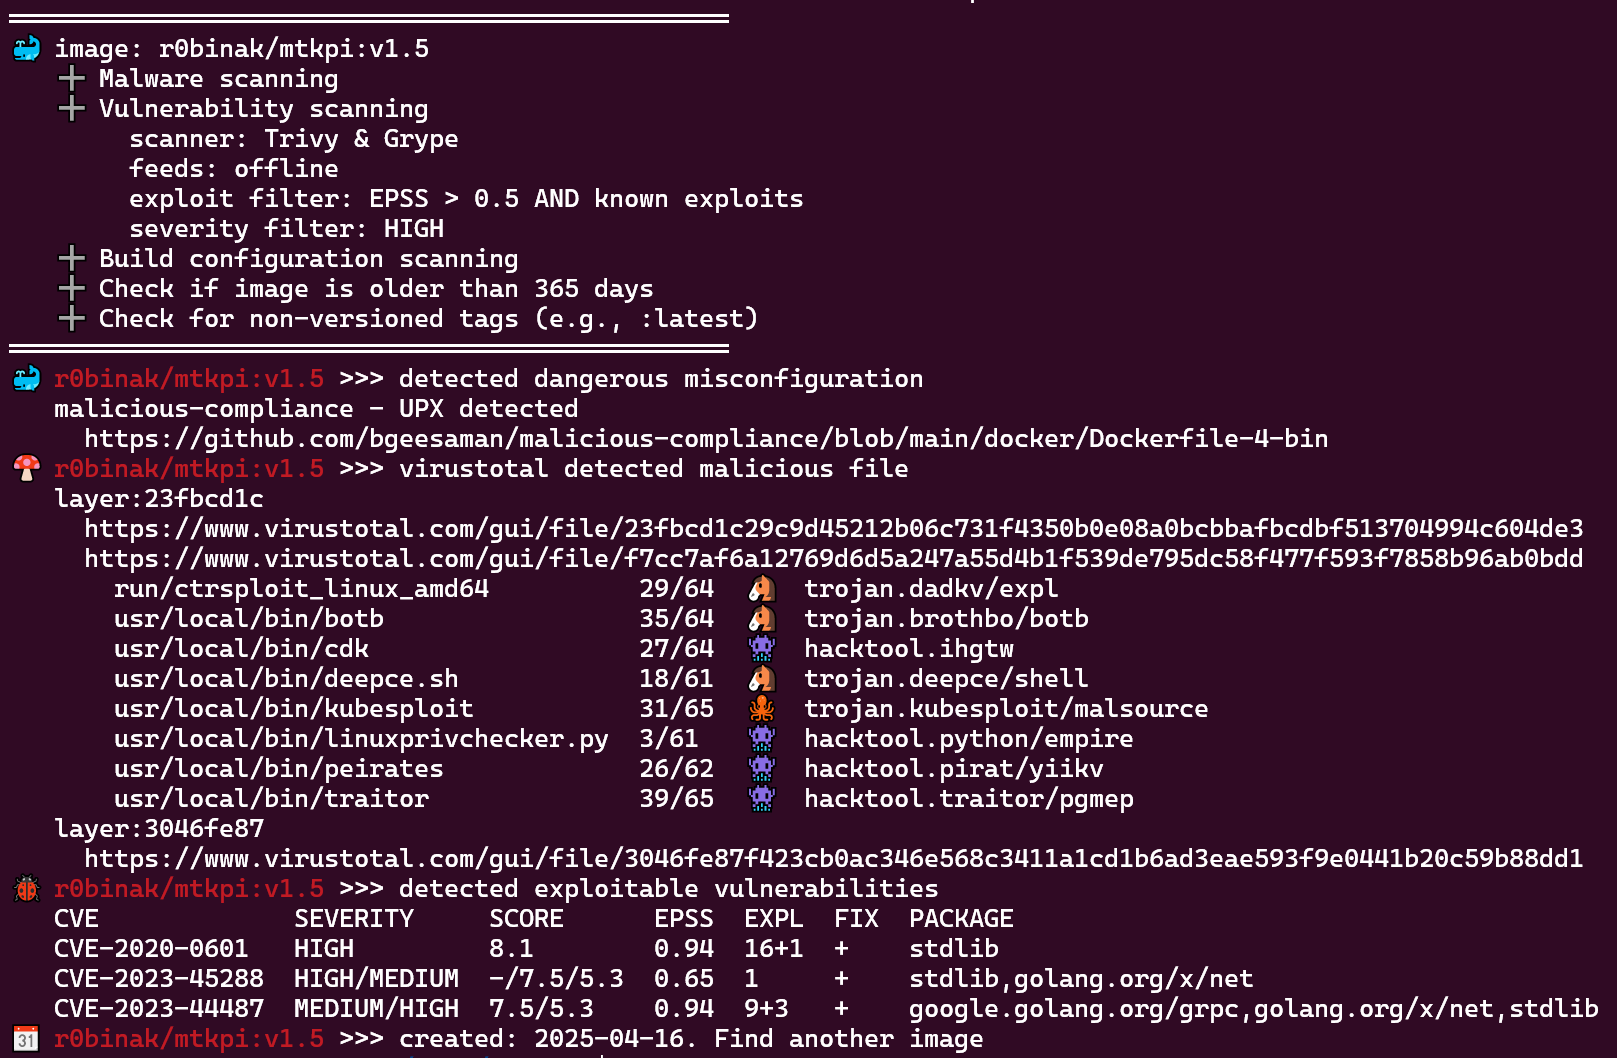
pisc
 ecomtech-oss/pisc
Public OCI-Image (docker image) Security Checker
container-securitydevsecopsmalware-analysis+3
217 months ago
ecomtech-oss/piscPublic OCI-Image (docker image) Security Checker
 brinhosa/cve-2024-3094-one-liner
One-liner scripts to check server and Docker image vulnerability to CVE-2024-3094, including version detection and repository scanning for xz…
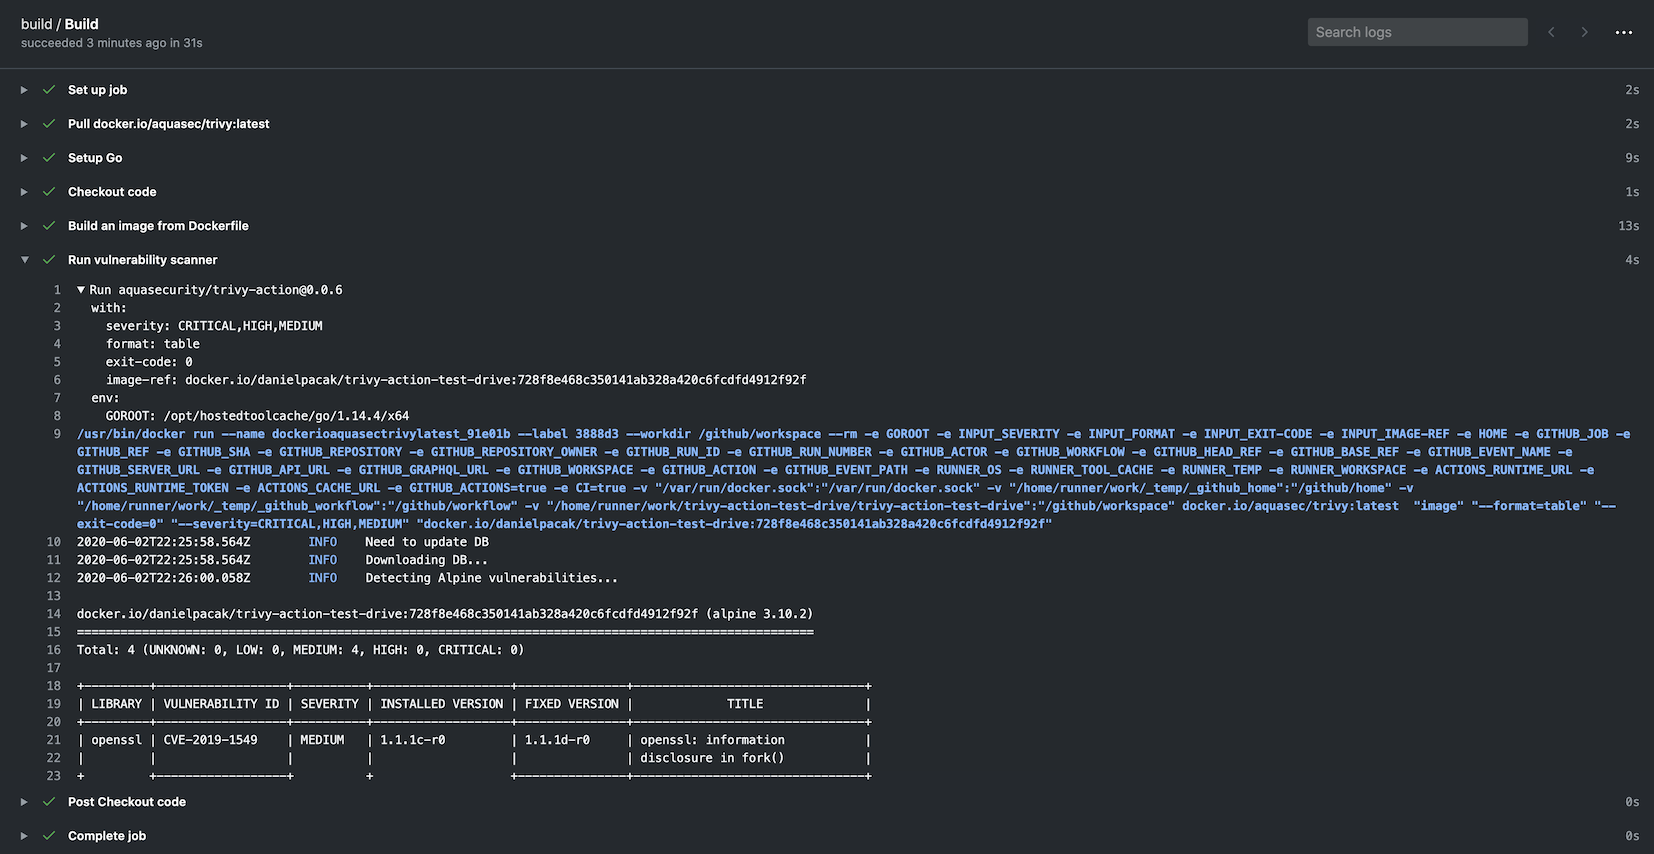 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 kavin71725/cve-2025-12543-fix-for-wildfly
Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…
 crazycatmyopic/cve
Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
 lhotari/pulsar-docker-images-patch-cve-2021-44228
Patch Pulsar Docker images with Log4J 2.17.1 update to mitigate Apache Log4J Security Vulnerabilities including Log4Shell
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 george0papasotiriou/cve-2026-21005-docker-registry-v2-schema-1-image-poisoning
Exploits CVE-2026-21005 by poisoning Docker Registry V2 Schema 1 manifests via unauthenticated pushes, enabling tag overwrite and supply-chain…
 snyk/snyk-scan
Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.
 rotavori/dasel-melange-apko
dasel v3.3.1 packaged with Melange and shipped as a minimal apko image, patched for CVE-2026-33320
 shoucheng3/eclipse__hawkbit_cve-2020-27219_0-3-0m6
Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…