jenkinsci__workflow-cps-global-lib-plugin_CVE-2022-25174_544-vff04fa68714d

Exploit for CVE-2022-25174 in Jenkins Pipeline Shared Libraries plugin, demonstrating code injection via crafted library definitions for security…

Exploit for CVE-2022-25174 in Jenkins Pipeline Shared Libraries plugin, demonstrating code injection via crafted library definitions for security…

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…

opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis

Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.

GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

Collect VEX documents and update VEX Hub

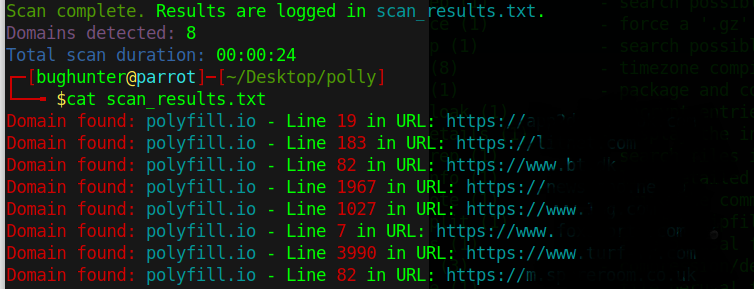
CVE-2024-38526 - Polyfill Scanner

Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows

Minimal reproduction of CVE-2022-46175 demonstrating a JSON5 prototype pollution vulnerability in Quasar webpack projects for security education and…

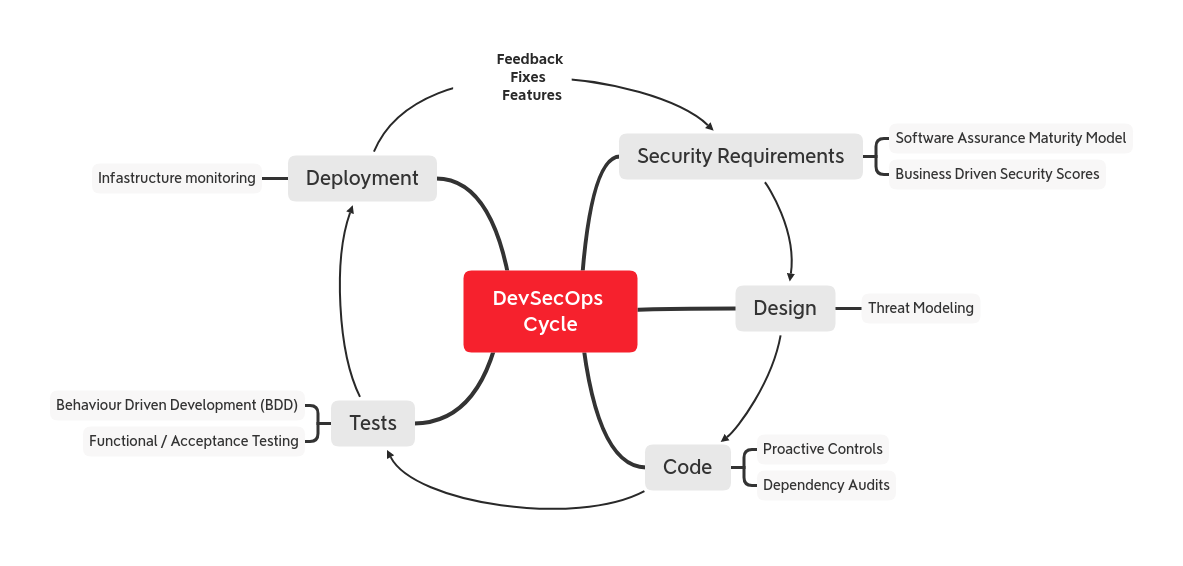
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.

Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…

Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…

OWASP Autonomous Penetration Testing Standard

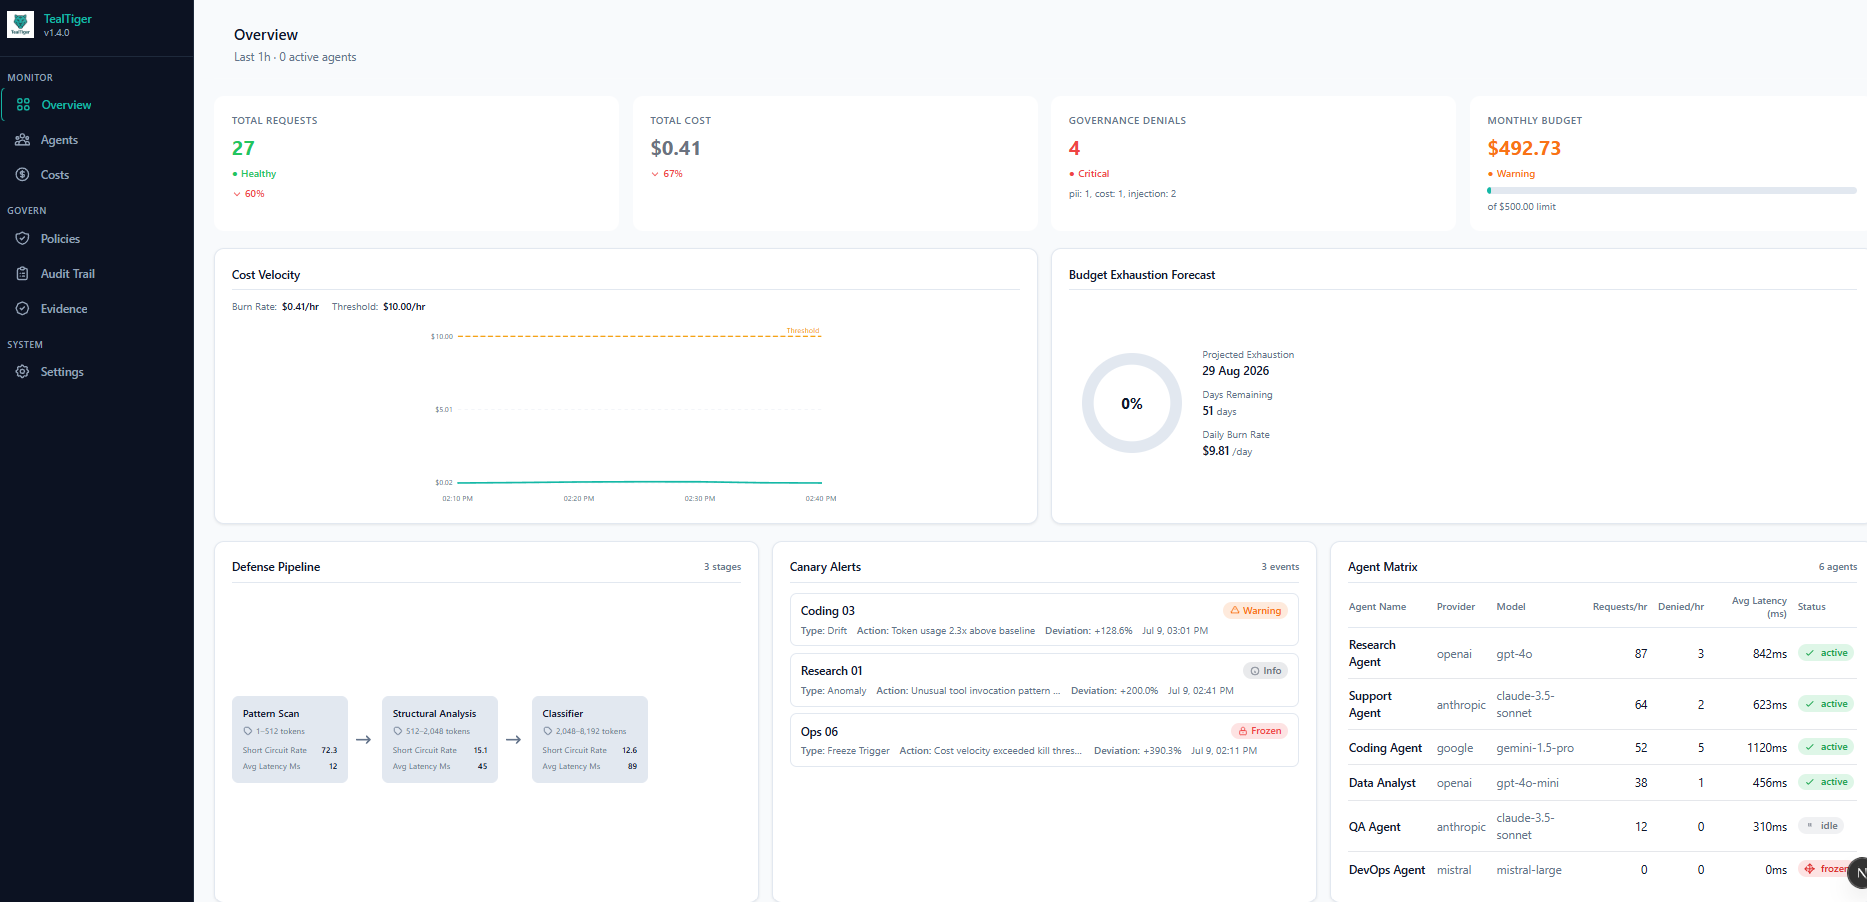
Powerful protection for AI agents - Open-source security and cost tracking for AI applications

100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI

Security gateway for MCP servers with per-tool policy enforcement, Ed25519-signed audit receipts, and shadow-mode logging. Supports Cedar, OPA, and…